Skip to content
November 1, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
CVE-2026-63077: TeamCity RCE Flaw Exploited in the Wild, CISA Warns JetBrains TeamCity vulnerability CVE-2026-63077 remote code execution alert added to CISA KEV catalog
  • Vulnerability Report

CVE-2026-63077: TeamCity RCE Flaw Exploited in the Wild, CISA Warns

Do Son August 6, 2026 0

TeamCity vulnerability CVE-2026-63077 enables unauthenticated remote code execution. CISA added it to the KEV catalog amid active exploitation.
CVE-2026-70426: Critical Jenkins RCE Flaw Bypasses Deserialization Filter Critical Jenkins vulnerability CVE-2026-70426 lets attackers bypass the JEP-200 filter and run code on the controller. Patch now.
  • Vulnerability Report

CVE-2026-70426: Critical Jenkins RCE Flaw Bypasses Deserialization Filter

Do Son August 6, 2026 0

Critical Jenkins vulnerability CVE-2026-70426 lets attackers bypass the JEP-200 filter and run code on the controller. Patch now.

CVE-2026-20303 & CVE-2026-20304: Cisco SD-WAN Flaws Hit CVSS 9.9 Cisco Catalyst SD-WAN vulnerability dashboard showing CVE-2026-20303 and CVE-2026-20304 critical CVSS 9.9 advisory
  • Vulnerability Report

CVE-2026-20303 & CVE-2026-20304: Cisco SD-WAN Flaws Hit CVSS 9.9

Do Son August 5, 2026 0

Cisco SD-WAN vulnerability CVE-2026-20303 and CVE-2026-20304 reach CVSS 9.9. Cisco urges Catalyst SD-WAN customers to patch now.
SGLang Hit by Six Vulnerabilities, Including Unauthenticated RCE (CVE-2026-15969) SGLang vulnerabilities unauthenticated remote code execution CVE-2026-15969
  • Vulnerability Report

SGLang Hit by Six Vulnerabilities, Including Unauthenticated RCE (CVE-2026-15969)

Do Son August 5, 2026 0

Six SGLang vulnerabilities include unauthenticated RCE via CVE-2026-15969, plus data and model-weight theft. No patch exists yet.
CVE-2026-9044: TP-Link Command Injection Hits Archer AXE75 TP-Link command injection vulnerability CVE-2026-9044 in Archer AXE75 OpenVPN module
  • Vulnerability Report

CVE-2026-9044: TP-Link Command Injection Hits Archer AXE75

Do Son August 5, 2026 0

CVE-2026-9044 is a command injection flaw in TP-Link Archer AXE75 OpenVPN, CVSS 8.5. Update to firmware 1.5.6 Build 20260623 now.
IBM Patches Three CVSS 9.8 Flaws, Including CVE-2026-12943 Command Execution IBM critical vulnerabilities CVE-2026-12943 arbitrary command execution at CVSS 9.8
  • Vulnerability Report

IBM Patches Three CVSS 9.8 Flaws, Including CVE-2026-12943 Command Execution

Do Son August 5, 2026 0

IBM critical vulnerabilities hit App Connect, Power HMC, and webMethods. CVE-2026-12943 lets attackers execute arbitrary commands at CVSS 9.8.
New Research: The Confidence Gap Between CISOs and Their Boards Is Real, and It’s Measurable CISO-Board_Communication_Gap_1785865092WlZ0ppW5K6
  • Press Release

New Research: The Confidence Gap Between CISOs and Their Boards Is Real, and It’s Measurable

cybernewswire August 5, 2026 0
Las Vegas, United States, 5th August 2026, CyberNewswire
Read More Read more about New Research: The Confidence Gap Between CISOs and Their Boards Is Real, and It’s Measurable
Linux suTrap Local Privilege Escalation Flaw PoC Exploit Disclosed Diagram demonstrating the Linux suTrap LPE flaw and the interactive su TIOCSTI bug attack flow
  • Vulnerability Report

Linux suTrap Local Privilege Escalation Flaw PoC Exploit Disclosed

Do Son August 5, 2026 0

This interactive su TIOCSTI bug is a critical Linux suTrap LPE flaw allowing root session hijacking. Exploit code details are publicly disclosed.
CVE-2026-20272 & CVE-2026-20267: Cisco IOS XE Flaws Hit CVSS 9.8 Cisco IOS XE vulnerability dashboard showing CVE-2026-20272 and CVE-2026-20267 critical CVSS 9.8 security advisory
  • Vulnerability Report

CVE-2026-20272 & CVE-2026-20267: Cisco IOS XE Flaws Hit CVSS 9.8

Do Son August 5, 2026 0

Cisco IOS XE vulnerability CVE-2026-20272 hits CVSS 9.8 and CVE-2026-20267 scores 9.0. Cisco urges customers to patch now.
Uppsala Security Becomes First Blockchain Intelligence Company to Join Cyber Threat Alliance pi-social-post-en_1785828810lSp7i5hdEe
  • Press Release

Uppsala Security Becomes First Blockchain Intelligence Company to Join Cyber Threat Alliance

cybernewswire August 5, 2026 0
SIngapore, Singapore, 5th August 2026, CyberNewswire
Read More Read more about Uppsala Security Becomes First Blockchain Intelligence Company to Join Cyber Threat Alliance
NVIDIA Dynamo Code Execution Flaw CVE-2026-24254 CVSS 9.8 NVIDIA Dynamo flaw diagram explaining the code execution attack vector and CVE-2026-24254 CVSS score
  • Vulnerability Report

NVIDIA Dynamo Code Execution Flaw CVE-2026-24254 CVSS 9.8

Do Son August 5, 2026 0

NVIDIA warns of a critical 9.8 CVSS NVIDIA Dynamo flaw (CVE-2026-24254) leading to code execution. Update to the latest version to secure your systems.
Apple Bug Bounty Limits AI Slop and Fake Reports Apple Bug Bounty AI vulnerability reports limitation
  • Technology

Apple Bug Bounty Limits AI Slop and Fake Reports

Do Son August 5, 2026 0

Apple restricts its Bug Bounty program to combat a surge of fake AI-generated vulnerability reports, instituting caps to protect critical flaw detection.
Perplexity Achieves Major Legal Victory Over Amazon Perplexity AI shopping bot overturning Amazon legal injunction
  • Technology

Perplexity Achieves Major Legal Victory Over Amazon

Do Son August 5, 2026 0

Perplexity secured a major legal victory as an appeals court overturned an Amazon ban, allowing the Perplexity AI shopping bot to resume price comparisons.
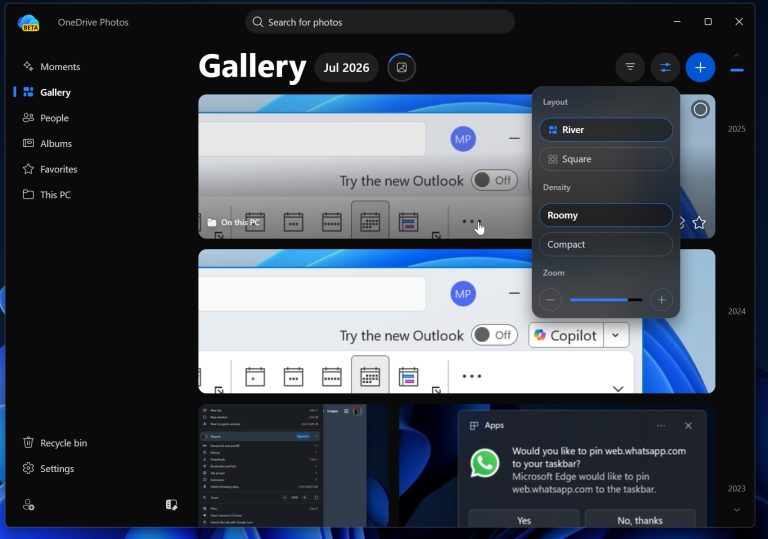
Microsoft Forces OneDrive Photos Install on Windows Microsoft OneDrive Photos forced install error on Windows
  • Technology

Microsoft Forces OneDrive Photos Install on Windows

Do Son August 5, 2026 0

Microsoft is aggressively pushing a OneDrive Photos forced install on all Windows devices. This beta app frustrates enterprise IT admins and individual users.
OctLurk and SilkLurk Backdoors Hit Central Asian Government Networks OctLurk and SilkLurk backdoors targeting Central Asian government espionage campaign
  • Malware

OctLurk and SilkLurk Backdoors Hit Central Asian Government Networks

Do Son August 5, 2026 0

Kaspersky GReAT uncovered OctLurk and SilkLurk, two new memory-resident backdoors targeting Central Asian governments since January 2025.
XMRig Botnet Abuses Linux PAM to Spread Forensic Smokescreen Across User Accounts XMRig Linux PAM abuse fileless cryptominer V25 botnet forensic smokescreen
  • Malware

XMRig Botnet Abuses Linux PAM to Spread Forensic Smokescreen Across User Accounts

Do Son August 5, 2026 0

Group-IB uncovered XMRig Linux PAM abuse that lets a fileless Monero miner regenerate across user accounts and vanish from disk forensics.
Chinese Threat Actor Runs Autonomous AI Cyberattacks Using DeepSeek JADEPUFFER agentic ransomware attack chain diagram from Langflow RCE to database extortion
  • Cybercriminals

Chinese Threat Actor Runs Autonomous AI Cyberattacks Using DeepSeek

Do Son August 5, 2026 0

Unit 42 exposed an autonomous AI cyberattack by a Chinese threat actor using DeepSeek to scan, pivot, and exploit targets on its own.
Adform Cyber Attack: Malicious Scripts Hijack Crypto Wallets CVE-2026-18072 video embedder backdoor authentication bypass
  • Cybercriminals

Adform Cyber Attack: Malicious Scripts Hijack Crypto Wallets

Do Son August 5, 2026 0

Adform experienced a cyber attack where hackers altered ad scripts to hijack cryptocurrency addresses. Learn how this supply chain attack affects users.
Windows Control Panel Migration: Why Legacy Code Persists Windows Control Panel migration to modern Settings app in Windows 11
  • Windows

Windows Control Panel Migration: Why Legacy Code Persists

Do Son August 5, 2026 0

Microsoft explains why Windows Control Panel migration takes so long. Legacy driver support and enterprise compatibility delay the complete transition.
Cloudflare Wallets: Programmable Payment and Identity Infrastructure for AI Agents Cloudflare Wallets programmable payment and identity infrastructure for AI agents using x402 protocol and virtual wallet system
  • Technology

Cloudflare Wallets: Programmable Payment and Identity Infrastructure for AI Agents

Do Son August 5, 2026 0

Cloudflare Wallets gives AI agents a native payment method and verifiable identity via x402 protocol, enabling autonomous micropayments without human intervention.
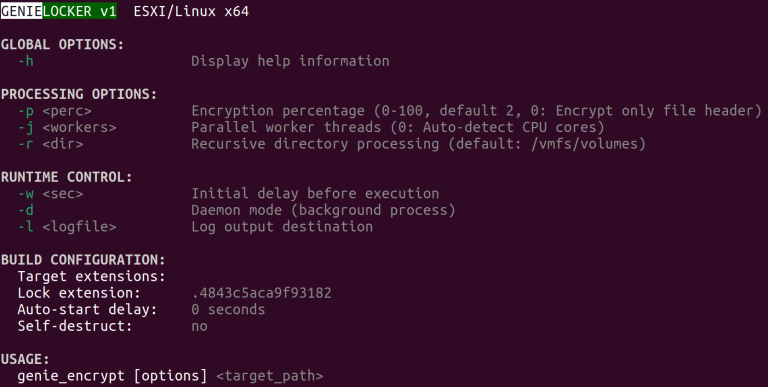
GenieLocker Ransomware Targets Russian Manufacturers on Windows, Linux, and ESXi GenieLocker ransomware by Toy Ghouls targeting Russian manufacturing on Windows Linux ESXi
  • Malware

GenieLocker Ransomware Targets Russian Manufacturers on Windows, Linux, and ESXi

Do Son August 5, 2026 0

GenieLocker ransomware hits Russia's manufacturing sector on Windows, Linux, and ESXi. Linked to the Toy Ghouls group, it leaves no ransom note.
Django Vulnerability CVE-2026-15307 Can Enable Remote Code Execution Django vulnerability CVE-2026-15307 server-side file write and remote code execution via spatial lookups security release
  • Vulnerability Report

Django Vulnerability CVE-2026-15307 Can Enable Remote Code Execution

Do Son August 5, 2026 0

A high-severity Django vulnerability, CVE-2026-15307, can enable remote code execution through spatial lookups. Update to Django 6.0.8 or 5.2.17 now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    📅 Updated: Oct 31, 2026
  • CVE-2026-118636CVSS 9.8
    **UNSUPPORTED WHEN ASSIGNED**  JavaNativeMessageDecoder in the MINA 3.0 codec module calls ObjectInputStream.readObject() on frame bytes with no class...
    📅 Updated: Oct 31, 2026
  • CVE-2026-120209CVSS 9.3
    AJ-Report through 1.7.1 signs share tokens with a hard-coded JWT secret, allowing attackers to forge valid Share-Tokens offline....
    📅 Updated: Oct 31, 2026
  • CVE-2026-120201CVSS 9.3
    Jpom 2.10.0 through 2.11.12 contains an authentication bypass vulnerability that allows unauthenticated attackers to gain super-administrator access by...
    📅 Updated: Oct 31, 2026
  • CVE-2026-69399CVSS 9.9
    Unintended proxy or intermediary in Azure Arc allows an authorized attacker to elevate privileges over a network.
    📅 Updated: Oct 31, 2026
  • CVE-2026-113380CVSS 9.3
    In the RingRTC library before 2.72.0 for Signal, a peer that saturates a call's FSM queue can interfere...
    📅 Updated: Oct 31, 2026
  • CVE-2026-99153CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: scsi: libiscsi: Validate the ITT reflected in a...
    📅 Updated: Oct 31, 2026
  • CVE-2026-99154CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: scsi: libiscsi: Reject a negative task index from...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.