 Do Son
CISA added three bugs to its KEV list. An N-able N-central authentication bypass is exploited in the wild to deploy RMM tools. Patch by August 7.
A pgAdmin 4 RCE flaw, CVE-2026-17566, lets attackers run OS commands via psql. Two more critical bugs also got fixed in version 9.17.
 cybernewswire
A critical Veeam ONE vulnerability, CVE-2026-64633, allows remote unauthenticated code execution at CVSS 10.0. Update to build 13.1.0.7034 now.
Las Vegas, United States, 4th August 2026, CyberNewswire
A critical Xlight FTP Server flaw, CVE-2026-67192, is a pre-authentication stack buffer overflow that risks remote code execution. Update to 3.9.5 now.
A new npm supply chain attack hijacked keyv and dozens of packages, spreading Shai-Hulud malware that steals cloud and CI/CD secrets. Rotate keys now.
A critical Terraform MCP Server flaw, CVE-2026-16498, hits CVSS 10.0. Three bugs risk Terraform token theft and cross-tenant reuse. Upgrade to 1.1.0.
Apache Traffic Server vulnerabilities: 38 flaws fixed in 9.2.15 and 10.1.4, including request smuggling and memory-safety bugs. Update your CDN proxy now.
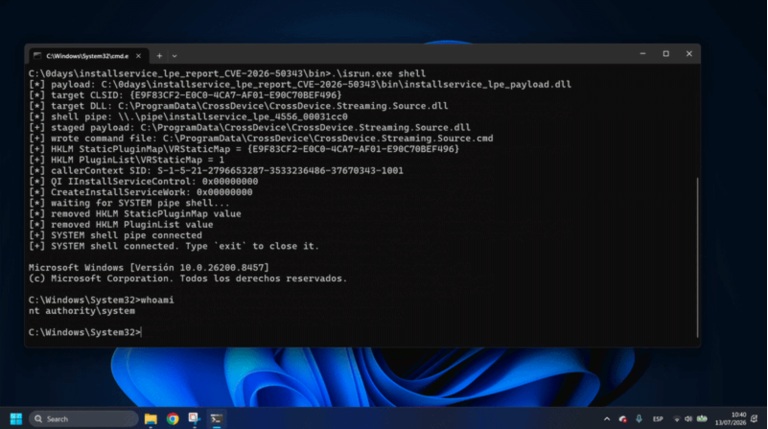
Details and proof-of-concept exploit code for CVE-2026-50343 are now public. The Windows privilege escalation flaw hands standard users SYSTEM privileges.
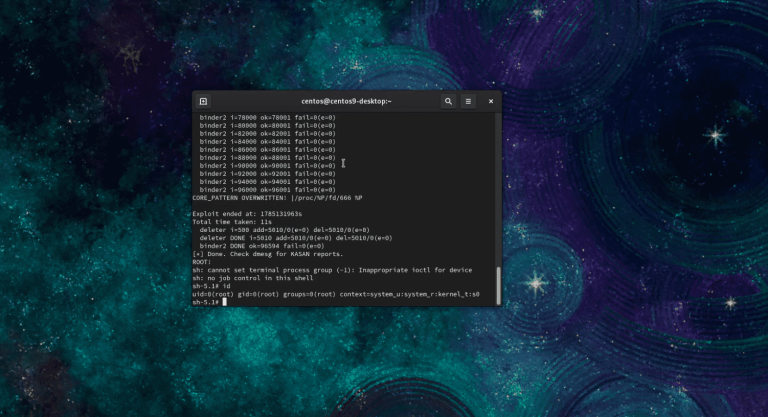
A Linux kernel vulnerability, CVE-2026-53264, lets a local user run arbitrary code via a net/sched use-after-free. A public PoC is now available.
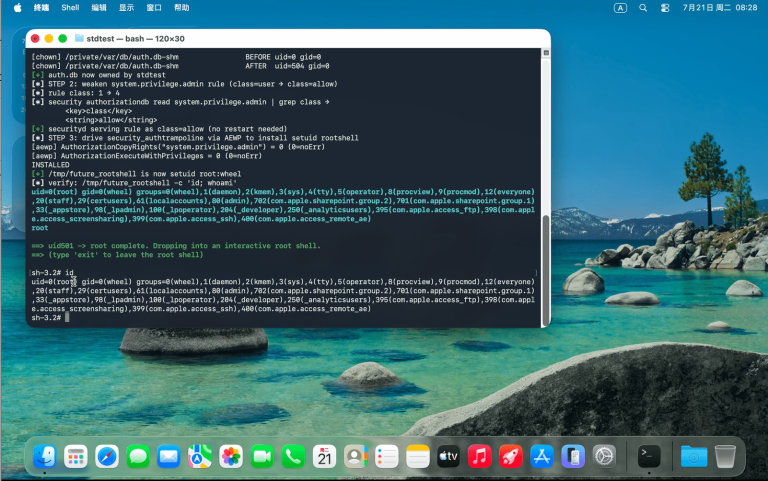
A macOS privilege escalation flaw gives an unprivileged user root with no user interaction. A full public PoC is out; Apple fixed it in 26.6 with no CVE.
Amazon ties North Korean hackers to open-source supply chain attacks on the axios, debug, and chalk NPM packages. Here's how the campaign worked.
A critical Gitea vulnerability, CVE-2026-59774, lets unauthenticated attackers read server files and reach remote code execution. Update to 1.27.1 now.
A Microsoft Teams vishing campaign tracked as STAC4749 hit dozens of North American firms and deployed Chaos ransomware in under 17 hours.

The Dysphoria botnet uses blockchain ENS/SNS domains for covert C2 and turns victims into relays. XLab tracked over 200,000 bots in this IoT DDoS botnet.
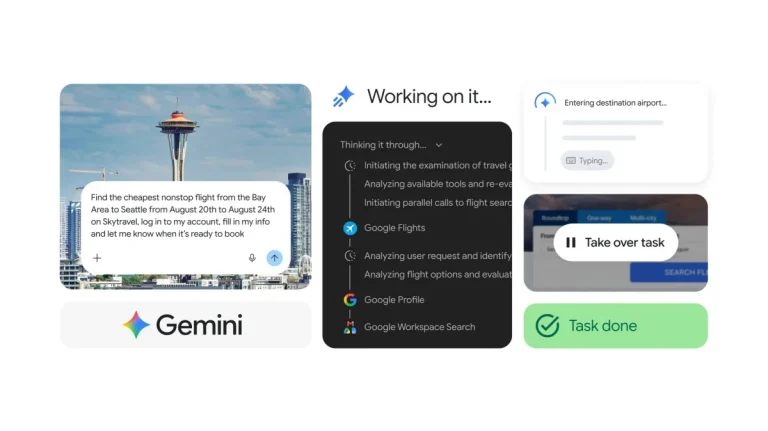
Discover the Gemini Spark Auto Browse feature. Google transforms Chrome with an agentic AI assistant that safely automates complex tasks and web browsing.
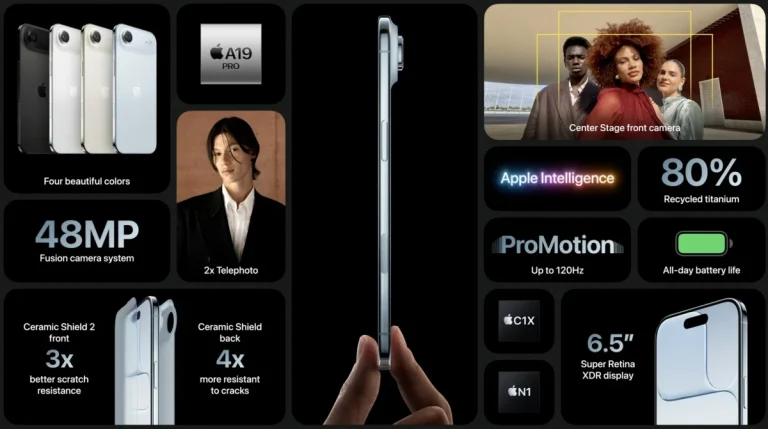
Apple will finally develop a universal iPhone Windows copy paste feature due to EU regulations. Microsoft successfully petitioned for seamless clipboard sync.
Google is testing a Chrome security feature that blocks malware from using enterprise policy tools to hijack the default search engine or new tab page.
A critical Veeam Service Provider Console flaw lets attackers steal agent credentials, while a second enables remote code execution. Update to 9.3 now.
The EU AI Act transparency rules are now active. Article 50 forces strict labels for deepfakes, chatbots, and AI content. Discover the new obligations.