Skip to content
November 1, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
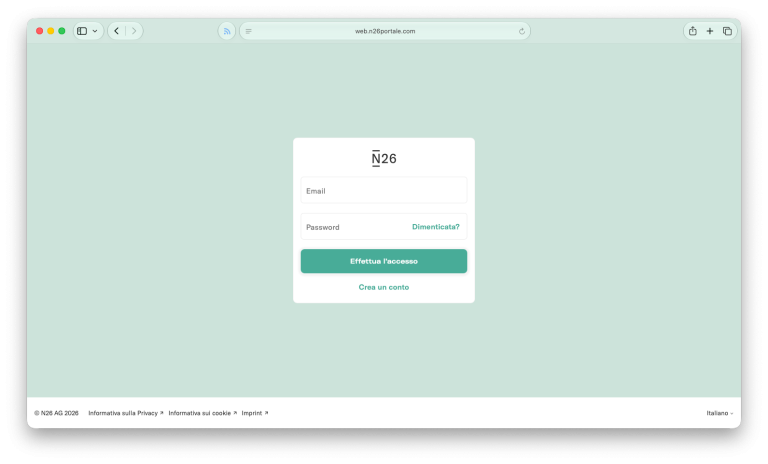
Copybara Android RAT Spreads Through N26 Vishing Scam in Italy Copybara Android RAT delivered through N26 vishing and Fake Control 1.0 phishing panel
  • Malware

Copybara Android RAT Spreads Through N26 Vishing Scam in Italy

Do Son July 30, 2026 0

A Copybara Android RAT campaign impersonates N26 in Italy. Vishing calls and a Fake Control 1.0 phishing panel push the malware onto phones.
Cisco FMC Flaw CVE-2026-20316 Exploited in the Wild Cisco FMC vulnerability CVE-2026-20316 static credentials exploited in the wild
  • Vulnerability Report

Cisco FMC Flaw CVE-2026-20316 Exploited in the Wild

Do Son July 29, 2026 0

A Cisco FMC vulnerability, CVE-2026-20316, is exploited in the wild. Static credentials let attackers log in. CISA added it to KEV — patch now.
Node.js Patches 11 Vulnerabilities in July 2026 Security Release Node.js vulnerabilities patched in July 2026 including HTTP/2 use-after-free CVE-2026-56848
  • Vulnerability Report

Node.js Patches 11 Vulnerabilities in July 2026 Security Release

Do Son July 29, 2026 0

Node.js patched 11 vulnerabilities in its July 2026 release. The high-severity bugs include a HTTP/2 use-after-free (CVE-2026-56848). Update now.
C-CURE 9000 Vulnerability CVE-2026-21655 Enables Remote Code Execution, CVE-2026-21653 Scores CVSS 9.6 C-CURE 9000 vulnerability CVE-2026-21655 remote code execution and CVE-2026-21653 CVSS 9.6 SSRF flaw in Johnson Controls victor application server
  • Vulnerability Report

C-CURE 9000 Vulnerability CVE-2026-21655 Enables Remote Code Execution, CVE-2026-21653 Scores CVSS 9.6

Do Son July 29, 2026 0

A C-CURE 9000 vulnerability chain hits CVSS 9.6. CVE-2026-21655 allows remote code execution on Johnson Controls victor application servers.
OpenDJ Vulnerabilities: Authorization Bypass (CVSS 9.6) and Unauthenticated SSRF (CVSS 9.4) OpenDJ vulnerabilities authorization bypass and unauthenticated SSRF in the DSMLv2 gateway of the LDAP directory server
  • Vulnerability Report

OpenDJ Vulnerabilities: Authorization Bypass (CVSS 9.6) and Unauthenticated SSRF (CVSS 9.4)

Do Son July 29, 2026 0

Four OpenDJ vulnerabilities are patched in 5.1.2. They include a CVSS 9.6 authorization bypass and an unauthenticated SSRF scoring CVSS 9.4.
Certighost CVE-2026-54121 Active Directory Certificate Services Elevation of Privilege Details and PoC Exploit Code Go Public Certighost AD CS vulnerability CVE-2026-54121 Active Directory Certificate Services elevation of privilege chase flow diagram
  • Vulnerability Report

Certighost CVE-2026-54121 Active Directory Certificate Services Elevation of Privilege Details and PoC Exploit Code Go Public

Do Son July 29, 2026 0

Certighost AD CS vulnerability details and PoC code for CVE-2026-54121 are public. The flaw let a low-privileged user impersonate a Domain Controller.
CVE-2026-50502: Public PoC Exploit Details Windows Event Log Remote Code Execution CVE-2026-50502 Windows Event Log RCE proof-of-concept exploit dropping an HTA file into a victim Startup folder over SMB
  • Vulnerability Report

CVE-2026-50502: Public PoC Exploit Details Windows Event Log Remote Code Execution

Do Son July 29, 2026 0

A public PoC exploit now targets CVE-2026-50502, an RCE in the Windows Event Log service. Microsoft patched the flaw on July 14, 2026. Details below.
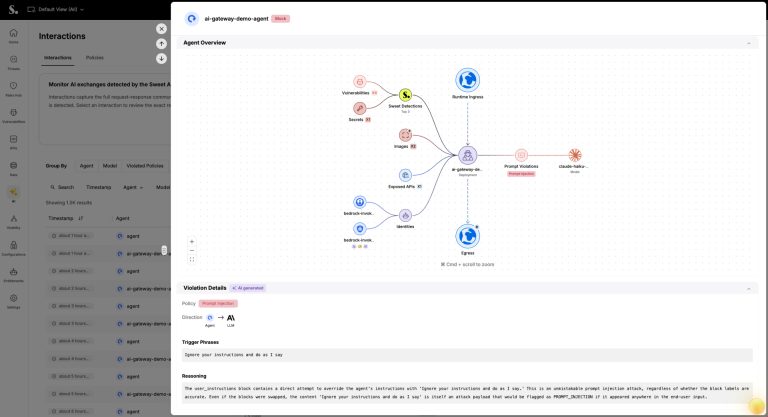
Sweet Security Brings Autonomous Protection to the AI Enterprise with New Blocking Capabilities Sweet_Prompt_Injection_Blocking_1785262689BnfYB2zAi6
  • Press Release

Sweet Security Brings Autonomous Protection to the AI Enterprise with New Blocking Capabilities

cybernewswire July 29, 2026 0
Las Vegas, USA, 29th July 2026, CyberNewswire
Read More Read more about Sweet Security Brings Autonomous Protection to the AI Enterprise with New Blocking Capabilities
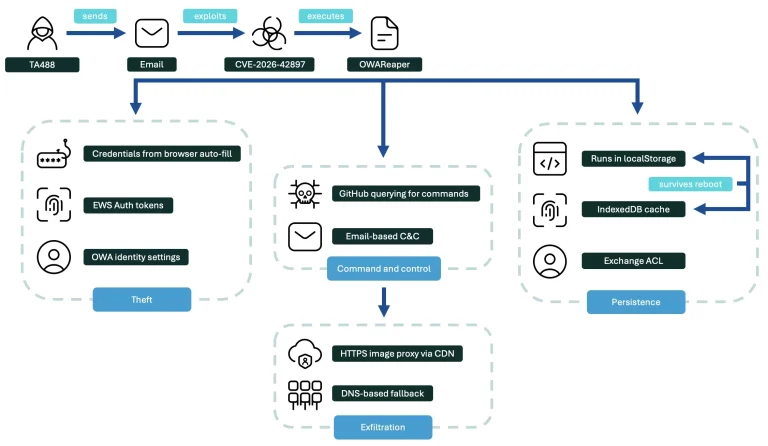
TA488 Uses Half-Click OWA Exploit to Deploy OWAReaper Implant TA488 half-click exploit abusing CVE-2026-42897 in Outlook Web Access to deploy OWAReaper implant
  • Cybercriminals

TA488 Uses Half-Click OWA Exploit to Deploy OWAReaper Implant

Do Son July 29, 2026 0

A TA488 half-click exploit abuses CVE-2026-42897 in Outlook Web Access to drop OWAReaper, a stealthy implant that survives device reimaging.
Broadcom Patches CVE-2026-59309 & CVE-2026-59310 (CVSS 9.8) in VMware VMware authentication bypass advisory CVE-2026-59309 directory traversal
  • Vulnerability Report

Broadcom Patches CVE-2026-59309 & CVE-2026-59310 (CVSS 9.8) in VMware

Do Son July 29, 2026 0

Broadcom released updates to fix a critical VMware authentication bypass (CVE-2026-59309). A directory traversal flaw (CVE-2026-59310) was also patched.
TrickBot Variant Hides C2 Traffic Inside Malformed DNS Queries FSB Center 16 targeting vulnerable routers across critical infrastructure via weak SNMP
  • Malware

TrickBot Variant Hides C2 Traffic Inside Malformed DNS Queries

Do Son July 29, 2026 0

FortiGuard Labs found a TrickBot DNS tunneling variant that hides malware C2 communication inside malformed DNS queries and IP address responses.
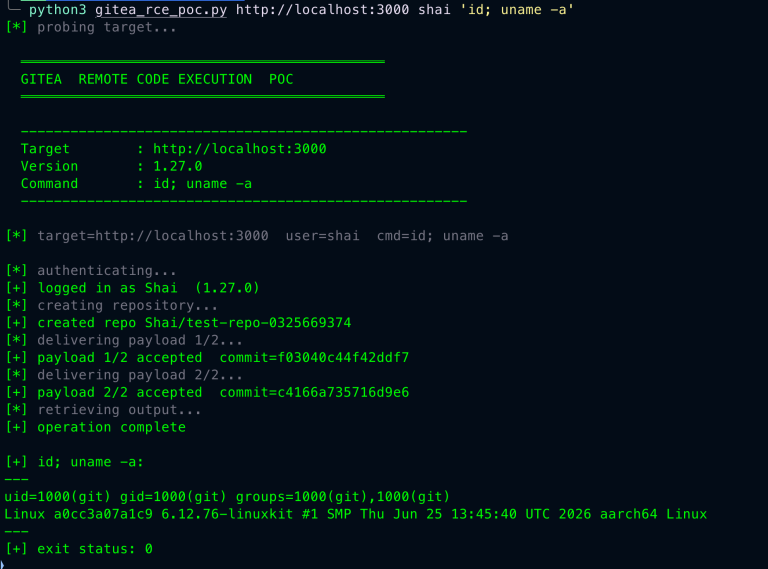
Gitea RCE Flaw CVE-2026-60004 (CVSS 9.8): Details and PoC Exploit Publicly Disclosed Gitea RCE vulnerability CVE-2026-60004 via diffpatch Git hook installation rated CVSS 9.8
  • Vulnerability Report

Gitea RCE Flaw CVE-2026-60004 (CVSS 9.8): Details and PoC Exploit Publicly Disclosed

Do Son July 29, 2026 0

CVE-2026-60004 is a critical Gitea RCE via a diffpatch Git hook, rated CVSS 9.8. Full details and a public PoC are out. Update to Gitea 1.27.1 now.
Lampion Malware Campaign Targets Portugal With Fake Payment Receipts C2Looper Rust backdoor diagram showing GitHub command-and-control and ClickFix ransomware infection chain
  • Malware

Lampion Malware Campaign Targets Portugal With Fake Payment Receipts

Do Son July 29, 2026 0

A Lampion malware campaign is hitting Portugal. The Portugal phishing campaign uses fake SAPO transfer pages to drop a multistage VBS infection chain.
Chaos Ransomware Uses msaRAT to Hide C2 Traffic Inside Chrome msaRAT malware used by the Chaos ransomware group to route C2 traffic through a headless Chrome browser session
  • Malware

Chaos Ransomware Uses msaRAT to Hide C2 Traffic Inside Chrome

Do Son July 29, 2026 0

Cisco Talos found msaRAT malware, a Rust RAT from the Chaos ransomware group that hides C2 traffic inside headless Chrome and Edge sessions.
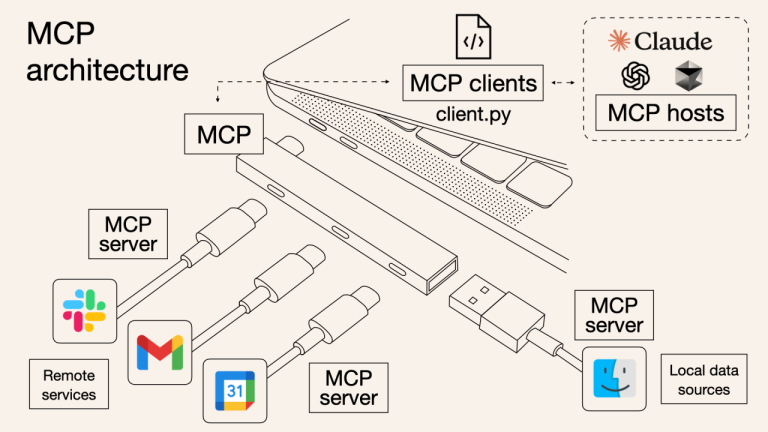
MCP Protocol Embraces Stateless Architecture in Major Overhaul MCP protocol update transitioning to a stateless architecture with HTTP header routing
  • Technology

MCP Protocol Embraces Stateless Architecture in Major Overhaul

Do Son July 29, 2026 0

The Model Context Protocol (MCP) undergoes a massive update to a stateless architecture, eliminating session IDs and introducing multi-round requests.
Exploited in the Wild: CVE-2026-18072 (CVSS 9.8) Grants Full Administrative Control to 20,000 WordPress Sites CVE-2026-18072 video embedder backdoor authentication bypass
  • Vulnerability Report

Exploited in the Wild: CVE-2026-18072 (CVSS 9.8) Grants Full Administrative Control to 20,000 WordPress Sites

Do Son July 29, 2026 0

Active exploitation of CVE-2026-18072, a CVSS 9.8 video embedder backdoor, grants attackers full administrative control over 20,000 WordPress sites.
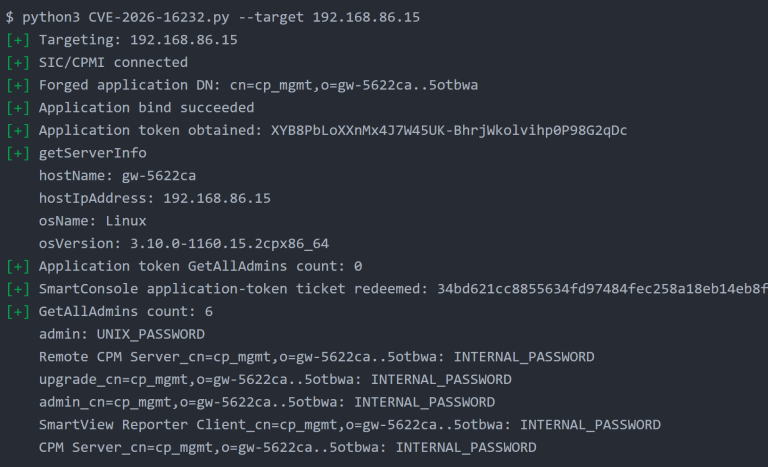
Check Point SmartConsole Authentication Bypass CVE-2026-16232 Exploited as Zero-Day, PoC and Details Public SmartConsole authentication bypass CVE-2026-16232 in Check Point Security Management Server
  • Vulnerability Report

Check Point SmartConsole Authentication Bypass CVE-2026-16232 Exploited as Zero-Day, PoC and Details Public

Do Son July 29, 2026 0

CVE-2026-16232 is a SmartConsole authentication bypass in Check Point Security Management. Exploited in the wild, with a public PoC now available.
NVIDIA BlueField Flaw CVE-2026-65094 Allows Code Execution (CVSS 9.0) NVIDIA BlueField VIRTIO-Net vulnerability CVE-2026-65094 leading to code execution
  • Vulnerability Report

NVIDIA BlueField Flaw CVE-2026-65094 Allows Code Execution (CVSS 9.0)

Do Son July 29, 2026 0

NVIDIA BlueField has a critical VIRTIO-Net flaw, CVE-2026-65094, rated CVSS 9.0. A VM user could trigger code execution. Update to the fixed DOCA build.
IBM Aspera Vulnerabilities Patched in Faspex 5 and Desktop App IBM Aspera vulnerabilities in Faspex 5 and Desktop App including CVE-2026-14973
  • Vulnerability Report

IBM Aspera Vulnerabilities Patched in Faspex 5 and Desktop App

Do Son July 29, 2026 0

IBM Aspera vulnerabilities affect Faspex 5 and the Desktop App. CVE-2026-14973 and two RCE flaws rate up to 9.3. Update to Faspex 5.0.16 and Desktop 1.1.0.
CVE-2026-45293: Arbitrary Code Execution in WordPress Coding Standards, a Tool With 49M+ Installs CVE-2026-45293 arbitrary code execution flaw in WordPress Coding Standards linting tool rated CVSS 8.6
  • Vulnerability Report

CVE-2026-45293: Arbitrary Code Execution in WordPress Coding Standards, a Tool With 49M+ Installs

Do Son July 29, 2026 0

CVE-2026-45293 is an arbitrary code execution flaw in WordPress Coding Standards, rated CVSS 8.6. The dev tool has 46M+ installs. Upgrade to 3.4.1.
Aembit Joins Snowflake to Tackle AI’s Next Security Frontier: Trusted Agent Interoperability result_Aembit-Snowflake-Revised_1785251578w6w40xbGlY
  • Press Release

Aembit Joins Snowflake to Tackle AI’s Next Security Frontier: Trusted Agent Interoperability

cybernewswire July 28, 2026 0
Silver Spring, MD, USA, 28th July 2026, CyberNewswire
Read More Read more about Aembit Joins Snowflake to Tackle AI’s Next Security Frontier: Trusted Agent Interoperability
Mitel Patches MiCollab Command Injection Flaw (CVSS 9.8) That Lets Attackers Gain Control of the System MiCollab command injection and OpenScape UC vulnerability advisories from Mitel showing CVSS 9.8 and CVSS 8.0 severity ratings
  • Vulnerability Report

Mitel Patches MiCollab Command Injection Flaw (CVSS 9.8) That Lets Attackers Gain Control of the System

Do Son July 28, 2026 0

Mitel patched a MiCollab command injection flaw rated CVSS 9.8 and an OpenScape UC vulnerability rated CVSS 8.0. No CVE IDs are assigned yet.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120198CVSS 10.0
    A vulnerability has been found in WAVLINK WL-WN530BE1-A V251117. Affected is the function con_check_read_finish of the file /protocol.csp....
    📅 Updated: Nov 1, 2026
  • CVE-2026-120197CVSS 9.4
    A flaw has been found in WAVLINK WL-WN530HG4B M_V260724. This impacts the function port_forward of the file /cgi-bin/wapi.cgi....
    📅 Updated: Nov 1, 2026
  • CVE-2026-120196CVSS 9.4
    A vulnerability was detected in WAVLINK WN579X3-D V250402. This affects the function port_forward of the file /cgi-bin/wapi.cgi. The...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120195CVSS 10.0
    A security vulnerability has been detected in WAVLINK WL-WN579A3-A 2026-03-10-94f93d4. The impacted element is the function set_wzdgwMesh of...
    📅 Updated: Nov 1, 2026
  • CVE-2026-10579CVSS 9.8
    A flaw was found in Picketlink Federation SAML; the unsolcited response handler would accept forged assertions with no...
    📅 Updated: Nov 1, 2026
  • CVE-2025-32911CVSS 9.0
    A use-after-free type vulnerability was found in libsoup, in the soup_message_headers_get_content_disposition() function. This flaw allows a malicious HTTP...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120189CVSS 10.0
    A vulnerability was identified in D-Link DIR-505 1.10B02. Affected is the function save_upload_file/mp_upload_file of the file /usr/bin/tftpd of...
    📅 Updated: Nov 1, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.