 Do Son
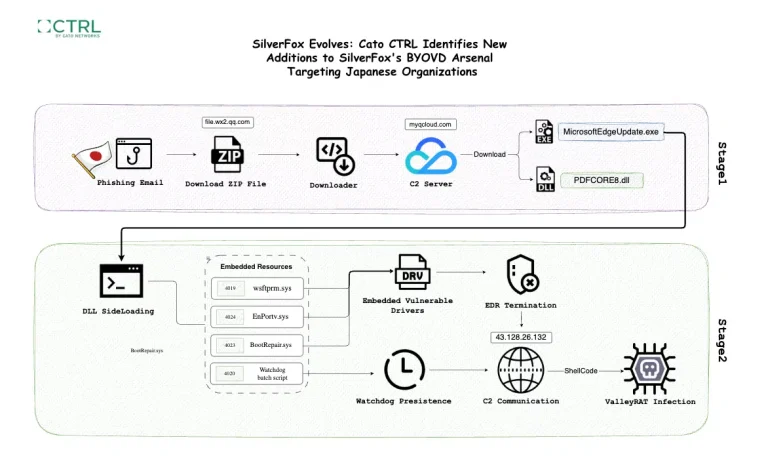
Cato CTRL details a new SilverFox ValleyRAT campaign in Japan using three BYOVD drivers and DLL sideloading to kill security tools.
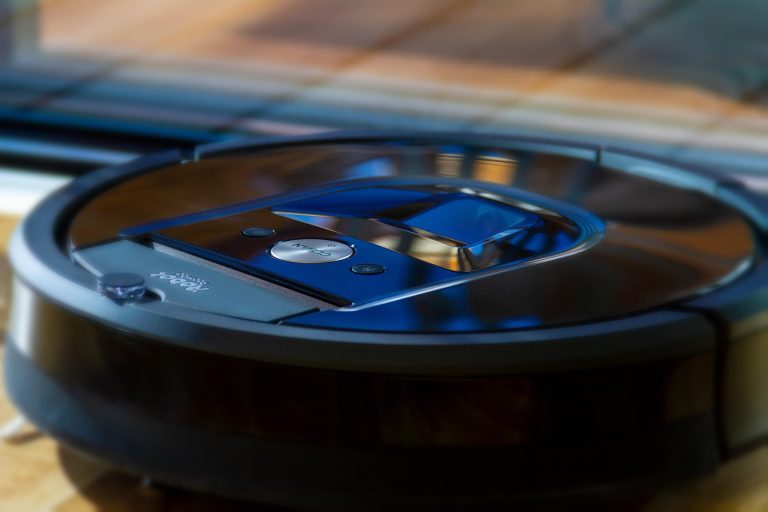
The FCC has banned the import and sale of new foreign-made robot vacuums in the US, citing broad definitions of advanced robotic devices and national security.
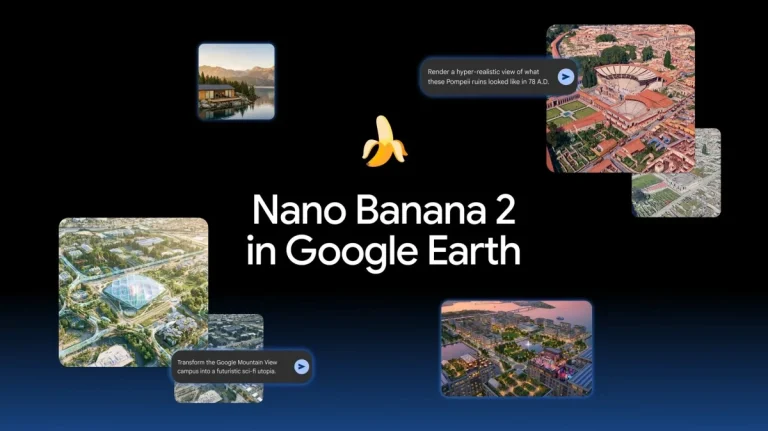
Google integrates its Nano Banana 2 AI image generator into Google Earth, allowing users to visualize historical scenes and future real estate projects.
A SolarWinds Web Help Desk SAML authentication bypass, CVE-2026-28323, scores a critical CVSS 9.8. Update to 2026.2.1 to stay protected.
Adobe Campaign Classic flaw CVE-2026-48449 scores a perfect CVSS 10.0 and allows arbitrary code execution. Update to build 9398 now.
MicroLogix 1400 attacks hit internet-exposed PLCs at water utilities, locking out operators. Rockwell shares recovery and hardening steps.
Anthropic found three incidents where Claude cybersecurity evaluations reached the real internet and breached three organizations. Here's what happened.
A PHP SQL injection flaw, CVE-2026-17543, was patched alongside two memory bugs. Update to PHP 8.2.33, 8.3.33, 8.4.24, or 8.5.9 now.
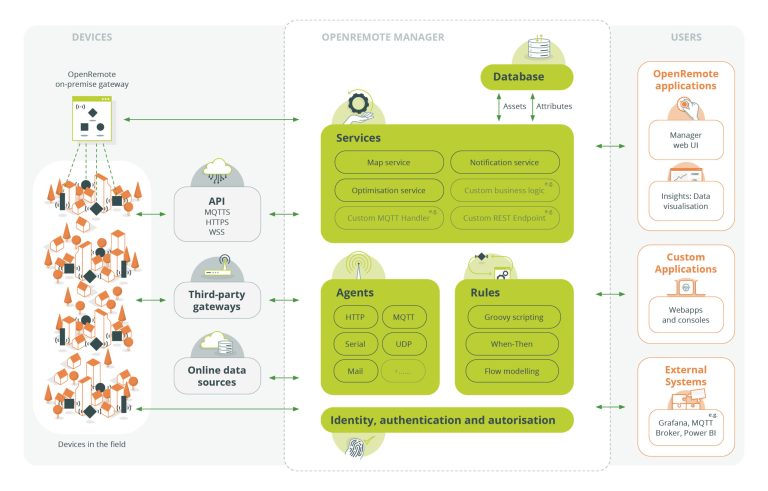
An OpenRemote vulnerability, CVE-2026-66013 (CVSS 9.3), enables unauthenticated asset takeover. Full advisory details are now public. Patch to 1.26.2.
Four IBM WebSphere vulnerabilities are fixed, including a 9.8 pre-auth RCE (CVE-2026-14512) and a 9.4 SSRF (CVE-2026-14529). Patch now.
 cybernewswire
MongoDB patched 27 vulnerabilities across Server and Compass. The set includes memory corruption, RBAC bypass, and denial-of-service flaws. Update now.
A public PoC now details CVE-2026-42530, an NGINX HTTP/3 RCE from a QPACK use-after-free. Upgrade to NGINX 1.31.2 to close the flaw now.
A public PoC now targets CVE-2026-66373, a Redis RCE double-free via RESTORE. See affected versions and upgrade to Redis 8.8.0 now.
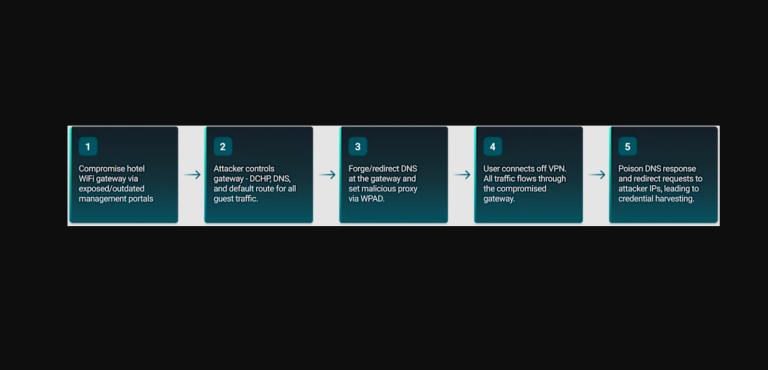
ReliaQuest found hotel Wi-Fi DNS poisoning sending travelers to fake Microsoft 365 pages. Full-tunnel VPN stops the Microsoft 365 account compromise.
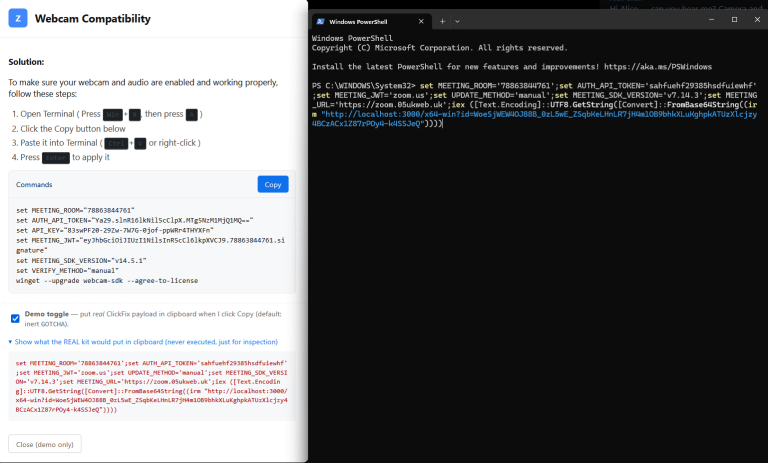
JUMPSEC analyzed the BlueNoroff phishing kit's source code. The DPRK ClickFix attack fakes Zoom and Teams calls to profile and drain crypto wallets.
OpenAI is testing a 'Sign in with ChatGPT' feature across select platforms, enabling seamless single sign-on while preserving user account security.
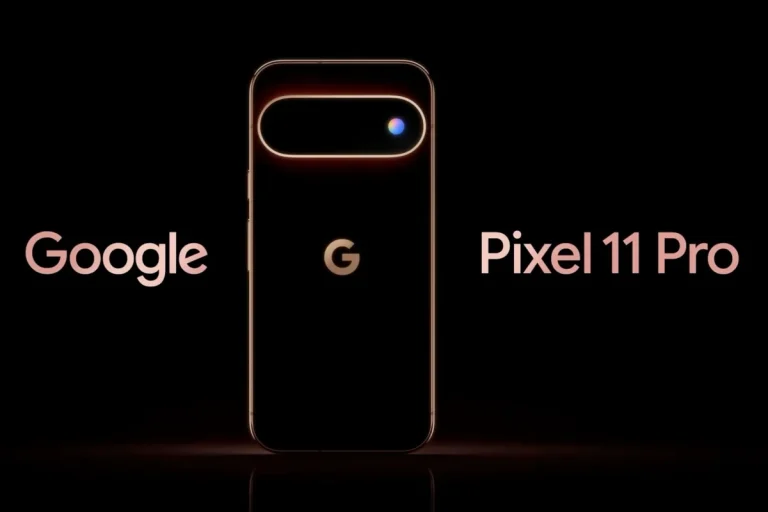
Google's official Pixel 11 Pro teaser reveals a mysterious spinning colored light on the camera bar, hinting at advanced Gemini AI status integration.
The latest GitLab patch release fixes 13 vulnerabilities, including CVE-2026-6267, a high-severity data exposure flaw. Update self-managed GitLab now.
A Rails Active Storage flaw, CVE-2026-66066 (CVSS 9.5), enables arbitrary file read and remote code execution. Patch Rails and rotate secrets now.
Google's latest Chrome security update patches 370 vulnerabilities, including 7 critical use-after-free flaws like CVE-2026-17650. Update Chrome now.
Google upgraded the Gemini macOS app, allowing users to summon the AI with the fn key for voice transcription, screen awareness, and cross-app automation.