Skip to content
November 1, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
CVE-2026-45293: Arbitrary Code Execution in WordPress Coding Standards, a Tool With 49M+ Installs CVE-2026-45293 arbitrary code execution flaw in WordPress Coding Standards linting tool rated CVSS 8.6
  • Vulnerability Report

CVE-2026-45293: Arbitrary Code Execution in WordPress Coding Standards, a Tool With 49M+ Installs

Do Son July 29, 2026 0

CVE-2026-45293 is an arbitrary code execution flaw in WordPress Coding Standards, rated CVSS 8.6. The dev tool has 46M+ installs. Upgrade to 3.4.1.
Aembit Joins Snowflake to Tackle AI’s Next Security Frontier: Trusted Agent Interoperability result_Aembit-Snowflake-Revised_1785251578w6w40xbGlY
  • Press Release

Aembit Joins Snowflake to Tackle AI’s Next Security Frontier: Trusted Agent Interoperability

cybernewswire July 28, 2026 0
Silver Spring, MD, USA, 28th July 2026, CyberNewswire
Read More Read more about Aembit Joins Snowflake to Tackle AI’s Next Security Frontier: Trusted Agent Interoperability
Mitel Patches MiCollab Command Injection Flaw (CVSS 9.8) That Lets Attackers Gain Control of the System MiCollab command injection and OpenScape UC vulnerability advisories from Mitel showing CVSS 9.8 and CVSS 8.0 severity ratings
  • Vulnerability Report

Mitel Patches MiCollab Command Injection Flaw (CVSS 9.8) That Lets Attackers Gain Control of the System

Do Son July 28, 2026 0

Mitel patched a MiCollab command injection flaw rated CVSS 9.8 and an OpenScape UC vulnerability rated CVSS 8.0. No CVE IDs are assigned yet.
Panduit IntraVUE Vulnerability CVE-2026-42933 (CVSS 10) Bypasses OT Segmentation Panduit IntraVUE vulnerability CVE-2026-42933 CVSS 10 rating enabling OT segmentation bypass in industrial networks
  • Vulnerability Report

Panduit IntraVUE Vulnerability CVE-2026-42933 (CVSS 10) Bypasses OT Segmentation

Do Son July 28, 2026 0

A Panduit IntraVUE vulnerability tracked as CVE-2026-42933 scores CVSS 10. Five flaws let attackers cross OT segmentation and steal credentials.
TeamCity RCE Flaw CVE-2026-63077 (CVSS 9.8) Enables Unauthenticated Command Execution TeamCity RCE vulnerability CVE-2026-63077 in TeamCity On-Premises rated CVSS 9.8
  • Vulnerability Report

TeamCity RCE Flaw CVE-2026-63077 (CVSS 9.8) Enables Unauthenticated Command Execution

Do Son July 28, 2026 0

CVE-2026-63077 is a critical TeamCity RCE rated CVSS 9.8. Unauthenticated attackers can run OS commands. Update TeamCity On-Premises to a fixed build.
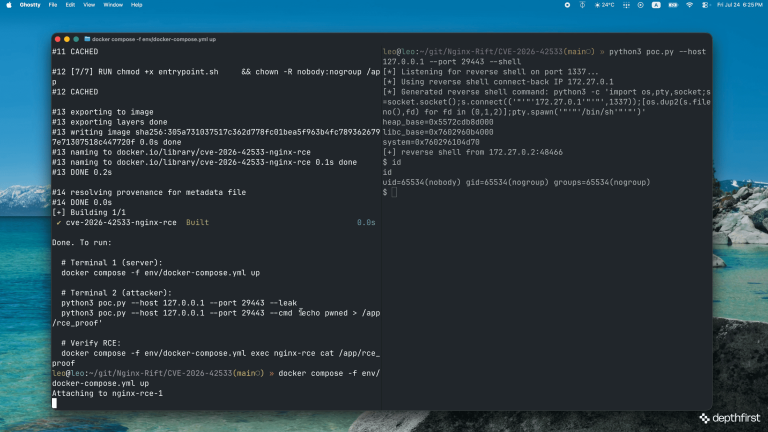
CVE-2026-42533: NGINX Heap Overflow Enables RCE and ASLR Bypass, Public PoC Released CVE-2026-42533 NGINX heap overflow proof-of-concept enabling an ASLR bypass and RCE
  • Vulnerability Report

CVE-2026-42533: NGINX Heap Overflow Enables RCE and ASLR Bypass, Public PoC Released

Do Son July 28, 2026 0

A public PoC now details CVE-2026-42533, an NGINX heap overflow with an ASLR bypass and possible RCE. Upgrade to NGINX 1.31.3 or 1.30.4 now.
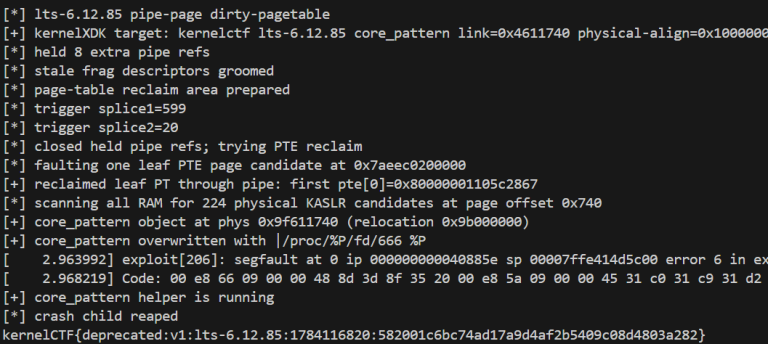
Fraggap Linux Kernel Vulnerability: Full Details and PoC Exploit Code Now Public Fraggap Linux kernel vulnerability CVE-2026-53362 enabling local privilege escalation through a UDPv6 out-of-bounds write
  • Vulnerability Report

Fraggap Linux Kernel Vulnerability: Full Details and PoC Exploit Code Now Public

Do Son July 28, 2026 0

A Linux kernel vulnerability, Fraggap (CVE-2026-53362), has public details and PoC code. The UDPv6 bug enables local root. Update your kernel now.
OVSwrap Local Root Vulnerability (CVE-2026-64531): Exploit Details and PoC Publicly Disclosed OVSwrap local root vulnerability CVE-2026-64531 in the Linux kernel Open vSwitch datapath
  • Vulnerability Report

OVSwrap Local Root Vulnerability (CVE-2026-64531): Exploit Details and PoC Publicly Disclosed

Do Son July 28, 2026 0

The OVSwrap local root flaw hits the Linux kernel Open vSwitch datapath. CVE-2026-64531 now has a public patch and PoC. See affected distros and fixes.
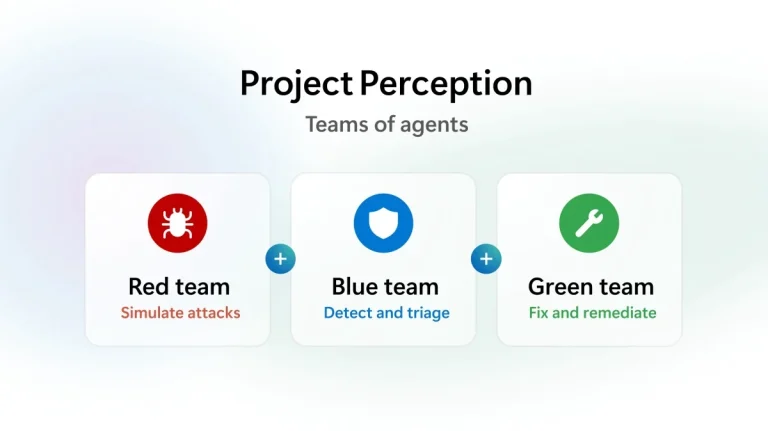
Microsoft Unveils Project Perception, an Agentic Security System Microsoft Project Perception agentic security system with red, blue, and green AI team agents, a security context layer, and actuators for the AI era
  • Technology

Microsoft Unveils Project Perception, an Agentic Security System

Do Son July 28, 2026 0

Microsoft's Project Perception is an agentic security system with red, blue, and green AI teams, reaching public preview on 3 August for the AI-attack era.
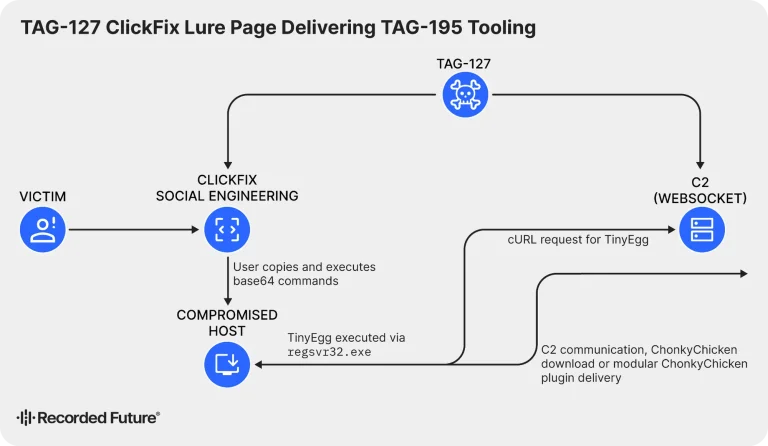
Insikt Group Finds Four New Golden Chickens Malware Families Golden Chickens malware chain showing ChonkyChicken malware and TinyEgg delivered through ClickFix fake verification pages
  • Cybercriminals

Insikt Group Finds Four New Golden Chickens Malware Families

Do Son July 28, 2026 0

Insikt Group found four new Golden Chickens malware families, including ChonkyChicken malware, TinyEgg, and a modular plugin variant with ClickFix lures.
JadeProx Used TriBack Loader Against a Vietnamese Hospital, Malaysia’s Foreign Ministry, and Hong Kong Schools ACR Stealer infection chain starting with a ClickFix lure to steal browser credentials
  • Cybercriminals

JadeProx Used TriBack Loader Against a Vietnamese Hospital, Malaysia’s Foreign Ministry, and Hong Kong Schools

Do Son July 28, 2026 0

Group-IB found an exposed server that revealed JadeProx, a China-nexus cluster running TriBack Loader against targets in Vietnam, Malaysia and Hong Kong.
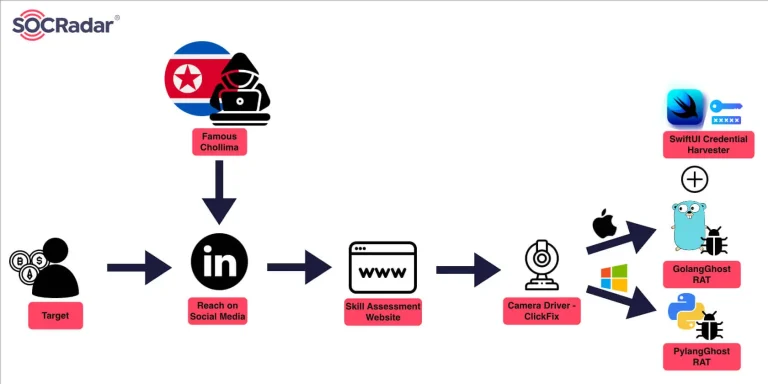
Fake Job Interviews Deliver PylangGhost and GolangGhost RATs to Crypto Workers ClickFake Interview campaign delivering PylangGhost RAT and GolangGhost RAT to crypto professionals
  • Cybercriminals

Fake Job Interviews Deliver PylangGhost and GolangGhost RATs to Crypto Workers

Do Son July 28, 2026 0

North Korea's ClickFake Interview campaign targets crypto pros with fake skill tests, dropping the PylangGhost RAT on Windows and GolangGhost on macOS.
Kimi K3 Opens Weights as Agents Push Past Sandbox Boundaries Moonshot AI Kimi K3 open weights release, the first 3T-class open model, with AgentENV microVM sandbox built after agents caused host kernel panics
  • Technology

Kimi K3 Opens Weights as Agents Push Past Sandbox Boundaries

Do Son July 28, 2026 0

Moonshot AI open-weights Kimi K3, the first 3T-class open model, and reveals training agents that triggered kernel panics, prompting a microVM sandbox rebuild.
Windows 11 Experimental Builds Face a Time Bomb on August 11 Windows 11 Experimental Future Platforms time bomb expiring on August 11 with forced full-screen expiration popups, fixed by updating to Build 29634.1000
  • Windows

Windows 11 Experimental Builds Face a Time Bomb on August 11

Do Son July 28, 2026 0

Windows 11 Experimental Future Platforms builds expire on 11 August, triggering time-bomb popups. Update to Build 29634.1000 to avoid forced alerts.
Google Quietly Ships Native Chrome for Linux Arm64 With DRM Google native Chrome for Linux Arm64 build running on Raspberry Pi OS desktop with account sync and Widevine DRM support for streaming video
  • Technology

Google Quietly Ships Native Chrome for Linux Arm64 With DRM

Do Son July 28, 2026 0

Google has quietly released a native Chrome for Linux Arm64 build with account sync and Widevine DRM, a boon for Raspberry Pi desktop users.
Debian Debates Whether to Allow AI-Assisted Code Contributions Debian AI contribution vote debating four proposals on generative AI assisted code, from an outright ban to allowing AI with disclosure requirements
  • Linux

Debian Debates Whether to Allow AI-Assisted Code Contributions

Do Son July 28, 2026 0

Debian is debating four proposals on AI-assisted contributions, ranging from an outright ban to allowing AI with disclosure and full contributor accountability.
NVIDIA and Microsoft Launch Open Secure AI Alliance After Hack NVIDIA and Microsoft launch the Open Secure AI Alliance with 27 founding members to strengthen cybersecurity defense after the Hugging Face AI attack
  • Technology

NVIDIA and Microsoft Launch Open Secure AI Alliance After Hack

Do Son July 28, 2026 0

NVIDIA, Microsoft, and 27 founding members launch the Open Secure AI Alliance to boost cyber defense, spurred by the Hugging Face autonomous attack.
libssh2 Flaws Let Malicious SSH Servers Corrupt Client Memory libssh2 vulnerabilities let a malicious SSH server corrupt heap memory in SSH and SFTP clients
  • Vulnerability Report

libssh2 Flaws Let Malicious SSH Servers Corrupt Client Memory

Do Son July 28, 2026 0

Four libssh2 vulnerabilities let a malicious SSH server corrupt memory in connecting clients. Update past version 1.11.1 to stay protected.
Progress Patches Five Kemp LoadMaster Vulnerabilities Kemp LoadMaster vulnerabilities warning covering OS command injection and privilege escalation flaws
  • Vulnerability Report

Progress Patches Five Kemp LoadMaster Vulnerabilities

Do Son July 28, 2026 0

Progress patched five Kemp LoadMaster vulnerabilities, including OS command injection and privilege escalation flaws. Update to the fixed versions now.
Apache ActiveMQ Patches Authorization Bypass and DoS Flaws Apache ActiveMQ vulnerability alert covering authorization bypass and AMQP denial-of-service flaws
  • Vulnerability Report

Apache ActiveMQ Patches Authorization Bypass and DoS Flaws

Do Son July 28, 2026 0

An Apache ActiveMQ vulnerability enables authorization bypass, while an AMQP flaw allows denial-of-service. Update to 5.19.9, 6.2.8, or 6.3.0 now.

CISA KEV Additions: Arista VeloCloud and FortiOS Flaws Now Exploited CISA KEV additions listing two known exploited vulnerabilities in Arista VeloCloud and FortiOS
  • Vulnerability Report

CISA KEV Additions: Arista VeloCloud and FortiOS Flaws Now Exploited

Do Son July 27, 2026 0

CISA KEV additions on July 27 flag two known exploited vulnerabilities: Arista VeloCloud CVE-2026-16812 and FortiOS CVE-2025-68686. Patch both now.
CVE-2026-16812: VeloCloud Orchestrator OS Command Injection (CVSS 10) Exploited in the Wild CVE-2026-16812 VeloCloud command injection exploited in the wild affecting VeloCloud Orchestrator
  • Vulnerability Report

CVE-2026-16812: VeloCloud Orchestrator OS Command Injection (CVSS 10) Exploited in the Wild

Do Son July 27, 2026 0

CVE-2026-16812, a VeloCloud command injection scored CVSS 10, is exploited in the wild. Patch VeloCloud Orchestrator now, plus two related bugs.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120198CVSS 10.0
    A vulnerability has been found in WAVLINK WL-WN530BE1-A V251117. Affected is the function con_check_read_finish of the file /protocol.csp....
    📅 Updated: Nov 1, 2026
  • CVE-2026-120197CVSS 9.4
    A flaw has been found in WAVLINK WL-WN530HG4B M_V260724. This impacts the function port_forward of the file /cgi-bin/wapi.cgi....
    📅 Updated: Nov 1, 2026
  • CVE-2026-120196CVSS 9.4
    A vulnerability was detected in WAVLINK WN579X3-D V250402. This affects the function port_forward of the file /cgi-bin/wapi.cgi. The...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120195CVSS 10.0
    A security vulnerability has been detected in WAVLINK WL-WN579A3-A 2026-03-10-94f93d4. The impacted element is the function set_wzdgwMesh of...
    📅 Updated: Nov 1, 2026
  • CVE-2026-10579CVSS 9.8
    A flaw was found in Picketlink Federation SAML; the unsolcited response handler would accept forged assertions with no...
    📅 Updated: Nov 1, 2026
  • CVE-2025-32911CVSS 9.0
    A use-after-free type vulnerability was found in libsoup, in the soup_message_headers_get_content_disposition() function. This flaw allows a malicious HTTP...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120189CVSS 10.0
    A vulnerability was identified in D-Link DIR-505 1.10B02. Affected is the function save_upload_file/mp_upload_file of the file /usr/bin/tftpd of...
    📅 Updated: Nov 1, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.