Skip to content
November 1, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
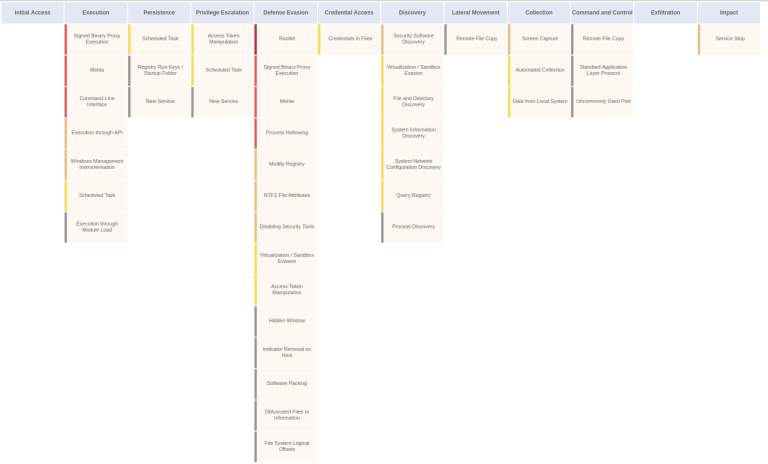
VMRay Exposes Operation STANDOFF, a Russian-Speaking Intrusion Campaign Hidden Behind GitHub Operation STANDOFF infrastructure map showing a Russian-speaking threat group hiding C2 servers behind GitHub redirects
  • Cybercriminals

VMRay Exposes Operation STANDOFF, a Russian-Speaking Intrusion Campaign Hidden Behind GitHub

Do Son July 27, 2026 0

VMRay Labs details Operation STANDOFF, a Russian-speaking threat group running malware, a proxy-botnet and AI influence tools behind fake GitHub traffic.
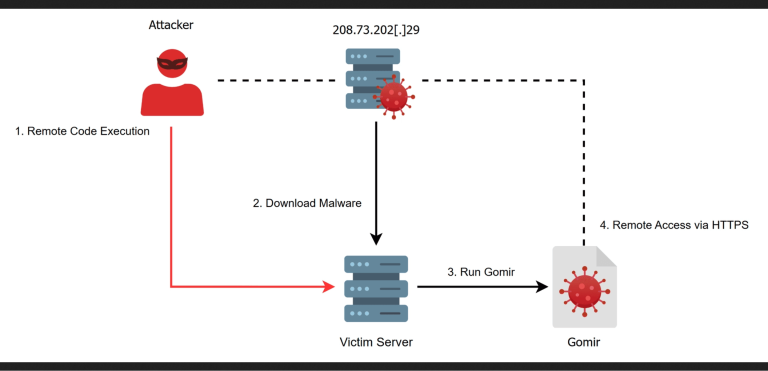
Kimsuky Hacked South Korean Groupware Vendors With New Gomir Variants Kimsuky Gomir variant attack chain showing the DriveTroy backdoor using Google Drive as a covert C2 channel
  • Cybercriminals

Kimsuky Hacked South Korean Groupware Vendors With New Gomir Variants

Do Son July 27, 2026 0

ENKI WhiteHat traced a Kimsuky Gomir variant into South Korean groupware vendors, plus a new DriveTroy backdoor that hides its C2 in Google Drive.
Security Risk Advisors Named a Finalist in CRN’s 2026 Best of the Channel Awards Joe_Channel_Awards_2_1785157894FHsYNffOlZ
  • Press Release

Security Risk Advisors Named a Finalist in CRN’s 2026 Best of the Channel Awards

cybernewswire July 27, 2026 0
Philadelphia, Pennsylvania, 27th July 2026, CyberNewswire
Read More Read more about Security Risk Advisors Named a Finalist in CRN’s 2026 Best of the Channel Awards
Unpatched Plane Authorization Bypass CVE-2026-15342 Exposes Other Workspaces Plane authorization bypass CVE-2026-15342 exposing multi-tenant workspace assets
  • Vulnerability Report

Unpatched Plane Authorization Bypass CVE-2026-15342 Exposes Other Workspaces

Do Son July 27, 2026 0

CERT/CC warns of a Plane authorization bypass, CVE-2026-15342. It lets users reach other workspaces' files, and no patch exists yet.
Apache Fory Patches Four Deserialization Flaws Across Java, C++, and Rust Apache Fory vulnerabilities in Java, C++, and Rust deserialization fixed in version 1.4.0
  • Vulnerability Report

Apache Fory Patches Four Deserialization Flaws Across Java, C++, and Rust

Do Son July 27, 2026 0

Apache Fory vulnerabilities hit Java, C++, and Rust deserialization, including CVE-2026-64606. Upgrade to Fory 1.4.0 to fix all four flaws.
CVE-2026-61511: vBulletin Preauth RCE with Public PoC Disclosed CVE-2026-61511 vBulletin preauth RCE proof-of-concept abusing the runMaths eval for remote code execution
  • Vulnerability Report

CVE-2026-61511: vBulletin Preauth RCE with Public PoC Disclosed

Do Son July 27, 2026 0

A public PoC now targets CVE-2026-61511, a vBulletin preauth RCE via runMaths eval. Patch to vBulletin 6.2.2 to block remote code execution.

TELESHIM Malware Targets Middle East Governments Through Telegram SonicWall Reconnaissance Akira Ransomware residential proxy malware TraderTraitor BreachForums Honeypot, French Interior Ministry Leak
  • Cybercriminals

TELESHIM Malware Targets Middle East Governments Through Telegram

Do Son July 27, 2026 0

TELESHIM malware hits Middle East governments and abuses Telegram C2 to hide traffic. Zscaler ThreatLabz found the new backdoor and its tooling.
RenPy Loader Spreads Amatera Stealer Through Fake Game Downloads RenPy Loader infection chain in fake game installers using MSBuild and EtherHiding to deploy Amatera Stealer
  • Malware

RenPy Loader Spreads Amatera Stealer Through Fake Game Downloads

Do Son July 27, 2026 0

Malwarebytes finds fake games spreading Amatera Stealer through RenPy Loader, MSBuild abuse, and EtherHiding C2. See the infection chain and defenses.
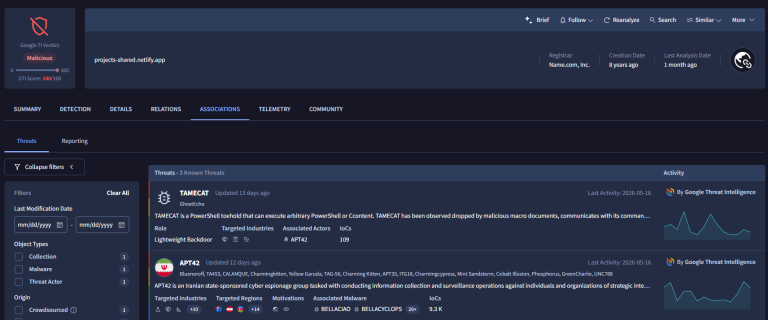
APT42 TAMECAT Malware Grows with AI-Assisted Phishing Tamecat
  • Cybercriminals

APT42 TAMECAT Malware Grows with AI-Assisted Phishing

Do Son July 27, 2026 0

APT42 TAMECAT malware now blends AI-assisted phishing with cloud C2 to steal credentials from defense and nuclear-sector targets.
Google AI Overviews Traffic Loss Drives Publisher Backlash Google AI Overviews traffic decline chart and publisher organic search impact
  • Technology

Google AI Overviews Traffic Loss Drives Publisher Backlash

Do Son July 27, 2026 0

Prominent publishers re-evaluate Google partnerships as Google AI Overviews traffic decline severely impacts organic search referrals and audience growth.
Samsung One UI 9 Locks the Phone Forever After 13 Wrong Codes Samsung One UI 9 lockscreen security on Android 17 permanently locks the device after 13 failed passcode attempts, requiring a factory reset
  • Android

Samsung One UI 9 Locks the Phone Forever After 13 Wrong Codes

Do Son July 27, 2026 0

Samsung One UI 9 permanently locks a phone after 13 wrong passcodes, forcing a factory reset. Accidental lockouts remain very unlikely by design.
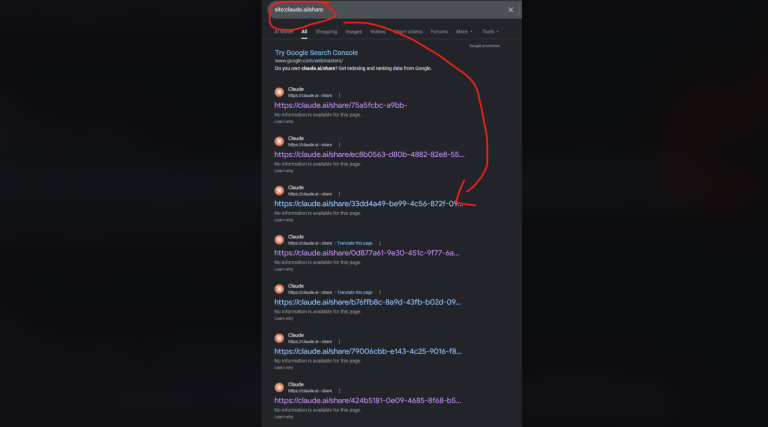
Claude AI Shared Chats Surfaced in Google Over a Config Error Claude AI shared conversation links indexed in Google search due to a robots.txt and X-Robots-Tag misconfiguration exposing private chat content
  • Data Leak

Claude AI Shared Chats Surfaced in Google Over a Config Error

Do Son July 27, 2026 0

Claude AI shared conversation links were indexed by Google due to a config error, exposing some chats with private data. Delete sensitive shares now.
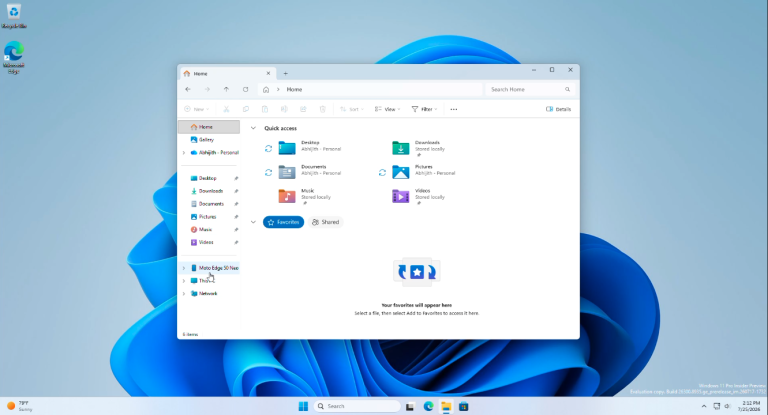
Windows 11 File Explorer Now Deletes Large Fragmented Files Faster Windows 11 File Explorer faster deletion of large fragmented files in Build 26300.8935, a rare NTFS performance win from Microsoft
  • Windows

Windows 11 File Explorer Now Deletes Large Fragmented Files Faster

Do Son July 27, 2026 0

Windows 11 Build 26300.8935 speeds up deleting large, heavily fragmented files in File Explorer, a rare performance win rolling out gradually.
Intel to Bring Back Hyper-Threading in 2028 Coral Rapids Xeon Intel hyper-threading return in 2028 Coral Rapids Xeon server CPUs announced by CEO Lip-Bu Tan to reclaim data center CPU market share
  • Technology

Intel to Bring Back Hyper-Threading in 2028 Coral Rapids Xeon

Do Son July 27, 2026 0

Intel will revive hyper-threading in its 2028 Coral Rapids Xeon server CPUs, CEO Lip-Bu Tan said, as it fights to reclaim CPU market share.
EU Says TikTok Breaches DSA Rules on Protecting Minors’ Privacy EU preliminary findings accuse TikTok of breaching DSA minor-safety rules over public-by-default accounts and For You algorithmic recommendation
  • Technology

EU Says TikTok Breaches DSA Rules on Protecting Minors’ Privacy

Do Son July 27, 2026 0

The EU's preliminary findings accuse TikTok of breaching DSA minor-safety rules through public-by-default accounts and For You algorithmic exposure.
Qualcomm Announces Double-Digit Chip Price Increase Qualcomm chip price increase notification letter to OEM customers
  • Technology

Qualcomm Announces Double-Digit Chip Price Increase

Do Son July 27, 2026 0

Qualcomm notifies clients of double-digit chip price hikes starting September 2026, impacting Android smartphones and wearable technology.
Weekly Threat Intelligence Briefing: Late July 2026 CISA flagged 6 actively exploited CVEs this week, from a SharePoint RCE to a Check Point auth bypass. See the full CISA KEV list and patch fast.
  • Weekly Recap

Weekly Threat Intelligence Briefing: Late July 2026

Do Son July 27, 2026 0

Read our latest weekly threat intelligence briefing. This active vulnerability update reveals critical Microsoft Exchange and Oracle flaws for July 2026.
CVE-2026-49176 Windows WalletService Elevation of Privilege Flaw Gets Public PoC Exploit CVE-2026-49176 Windows WalletService elevation of privilege exploit escalating to SYSTEM
  • Vulnerability Report

CVE-2026-49176 Windows WalletService Elevation of Privilege Flaw Gets Public PoC Exploit

Do Son July 27, 2026 0

CVE-2026-49176 is a Windows WalletService elevation of privilege flaw. Full details and a public PoC exploit are out, so patch Windows now.

Cruciferra Crypter Service Cloaks RATs and Infostealers for Many Threat Actors Kali365 phishing platform EmEditor Supply Chain Attack, WALSHAM INVESTMENTS LIMITED EggStreme, fileless malware North Korea Cybercrime, Remote IT Job Fraud RedDelta APT
  • Malware

Cruciferra Crypter Service Cloaks RATs and Infostealers for Many Threat Actors

Do Son July 27, 2026 0

Proofpoint details the Cruciferra crypter service that cloaks RATs and infostealers using BYOVD EDR tampering and 90+ custom encryption routines.
The Operational Systems That Protect Private Jet Passengers tech-pass
  • Technique

The Operational Systems That Protect Private Jet Passengers

Do Son July 27, 2026 0

Discover the operational systems that protect private jet passengers, from pilot training and aircraft maintenance to safety management systems, flight planning, and risk assessment procedures.
Microsoft Fortifies KMS Activation with TPM Hardware Trust Microsoft China AI business growth via OpenAI and ByteDance partnership
  • Technology

Microsoft Fortifies KMS Activation with TPM Hardware Trust

Do Son July 26, 2026 0

Discover how Microsoft is strengthening KMS activation by introducing hardware-based trust and TPM verification to combat forged licensing servers.
Google Weighs Restricting Local ADB, Threatening Shizuku on Android Google proposal to restrict local ADB loopback connections on Android, potentially breaking Shizuku and aShell no-root tools over security concerns
  • Android

Google Weighs Restricting Local ADB, Threatening Shizuku on Android

Do Son July 26, 2026 0

Google engineers propose restricting local ADB loopback connections on Android to close a security gap, a change that could break Shizuku and aShell.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120198CVSS 10.0
    A vulnerability has been found in WAVLINK WL-WN530BE1-A V251117. Affected is the function con_check_read_finish of the file /protocol.csp....
    📅 Updated: Nov 1, 2026
  • CVE-2026-120197CVSS 9.4
    A flaw has been found in WAVLINK WL-WN530HG4B M_V260724. This impacts the function port_forward of the file /cgi-bin/wapi.cgi....
    📅 Updated: Nov 1, 2026
  • CVE-2026-120196CVSS 9.4
    A vulnerability was detected in WAVLINK WN579X3-D V250402. This affects the function port_forward of the file /cgi-bin/wapi.cgi. The...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120195CVSS 10.0
    A security vulnerability has been detected in WAVLINK WL-WN579A3-A 2026-03-10-94f93d4. The impacted element is the function set_wzdgwMesh of...
    📅 Updated: Nov 1, 2026
  • CVE-2026-10579CVSS 9.8
    A flaw was found in Picketlink Federation SAML; the unsolcited response handler would accept forged assertions with no...
    📅 Updated: Nov 1, 2026
  • CVE-2025-32911CVSS 9.0
    A use-after-free type vulnerability was found in libsoup, in the soup_message_headers_get_content_disposition() function. This flaw allows a malicious HTTP...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120189CVSS 10.0
    A vulnerability was identified in D-Link DIR-505 1.10B02. Affected is the function save_upload_file/mp_upload_file of the file /usr/bin/tftpd of...
    📅 Updated: Nov 1, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.