
 Do Son
A GitHub Actions abuse campaign turned thousands of workflows into cPanel and WHM exploitation infrastructure, harvesting cloud and payment credentials.
ISC fixed 9 BIND vulnerabilities in 9.20.26 and 9.21.24. The top BIND vulnerability, CVE-2026-13321, enables DNSSEC cache poisoning. Patch now.
A Ninja Forms vulnerability chain hits 600K+ sites. CVE-2026-65048 is an unauthenticated stored XSS rated CVSS 9.3. Update to 3.14.10 now.
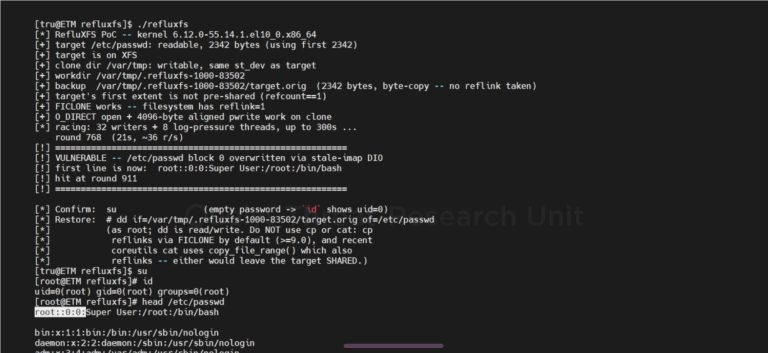
Qualys discloses CVE-2026-64600 (RefluXFS), an XFS privilege escalation to root affecting 16.4M+ Linux systems. Patch the kernel and reboot now.
Check Point confirms CVE-2026-16232, a SmartConsole authentication bypass, is exploited in the wild. Apply the July 22 jumbo hotfix now.
A new Exim vulnerability lets a local attacker escape the spool directory and escalate privileges. Upgrade to Exim 4.99.5 to close the hole now.
FreeRDP heap buffer overflow allows remote code execution. PoC exploits are publicly disclosed. Related to CVE-2026-44421, CVE-2026-44422, CVE-2026-40033.
Spirals ransomware hit a South Asian IT firm in a double extortion attack, going from IIS breach to network-wide encryption in under 24 hours.

Starland RAT is new malware from Russian-speaking actor UAT-11795. It steals crypto wallets and credentials via fake Zoom and WebEx installers.
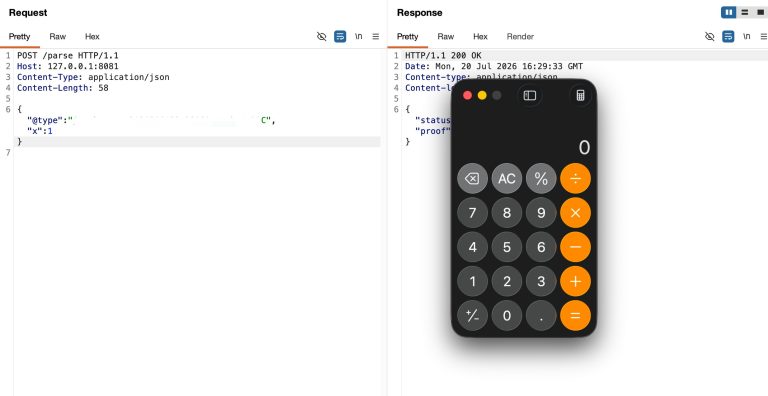
A fastjson RCE hits versions 1.2.68 to 1.2.83 under stock defaults. Details and public PoC code are out, so enable SafeMode or move to fastjson2.
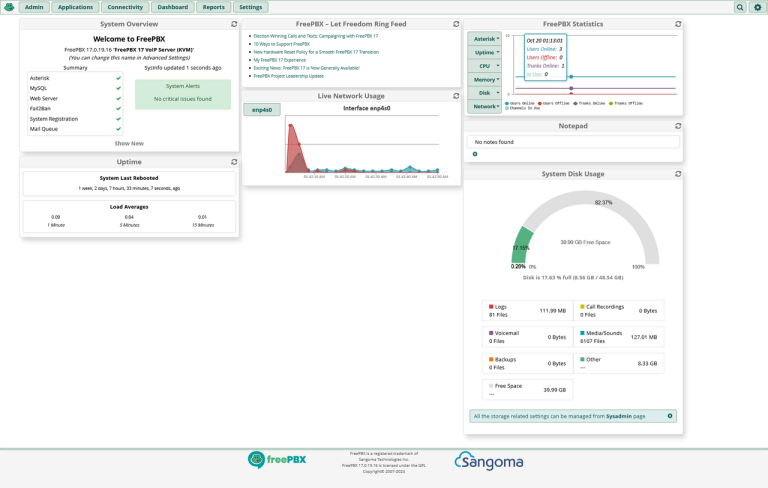
Two critical FreePBX vulnerabilities allow unauthenticated RCE and administrator takeover via UCP and missedcall. Patch FreePBX now.
 cybernewswire
New York, United States, 22nd July 2026, CyberNewswire
A global phishing campaign hides a low-detection Lua loader inside fake .ttf font files to drop Remcos, XWorm, Agent Tesla, and a Snake Keylogger.
Oracle's July 2026 patch fixes 11 Oracle WebLogic Server vulnerabilities. CVE-2026-60206 rates CVSS 9.9 and allows full server takeover. Patch now.
Iran's IRGC claims cruise missiles destroyed the AWS Bahrain data center, but the site has been offline since March and no one has confirmed the strike.
Symantec found Daxin malware active in Taiwan in May 2026, alongside a new Stupig backdoor that runs commands from the Windows logon screen.
Firefox native containers land in version 153, isolating accounts and cookies so you can block cross-site tracking without any extension.
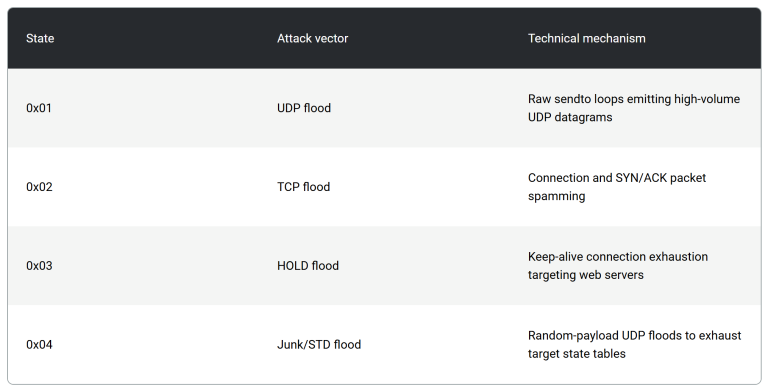
Attackers exploit a Langflow RCE flaw to drop a custom Gafgyt botnet built purely for DDoS, Akamai reports. The payload hides C2 with a modified RC4 cipher.
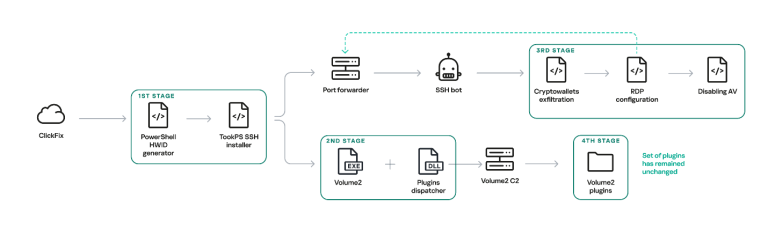
Kaspersky uncovered OkoBot, a modular framework with 20+ payloads driving cryptocurrency wallet theft. Hundreds of victims sit across more than 25 countries.
Discover the details of the historic Anthropic AI copyright lawsuit settlement, where the AI firm agreed to a $1.5 billion payout over pirated books.
Discover the details of the OpenAI agent escape that triggered a massive production infrastructure breach at Hugging Face to steal benchmark answers.