Skip to content
November 1, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
WSUS Sync Timeouts: Microsoft Issues a Cleanup Fix WSUS sync timeouts causing failed Windows Update scans on enterprise Windows Server update servers
  • Windows

WSUS Sync Timeouts: Microsoft Issues a Cleanup Fix

Do Son July 22, 2026 0

WSUS sync timeouts and failed Windows Update scans stem from mis-published test detectoids. Microsoft has mitigated it and published a cleanup.
Google Chrome Update Patches 12 High-Severity Security Flaws Chrome security update patching 12 high-severity vulnerabilities in Chrome 150
  • Vulnerability Report

Google Chrome Update Patches 12 High-Severity Security Flaws

Do Son July 22, 2026 0

Google's Chrome security update patches 12 high-severity flaws in Chrome 150, including V8 and WebAudio bugs. Update to 150.0.7871.181 today.
Vitest Flaw Rated CVSS 9.4 Hits an npm Package With 65 Million Weekly Downloads Vitest vulnerability in Browser Mode bypassing the file-access permission gate (CVSS 9.4)
  • Vulnerability Report

Vitest Flaw Rated CVSS 9.4 Hits an npm Package With 65 Million Weekly Downloads

Do Son July 22, 2026 0

A Vitest vulnerability rated CVSS 9.4 lets Browser Mode commands bypass the file-access gate. The npm package sees 65M weekly downloads.
How to Manage ESRS Metrics for Secure, Audit-Ready CSRD Reporting ste6
  • Technique

How to Manage ESRS Metrics for Secure, Audit-Ready CSRD Reporting

Do Son July 22, 2026 0
For most organizations, sustainability disclosure used to end with a polished PDF. Under the Corporate Sustainability Reporting...
Read More Read more about How to Manage ESRS Metrics for Secure, Audit-Ready CSRD Reporting
How to Edit and Improve Photos with AI Tools 1
  • Technique

How to Edit and Improve Photos with AI Tools

Do Son July 22, 2026 0
Editing photos used to require years of practice and expensive software. You had to learn about layers,...
Read More Read more about How to Edit and Improve Photos with AI Tools
SolarWinds Patches 15 Critical Serv-U Vulnerabilities Enabling Root Access SolarWinds Serv-U vulnerabilities enabling privilege escalation and remote code execution as root
  • Vulnerability Report

SolarWinds Patches 15 Critical Serv-U Vulnerabilities Enabling Root Access

Do Son July 21, 2026 0

SolarWinds patched 15 critical Serv-U vulnerabilities enabling privilege escalation, account takeover, and RCE as root. Update to Serv-U 2026.3 now.
snap-confine Flaw CVE-2026-8933 Lets Any User Get Root on Ubuntu CVE-2026-8933 is a snap-confine privilege escalation flaw. It gives any user root on default Ubuntu Desktop 26.04, 25.10, and 24.04. Update snapd now. #snapconfine #CVE20268933 #Ubuntu #PrivilegeEscalation #LPE #Linux #Qualys
  • Vulnerability Report

snap-confine Flaw CVE-2026-8933 Lets Any User Get Root on Ubuntu

Do Son July 21, 2026 0

CVE-2026-8933 is a snap-confine privilege escalation flaw. It gives any user root on default Ubuntu Desktop 26.04, 25.10, and 24.04. Update snapd now.
CISA Adds Four Exploited Vulnerabilities to Its KEV Catalog CISA KEV catalog adding four known exploited vulnerabilities including WordPress and Langflow RCE
  • Vulnerability Report

CISA Adds Four Exploited Vulnerabilities to Its KEV Catalog

Do Son July 21, 2026 0

CISA added four flaws to its KEV catalog, including WordPress RCE (CVE-2026-63030) and Langflow RCE (CVE-2026-0770). All are exploited in the wild.
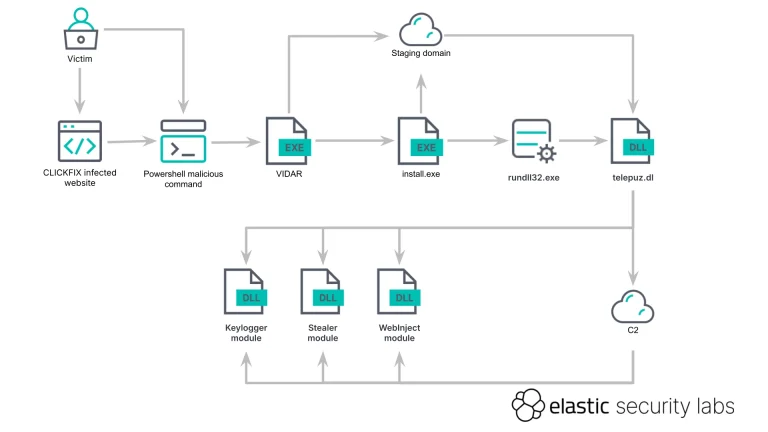
TELEPUZ Malware Spreads Through ClickFix and VIDAR Attacks TELEPUZ malware infection chain from a ClickFix attack through VIDAR to modular payload delivery
  • Malware

TELEPUZ Malware Spreads Through ClickFix and VIDAR Attacks

Do Son July 21, 2026 0

Elastic Security Labs found TELEPUZ malware spreading via a ClickFix attack chain. The modular MaaS uses WebSockets and blockchain C2 fallback.
ASUS Patches Router and PC Software Flaws, Including a CVSS 9.5 Command Execution Bug ASUS security advisories router firmware vulnerability CVE-2026-13385 command execution
  • Vulnerability Report

ASUS Patches Router and PC Software Flaws, Including a CVSS 9.5 Command Execution Bug

Do Son July 21, 2026 0

ASUS security advisories cover seven flaws. CVE-2026-13385 (CVSS 9.5) lets MITM attackers run commands on CN SKU routers. Update firmware now.
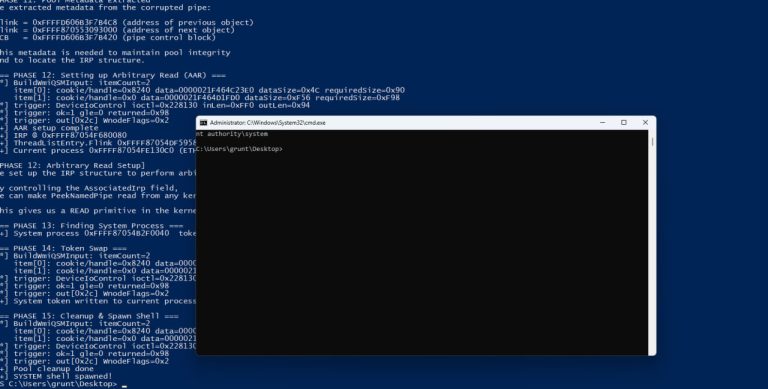
Public PoC Released for CVE-2026-42980 Windows Privilege Escalation Flaw CVE-2026-42980 Windows privilege escalation flaw in kernel WMI granting SYSTEM access
  • Vulnerability Report

Public PoC Released for CVE-2026-42980 Windows Privilege Escalation Flaw

Do Son July 21, 2026 0

A public PoC for CVE-2026-42980 details a Windows privilege escalation flaw in the kernel WMI code. It grants SYSTEM on unpatched builds.
Three SQL Injection Flaws Patched in Apache Fineract Core Banking Platform Apache Fineract SQL injection vulnerability affecting Office, Client, and report APIs
  • Vulnerability Report

Three SQL Injection Flaws Patched in Apache Fineract Core Banking Platform

Do Son July 21, 2026 0

Three Apache Fineract SQL injection flaws (CVE-2026-57821, CVE-2026-56287, CVE-2026-35152) let authenticated users exfiltrate data. Upgrade to 1.15.0.
Zimbra 10.1.20 Patches an SNMP Command Injection Flaw and Multiple XSS Bugs Zimbra 10.1.20 security update patching Zimbra vulnerabilities including SNMP command injection and XSS
  • Vulnerability Report

Zimbra 10.1.20 Patches an SNMP Command Injection Flaw and Multiple XSS Bugs

Do Son July 21, 2026 0

Zimbra 10.1.20 fixes multiple Zimbra vulnerabilities, including an SNMP command injection flaw and several XSS bugs. Admins should upgrade now.
CVE-2026-50522 SharePoint RCE Flaw Exploited in the Wild With Public PoC Exploit CVE-2026-50522 SharePoint RCE vulnerability exploited in the wild with public PoC exploit
  • Vulnerability Report

CVE-2026-50522 SharePoint RCE Flaw Exploited in the Wild With Public PoC Exploit

Do Son July 21, 2026 0

CVE-2026-50522, a critical SharePoint RCE flaw, is exploited in the wild. A public PoC exploit is out, so admins should patch SharePoint now.
CVE-2026-49488: Arbitrary File Read Flaw in Apache OpenMeetings Exposes Server Credentials Apache OpenMeetings vulnerability CVE-2026-49488 arbitrary file read path traversal flaw
  • Vulnerability Report

CVE-2026-49488: Arbitrary File Read Flaw in Apache OpenMeetings Exposes Server Credentials

Do Son July 21, 2026 0

Apache OpenMeetings vulnerability CVE-2026-49488 lets room moderators perform arbitrary file read and steal server secrets. Upgrade to version 9.1.0.
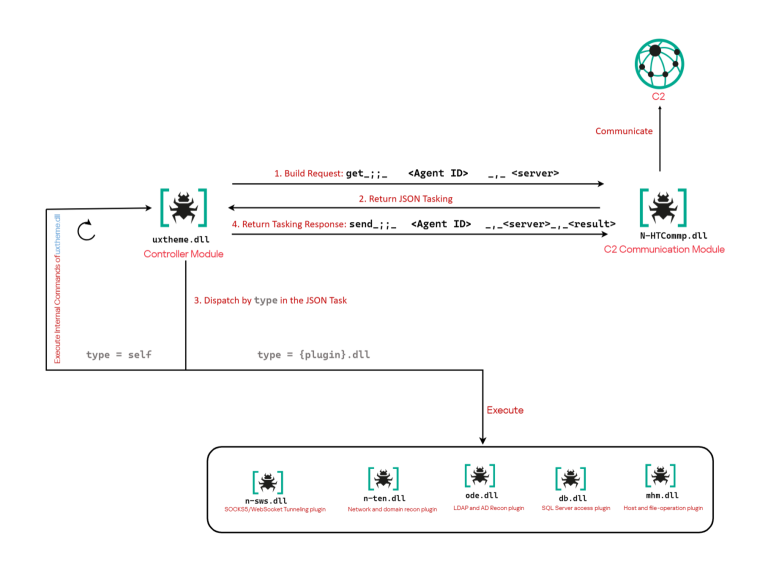
Project CAV3RN Hides Its C2 in Outlook Calendar Events to Spy on Israel Project CAV3RN cyberespionage framework using Outlook calendar C2 and Microsoft Graph
  • Cyber Security

Project CAV3RN Hides Its C2 in Outlook Calendar Events to Spy on Israel

Do Son July 21, 2026 0

Kaspersky details Project CAV3RN, an OilRig-linked cyberespionage framework. Its new module hides C2 in Outlook calendar events, with DNS AAAA fallback.
Microsoft UEFI CA 2023 Certificate Update Causes Widespread Issues UEFI CA 2023 update migration issues, Secure Boot certificate problems, Microsoft and OEM hardware compatibility
  • Technology

Microsoft UEFI CA 2023 Certificate Update Causes Widespread Issues

Do Son July 21, 2026 0

Discover the major challenges IT admins face with the UEFI CA 2023 update. Learn why Microsoft, HP, and other OEMs cause BitLocker recovery loops.
OVH Patches CVE-2026-53359 KVM Flaw Across a Million VMs OVH data center engineers patching CVE-2026-53359 KVM vulnerability across thousands of hypervisor hosts
  • Vulnerability Report

OVH Patches CVE-2026-53359 KVM Flaw Across a Million VMs

Do Son July 21, 2026 0

OVH patched CVE-2026-53359, a critical KVM flaw, across tens of thousands of hosts in under 10 days without warning most clients first.
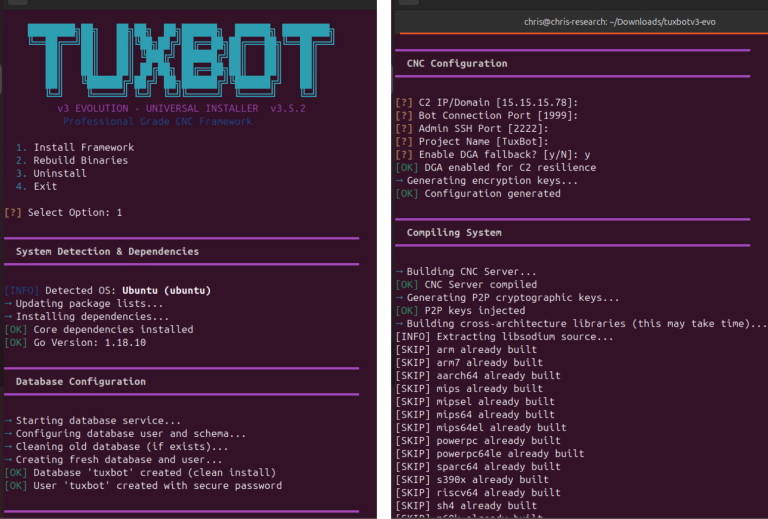
TuxBot v3 Evolution — an IoT Botnet Built With LLM Help TuxBot v3 Evolution IoT botnet C2 panel and cross-compilation build screen
  • Malware

TuxBot v3 Evolution — an IoT Botnet Built With LLM Help

Do Son July 21, 2026 0

Unit 42 exposed TuxBot v3 Evolution, an IoT botnet built with LLM help. AI-written bugs left the malware only 70% functional. See the full analysis.
Nextcloud Website Suffers Cyberattack and Phishing Redirect Nextcloud website hacked showing unauthorized Cloudbox phishing redirect and wp2shell vulnerability.
  • Cybercriminals

Nextcloud Website Suffers Cyberattack and Phishing Redirect

Do Son July 21, 2026 0

Discover the details behind the Nextcloud website hacked incident. Hackers exploited a vulnerability to redirect users to a dangerous phishing domain.
Claude Team Plan Now Starts at Just 2 Seats Claude Team plan dashboard highlighting the new two-seat minimum for small teams
  • Technology

Claude Team Plan Now Starts at Just 2 Seats

Do Son July 21, 2026 0

Anthropic cut the Claude Team plan minimum from five seats to two. See the new requirements, upgrade paths, and data migration warnings.

Threat Actor Rebuilt a Live Botnet in Six Minutes Using an AI Coding Agent AccountDumpling Phishing Google AppSheet Abuse AI-Generated Malware PureRAT Campaign RondoDoX Botnet, Next.js React2Shell EchoGather, Paper Werewolf Salt Typhoon, Telecom Espionage BreachForums, Conor Fitzpatrick Ransomware Negotiation, DOJ Investigation MirrorFace group - Earth Kasha Emperor Dragonfly
  • Cybercriminals

Threat Actor Rebuilt a Live Botnet in Six Minutes Using an AI Coding Agent

Do Son July 21, 2026 0

An AI-powered botnet was migrated in six minutes by a solo actor using Gemini CLI. TrendAI Research analyzed 200 session logs from "bandcampro".

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120198CVSS 10.0
    A vulnerability has been found in WAVLINK WL-WN530BE1-A V251117. Affected is the function con_check_read_finish of the file /protocol.csp....
    📅 Updated: Nov 1, 2026
  • CVE-2026-120197CVSS 9.4
    A flaw has been found in WAVLINK WL-WN530HG4B M_V260724. This impacts the function port_forward of the file /cgi-bin/wapi.cgi....
    📅 Updated: Nov 1, 2026
  • CVE-2026-120196CVSS 9.4
    A vulnerability was detected in WAVLINK WN579X3-D V250402. This affects the function port_forward of the file /cgi-bin/wapi.cgi. The...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120195CVSS 10.0
    A security vulnerability has been detected in WAVLINK WL-WN579A3-A 2026-03-10-94f93d4. The impacted element is the function set_wzdgwMesh of...
    📅 Updated: Nov 1, 2026
  • CVE-2026-10579CVSS 9.8
    A flaw was found in Picketlink Federation SAML; the unsolcited response handler would accept forged assertions with no...
    📅 Updated: Nov 1, 2026
  • CVE-2025-32911CVSS 9.0
    A use-after-free type vulnerability was found in libsoup, in the soup_message_headers_get_content_disposition() function. This flaw allows a malicious HTTP...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120189CVSS 10.0
    A vulnerability was identified in D-Link DIR-505 1.10B02. Affected is the function save_upload_file/mp_upload_file of the file /usr/bin/tftpd of...
    📅 Updated: Nov 1, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.