 Do Son
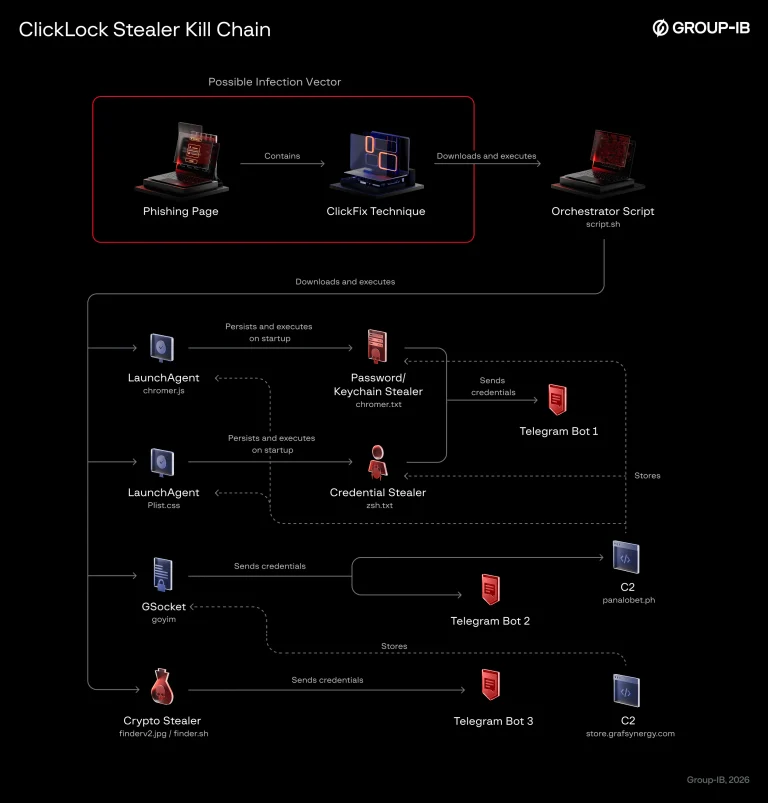
ClickLock Stealer is macOS malware that freezes your Mac until you type your password. Group-IB found 100+ victims across 33 countries.
The White House launched the GOLD EAGLE initiative for faster vulnerability coordination across U.S. critical infrastructure, using AI to patch flaws.
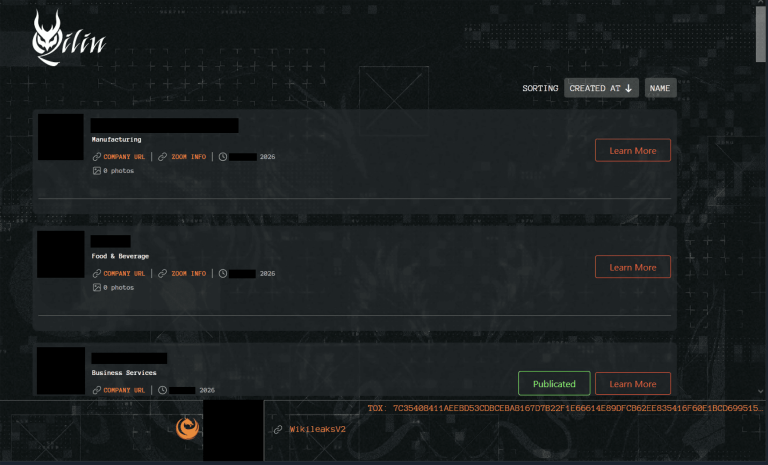
Arctic Wolf links Qilin ransomware attacks to CVE-2026-0257, a Palo Alto GlobalProtect auth bypass used for initial access. Patch PAN-OS now.
Linux kernel CVEs surged to 440 advisories in just 24 hours, with many flaws found by AI. Most are already patched, so update your kernel promptly.
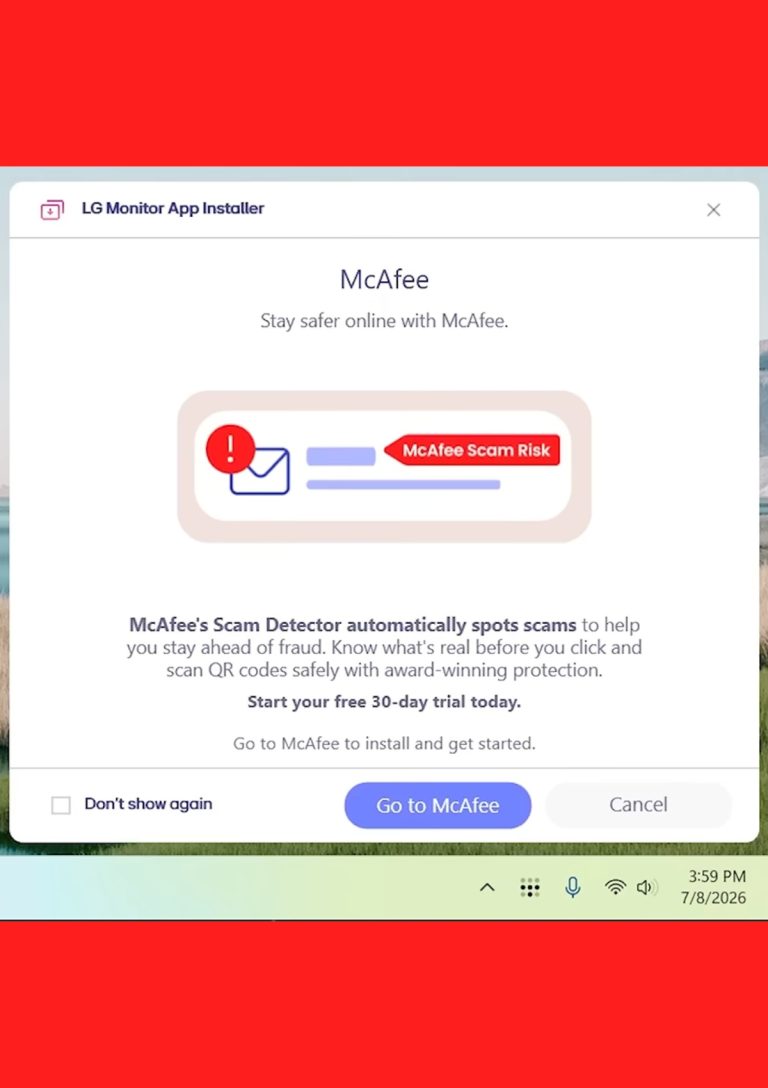
LG monitor adware installs itself via Windows device metadata and pushes McAfee pop-ups. Learn how a Group Policy tweak blocks the unwanted software.
wp2shell, a WordPress Core RCE chain (CVE-2026-63030, CVE-2026-60137), is exploited in the wild. Public PoC code is out. Patch WordPress now.

The logistics industry has undergone an incredible change over the last decade. Increasing customer demand, global supply...
The US seized 1,000+ domains in an illegal World Cup streaming crackdown, part of global streaming domain seizures under Operation Offsides.
Gitea vulnerability CVE-2026-58443 (CVSS 9.6) lets public-only tokens write to private repos. Details and PoC code are public. Update to v1.27.0.
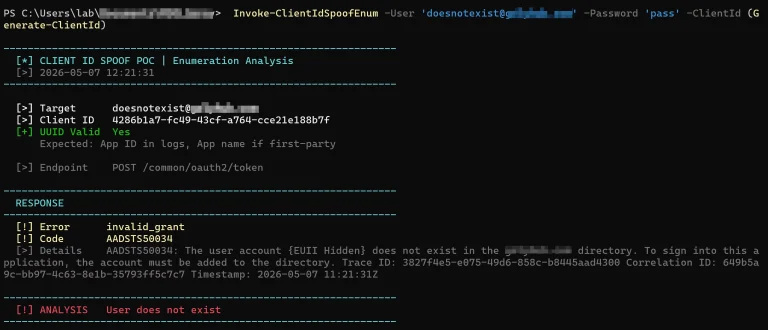
Proofpoint details OAuth client ID spoofing, a stealthy account enumeration technique probing Microsoft Entra ID without a successful sign-in event.
Apache Doris vulnerability CVE-2026-58319 lets unauthenticated attackers hit FE HTTP admin APIs. Upgrade to Doris 3.1.0 now to close the flaw.
Siemens Opcenter X authentication bypass (CVE-2026-56451, CVSS 10) lets attackers forge JWTs for full unauthorized access. Update to V2604 now.
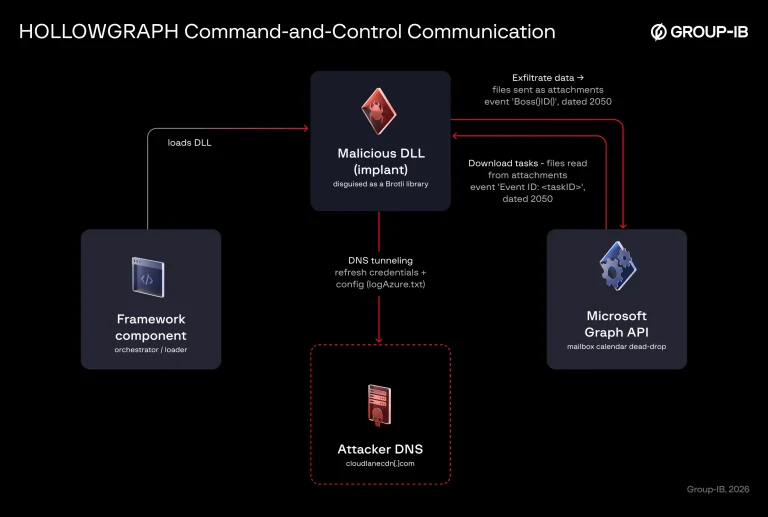
HOLLOWGRAPH malware turns Microsoft 365 calendars into covert C2 through Microsoft Graph API abuse. Group-IB links it to the Cavern framework.
CrashStealer is a native C++ macOS infostealer posing as Apple's crash reporter. Jamf details its notarized dropper, AES-GCM theft, and persistence.

Operation ShadowRecruit targets Indian job seekers with SheetAgent RAT, abusing ControlR and Google Sheets for C2. Seqrite links it to APT36.

LabubaRAT is a Rust-based remote access tool disguised as NVIDIA software. It supports HTTPS, WebView2, and DNS tunneling for command and control.
OpenAI trims the Codex context window from 372K to 272K and adds a system-prompt rule banning rm -rf $HOME after GPT-5.6 Sol wiped user home directories.
Microsoft's KB5121767 out-of-band update fixes a Dell USB-C driver fault from the July 2026 patch that caused shutdowns, overheating, and battery drain.
Gurman reveals a secret new Intel Mac Pro (J170) and cancelled M2/M3 Extreme chips behind the Mac Pro discontinuation, as Mac Studio takes the crown.
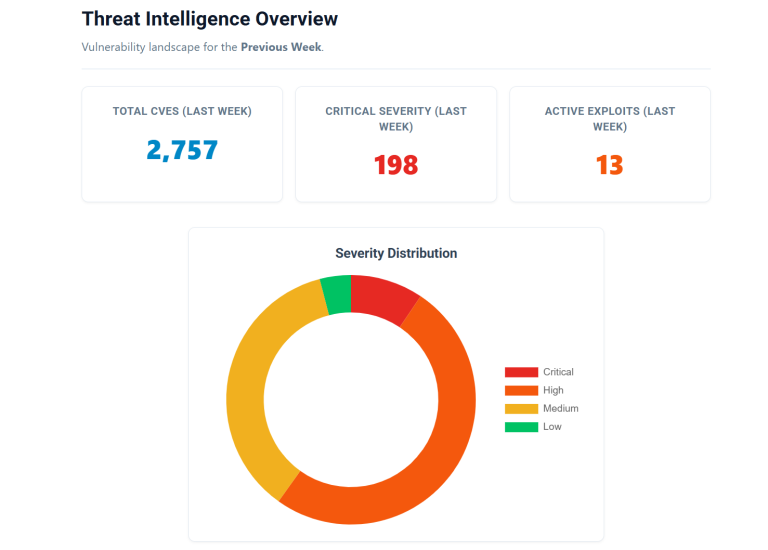
Read our mid-July weekly threat intelligence report. Stay informed on active vulnerability updates, Fortinet flaws, and CISA KEV additions.
Kimai vulnerability CVE-2026-52824 (CVSS 9.1) lets attackers forge cookies for account takeover via a default Docker APP_SECRET. Update to 2.58.0 now.
External routing lookups carry hidden costs: rate limits, data exposure and availability coupling. Here is why teams are moving to self-hosted routing intelligence.