Skip to content
November 1, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
OpenSSL HollowByte Vulnerability Causes Memory Exhaustion Diagram explaining the OpenSSL HollowByte vulnerability and OpenSSL DoS attack mechanism
  • Vulnerability Report

OpenSSL HollowByte Vulnerability Causes Memory Exhaustion

Do Son July 20, 2026 0

A new OpenSSL HollowByte vulnerability enables remote DoS attacks using just 11 bytes. Learn how to protect your servers against this OpenSSL DoS attack.
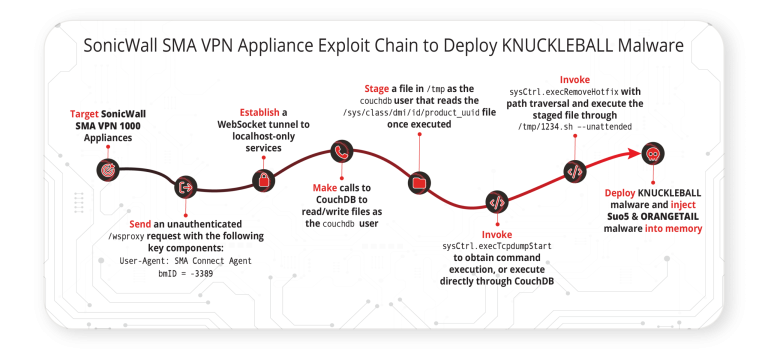
SonicWall SMA Zero-Day Chain Roots VPN Appliances and Plants Hidden Malware SonicWall SMA zero-day exploit chain compromising SMA VPN appliances to deploy malware
  • Cybercriminals

SonicWall SMA Zero-Day Chain Roots VPN Appliances and Plants Hidden Malware

Do Son July 19, 2026 0

Volexity found attackers chaining SonicWall SMA zero-day flaws to root SMA VPN appliances and plant stealth malware. Patch the hotfix now.
US Justice Department Approves TikTok for Government Devices DOJ lifts TikTok ban for federal workers and allows government downloads
  • Technology

US Justice Department Approves TikTok for Government Devices

Do Son July 18, 2026 0

The Justice Department now allows federal employees to download TikTok on government devices following massive structural changes and security updates.
Hugging Face Discloses Production Breach Driven by an Autonomous AI Agent Hugging Face breach driven by an autonomous AI agent attack exposing internal datasets and credentials
  • Data Leak

Hugging Face Discloses Production Breach Driven by an Autonomous AI Agent

Do Son July 18, 2026 0

The Hugging Face breach was driven end-to-end by an autonomous AI agent attack. Internal datasets and service credentials were exposed.
Meta and Anthropic Negotiate Computing Power Lease Meta AI computing power lease and Anthropic data center negotiations
  • Technology

Meta and Anthropic Negotiate Computing Power Lease

Do Son July 18, 2026 0

Meta and Anthropic are negotiating a $10 billion lease for AI computing power. This deal could transform Meta into a major cloud infrastructure provider.
Claude Fable 5 Subscription Changes Announced Claude Fable 5 subscription updates and AI computational limitations
  • Technology

Claude Fable 5 Subscription Changes Announced

Do Son July 18, 2026 0

Anthropic updates its Claude Fable 5 subscription model due to computational constraints, removing free access for Pro tiers.
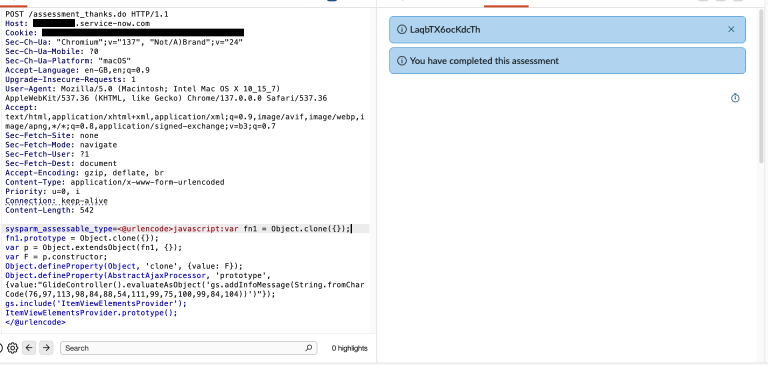
Active Exploitation and Public PoC Disclosed for CVE-2026-6875 ServiceNow Sandbox Escape Remote Code Execution Diagram of CVE-2026-6875 ServiceNow sandbox escape RCE and pre-auth code execution
  • Vulnerability Report

Active Exploitation and Public PoC Disclosed for CVE-2026-6875 ServiceNow Sandbox Escape Remote Code Execution

Do Son July 18, 2026 0

Attackers are exploiting a ServiceNow sandbox escape RCE in the wild. Public proof-of-concept details for CVE-2026-6875 pre-auth code execution are out.
Cloudflare Blocks Critical WordPress wp2shell Vulnerability Cloudflare firewall blocking the critical WordPress wp2shell vulnerability and RCE attacks
  • Vulnerability Report

Cloudflare Blocks Critical WordPress wp2shell Vulnerability

Do Son July 18, 2026 0

Cloudflare deploys emergency WAF rules to block the critical WordPress wp2shell vulnerability. Update your site now to prevent severe RCE security risks.
Microsoft Ends OneDrive Support for Windows 10 Microsoft ending OneDrive updates and support for Windows 10 lifecycle
  • Technology

Microsoft Ends OneDrive Support for Windows 10

Do Son July 18, 2026 0

Microsoft will gradually end OneDrive updates and support for Windows 10 versions 21H2 and 22H2. Discover the complete timeline and alternatives for users.
Ubuntu Pro Client Flaw CVE-2026-11386 Allows Arbitrary Code Execution With Root Privileges Ubuntu Pro Client vulnerability CVE-2026-11386 APT source injection arbitrary code execution root privileges
  • Vulnerability Report

Ubuntu Pro Client Flaw CVE-2026-11386 Allows Arbitrary Code Execution With Root Privileges

Do Son July 18, 2026 0

Ubuntu Pro Client vulnerability CVE-2026-11386 (CVSS 9.0) lets a spoofed contract server inject APT sources and run code with root privileges.
WordPress Pre-Auth RCE CVE-2026-63030: Vulnerability Details and PoC Exploit Code Now Public WordPress pre-auth RCE CVE-2026-63030 REST batch route confusion SQL injection public PoC
  • Vulnerability Report

WordPress Pre-Auth RCE CVE-2026-63030: Vulnerability Details and PoC Exploit Code Now Public

Do Son July 18, 2026 0

WordPress pre-auth RCE CVE-2026-63030 chains a REST batch bug with SQL injection. Details and a public PoC are out. Update to WordPress 7.0.2 now.
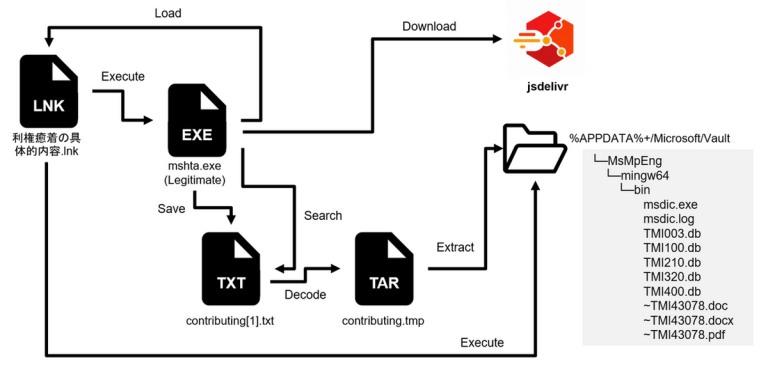
APT-C-60 Attacks Target Japan With SpyGlace Malware APT-C-60 attacks on Japan using LNK files and legitimate services to deploy SpyGlace malware
  • Cybercriminals

APT-C-60 Attacks Target Japan With SpyGlace Malware

Do Son July 18, 2026 0

JPCERT/CC details new APT-C-60 attacks on Japan. The group abuses Proton Drive, LNK files, and GitHub to deploy SpyGlace malware.
CheapSSLWEB Review: Best Place to Buy Cheap SSL Certificates with SSL Automation cheapsslweb-ssl-provider
  • Technique

CheapSSLWEB Review: Best Place to Buy Cheap SSL Certificates with SSL Automation

Do Son July 18, 2026 0
As cyber threats continue to grow and SSL certificate lifecycles become shorter, businesses need a security provider...
Read More Read more about CheapSSLWEB Review: Best Place to Buy Cheap SSL Certificates with SSL Automation
Certera Review: A Trusted Leader in SSL Certificates, PKI, and Digital Trust Solutions certera-ssl-provider
  • Technique

Certera Review: A Trusted Leader in SSL Certificates, PKI, and Digital Trust Solutions

Do Son July 18, 2026 0
In today’s digital world, protecting websites, applications, users, and sensitive data requires more than simply installing an...
Read More Read more about Certera Review: A Trusted Leader in SSL Certificates, PKI, and Digital Trust Solutions
GoldPickaxe Banking Trojan Returns to Steal Faces and Bank Logins GoldPickaxe banking Trojan stealing biometric data and lock screen credentials from an Android phone
  • Malware

GoldPickaxe Banking Trojan Returns to Steal Faces and Bank Logins

Do Son July 17, 2026 0

The GoldPickaxe banking Trojan returns, stealing biometric data, SMS, and lock screens from Android users across Asia, Zimperium warns.
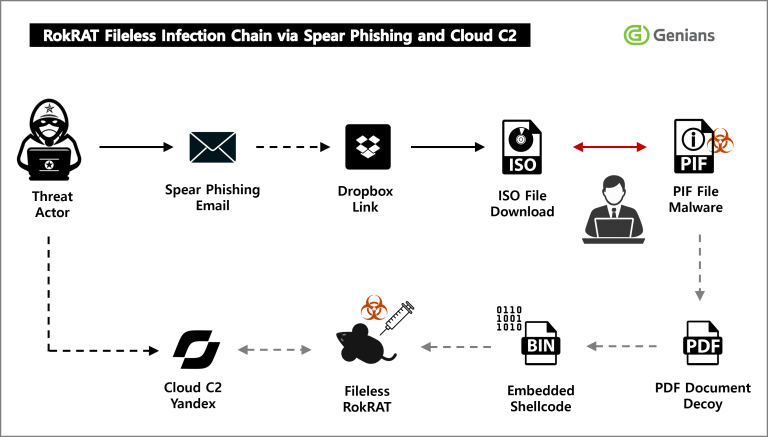
RokRAT Malware Hides in Fake PDF Files to Spy on Academics APT37 RokRAT malware delivered via fake PDF in Operation Capsule Vault spear-phishing
  • Malware

RokRAT Malware Hides in Fake PDF Files to Spy on Academics

Do Son July 17, 2026 0

Genians exposed Operation Capsule Vault, an APT37 campaign. The RokRAT malware hides inside a fake PDF to spy on academics and researchers.
CVE-2026-54523 (CVSS 9.6): Public PoC Exploit Enables Kyverno Privilege Escalation to Admin in Any Namespace Kyverno vulnerability CVE-2026-54523 privilege escalation to admin in any namespace including kube-system
  • Vulnerability Report

CVE-2026-54523 (CVSS 9.6): Public PoC Exploit Enables Kyverno Privilege Escalation to Admin in Any Namespace

Do Son July 17, 2026 0

Kyverno vulnerability CVE-2026-54523 (CVSS 9.6) is public with PoC exploit code. It lets a tenant gain admin in any namespace. Update to v1.18.2.
Citrix Secure Access Vulnerability Lets Local Users Gain SYSTEM Privileges Citrix Secure Access vulnerability CVE-2026-53565 privilege escalation illustration
  • Vulnerability Report

Citrix Secure Access Vulnerability Lets Local Users Gain SYSTEM Privileges

Do Son July 17, 2026 0

Citrix patched CVE-2026-53565, a Citrix Secure Access vulnerability letting local users gain SYSTEM, plus the CVE-2026-53566 out-of-bounds read bug.
Misconfigured Server Exposes Three AiTM Phishing Operators Open directory exposing three AiTM phishing operators using Evilginx MFA bypass tooling
  • Cybercriminals

Misconfigured Server Exposes Three AiTM Phishing Operators

Do Son July 17, 2026 0

A misconfigured server exposed three AiTM phishing operators running Evilginx MFA bypass and Device Code attacks on Microsoft 365 accounts.
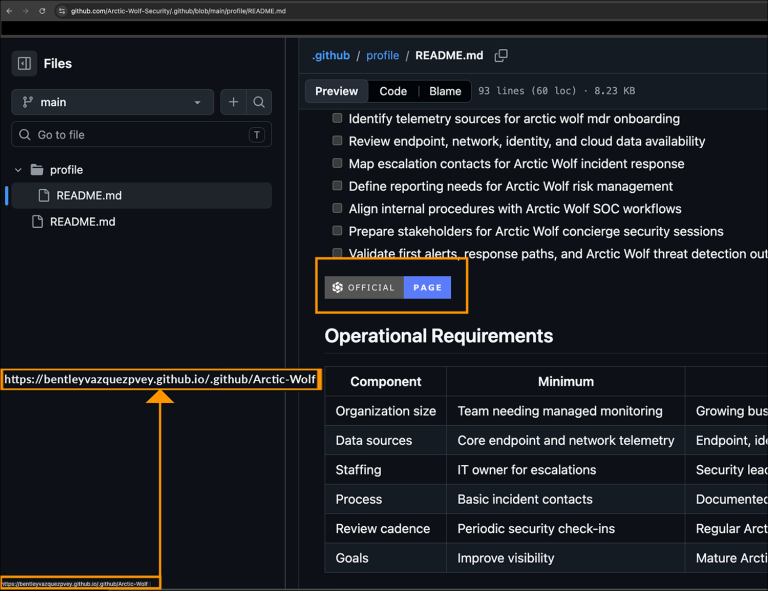
292 Fake GitHub Repositories Deliver BoryptGrab Infostealer to Windows Users Fake GitHub repositories BoryptGrab infostealer attack chain diagram
  • Malware

292 Fake GitHub Repositories Deliver BoryptGrab Infostealer to Windows Users

Do Son July 17, 2026 0

Arctic Wolf found 292 fake GitHub repositories impersonating software vendors to deliver a BoryptGrab-lineage infostealer via DLL side-loading.
EU Orders Google to Open Android to Rival AI Assistants and Share Search Data Under the DMA Google DMA ruling opening Android to third-party AI assistants and search data sharing
  • Technology

EU Orders Google to Open Android to Rival AI Assistants and Share Search Data Under the DMA

Do Son July 17, 2026 0

The Google DMA ruling forces Android to open core access to rival AI assistants and share search data by 2027, sparking privacy and security warnings.
Farewell NotebookLM: Google Rebrands Its AI Research Tool as Gemini Notebook, Adds Native Code Execution Gemini Notebook rebrand of NotebookLM with native code execution
  • Technology

Farewell NotebookLM: Google Rebrands Its AI Research Tool as Gemini Notebook, Adds Native Code Execution

Do Son July 17, 2026 0

Google rebrands NotebookLM as Gemini Notebook, adding native code execution, AI Mode integration, and citing over 30 million active users.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-76500CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality, the Cisco Application Policy Infrastructure Controller...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-76499CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality, the Cisco Application Policy Infrastructure Controller...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-76498CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality, the Cisco Application Policy Infrastructure Controller...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120308CVSS 9.9
    A Beta9 tenant can attach a volume when deploying a function, endpoint, or task queue. The gateway builds...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120307CVSS 9.9
    The Beta9 worker serves the sandbox file API from outside the container. getHostPathFromContainerPath turns the tenant's container path...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120306CVSS 9.9
    Beta9 turns each shell command in a tenant image definition into a Dockerfile RUN line and executes it...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120227CVSS 9.4
    A vulnerability was detected in WAVLINK WN701AE M01AE_V260105. This affects the function del_staticrule of the file static_route_setting.sh of...
    📅 Updated: Nov 1, 2026
  • CVE-2026-39738CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Aman FunnelKit Automations wp-marketing-automations allows Object Injection.This issue affects FunnelKit Automations: from...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120225CVSS 9.4
    A weakness has been identified in Oray Pugongying X5 Pro up to 7.6.1. Affected by this vulnerability is...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120224CVSS 9.4
    A security flaw has been discovered in Oray Pugongying X5 Pro up to 7.6.1. Affected is the function...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120198CVSS 10.0
    A vulnerability has been found in WAVLINK WL-WN530BE1-A V251117. Affected is the function con_check_read_finish of the file /protocol.csp....
    📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.