 Do Son
Chrome security update 150.0.7871.128 patches 7 flaws, including three critical use-after-free bugs in CameraCapture, GPU, and Network. Update now.

Doctor Web found a supply chain trojan targeting software developers. This developer-targeting malware steals data, crypto wallets, and mines coins.
TP-Link Kasa vulnerability CVE-2026-9770 (CVSS 8.6) lets local attackers intercept admin credentials on EC70 and EC71 cameras. Update firmware now.
CISA KEV catalog adds three actively exploited flaws: FortiSandbox CVE-2026-25089, CVE-2026-39808, and SharePoint CVE-2026-58644. Patch by July 19.
7-Zip vulnerability CVE-2026-14266 (CVSS 7.0) allows remote code execution via crafted XZ data. Update to 7-Zip 26.02. No exploitation confirmed.
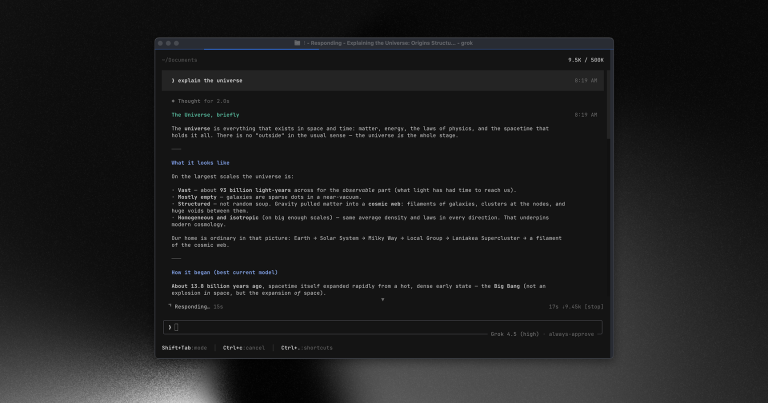
Grok Build open source release lets the community audit the code with data sharing disabled by default, yet GitHub Issues and PRs remain closed.
CVE-2026-15378 is a blind SSRF in Red Hat OpenShift AI. The guardrails-detectors flaw exposes cloud credentials and Kubernetes secrets.
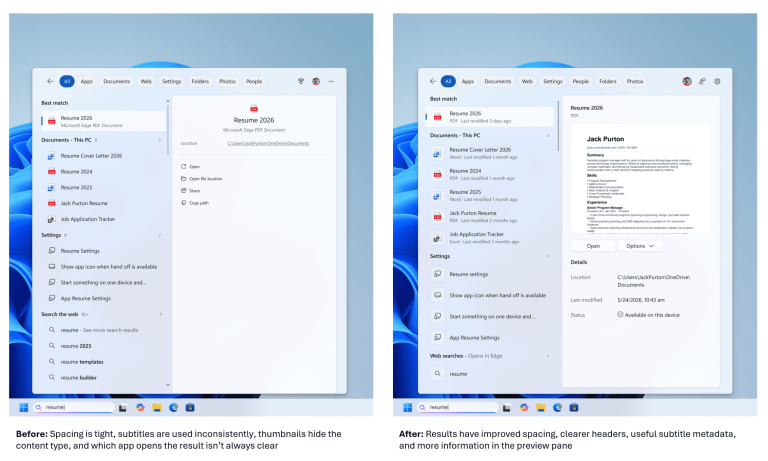
Microsoft explains Windows monthly updates terminology: B releases, quality updates, optional previews, OOB patches, and CFR rollouts clarified.
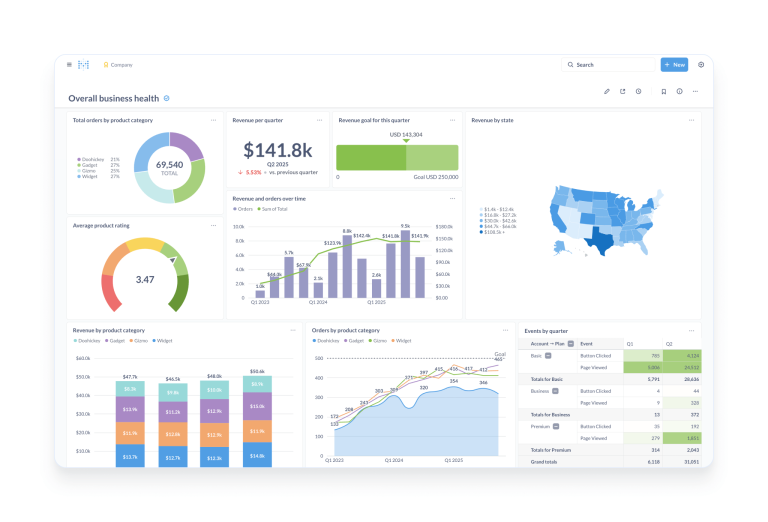
Metabase patched CVE-2026-59827 (CVSS 9.9) and CVE-2026-59826 (CVSS 9.1). These flaws enable remote code execution via unsafe H2 deserialization.
Apache IoTDB fixes five flaws in its time-series database, including privilege escalation and an unauthenticated DoS. Upgrade to 2.0.10 now.
SonicWall SMA1000 vulnerability CVE-2026-15409 (CVSS 10.0) is exploited in the wild. Public PoC enables remote code execution patch now.
Dell patched CVE-2026-56688, a PowerFlex command execution bug. This OS command injection flaw lets a privileged attacker run code as root.
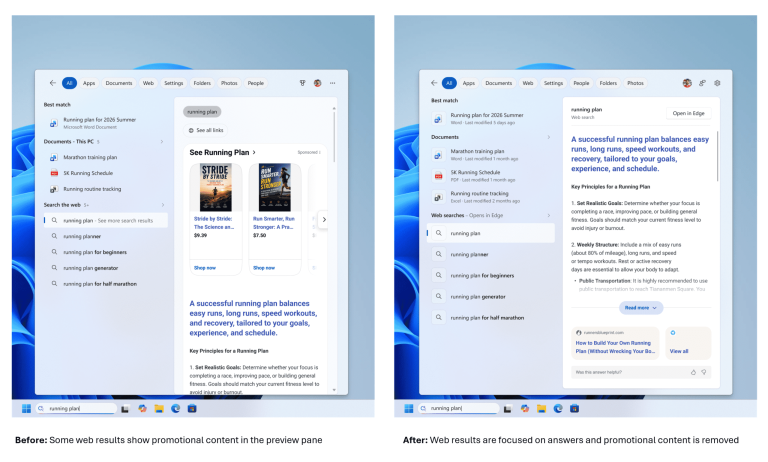
Microsoft has the Windows 11 update blocked on some Dell devices after an Intel driver clashed with the new USB-C Connection Manager from KB5095093.
Elon Musk says X Twitter open source plans will cover the entire codebase for review, backed by independent audits but no timeline exists yet.
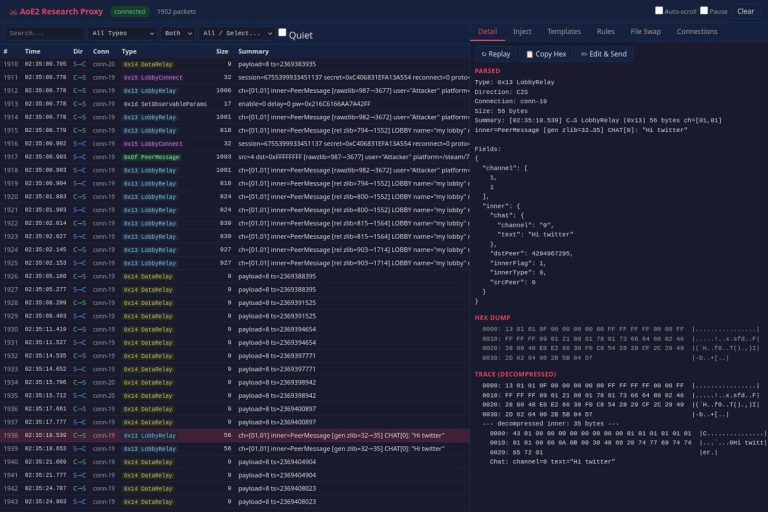
Microsoft patched a severe Age of Empires CVE. Attackers exploited game lobbies for remote code execution. Update your game immediately to stay safe.
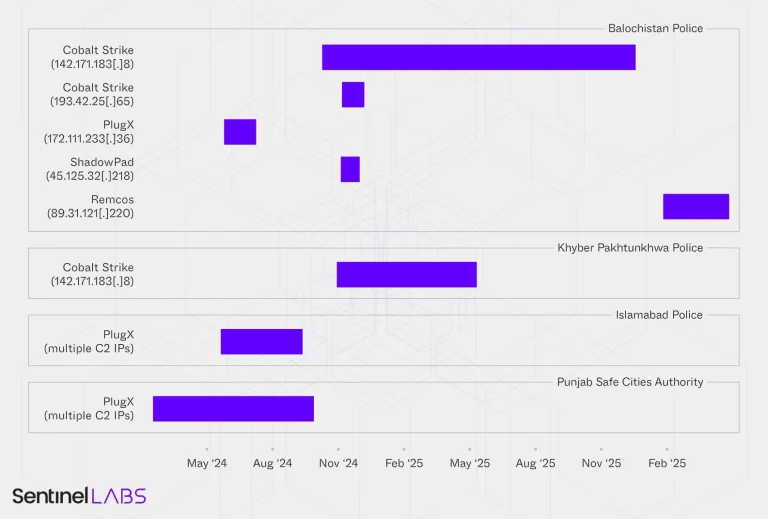
SentinelLABS found Chinese cyberespionage and India-nexus actors converging on Pakistani law enforcement, hitting Balochistan Police records and citizens.
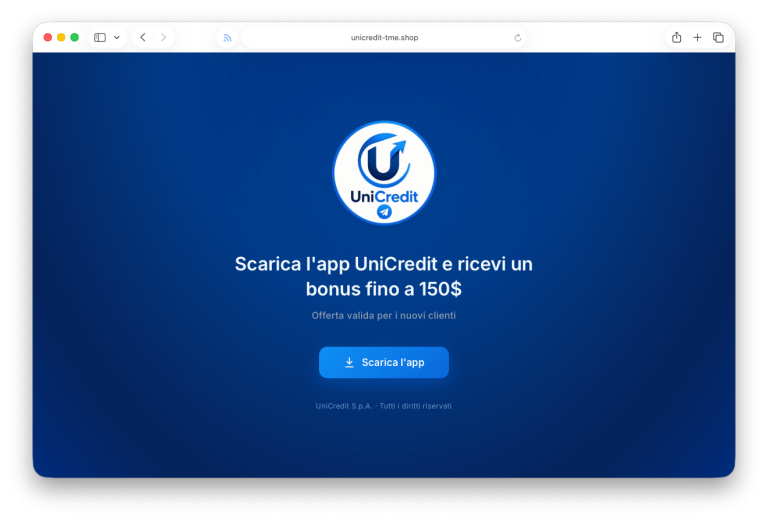
Albiriox malware spreads via a fake UniCredit reward and a Telegram bot. The Android banking trojan abuses Accessibility to steal OTPs and hijack devices.
ReliaQuest links the new Helix data extortion group to BlackFile, using vishing and device code phishing to steal SharePoint data.

Microsoft exposes the GigaWiper backdoor, a destructive tool that bundles disk wiping malware, fake ransomware, and remote control in one implant.
CISA KEV catalog now lists CVE-2026-46817, a critical Oracle E-Business Suite flaw, and CVE-2023-4346 in KNX devices. Both are exploited in the wild.
Splunk patched three Splunk Enterprise vulnerabilities: CVE-2026-20296 CSRF, CVE-2026-20297 path traversal, and CVE-2026-20298 credential exposure.
F5 patched the NGINX code execution flaw CVE-2026-42533, along with CVE-2026-60005 and CVE-2026-56434. Update NGINX Plus and Open Source builds now.