 Do Son
QNAP PHP2Shell vulnerabilities CVE-2026-109618 and CVE-2026-109619 affect QTS, QuTS hero and apps. No patch yet, so take NAS devices offline.
The EU's Booking.com DSA investigation targets fake listings, Booking.com phishing scams and hidden ads. Fines could hit 6% of global turnover.
Two critical Portainer vulnerabilities enable a bind mount bypass and Docker host takeover by standard users. Upgrade to Portainer 2.45.2 now.

Kaspersky uncovered the BlackX UEFI bootkit APT41 campaign bypassing Secure Boot via Baton Drop to spy on Central Asian diplomatic agencies.
Fortinet security updates for FortiOS, FortiManager and FortiAnalyzer fix critical AI-found flaws. Advisories follow November 10. Patch now.

APT28 used the Hookedge backdoor, SSH tunnels, and a new loader to spy on a naval shipbuilder and defense firms in two NATO countries.
The Claude Duet AI agent debuts as a research preview on Opus 5.5, with a private VM and a planned $20 Claude Pro price.
A new StopRansomware advisory warns SafePay ransomware has hit 600+ victims via VPN logins and edge flaws. See its tactics and key defenses.
A China-linked operator ran an AI-driven hacking campaign from one server, hitting ministries in Vietnam, Taiwan, Indonesia, and India.
The Zeabur platform shutdown is set for December 2026 after an attacker read 3.21 million environment variables and 321,800 accounts.
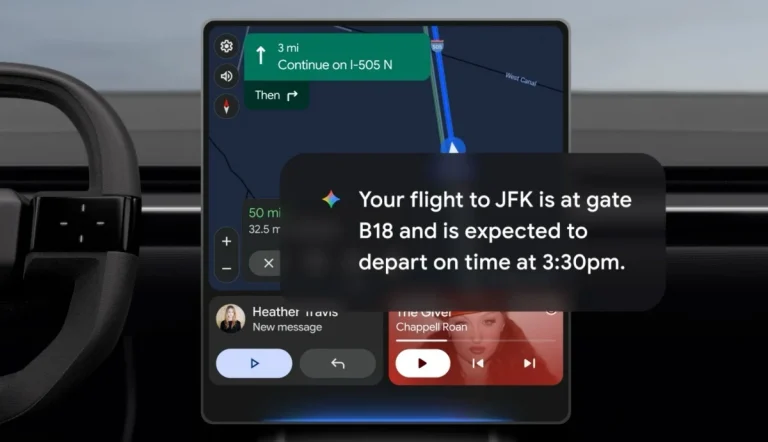
Google Maps brings Gemini in Apple CarPlay, introducing conversational AI navigation, complex trip planning, and hands-free traffic reporting.
Details and a PoC are public for CVE-2026-113380, a Signal call vulnerability in RingRTC that keeps calls live after hang-up. Update now.
Cisco fixes 13 Snort 3 vulnerabilities, including CVE-2026-20043 and denial of service flaws affecting FTD, Meraki MX and IOS XE.
Railway security incident: attackers may have decrypted Railway environment variables. Builds are paused. Rotate API keys and credentials now.
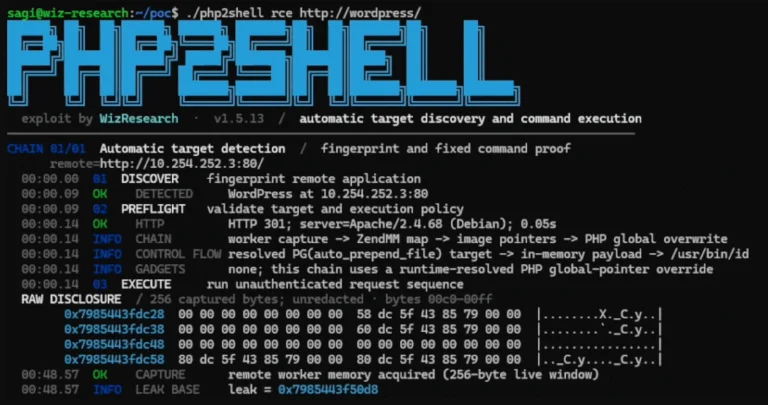
PHP2Shell remote code execution flaws CVE-2026-109618 and CVE-2026-109619 are exploited in the wild as PoCs go public. Patch PHP now.
Splunk fixes 31 Splunk vulnerabilities in Enterprise and Splunk SOAR, including CVSS 9.9 flaws CVE-2026-76531, CVE-2026-76299 and CVE-2026-76302.
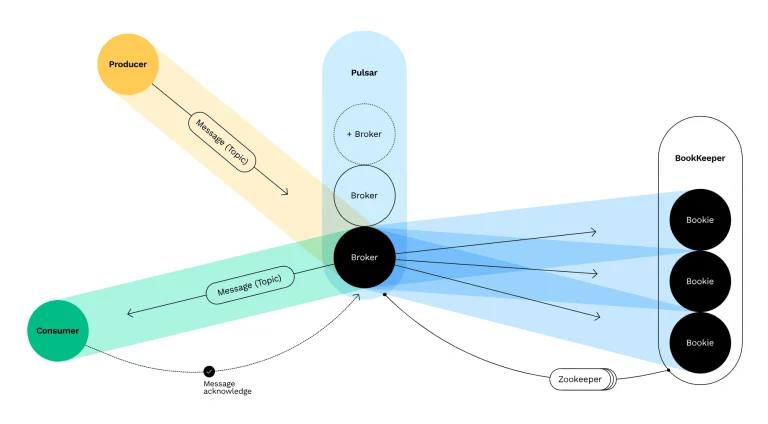
Patch 13 Apache Pulsar vulnerabilities and 4 Apache IoTDB flaws now, including critical bugs CVE-2026-105944, CVE-2026-105869, and CVE-2026-59229.
Review the latest Cisco security advisory to patch 10 Cisco Expressway vulnerabilities, including critical 9.8 CVSS root RCE flaw CVE-2026-76466.
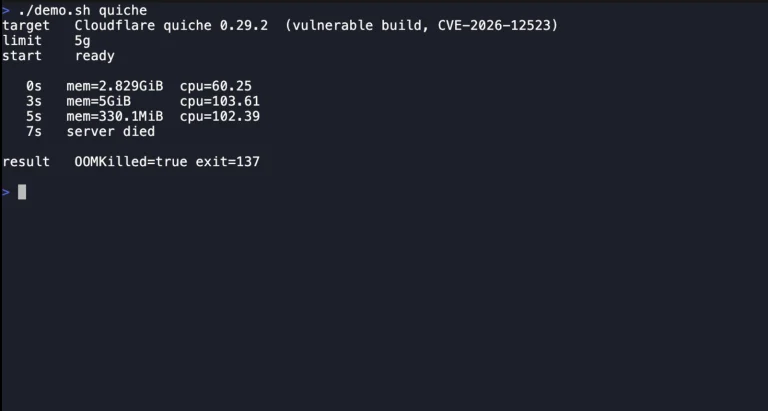
FoxIO released details and PoC code for a QPACK amplification attack that can crash HTTP/3 servers, including quic-go, quiche, lsquic and Bun.
15 Apache Traffic Server vulnerabilities, including CVSS 10.0 CVE-2026-111813, allow cache poisoning and smuggling. Upgrade to 10.2.1.
Based on our research, the top threat intelligence platforms in the Middle East in 2026 are CloudSEK,...
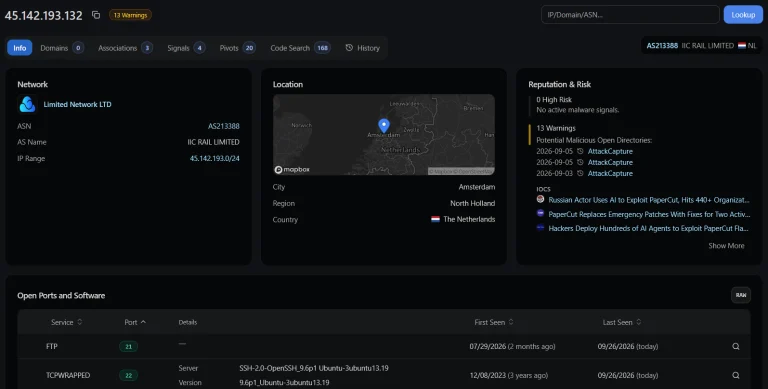
An exposed server reveals AI-assisted exploitation behind a PaperCut RCE campaign, a second XML-RPC attack path, and 45 live network pivots.