
 Do Son
PoC exploit code released for critical FortiSIEM flaw CVE-2025-64155 (CVSS 9.4). Unauthenticated RCE allows root access. Upgrade to v7.4.1 now.
Fortinet

Fortinet warns of active exploits for CVE-2020-12812, where attackers bypass 2FA on FortiGate firewalls by simply changing username capitalization.

Sophos CTU reveals how the ClickFix tactic led to a Qilin ransomware attack via NetSupport RAT and StealC V2 using stolen VPN credentials.

A critical FortiGate SSO flaw (CVSS 9.1) is under active exploitation, letting unauthenticated attackers bypass login via crafted SAML. The flaw is armed by default registration, risking config exfiltration. Patch immediately.
A Critical (CVSS 9.1) flaw in Fortinet's FortiCloud SSO allows unauthenticated admin bypass by forging SAML messages (Improper Signature Verification). The feature is often auto-enabled. Update or disable immediately.

Expel uncovered a phishing attack using Cache Smuggling to deliver malware. The technique uses a fake Fortinet lure and PowerShell to execute a payload staged in the browser's cache, bypassing network detection.
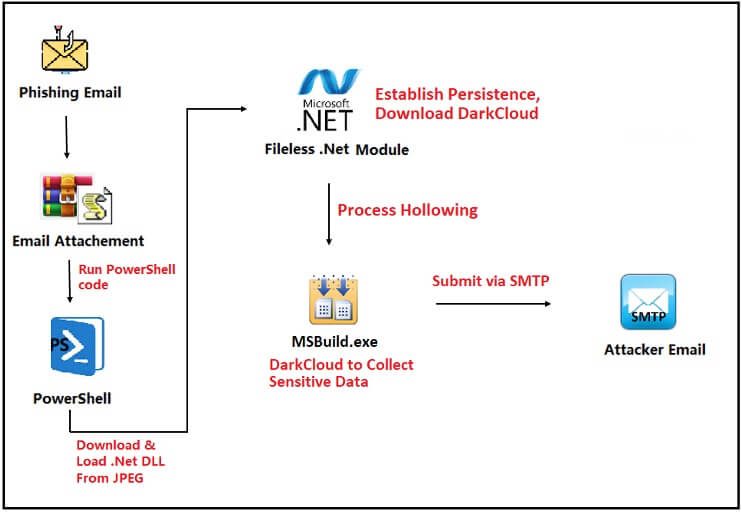
Fortinet uncovers a new DarkCloud stealer variant using a fileless, multi-stage attack chain with obfuscated PowerShell and process hollowing to evade detection and exfiltrate data.
CISA added CVE-2025-25257, a critical FortiWeb SQL injection vulnerability (CVSS 9.6), to its KEV Catalog, confirming active exploitation in the wild. Update immediately!

GeoServer's RCE flaw (CVE-2024-36401) is actively exploited to deploy NetCat reverse shells and XMRig CoinMiners on Windows/Linux, hijacking resources.
NCSC reveals "UMBRELLA STAND" malware targeting Fortinet FortiGate 100D firewalls. It establishes stealthy backdoors for long-term cyber-espionage

Fortinet fixes a critical TACACS+ authentication bypass flaw (CVE-2025-22252) affecting FortiOS and FortiProxy. Patch now to prevent admin-level access.

Horabot malware targets Latin America with fake invoices, hijacking Outlook to spread phishing emails and steal data via stealthy scripting.

Fortinet warns CVE-2025-32756 is exploited in the wild. The critical RCE flaw affects FortiVoice, FortiMail, FortiNDR, and more. Patch immediately.

A misconfiguration exposed APT41 tools targeting Shiseido, revealing Fortinet exploit scripts, webshells, and reconnaissance tactics.

Fortinet warns of a novel persistence exploit using symbolic links in FortiGate SSL-VPNs. Upgrade to patched FortiOS versions to mitigate the threat.

Fortinet has addressed a critical vulnerability (CVE-2024-48887) in FortiSwitch that allows unauthenticated attackers to change admin passwords. Upgrade to the latest version to secure your devices.

Explore the evolving tactics of the Hunters International group in ransomware attacks and their impact on businesses.

Learn about LARVA-208, the new threat actor using sophisticated social engineering tactics like smishing and vishing.

Critical vulnerabilities in Fortinet products - FortiClient VPN, FortiManager, and FortiWLM. Stay safe from CVE-2023-34990 with the latest updates.

Stay safe from a critical flaw (CVE-2024-47575) in FortiManager that can be exploited by remote, unauthenticated attackers. Take action now!

Stay informed about the CVE-2024-23113 vulnerability in Fortinet devices. Explore the potential impact and learn how to protect your network from exploitation.
Get the latest updates on exploited security vulnerabilities. Find out how to protect your systems from the newly added threats.