Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Google AI Mode Ads Expand Globally with Multiturn Format Google AI Mode ads interface showing multiturn conversational advertising and global rollout roadmap
  • Technology

Google AI Mode Ads Expand Globally with Multiturn Format

Do Son October 30, 2026 0

Google is rolling out Google AI Mode ads across 13 international markets and launching multiturn ads in the US to offset rising AI compute costs.
Critical ServiceNow Vulnerabilities Patched in AI Platform ServiceNow vulnerabilities overview showing patch for CVE-2026-103093 and CVE-2026-103094
  • Vulnerability Report

Critical ServiceNow Vulnerabilities Patched in AI Platform

Do Son October 30, 2026 0

Apply the latest ServiceNow vulnerabilities patch to fix three flaws, including critical sandbox escape CVE-2026-103093 and password leak CVE-2026-103094.
OpenAI Dot SMS Feature Launches for ChatGPT Pro OpenAI Dot SMS feature interface showing iMessage and RCS chat with the OpenAI Dot AI agent
  • Technology

OpenAI Dot SMS Feature Launches for ChatGPT Pro

Do Son October 30, 2026 0

The OpenAI Dot SMS feature enables ChatGPT Pro subscribers to control autonomous AI agents directly through iMessage and RCS texting.

Polymarket Supply Chain Attack Drains Trader Wallets Polymarket supply chain attack diagram illustrating DebugBear script compromise and crypto wallet drainer activity
  • Cybercriminals

Polymarket Supply Chain Attack Drains Trader Wallets

Do Son October 30, 2026 0

A Polymarket supply chain attack compromised a third-party analytics script to deploy a crypto wallet drainer, prompting an immediate trading halt.
Chrome 156 Security Update Fixes 21 Flaws, Including a Critical MediaStream Bug Chrome 156 security update 156.0.8078.79 fixes critical Chrome vulnerability CVE-2026-76024 in MediaStream
  • Vulnerability Report

Chrome 156 Security Update Fixes 21 Flaws, Including a Critical MediaStream Bug

Do Son October 30, 2026 0

Chrome 156 security update 156.0.8078.79 fixes 21 flaws, including critical Chrome vulnerability CVE-2026-76024 in MediaStream. Update now.
Binance Hot Wallet Breach Prompts Multibillion-Dollar Inquiry Binance hot wallet breach diagram illustrating EIP-7702 smart contract authorization and asset freezing
  • Cybercriminals

Binance Hot Wallet Breach Prompts Multibillion-Dollar Inquiry

Do Son October 30, 2026 0

A suspected Binance hot wallet breach prompted emergency investigations as issuers froze over $2.3 billion in stablecoins amid massive token outflows.
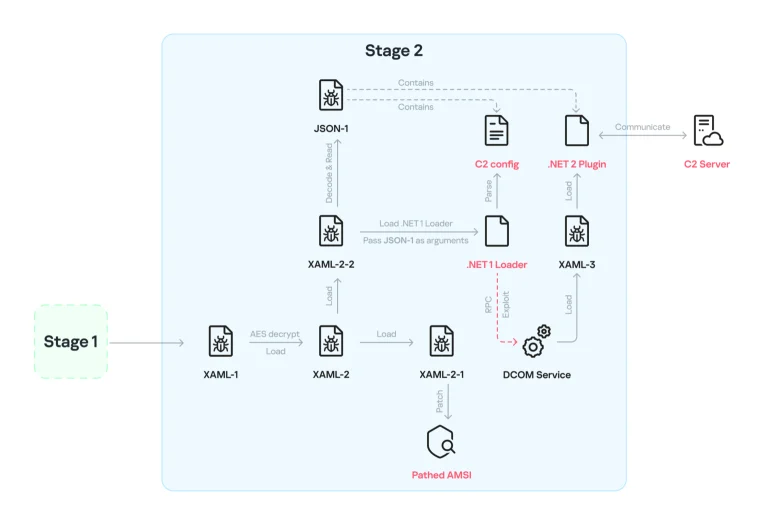
NetamLoader Hides in Windows Update Folder in Suspected Supply Chain Attack on Asian Government NetamLoader XAML infection chain in a suspected supply chain attack on a government Windows build in Asia
  • Cybercriminals

NetamLoader Hides in Windows Update Folder in Suspected Supply Chain Attack on Asian Government

Do Son October 30, 2026 0

NetamLoader, a new XAML-based .NET loader, points to a supply chain attack on a custom Windows build used by government entities in Asia.
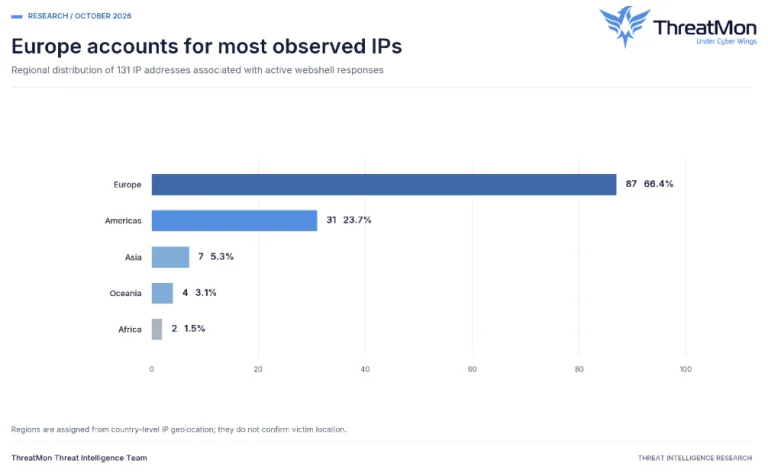
Exposed Workspace Shows AhsayCBS Webshells Turned Into SOCKS Proxy Tunnels AhsayCBS webshell access converted into SOCKS proxy tunnels using Chisel and GOST
  • Cybercriminals

Exposed Workspace Shows AhsayCBS Webshells Turned Into SOCKS Proxy Tunnels

Do Son October 30, 2026 0

An exposed workspace shows AhsayCBS webshell access turned into SOCKS proxy tunnels with Chisel and GOST across 141 hosts, per the logs.
Composer 2.11.0 and 2.2.31 Patch Path Traversal and Token Leak Vulnerabilities Composer vulnerabilities diagram showing Composer 2.11.0 fixes for GHSA-c968-33g3-wh7p and GHSA-fm2w-xgf2-f9fh
  • Vulnerability Report

Composer 2.11.0 and 2.2.31 Patch Path Traversal and Token Leak Vulnerabilities

Do Son October 30, 2026 0

Upgrade to Composer 2.11.0 or 2.2.31 to fix two Composer vulnerabilities: path traversal GHSA-c968-33g3-wh7p and token leak GHSA-fm2w-xgf2-f9fh.
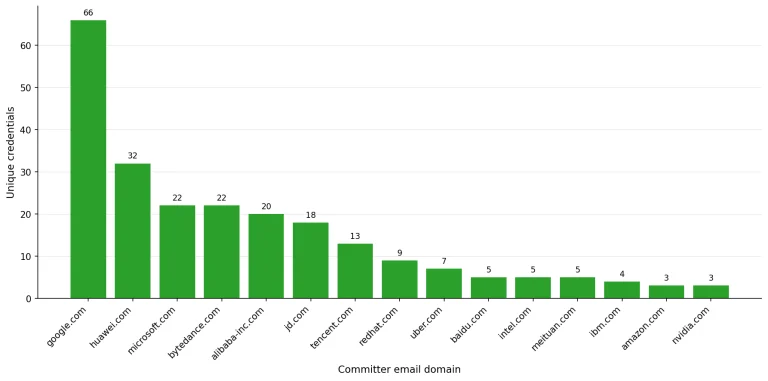
Gitee Exposed Credentials Found Across Millions of Repositories Gitee exposed credentials analysis diagram illustrating exposed API secrets across public repositories
  • Data Leak

Gitee Exposed Credentials Found Across Millions of Repositories

Do Son October 30, 2026 0

A security scan revealed over 26,000 Gitee exposed credentials across 7.25 million public repositories, affecting major cloud and AI platforms.
Veeam Patches Seven Vulnerabilities in Backup for Microsoft 365 and Management Pack Veeam vulnerabilities in Veeam Backup for Microsoft 365 and Management Pack, including RCE flaw CVE-2023-22793
  • Vulnerability Report

Veeam Patches Seven Vulnerabilities in Backup for Microsoft 365 and Management Pack

Do Son October 30, 2026 0

Veeam fixes seven vulnerabilities in Veeam Backup for Microsoft 365 and Management Pack, including RCE flaws CVE-2023-22793 and CVE-2026-106076.
Windows CLAT IPv6 Support Arrives in Windows 11 Windows CLAT IPv6 support diagram illustrating 464XLAT translation architecture and Windows 11 network settings
  • Windows

Windows CLAT IPv6 Support Arrives in Windows 11

Do Son October 30, 2026 0

Microsoft announced Windows CLAT IPv6 support in Windows 11, enabling legacy IPv4 applications to run seamlessly on modern IPv6-only enterprise networks.
Drupal Commerce Vulnerability CVE-2026-118539 Exploited in the Wild Drupal Commerce vulnerability CVE-2026-118539 access bypass exploited in the wild
  • Vulnerability Report

Drupal Commerce Vulnerability CVE-2026-118539 Exploited in the Wild

Do Son October 29, 2026 0

Drupal Commerce vulnerability CVE-2026-118539, a highly critical access bypass, is exploited in the wild. Upgrade to 3.3.13 or 8.x-2.41 now.

Building more resilient industrial control systems tech
  • Technique

Building more resilient industrial control systems

Do Son October 29, 2026 0
Modern industrial control systems can be a tremendous boon when it comes to productivity. But they can...
Read More Read more about Building more resilient industrial control systems
Google Search AI Ads Expand Amid Growth Slowdown Google Search AI ads interface illustrating conversational sponsored results and query monetization
  • Technology

Google Search AI Ads Expand Amid Growth Slowdown

Do Son October 29, 2026 0

Google is rolling out Google Search AI ads to new global markets and conversational queries as traditional advertising revenue growth decelerates.
Google Gemini 4 Carbon Launches with Elite AI Security Google Gemini 4 Carbon benchmark diagram illustrating cybersecurity performance and AI evaluation scores
  • Technology

Google Gemini 4 Carbon Launches with Elite AI Security

Do Son October 29, 2026 0

Google revealed Gemini 4 Carbon, a flagship model dominating benchmarks with zero prompt injection flaws and autonomous cybersecurity capabilities.
AppViewX Expands Quantum Trust Hub with Cryptographic Discovery, Posture Management, and Remediation PR_Banner_1200x720_3_1793213771AzzyxWguc4
  • Press Release

AppViewX Expands Quantum Trust Hub with Cryptographic Discovery, Posture Management, and Remediation

cybernewswire October 29, 2026 0
New York, New York, 29th October 2026, CyberNewswire
Read More Read more about AppViewX Expands Quantum Trust Hub with Cryptographic Discovery, Posture Management, and Remediation
South Korea App Store Fine Hits Apple and Google South Korea app store fine diagram showing regulatory penalties against Apple and Google in-app payment systems
  • Technology

South Korea App Store Fine Hits Apple and Google

Do Son October 29, 2026 0

A South Korea app store fine penalizes Apple and Google $48 million for enforcing coercive in-app payment rules and imposing excessive commission fees.
Google Registered App Stores Launch for Android Google Registered App Stores diagram illustrating one-click installation and malware scanning on Android
  • Android

Google Registered App Stores Launch for Android

Do Son October 29, 2026 0

The Google Registered App Stores program brings seamless one-click app installs and background updates to verified third-party Android marketplaces.
PS5 Hypervisor Vulnerability Bounty Sparks Backlash PS5 hypervisor vulnerability diagram showing exploit disclosure and PS5 Linux project impact
  • Technology

PS5 Hypervisor Vulnerability Bounty Sparks Backlash

Do Son October 29, 2026 0

A researcher reported a critical PS5 hypervisor vulnerability to Sony for $50,000, triggering fierce debate and halting the PS5 Linux project.
Report Slams Microsoft Edge Dark Patterns in Windows Microsoft Edge dark patterns report illustrating Windows browser steering tactics
  • Technology

Report Slams Microsoft Edge Dark Patterns in Windows

Do Son October 29, 2026 0

A new report exposes ten Microsoft Edge dark patterns across Windows and Bing that steer users away from competing web browsers.
GMO Internet Ransom Demand Slashed After Cloud Breach GMO Internet ransom demand diagram illustrating cloud security misconfiguration and breach leak
  • Cybercriminals

GMO Internet Ransom Demand Slashed After Cloud Breach

Do Son October 29, 2026 0

Hackers reduced the GMO Internet ransom demand from $50M to $1M and leaked victim files after the Japanese conglomerate ignored multiple bug warnings.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-117691CVSS 9.1
    A flaw was found in the SAML HTTP-Redirect binding implementation of Keycloak. The issue occurs because the server...
    📅 Updated: Nov 7, 2026
  • CVE-2026-120984CVSS 9.1
    A flaw was found in the Keycloak server's client management component. When a client is created or imported...
    📅 Updated: Nov 7, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-118066CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2023-3961CVSS 9.1
    A path traversal vulnerability was identified in Samba when processing client pipe names connecting to Unix domain sockets...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.