Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Juniper Fixes 18 Session Smart Router Vulnerabilities, Two Rated CVSS 9.8 Session Smart Router vulnerabilities fixed in Juniper security bulletin JSA112183, including critical CVE-2026-103406
  • Vulnerability Report

Juniper Fixes 18 Session Smart Router Vulnerabilities, Two Rated CVSS 9.8

Do Son October 28, 2026 0

Juniper security bulletin fixes 18 Session Smart Router vulnerabilities, including CVSS 9.8 flaws CVE-2026-103406 and CVE-2026-103409. Update now.
MLflow Vulnerability CVE-2026-116690 Exploited in the Wild as PoC Details Go Public MLflow vulnerability CVE-2026-116690 exploited in the wild, proof-of-concept public for CVE-2026-116692 RCE
  • Vulnerability Report

MLflow Vulnerability CVE-2026-116690 Exploited in the Wild as PoC Details Go Public

Do Son October 28, 2026 0

An MLflow vulnerability, CVE-2026-116690, is exploited in the wild as proof-of-concept code for it and RCE flaw CVE-2026-116692 goes public. Patch now.
Apple Selfie Age Verification Arrives in iOS 27.2 Apple selfie age verification interface showing facial scanning and iOS age verification controls
  • Technology

Apple Selfie Age Verification Arrives in iOS 27.2

Do Son October 28, 2026 0

Apple selfie age verification launches in iOS 27.2, using on-device and Private Cloud Compute models to verify adult users across select global regions.
Discord Public Messages to Appear in Google Search Discord public messages search engine indexing and privacy settings interface
  • Technology

Discord Public Messages to Appear in Google Search

Do Son October 28, 2026 0

Discord announced that Discord public messages from discoverable servers will soon be indexed by search engines and published on the open web.
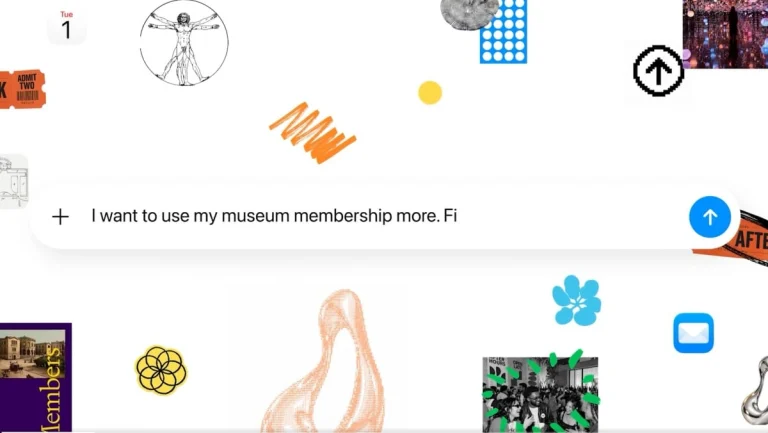
ChatGPT iCloud Integration Links Mail and Calendar ChatGPT iCloud integration interface displaying Mail and Calendar plugin synchronization
  • Technology

ChatGPT iCloud Integration Links Mail and Calendar

Do Son October 28, 2026 0

The official ChatGPT iCloud integration enables users to search emails, organize inboxes, and manage calendar appointments through natural conversations.
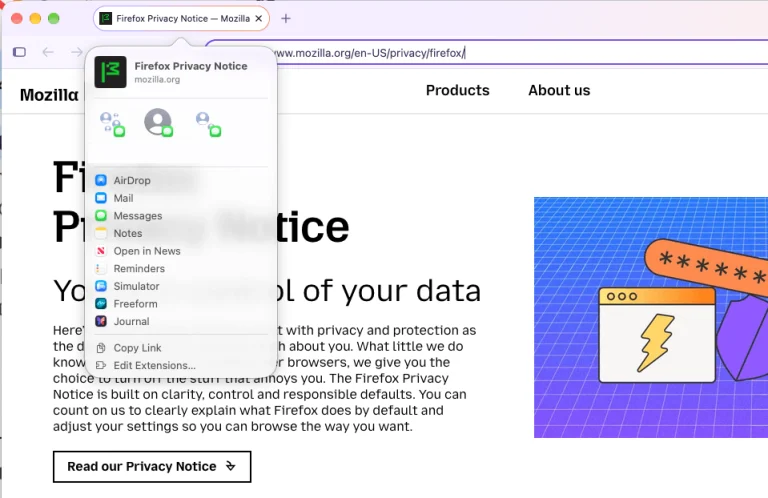
Mozilla Firefox 159 Debuts Sidebar Passwords and AI Tools Mozilla Firefox 159 interface showcasing sidebar passwords and AI page watch features
  • Technology

Mozilla Firefox 159 Debuts Sidebar Passwords and AI Tools

Do Son October 28, 2026 0

The Mozilla Firefox 159 release introduces default sidebar passwords, open tab search shortcuts, Wayland fixes on Linux, and an AI-driven webpage monitor.
Anthropic’s AI Vulnerability Research Uncovers Critical RCE Chains AI vulnerability research by Claude uncovering remote code execution chains in Chrome, Safari, Android, Windows and Linux
  • Technology

Anthropic’s AI Vulnerability Research Uncovers Critical RCE Chains

Do Son October 28, 2026 0

Anthropic's AI vulnerability research found remote code execution chains in Chrome, Safari, Android, Windows and Linux. All are now fixed.
Hive Ransomware Affiliate Artem Stryzhak Sentenced to 70 Months in US Prison Hive ransomware affiliate sentenced in US court for Hive and Nefilim ransomware attacks
  • Cybercriminals

Hive Ransomware Affiliate Artem Stryzhak Sentenced to 70 Months in US Prison

Do Son October 28, 2026 0

A Hive ransomware affiliate who also used Nefilim ransomware got 70 months in prison. A co-conspirator remains at large with an $11M reward.
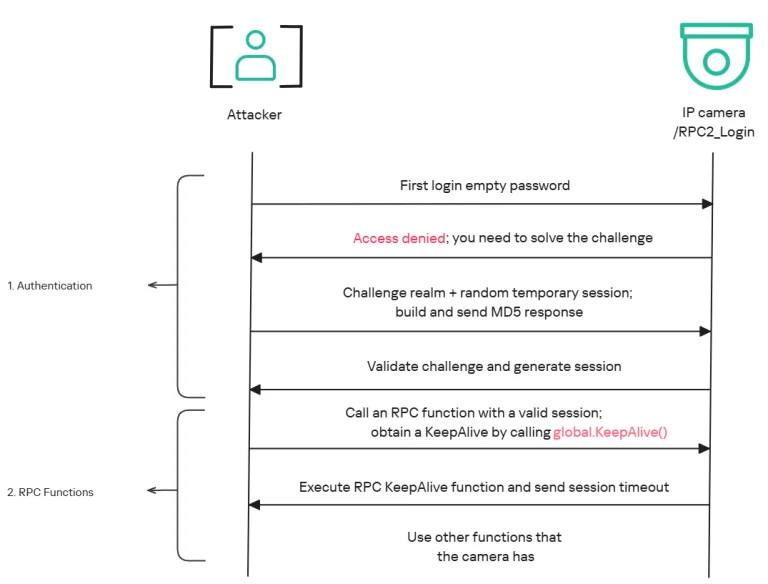
Intelbras Camera Vulnerability Lets Attackers Knock Mibo Cameras Offline Intelbras camera vulnerability enables denial-of-service attack on Mibo IP cameras via unauthenticated firmware update
  • Vulnerability Report

Intelbras Camera Vulnerability Lets Attackers Knock Mibo Cameras Offline

Do Son October 28, 2026 0

An Intelbras camera vulnerability enables a denial-of-service attack that knocks Mibo cameras offline from the local network. Update to R.260804.
How to control IoT devices securely AISelect_20261027_210513_Docs
  • Technique

How to control IoT devices securely

Do Son October 28, 2026 0
Most IoT security coverage is about devices being taken over: botnets, unsigned firmware, exposed admin ports. The...
Read More Read more about How to control IoT devices securely
Body-Parser Flaw CVE-2026-111181 Lets One Request Crash Express Servers, PoC Public Body-parser vulnerability CVE-2026-111181 enables Express denial of service with a single request
  • Vulnerability Report

Body-Parser Flaw CVE-2026-111181 Lets One Request Crash Express Servers, PoC Public

Do Son October 28, 2026 0

Body-parser vulnerability CVE-2026-111181 (CVSS 7.5) enables Express denial of service with one request. Upgrade to body-parser 2.4.0 or 1.20.9.
ADEX: AI involved in 52% of detected ad fraud schemes – shopping agents could be next Cover picture, ADEX State of Ad Fraud 2026
  • Technique

ADEX: AI involved in 52% of detected ad fraud schemes – shopping agents could be next

Do Son October 28, 2026 0
New ADEX research shows how AI is making familiar scams cheaper and harder to detect, while fraudsters...
Read More Read more about ADEX: AI involved in 52% of detected ad fraud schemes – shopping agents could be next
Unauthenticated File Read Leaks Master Key in LiteLLM Enterprise Proxy, CVSS 10.0 LiteLLM vulnerability lets unauthenticated file read leak master key on Enterprise proxy, CVSS 10
  • Vulnerability Report

Unauthenticated File Read Leaks Master Key in LiteLLM Enterprise Proxy, CVSS 10.0

Do Son October 28, 2026 0

A critical LiteLLM vulnerability (CVSS 10.0) lets an unauthenticated file read leak the master key on Enterprise proxies. Update to 1.106.5 now.
Adobe Patches Nine Critical Vulnerabilities in Campaign Classic and Connect Adobe vulnerabilities overview showing Adobe Campaign Classic fixes for CVE-2026-104351, CVE-2026-104353, and CVE-2026-48360
  • Vulnerability Report

Adobe Patches Nine Critical Vulnerabilities in Campaign Classic and Connect

Do Son October 28, 2026 0

Patch 9 critical Adobe vulnerabilities in Adobe Campaign Classic and Connect, including 9.9 CVSS RCE flaws CVE-2026-104351 and CVE-2026-48360.
Chrome Security Update Fixes 52 Flaws, Including Four Critical Bugs Chrome security update 156.0.8078.73 fixes 52 flaws, including critical Chrome vulnerabilities CVE-2026-118306
  • Vulnerability Report

Chrome Security Update Fixes 52 Flaws, Including Four Critical Bugs

Do Son October 28, 2026 0

Chrome security update 156.0.8078.73 fixes 52 flaws, including critical Chrome vulnerabilities like sandbox escape CVE-2026-118306. Update now.
TeamViewer Patches Three High-Severity Vulnerabilities in Client Software TeamViewer vulnerabilities diagram showing TeamViewer 15.83 fixes for CVE-2026-92372, CVE-2026-111585, and CVE-2026-92374
  • Vulnerability Report

TeamViewer Patches Three High-Severity Vulnerabilities in Client Software

Do Son October 28, 2026 0

Update to TeamViewer 15.83 to patch three high-severity TeamViewer vulnerabilities: CVE-2026-92372, CVE-2026-111585, and CVE-2026-92374.
VMware SDDC Manager Vulnerability CVE-2026-111497 (CVSS 9.8) Awaits a Patch VMware SDDC Manager vulnerability CVE-2026-111497 from Node.js Brotli vulnerability, CVSS 9.8
  • Vulnerability Report

VMware SDDC Manager Vulnerability CVE-2026-111497 (CVSS 9.8) Awaits a Patch

Do Son October 28, 2026 0

Broadcom warns of a VMware SDDC Manager vulnerability, CVE-2026-111497 (CVSS 9.8), from the Node.js Brotli vulnerability. Patches pending.

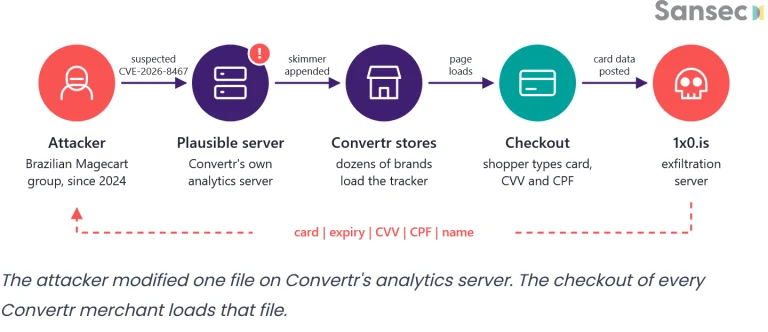
Brazilian Magecart Group Hits Convertr Ecommerce Platform in Plausible Analytics Supply Chain Attack Convertr supply chain attack and Plausible Convertr supply chain attack card skimmer flow
  • Malware

Brazilian Magecart Group Hits Convertr Ecommerce Platform in Plausible Analytics Supply Chain Attack
Do Son October 28, 2026 0

Sansec uncovers a Convertr supply chain attack. See how a Plausible Convertr supply chain attack planted a Magecart card and CPF skimmer on stores.
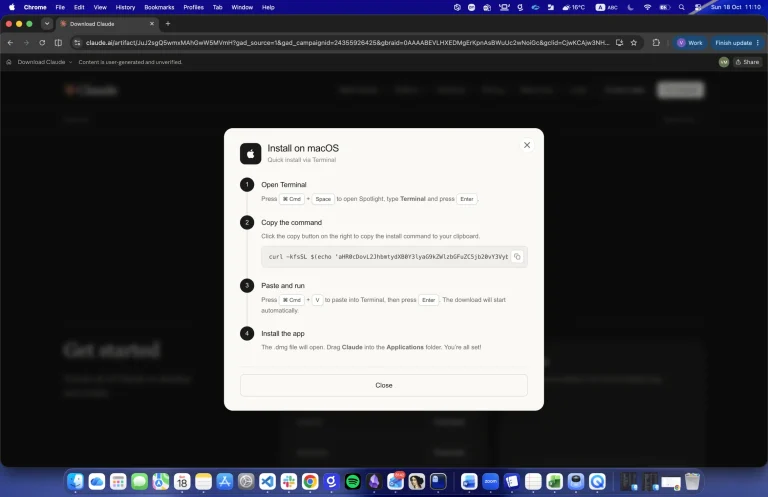
Attackers Abuse Claude Sharing Features and Google Ads to Deliver AMOS and Windows RAT Claude malware campaign and fake Download Claude malware campaign attack chain diagram
  • Malware

Attackers Abuse Claude Sharing Features and Google Ads to Deliver AMOS and Windows RAT

Do Son October 28, 2026 0

Gen Digital exposes a Claude malware campaign on claude.ai. This fake Download Claude malware campaign uses Google Ads and ClickFix to drop AMOS.
Windows 11 Prefetch Files: Performance and Forensics Windows 11 Prefetch files directory showing application launch traces and forensic artifacts
  • Windows

Windows 11 Prefetch Files: Performance and Forensics

Do Son October 28, 2026 0

Microsoft explains why deleting Windows 11 Prefetch files degrades application startup performance while highlighting their crucial digital forensics role.
Details and PoC Exploit Released for Linux nf_tables Vulnerability CVE-2026-23111 Linux nf_tables vulnerability CVE-2026-23111 kernelCTF exploit and PoC details published
  • Vulnerability Report

Details and PoC Exploit Released for Linux nf_tables Vulnerability CVE-2026-23111

Do Son October 28, 2026 0

PoC and full details are public for the Linux nf_tables vulnerability CVE-2026-23111. The kernelCTF exploit gains root and escapes containers. Patch now.
Supermicro BMC Vulnerabilities Hit 392 Boards, One Rated CVSS 9.8 Supermicro BMC vulnerabilities in IPMI firmware, including critical CVE-2026-18450
  • Vulnerability Report

Supermicro BMC Vulnerabilities Hit 392 Boards, One Rated CVSS 9.8

Do Son October 28, 2026 0

Supermicro BMC vulnerabilities hit 392 boards. Critical IPMI flaw CVE-2026-18450 (CVSS 9.8) lets attackers run commands. Update BMC firmware now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-117691CVSS 9.1
    A flaw was found in the SAML HTTP-Redirect binding implementation of Keycloak. The issue occurs because the server...
    📅 Updated: Nov 7, 2026
  • CVE-2026-120984CVSS 9.1
    A flaw was found in the Keycloak server's client management component. When a client is created or imported...
    📅 Updated: Nov 7, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-118066CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2023-3961CVSS 9.1
    A path traversal vulnerability was identified in Samba when processing client pipe names connecting to Unix domain sockets...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.