 Do Son
The new Claude CarPlay update introduces hands-free voice interaction for drivers, split-screen multitasking, and multi-account switching.
Install the latest JetBrains security update to fix critical JetBrains IDE vulnerabilities CVE-2026-118697 and CVE-2026-118696 affecting trusted certificates.

Players rarely open a game service with a product in mind. They open it with a question:...
CERT/CC warns of a critical Xerj authentication bypass tracked as CVE-2026-97406 that lets attackers mint persistent tokens without passkeys.
Reddit is testing a Reddit mandatory login policy to thwart unauthorized AI scrapers and counteract declining organic search traffic.
A Bitcoin Core DoS vulnerability allows remote peers to trigger out-of-memory crashes on Windows, macOS, and BSD nodes via TCP socket handling errors.
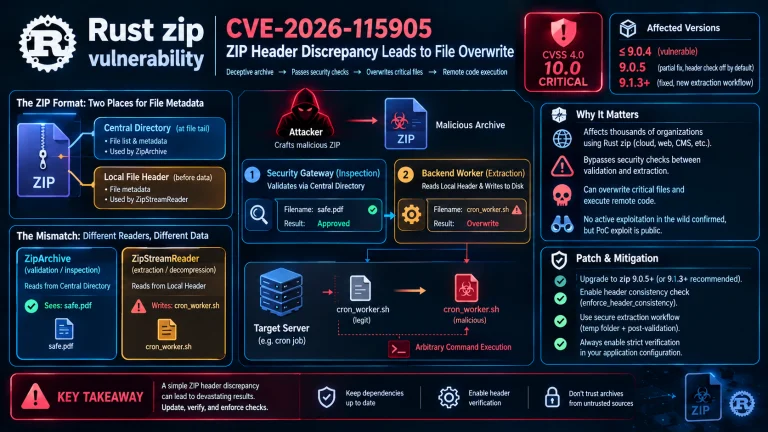
A critical Rust zip vulnerability CVE-2026-115905 allows attackers to bypass security gateways and overwrite server files using ZIP header discrepancies.
Won a contract but missing proof? Fast Cyber Essentials and a fast pen test help suppliers satisfy procurement without losing momentum.
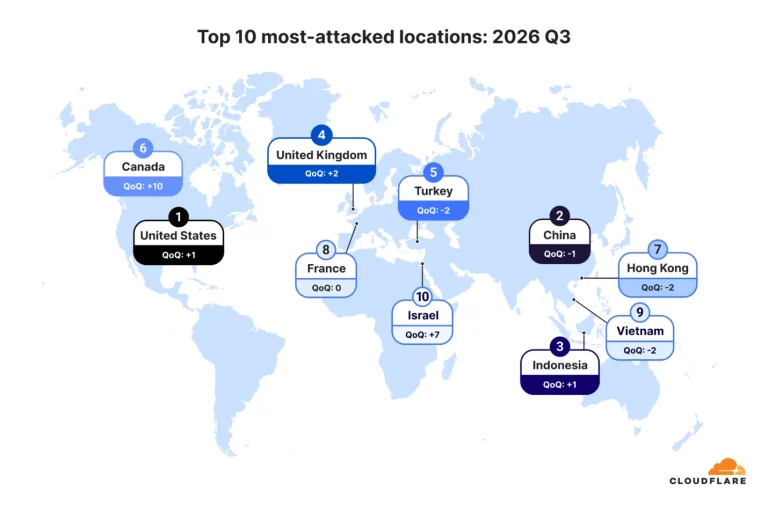
The Cloudflare DDoS report Q3 2026 reveals 18.2M network attacks, a 208% surge in short-burst floods, and a major shift toward DNS and UDP attacks.
Cursor removed a malicious Claude Code extension backdoor. Learn how the Cursor Claude Code extension backdoor planted SSH keys on up to 5,000 developer PCs.
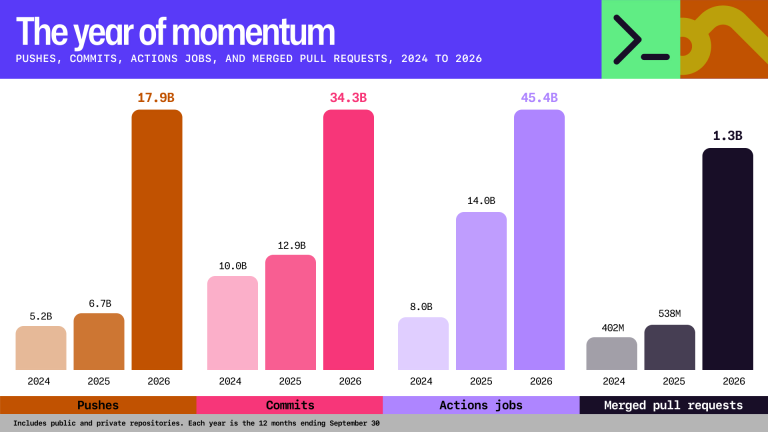
GitHub code activity reached historic highs in 2026, with over 7.3 billion monthly commits and 40% of pull requests drafted by AI coding agents.
The dramatic Stack Overflow question decline dropped monthly posts below 1,000 as developers embrace autonomous AI coding agents.
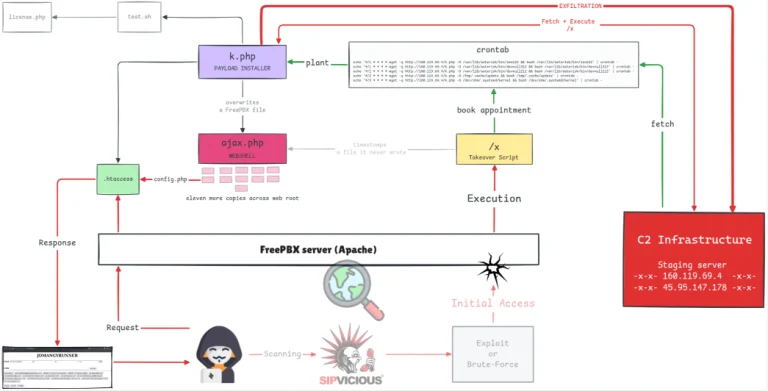
Cyble reveals how INJ3CTOR3 FreePBX malware steals 17 config files every minute. The JOMANGY INJ3CTOR3 FreePBX malware enables off-box toll fraud.
A critical Linux kernel CVE-2026-98432 flaw enables remote root execution via MPTCP race conditions, impacting multiple distributions including Ubuntu.
The Binance hack investigation reveals a $6.3B breach tied to TraderTraitor, prompting massive stablecoin freezes and an infrastructure overhaul.
Learn how to identify automated visitors, set sensible access rules, and protect sensitive website actions without blocking useful automation.
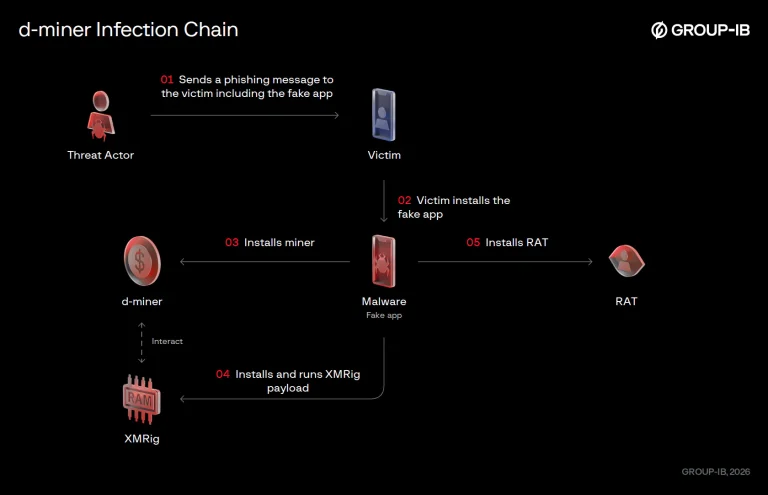
Group-IB exposes CyberDakait Android malware. The Indian CyberDakait Android malware campaign uses 7 trojans to infect 17,960 phones and steal 7.6M SMS.
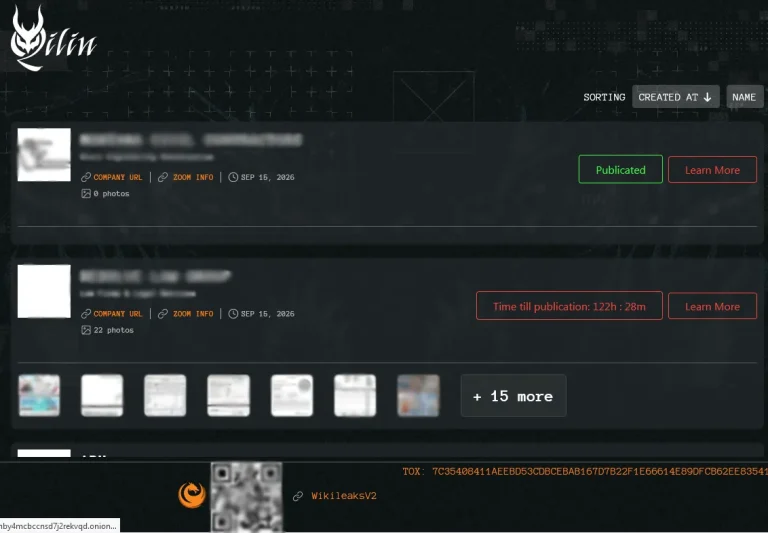
Acronis analyzes Qilin ransomware after 900+ attacks in 2026. See how ESXi Qilin ransomware scripts hijack VMware hosts and leak data on WikiLeaksV2.
Anthropic updated Claude Code permission modes with a toggle to suppress confirmation prompts for dangerous deletion commands during automated workflows.
Patch 15 WS_FTP Server vulnerabilities now, including 10.0 CVSS flaw CVE-2026-84295 and 9.9 CVSS command injection bug CVE-2026-90868.
A critical WordPress Core vulnerability is exploited in the wild. Update to WordPress 7.1.4 immediately to fix the unauthenticated race condition RCE.
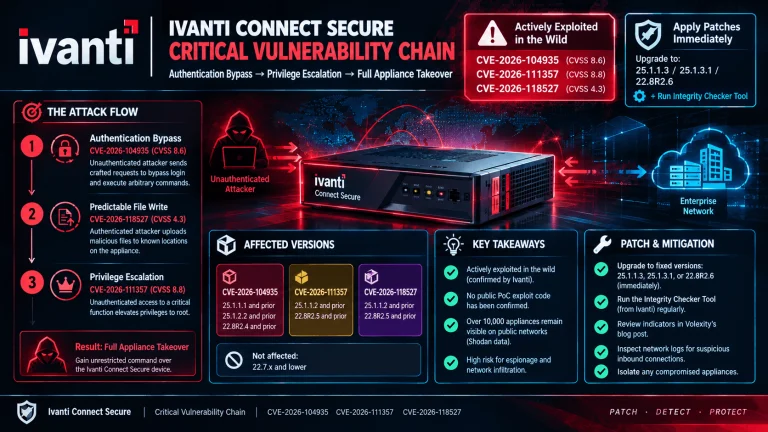
Patch the Ivanti Connect Secure vulnerability now. This Ivanti Connect Secure zero-day chain with CVE-2026-104935 is actively exploited in the wild.