Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Anthropic Restricts Claude Video Game Cloning in Major Policy Shift Claude video game cloning policy interface illustrating AI game cloning ban and system prompt rules
  • Technology

Anthropic Restricts Claude Video Game Cloning in Major Policy Shift

Do Son November 3, 2026 0

Anthropic updated Claude Opus 5.5 and Claude Code to block Claude video game cloning, preventing unauthorized remakes of commercial titles.

Hugging Face Malware Campaign Infects AI GPU Servers Exploit Jupyter Notebooks
  • Malware

Hugging Face Malware Campaign Infects AI GPU Servers

Do Son November 3, 2026 0

Pluto Research exposes Hugging Face malware. This Hugging Face malware campaign drops cryptominers and backdoors on self-hosted AI servers.
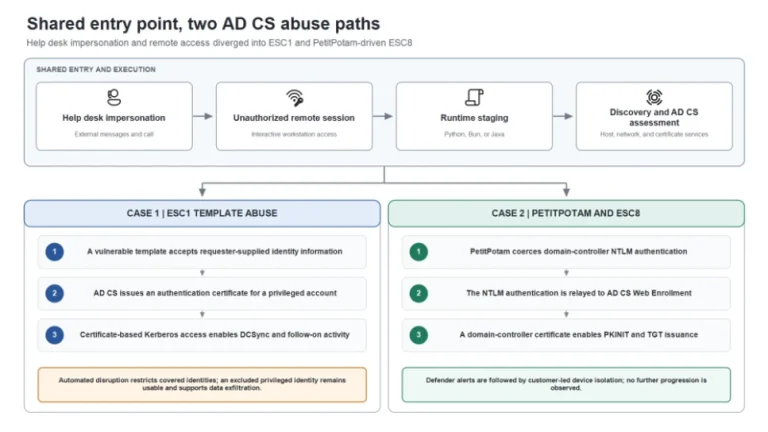
Help Desk Impersonation on Teams Leads to AD CS Abuse and Domain Takeover Attempts AD CS abuse attack chain starting with help desk impersonation on Microsoft Teams and Quick Assist
  • Cybercriminals

Help Desk Impersonation on Teams Leads to AD CS Abuse and Domain Takeover Attempts

Do Son November 3, 2026 0

Microsoft details help desk impersonation on Teams that led to AD CS abuse via ESC1 and ESC8, giving attackers privileged certificates.
Cogent Security Makes the Fortune Cyber 60 for a Second Year, With a Plan to Run Cyber Defense Like a Factory Cyber60_press_release_1793661492tW37PY7DGd
  • Press Release

Cogent Security Makes the Fortune Cyber 60 for a Second Year, With a Plan to Run Cyber Defense Like a Factory

cybernewswire November 3, 2026 0
San Francisco, CA, 3rd November 2026, CyberNewswire
Read More Read more about Cogent Security Makes the Fortune Cyber 60 for a Second Year, With a Plan to Run Cyber Defense Like a Factory
PSK Agent RAT Hits Magento Stores Through StyleSmuggler Exploitation PSK Agent RAT delivered to Magento stores through StyleSmuggler exploitation of CVE-2026-75650
  • Malware

PSK Agent RAT Hits Magento Stores Through StyleSmuggler Exploitation

Do Son November 3, 2026 0

StyleSmuggler exploitation of CVE-2026-75650 drops the PSK Agent RAT and a PHP webshell on Magento stores. See how to detect and respond.
7 Unpatched phpMyAdmin Vulnerabilities Exposed phpMyAdmin vulnerabilities diagram illustrating the phpMyAdmin vulnerabilities patch for CVE-2026-119426 and CVE-2026-119561
  • Vulnerability Report

7 Unpatched phpMyAdmin Vulnerabilities Exposed

Do Son November 3, 2026 0

Discover seven unpatched phpMyAdmin vulnerabilities exposing servers to SQL injection and auth bypass. Learn how to secure your databases today.
Critical Apache Security Vulnerabilities Patched in Core Projects Apache security vulnerabilities diagram illustrating Apache security fixes across Syncope, Fineract, and Arrow
  • Vulnerability Report

Critical Apache Security Vulnerabilities Patched in Core Projects

Do Son November 3, 2026 0

The ASF patched Apache security vulnerabilities with new Apache security fixes for Syncope, Arrow, and Fineract, including critical flaw CVE-2026-64618.
Rancher Security Vulnerabilities Expose Cloud Credentials Diagram of Rancher security vulnerabilities showing Rancher credential leak in meta proxy
  • Vulnerability Report

Rancher Security Vulnerabilities Expose Cloud Credentials

Do Son November 3, 2026 0

SUSE fixed Rancher security vulnerabilities, including Rancher credential leak CVE-2026-88811, an SSRF flaw, and an unauthorized shell bypass. Update now.
Android Security Update for November 2026 Fixes 216 Flaws, Including Zero-Click RCE Bugs Android security update November 2026 fixing remote code execution flaws CVE-2026-58868 and CVE-2026-58936
  • Vulnerability Report

Android Security Update for November 2026 Fixes 216 Flaws, Including Zero-Click RCE Bugs

Do Son November 3, 2026 0

The November 2026 Android security update fixes 216 flaws, including zero-click remote code execution bugs CVE-2026-58868 and CVE-2026-58936.
Arista Security Vulnerabilities Risk Remote Code Execution Arista security vulnerabilities diagram showing CVE-2026-111497 and CVE-2026-98432
  • Vulnerability Report

Arista Security Vulnerabilities Risk Remote Code Execution

Do Son November 3, 2026 0

Arista fixed critical Arista security vulnerabilities CVE-2026-111497 and CVE-2026-98432 that allow unauthenticated remote code execution. Update now.
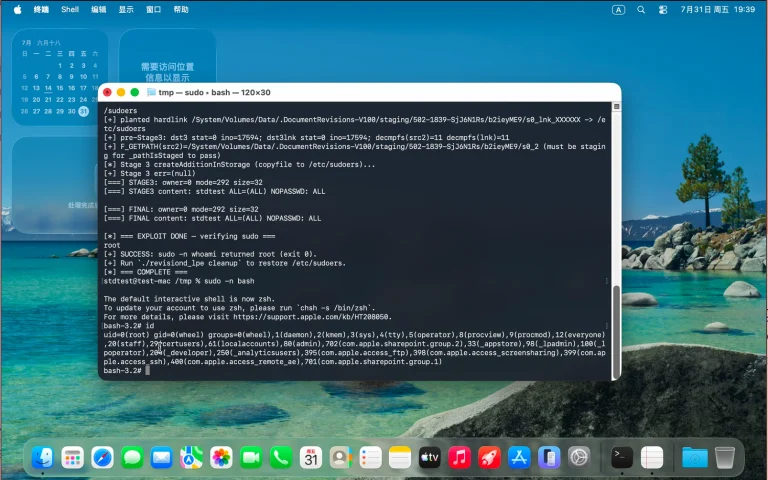
PoC Exploit Disclosed for macOS Local Privilege Escalation Vulnerability macOS revisiond vulnerability diagram showing macOS revisiond vulnerability PoC exploit for CVE-2026-112487
  • Vulnerability Report

PoC Exploit Disclosed for macOS Local Privilege Escalation Vulnerability

Do Son November 3, 2026 0

Technical details and a macOS revisiond vulnerability PoC exploit for CVE-2026-112487 are public, allowing root elevation. Update macOS immediately.
Public PoC Exploit Disclosed for Axis Camera Station RCE Axis Camera Station RCE diagram showing Axis Camera Station RCE PoC exploit chain for CVE-2025-30026 and CVE-2026-63286
  • Vulnerability Report

Public PoC Exploit Disclosed for Axis Camera Station RCE

Do Son November 3, 2026 0

Details and an Axis Camera Station RCE PoC are public. Patch CVE-2025-30026, CVE-2025-30023, and CVE-2026-63286 to prevent camera credential theft.
129 Linux Kernel Vulnerabilities Disclosed in One Week, Including Two Critical iSCSI Flaws Linux kernel vulnerabilities weekly roundup with kernel security update for critical iSCSI flaws CVE-2026-99154 and CVE-2026-99153
  • Vulnerability Report

129 Linux Kernel Vulnerabilities Disclosed in One Week, Including Two Critical iSCSI Flaws

Do Son November 3, 2026 0

Linux kernel vulnerabilities this week: 129 CVEs, including critical iSCSI flaws CVE-2026-99154 and CVE-2026-99153. Get the kernel security update.
Why does AI lose local context in translation, and what does the RUWIKI knowledge base change? Ruwiki
  • Technique

Why does AI lose local context in translation, and what does the RUWIKI knowledge base change?

Do Son November 3, 2026 0
AI can talk fluently about local history and culture in dozens of languages, yet it easily drops...
Read More Read more about Why does AI lose local context in translation, and what does the RUWIKI knowledge base change?
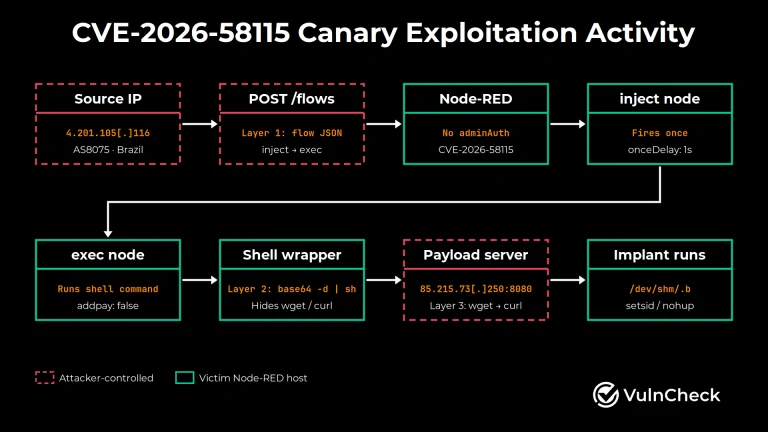
Node-RED Remote Code Execution Flaw CVE-2026-58115 with 10.0 CVSS Exploited in the Wild Node-RED RCE diagram showing Node-RED RCE vulnerability attack chain for CVE-2026-58115
  • Vulnerability Report

Node-RED Remote Code Execution Flaw CVE-2026-58115 with 10.0 CVSS Exploited in the Wild

Do Son November 3, 2026 0

A critical 10.0 CVSS Node-RED RCE vulnerability (CVE-2026-58115) is exploited in the wild to deploy Linux bot malware. Secure your exposed instances now.
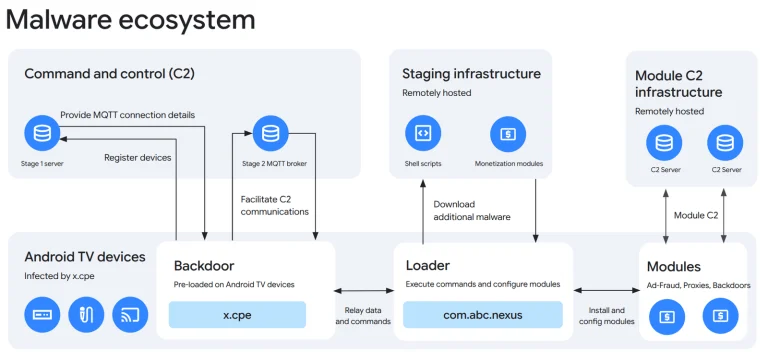
Google Disrupts Videostrong XCPE Botnet on Android TV XCPE botnet and Videostrong XCPE botnet architecture diagram
  • Malware

Google Disrupts Videostrong XCPE Botnet on Android TV

Do Son November 2, 2026 0

Google dismantled the Videostrong XCPE botnet infecting 1.3M set-top boxes. The XCPE botnet sold residential proxy access to cybercrime affiliates.
Stealthy Fileless Attacks Exploit Windows Tools to Evade Traditional Security Defenses sebastian-willius-GKCpRs0rcNY-unsplash (1)
  • Technique

Stealthy Fileless Attacks Exploit Windows Tools to Evade Traditional Security Defenses

Do Son November 2, 2026 0
Traditional antivirus software looks for suspicious files, but not every attack leaves one behind. In a fileless...
Read More Read more about Stealthy Fileless Attacks Exploit Windows Tools to Evade Traditional Security Defenses
Supermarket Freezer Hack Hits Stores Across Europe Supermarket freezer hack diagram showing industrial cooling controllers and retail refrigeration temperature spikes
  • Cybercriminals

Supermarket Freezer Hack Hits Stores Across Europe

Do Son November 2, 2026 0

A suspected supermarket freezer hack altered refrigeration units to 50C across Sweden, Belgium, and Estonia, spoiling food and forcing store closures.
Barracuda Patches Critical Authorization Bypass and Command Injection Flaws Barracuda vulnerabilities diagram showing how attackers chain CVE-2026-116606 and CVE-2026-111560 to gain Barracuda root access
  • Vulnerability Report

Barracuda Patches Critical Authorization Bypass and Command Injection Flaws

Do Son November 2, 2026 0

Patch two Barracuda vulnerabilities, CVE-2026-116606 and CVE-2026-111560, that allow attackers to gain Barracuda root access across multiple appliances.
Guardz Brings Palo Alto Networks Prisma Browser Protection to Small Businesses Guardz_1793620684bh13MmUP85
  • Press Release

Guardz Brings Palo Alto Networks Prisma Browser Protection to Small Businesses

cybernewswire November 2, 2026 0
Miami, United States, 2nd November 2026, CyberNewswire
Read More Read more about Guardz Brings Palo Alto Networks Prisma Browser Protection to Small Businesses
ChatGPT Violence Restrictions Tighten with Teen Safeguards ChatGPT violence restrictions interface illustrating AI moderation safeguards and ChatGPT teen safety protections
  • Technology

ChatGPT Violence Restrictions Tighten with Teen Safeguards

Do Son November 2, 2026 0

OpenAI announced new ChatGPT violence restrictions and teen safety protections, restricting weapon queries and terminating hazardous conversations.
AI Training Preference Standard Added to Robots.txt AI training preference standard robots.txt diagram illustrating web scraping rules and AI crawler directives
  • Technology

AI Training Preference Standard Added to Robots.txt

Do Son November 2, 2026 0

Tech giants support a new AI training preference standard in robots.txt, giving publishers granular control over model training data.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-117691CVSS 9.1
    A flaw was found in the SAML HTTP-Redirect binding implementation of Keycloak. The issue occurs because the server...
    📅 Updated: Nov 7, 2026
  • CVE-2026-120984CVSS 9.1
    A flaw was found in the Keycloak server's client management component. When a client is created or imported...
    📅 Updated: Nov 7, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-118066CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2023-3961CVSS 9.1
    A path traversal vulnerability was identified in Samba when processing client pipe names connecting to Unix domain sockets...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.