 Do Son
Google Project Zero security researcher James Forshaw recently vented on social media about a surprising Microsoft flaw. Specifically, he revealed that he uncovered an absurdly simple Windows UAC bypass technique. In James Forshaw’s Mastodon post on the UAC flaw, he mocked the vulnerable component as looking like AI-generated code. However, Forshaw withheld details regarding the affected module, exploitation method, and impacted Windows builds.
How Malware Silently Gains Full Administrator Privileges
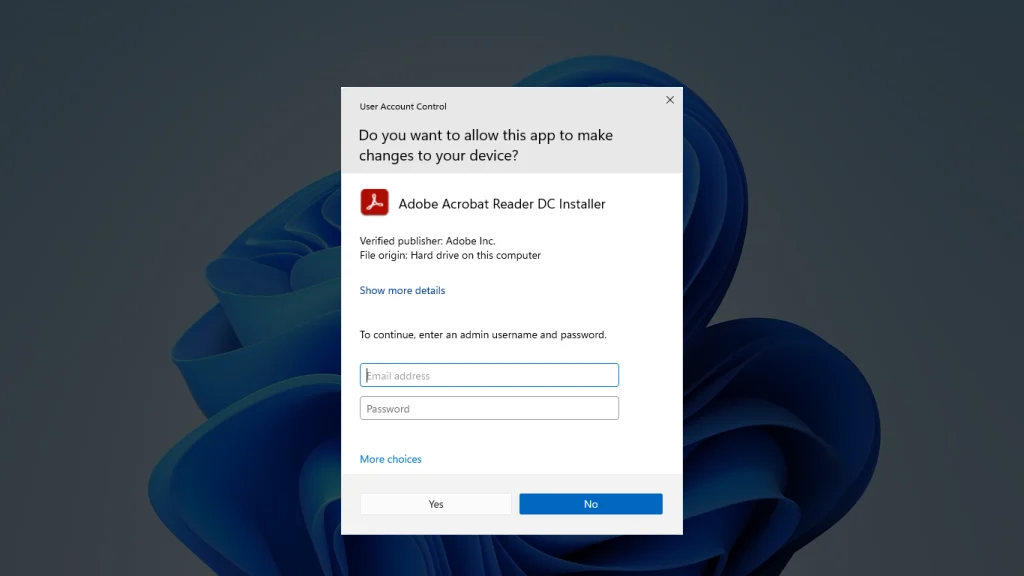
User Account Control (UAC) serves as Windows’ traditional mechanism for regulating administrative permissions. When an administrator signs into a PC, everyday applications launch with a restricted security token. Whenever a program tries to install software or alter system files, Windows displays a confirmation prompt.
Unfortunately, a UAC bypass lets malware running under a local admin account skip that prompt entirely. Consequently, the malicious payload acquires a full administrator token without alerting the user. Armed with elevated rights, attackers can tamper with system files, alter registry keys, disable defenses, or install persistent rootkits.
Importantly, Microsoft classifies UAC strictly as a defense-in-depth convenience rather than a formal security boundary. Under Microsoft’s security servicing criteria, standalone UAC bypasses do not qualify for bug bounties or emergency updates. Although engineers often harden abused components quietly in later releases, Microsoft rarely assigns CVE identifiers for UAC flaws. Therefore, Forshaw noted that Microsoft does not even need to treat this bypass as a formal security vulnerability.
Microsoft Has Already Patched the Flaw via Administrator Protection
Even without a formal CVE or public bulletin, Microsoft still resolves flaws reported by external researchers. Currently, the company is replacing legacy UAC Admin Approval Mode with Windows Administrator Protection. Specifically, this hardened architecture blocks many classic, low-level privilege escalation tricks.
Nine Preview Bypasses Fixed Ahead of General Release
During the Administrator Protection preview phase, Forshaw discovered nine distinct bypass methods. Fortunately, Microsoft patched all nine vulnerabilities before rolling out the feature to general availability. Now that the corrective update has shipped, Forshaw will likely publish a technical blog post and proof-of-concept exploit soon.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
