Weekly CVE Report Finds Oracle EBS, YOOtheme and FreeSWITCH Attacks Missing From CISA KEV
 Do Son
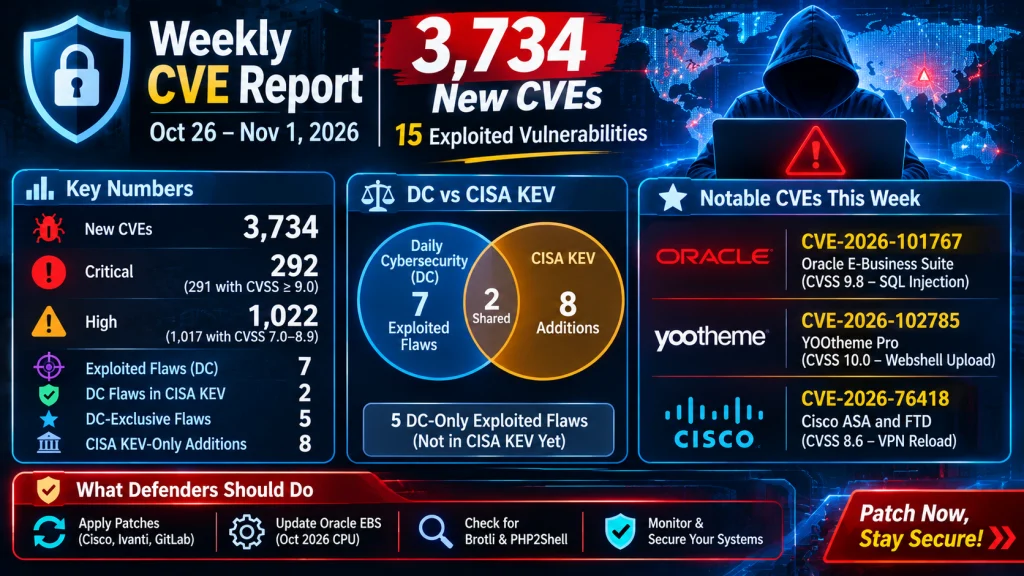
Between October 26 and November 1, 2026, CVE Watchtower logged 3,734 new CVEs. This weekly CVE report tracks 15 exploited vulnerabilities from that period. Daily Cybersecurity’s intelligence sources flagged seven of them. However, five of those seven are still missing from the CISA KEV catalog.
The Week in Numbers
- New CVEs: 3,734
- Critical: 292, with 291 scored CVSS 9.0 or higher
- High: 1,022, with 1,017 scored between 7.0 and 8.9
- Exploited flaws flagged by Daily Cybersecurity (DC): 7
- DC flaws that reached CISA KEV: 2
- DC-exclusive flaws: 5
- CISA KEV-only additions: 8
The Intelligence Lead: Daily Cybersecurity vs CISA KEV
For this weekly CVE report, we compared when DC marked each flaw exploited with when CISA added it to KEV. CISA data reflects catalog version 2026.10.30.
| CVE ID | Affected product | DC marked exploited | CISA KEV date added | Lead time |
|---|---|---|---|---|
| CVE-2026-76418 | Cisco Secure Firewall ASA and FTD | 2026-10-28 | 2026-10-29 | 1 day earlier |
| CVE-2026-118527 | Ivanti Connect Secure | 2026-10-30 | 2026-10-30 | Same day |
| CVE-2026-102785 | YOOtheme Pro | 2026-10-27 | Not listed | Not listed / Exclusive to DC |
| CVE-2026-101767 | Oracle E-Business Suite | 2026-10-28 | Not listed | Not listed / Exclusive to DC |
| CVE-2026-116690 | MLflow | 2026-10-28 | Not listed | Not listed / Exclusive to DC |
| CVE-2026-116779 | FreeSWITCH | 2026-10-29 | Not listed | Not listed / Exclusive to DC |
| CVE-2026-118539 | Drupal Commerce Core | 2026-10-29 | Not listed | Not listed / Exclusive to DC |
On shared flaws, DC led by one day on Cisco and matched CISA on Ivanti. Meanwhile, five flaws surfaced only through DC, including a maximum-severity YOOtheme bug. This is a feed-to-feed comparison, not a controlled benchmark, and “Not listed” flaws may still join KEV later.
Exploited Vulnerabilities From CISA KEV Only
| CVE ID | Affected product | Vulnerability type | CVSS | CISA KEV date added |
|---|---|---|---|---|
| CVE-2026-109618 | PHP (PHP2Shell) | Memory corruption | 9.2 | 2026-10-26 |
| CVE-2026-109619 | PHP (PHP2Shell) | Stale request-state memory | 9.2 | 2026-10-26 |
| CVE-2026-48356 | Adobe Commerce and Magento | Dangerous file upload | 9.3 | 2026-10-27 |
| CVE-2026-111497 | Google Brotli | Decoder out-of-bounds write | 9.2 | 2026-10-27 |
| CVE-2026-41709 | Broadcom VMware ESX | Insufficient logging | 2.7 | 2026-10-28 |
| CVE-2026-46300 | Linux kernel | Missing variable initialization | 7.8 | 2026-10-28 |
| CVE-2026-97229 | GitLab CE/EE | Integer overflow | 10.0 | 2026-10-29 |
| CVE-2026-111357 | Ivanti Connect Secure | Missing authentication | 7.0 | 2026-10-30 |
Notably, the two PHP2Shell flaws were DC exclusives in last week’s report. CISA added both on October 26.
The Flaws That Stand Out
Oracle E-Business Suite (CVE-2026-101767, CVSS 9.8)
This unauthenticated SQL injection sits in the Application Object Library of Oracle EBS 12.2.3 to 12.2.15. Oracle fixed it in its October 20 Critical Patch Update. Then, on October 27, Defused said its EBS decoys recorded “exploratory exploits” against the flaw. Shadowserver tracks over 670 exposed EBS instances. Oracle has not yet confirmed in-the-wild exploitation.
YOOtheme Pro (CVE-2026-102785, CVSS 10.0)
YOOtheme Pro 5.0.0 to 5.0.52 lets unauthenticated attackers write a webshell through its image handler. Palo Alto Networks Unit 42 confirmed in-the-wild attacks on October 26. In those attacks, automated scanners dropped PHP webshells hidden in image files. Version 5.0.53 fixes the bug.
Cisco ASA and FTD (CVE-2026-76418, CVSS 8.6)
A crafted request to the SSL remote access VPN can force Cisco firewalls to reload. Cisco says it knows of active exploitation, though it has not named the attackers. The bug needs secondary authentication on a tunnel group. Shadowserver counts more than 51,000 exposed ASA SSL VPN devices.
What Defenders Should Do
- Patch internet-facing gear first: Cisco ASA and FTD, Ivanti Connect Secure and GitLab.
- Apply Oracle’s October 2026 Critical Patch Update to every EBS 12.2 instance.
- Update YOOtheme Pro to 5.0.53, then search media folders for stray PHP files.
- Upgrade FreeSWITCH to 1.11.3, since the vendor confirms attacks in the default setup.
- Move MLflow to 3.17.0 and Drupal Commerce Core to 3.3.13 or 8.x-2.41.
- Finish PHP2Shell and Brotli patching across appliances, not just servers.
Get the Full Data
This premium content is securely locked. You must upgrade your subscription to access the full threat intelligence report, including detailed mitigation steps, deep-dive analysis, and active exploitation metrics. Your attempt to inspect the DOM will only reveal this placeholder text. Please support our work to read the actual coverage.
This premium content is securely locked. You must upgrade your subscription to access the full threat intelligence report, including detailed mitigation steps, deep-dive analysis, and active exploitation metrics. Your attempt to inspect the DOM will only reveal this placeholder text. Please support our work to read the actual coverage.
Unlock Premium Threat Intelligence
This is a premium content. Upgrade to Pro or Team to unlock full access and remove all reading restrictions.
 Buy Me a Coffee
