 Do Son
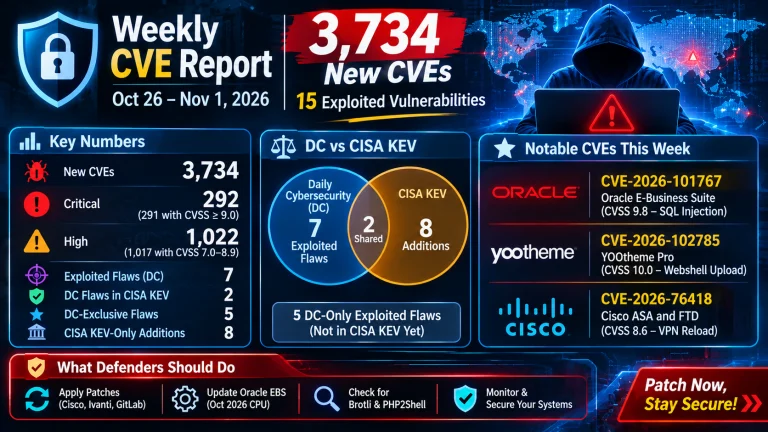
Our weekly CVE report for Oct 26-Nov 1, 2026 tracks 3,734 new CVEs and 15 exploited vulnerabilities, including Oracle EBS flaws not in CISA KEV.
FreeSWITCH
FreeSWITCH vulnerability CVE-2026-116779 (CVSS 9.8) is exploited in the wild, letting a SIP MESSAGE run server commands. Upgrade to 1.11.3 now.
A FreeSWITCH vulnerability in api-chat enables remote code execution and is exploited in the wild. Upgrade to 1.11.3 now to stay safe.

Two pre-auth FreeSWITCH heap buffer overflow bugs (CVE-2026-49841, CVE-2026-49840) hit mod_verto and libesl. Update to v1.11.1 to stay safe.

CVE-2023-51443, with a CVSS score of 7.5, exposes FreeSWITCH to DoS attacks during the delicate handshake phase of the DTLS protocol