 Do Son
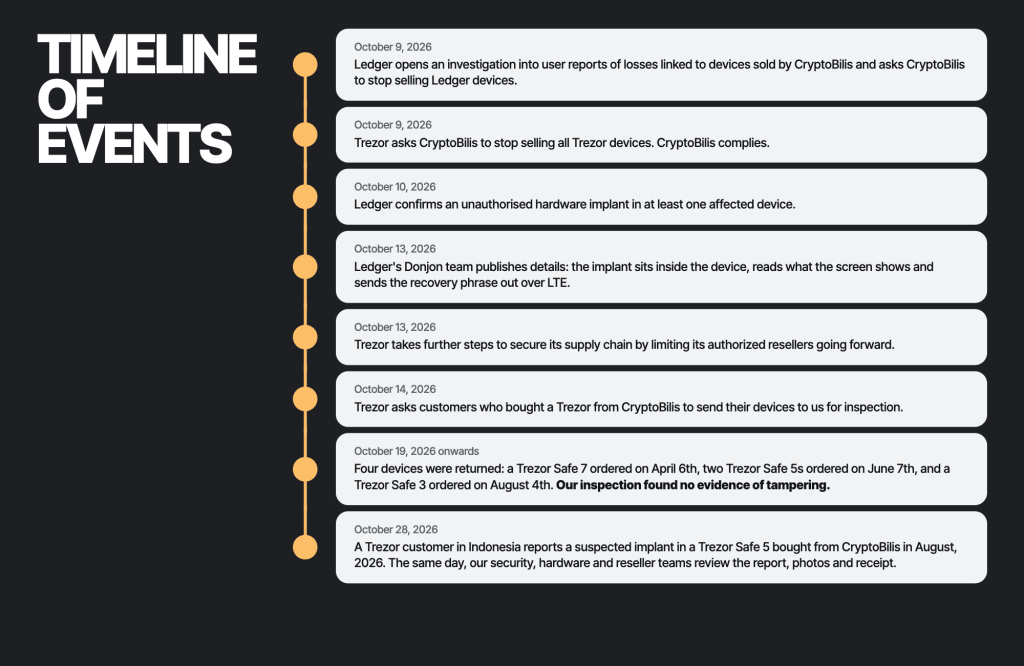
Hardware wallet manufacturer Trezor issued an urgent security alert regarding physical supply chain tampering. Specifically, security investigators identified a sophisticated Trezor hardware wallet implant hidden inside an altered Safe 5 unit. A customer originally purchased the compromised device from Southeast Asian distributor CryptoBilis. Furthermore, the clandestine module captured recovery seed phrases directly from the internal display and transmitted confidential credentials over cellular networks.
Interception Circuitry Sandwiched Beneath the Display
The hardware sabotage represents an unusually brazen physical supply chain attack. An Indonesian customer purchased the affected device in August 2026. After noticing physical discrepancies, the buyer dismantled the chassis on October 28 and uncovered rogue components.
Forensic teardowns revealed a custom secondary circuit board lodged tightly between the primary motherboard and the screen. This parasitic board housed an antenna alongside an integrated 4G LTE transceiver. Consequently, the implant silently recorded recovery seed phrases during initial device setup. Whenever users powered the hardware, the module transmitted captured telemetry to adversary infrastructure. As documented in the official Trezor security advisory on the CryptoBilis incident, the alert customer evacuated funds before suffering losses.
Reseller Compromise and Links to Covert Operations
Crucially, this physical breach mirrors an earlier intrusion targeting hardware manufacturer Ledger. Both incidents trace directly to distribution channels managed by regional retailer CryptoBilis. Mysterious buyers covertly acquired the dealership in March 2026 while forcing personnel to sign non-disclosure covenants.
Subsequently, intelligence analysts linked the covert buyout to North Korean state-sponsored cyber operations. Therefore, these physical implants suggest an aggressive campaign targeting cryptocurrency cold storage at the distribution level. Fortunately, Trezor confirmed zero verified financial theft among active customers thus far.
Emergency Mitigation and Device Replacement Guidelines
Trezor expanded its security warning to cover all models distributed by CryptoBilis since March 2026. This advisory includes orders fulfilled via third-party marketplaces such as Tokopedia.
Immediate Protective Measures for Owners
Impacted cryptocurrency holders must transfer their digital assets to verified secure environments immediately. First, users should establish fresh private keys on an uncompromised wallet platform. In addition, affected individuals can contact Trezor customer support to request free hardware replacements or store credit. Ultimately, hardware wallet users must purchase devices exclusively through direct manufacturer channels to guarantee physical integrity.
Support Our Threat Intelligence
Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
