 Do Son
A uutils coreutils vulnerability (CVSS 9.9) let translation files inject code; details and a proof-of-concept are now public. Upgrade to uucore 0.12.0.
supply chain attack
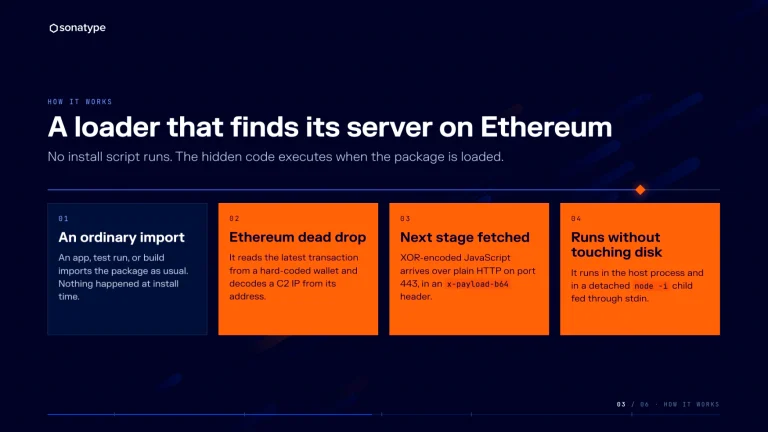
Sonatype uncovers the PolinRider loader in 12 releases across 10 hijacked packages. See how the npm PolinRider loader uses Ethereum to fetch malware.
cPGuard supply chain attack: an update channel compromise pushed a backdoor in versions 5.88.12-5.88.19. Update to 5.88.25 and rotate credentials.

Pluto Research exposes Hugging Face malware. This Hugging Face malware campaign drops cryptominers and backdoors on self-hosted AI servers.
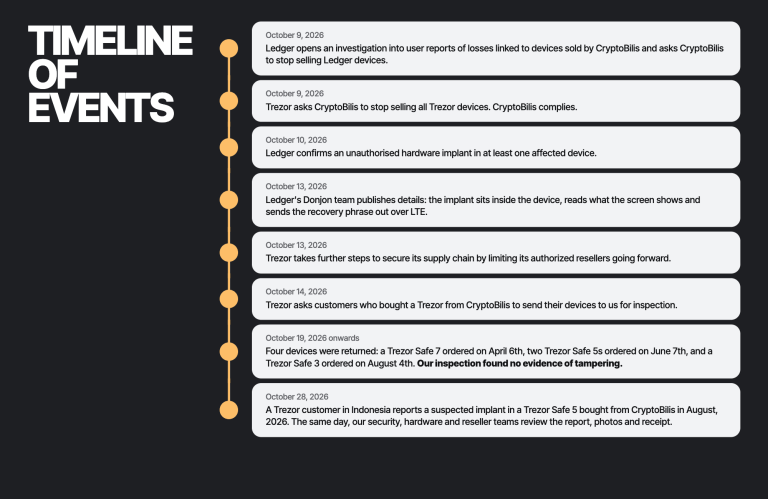
Trezor issued an alert after discovering a Trezor hardware wallet implant with a 4G module sold by compromised Southeast Asian reseller CryptoBilis.
Cursor removed a malicious Claude Code extension backdoor. Learn how the Cursor Claude Code extension backdoor planted SSH keys on up to 5,000 developer PCs.

A Polymarket supply chain attack compromised a third-party analytics script to deploy a crypto wallet drainer, prompting an immediate trading halt.
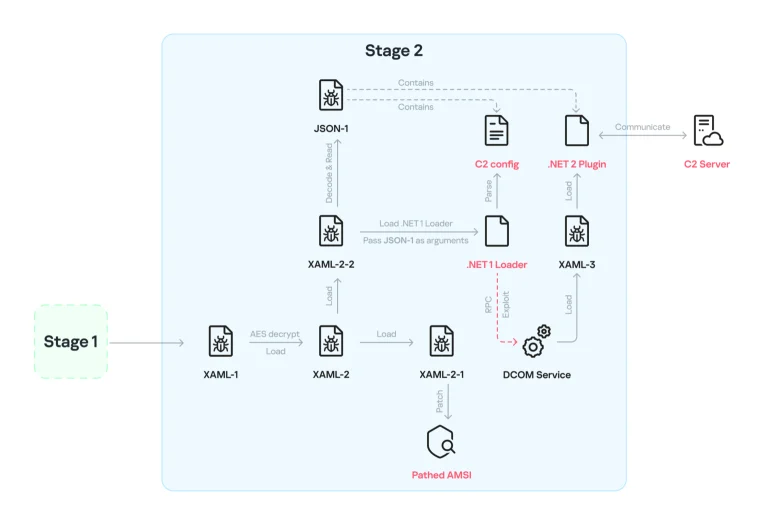
NetamLoader, a new XAML-based .NET loader, points to a supply chain attack on a custom Windows build used by government entities in Asia.
An ARTEX AI agent campaign against IT and software vendors overlaps with Storm-0940, targeting Okta, Entra ID, and AWS Cognito logins.
Railway security incident: attackers may have decrypted Railway environment variables. Builds are paused. Rotate API keys and credentials now.
Hackers abused a SkyKick API secret in a ConnectWise Cloud Backup breach, accessing 300+ Microsoft 365 tenants and planting rogue app credentials.
An OVHcloud CLI attack swapped GitHub release files with a secret-stealing binary. Learn which versions are hit in this supply chain attack.
UpdraftPlus data breach exposed customer data and keys now used in an UpdraftCentral backdoor campaign. Update to 1.26.12 and check your sites.
Our weekly CVE report for Oct 12-18, 2026 tracks 5,499 new flaws and 12 exploited vulnerabilities, with CISA KEV trailing by up to 8 days.
Update Rank Math SEO PRO to 3.0.124 now. CVE-2026-111862 is a critical supply-chain compromise actively exploited in the wild via embedded malware.
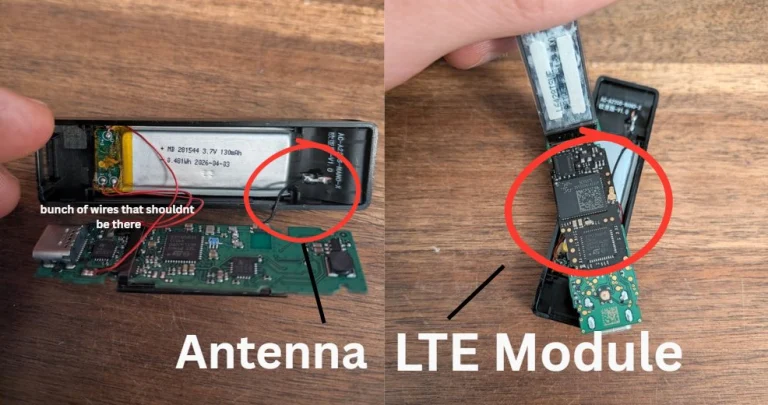
A devastating Ledger supply chain attack has reached Europe. Hackers are embedding malicious LTE modules into hardware wallets to steal cryptocurrency.
A fake Web3 accelerator used malicious npm packages to drop stealers on macOS and Windows and reroute AI coding agent traffic to its servers.
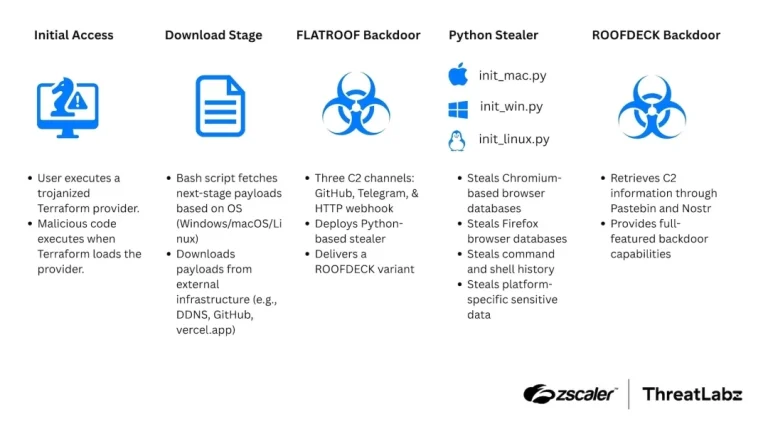
Suspected TraderTraitor hackers used a trojanized Terraform provider to drop FLATROOF and ROOFDECK malware on macOS, Linux, and Windows.
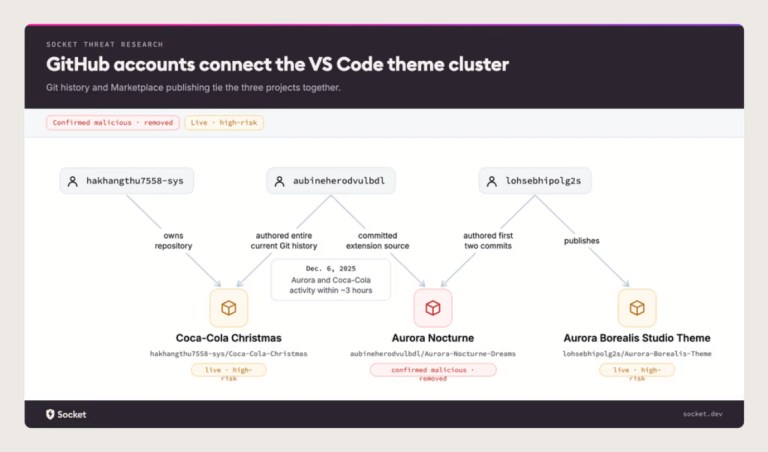
Socket links GlassWorm VS Code themes to malicious VS Code extensions with 8,000+ installs, including a Coca-Cola theme. See how to check yours.
Microsoft details NeedyMantis malware, a modular backdoor that uses DLL sideloading to keep long-term access in telecom, academic, and government networks.
Learn how to detect malicious Terraform providers. New malicious Terraform providers spread Graphalgo Go malware through typosquatted packages.
Discover the critical MemTensor MemOS compromise details. This MemTensor MemOS compromise targets AI developers via malicious npm and PyPI packages.