 Do Son
The Coder registry attack hijacked Cloudflare IPs to serve malicious Terraform modules from registry.coder.com, stealing developer secrets.
supply chain attack
Hackers hijacked BGP routing to intercept Virtualizor updates and distribute malware. Learn how this complex supply chain attack bypassed critical security checks.
A Virtualizor supply-chain attack used a 33-hour BGP hijack to deliver malicious updates, planting root backdoors on VPS hosts. Back up your data now.
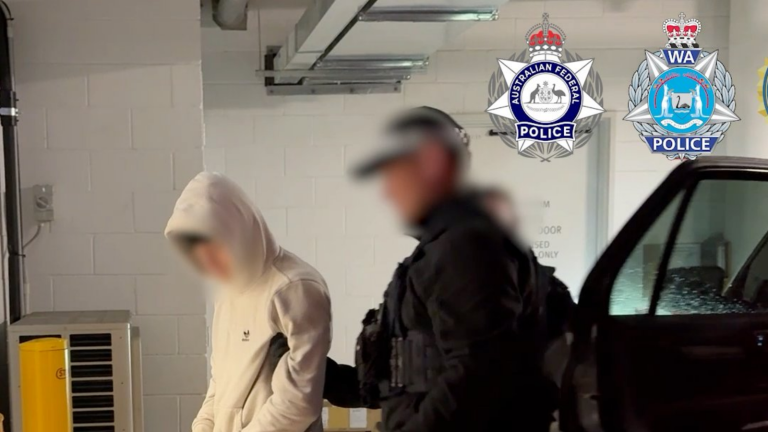
Discover the details of the TeamPCP hackers arrested in Australia for executing devastating open-source supply chain attacks using the Mini Shai-Hulud worm.
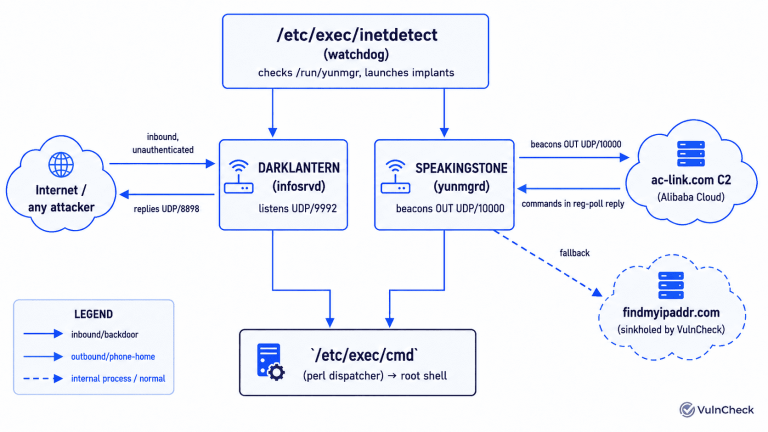
VulnCheck found a ZBT router backdoor in firmware, tracked as CVE-2026-74232 and CVE-2026-74233, granting unauthenticated root over the internet.
A Rust supply chain attack poisoned arrayref and two other crates to run malware at build time. Wiz ties the infrastructure to DPRK campaigns.

GEEKOM's official site served backdoored AMD mini PC drivers since December 2024 via a compromised legacy support page still indexed by Google.

ChainDrop npm worm infected 400+ packages, stealing cloud keys and CI secrets via blockchain C2. Unit 42 details the full attack chain and fixes.

A BdThemes supply chain attack poisoned a plugin API feed to run silent XSS in admin browsers, creating rogue admins across WordPress sites.
QuickFox supply chain attack trojanizes a VPN app to deploy the FDMTP implant on Windows users. FortiGuard Labs ties it to Twill Typhoon.

XCSSET v40 malware infects macOS developers through poisoned Xcode projects on GitHub, then hides in memory. Unit 42 found 17 modules and Chrome hijacking.

Group-IB uncovered XMRig Linux PAM abuse that lets a fileless Monero miner regenerate across user accounts and vanish from disk forensics.

Adform experienced a cyber attack where hackers altered ad scripts to hijack cryptocurrency addresses. Learn how this supply chain attack affects users.

A new npm supply chain attack hijacked keyv and dozens of packages, spreading Shai-Hulud malware that steals cloud and CI/CD secrets. Rotate keys now.
Amazon ties North Korean hackers to open-source supply chain attacks on the axios, debug, and chalk NPM packages. Here's how the campaign worked.

ENKI WhiteHat traced a Kimsuky Gomir variant into South Korean groupware vendors, plus a new DriveTroy backdoor that hides its C2 in Google Drive.

A GitHub Actions abuse campaign turned thousands of workflows into cPanel and WHM exploitation infrastructure, harvesting cloud and payment credentials.
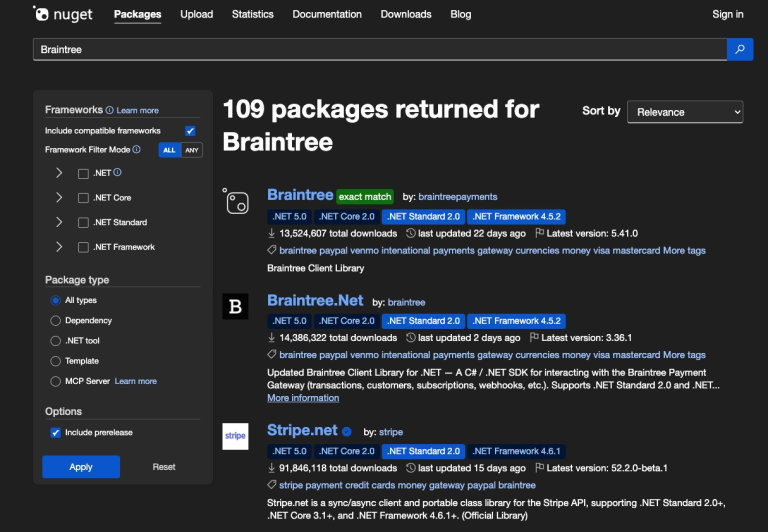
A malicious NuGet package, Braintree.Net, acts as a credit card skimmer and steals merchant API keys. The Braintree NuGet typosquat hits .NET devs.
Socket links the PolinRider supply chain attack to North Korean hackers. The campaign hid loaders in 108 open-source packages across four ecosystems.

The FBI issued an alert about a TeamPCP supply chain attack. The group uses malicious code to conduct a software supply chain compromise against developers.

New Lazarus npm malware masquerades as Rollup polyfills, hiding remote-access and wallet-theft payloads. JFrog uncovered six malicious packages.

LastPass confirms the Klue breach exposed customer CRM data via OAuth token theft in Salesforce. Vaults stayed safe. Here's what to know.