
 Do Son
Panther uncovers "OtterCookie," a North Korean npm campaign hiding malware in benign wrappers. It steals crypto wallets and installs SSH backdoors. Audit now!
supply chain attack

OpenAI revokes legacy macOS certificates after a malicious @Axios library incursion. Update ChatGPT and Codex by May 8, 2026, to avoid software failure.
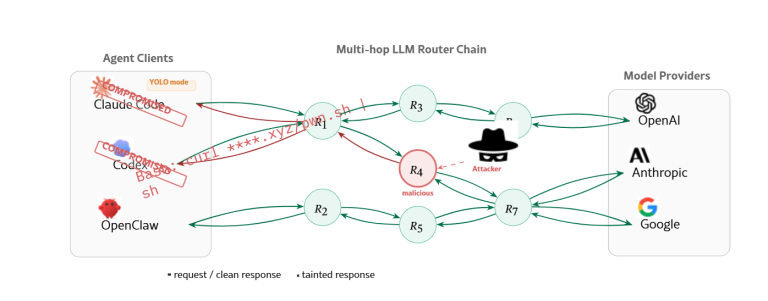
New research reveals massive security gaps in AI API aggregators. From stolen crypto to leaked tokens, learn why your API hub might be a Man-in-the-Middle trap.
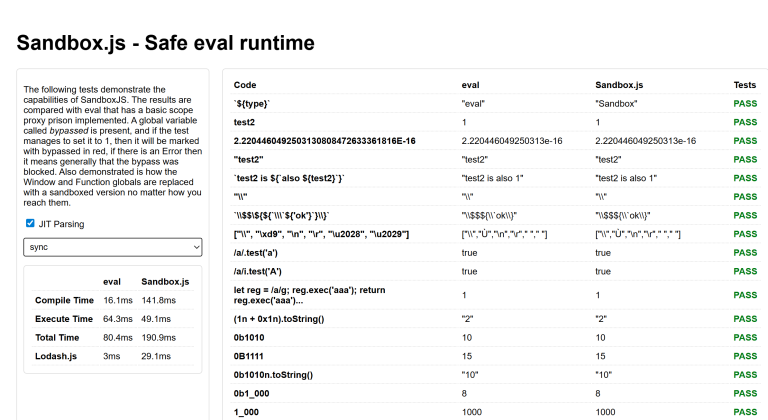
CVE-2026-34208: A critical 10.0 flaw in SandboxJS allows code to escape and poison host objects like Math.random. Secure your environment—update immediately!
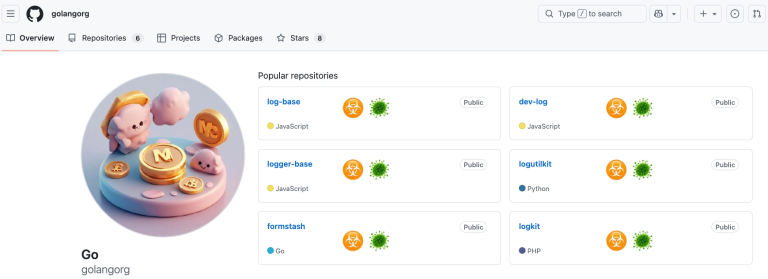
North Korea’s "Contagious Interview" campaign expands to 1,700+ malicious packages across npm, PyPI, and more. Learn how to protect your dev environment.
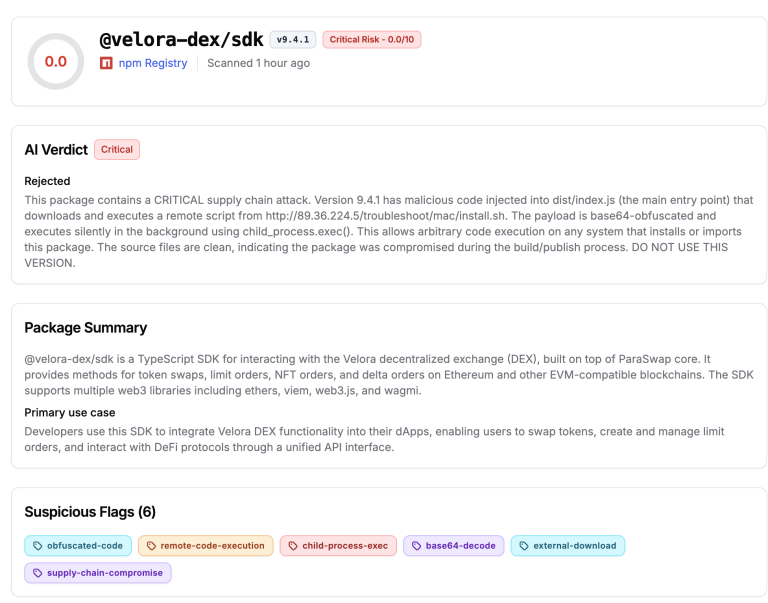
A malicious update to @velora-dex/sdk (v9.4.1) drops a stealthy macOS backdoor on import. Learn how to detect the zsh.profiler infection and rotate secrets.

Cisco Talos uncovers UAT-10608, an automated campaign using "NEXUS Listener" to harvest Next.js credentials via React2Shell. Patch your cloud tokens now!

A massive supply-chain attack hit the European Commission via a compromised Trivy update. 340GB of data was leaked by ShinyHunters. Rotate your AWS keys!

The Axios npm hijack exposed millions to a RAT. Discover how North Korean-nexus actor UNC1069 used a masterful phishing ruse to bypass 2FA and steal credentials.
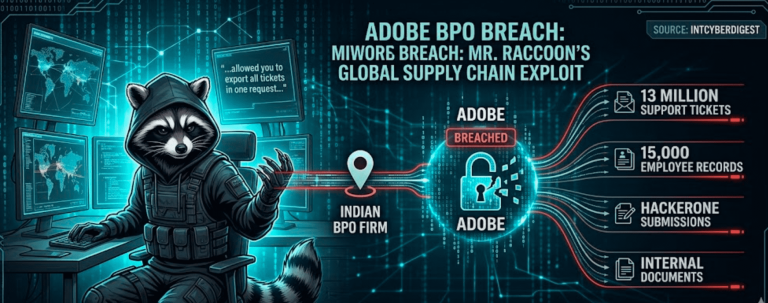
13M Adobe tickets leaked! Mr. Raccoon bypassed elite defenses by targeting a BPO partner in India. See how the "human element" cracked the supply chain.

Check Point reveals "TrueChaos," an espionage campaign exploiting a TrueConf zero-day (CVE-2026-3502) to drop malware via fake updates. Patch to 8.5.3 now.

Google warns of a massive Axios supply chain attack. Versions 1.14.1 & 0.30.4 deploy the WAVESHAPER.V2 backdoor via a hijacked NPM account. Patch now!

Axios versions 1.14.1 & 0.30.4 have been poisoned. A hijacked maintainer account is dropping a RAT via postinstall scripts. Revert to safe versions now!
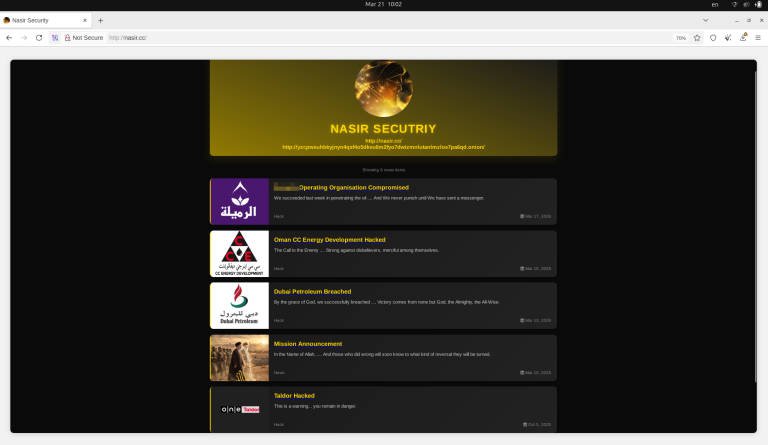
Resecurity uncovers Nasir Security, an Iranian threat actor using supply chain attacks and psy-ops to target Middle East energy vendors and leak blueprints.

Jamf Threat Labs uncovers GhostClaw, a macOS threat exploiting GitHub stars and AI workflows to steal credentials. Protect your dev environment today!
GoHarbor's Harbor faces a critical 9.4 CVSS flaw (CVE-2026-4404). Default admin passwords allow total registry compromise and image poisoning. Update now.
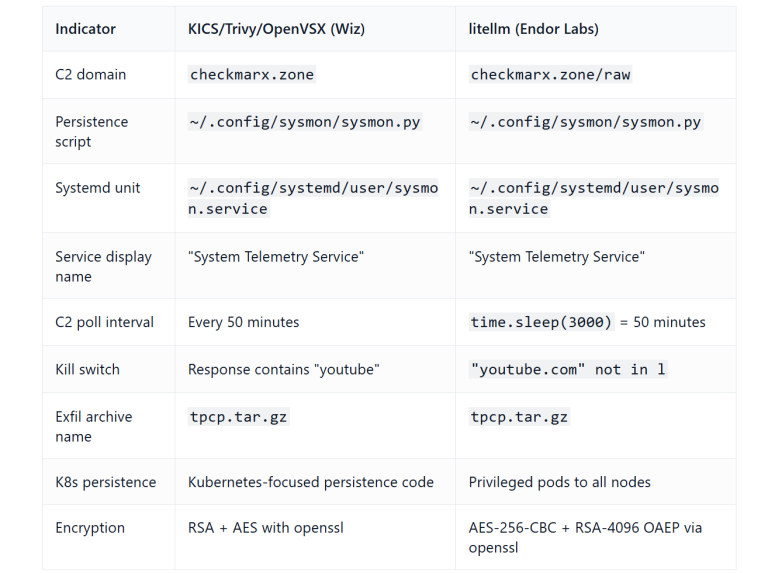
95M-download LiteLLM library hijacked on PyPI. TeamPCP's backdoor steals cloud tokens and hijacks Kubernetes clusters. Check for version 1.82.8 now.

Sophos uncovers Keenadu, a persistent Android firmware backdoor embedded in core libraries that gives attackers total control via the Zygote process.

Checkmarx warns of a supply chain breach on the OpenVSX registry and KICS GitHub Action. Malicious plugins were active briefly on March 23. Update now.
Researchers reveal Infostealer.Speagle, a "parasitic" malware hijacking Cobra DocGuard infrastructure to mask the theft of sensitive ballistic missile data.
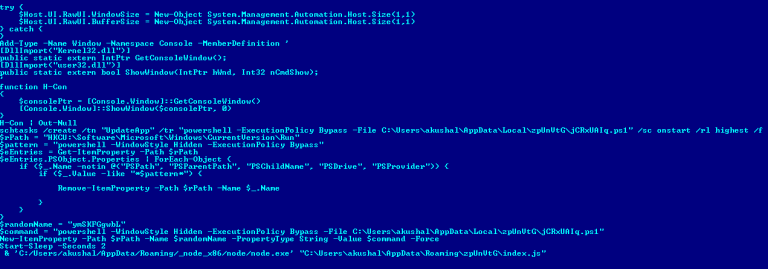
Bitdefender uncovers a malicious Windsurf IDE extension using the Solana blockchain as an unblockable C2 to steal developer credentials and source code.
Eclypsium researchers reveal how compromised IP-KVM switches bypass EDR and software security to grant attackers total, BIOS-level system takeover.