
 Do Son
Lotus Blossom hijacked Notepad++ updates to target admins. The supply chain attack deployed Chrysalis backdoor. Update to v8.9.1 immediately.
supply chain attack

Malicious Outlook add-in "AgreeTo" steals 4,000+ credentials. Attackers hijacked the abandoned tool in the official store. Uninstall immediately.

Lazarus Group targets crypto developers with fake job offers in new "Graphalgo" campaign. Malicious npm packages deliver multi-stage malware. Stay alert.

Critical dYdX supply chain attack: Compromised npm & PyPI packages steal seed phrases & deploy RATs. Remove @dydxprotocol/v4-client-js immediately.

Lotus Blossom compromises Notepad++ infrastructure to deploy "Chrysalis" malware. Rapid7 reveals the group using Microsoft Warbird to evade detection.

GlassWorm malware found in Open VSX extensions. Hackers stole AWS & SSH keys from macOS devs using Solana C2. 22k+ downloads affected. Check your tools.

VirusTotal warns of massive supply chain attack on OpenClaw. Hackers use fake "skills" to deploy malware like Atomic Stealer. Verify your agents.

Notepad++ confirms update infrastructure was compromised by state-sponsored actors targeting specific users. Update to version 8.8.9 immediately.
Critical supply chain attack hits eScan antivirus. Hackers hijacked updates to install malware and disable the AV. Manual patch required.
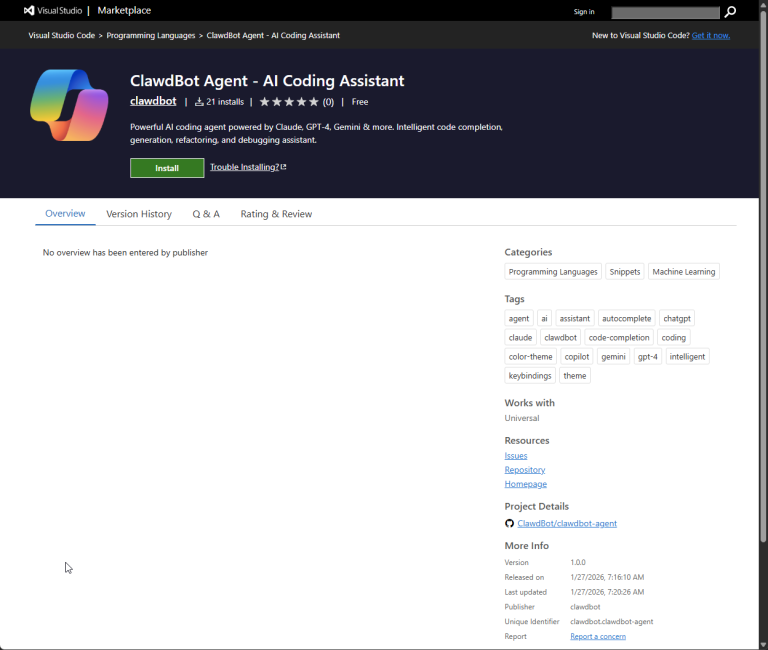
Malicious "ClawdBot Agent" VS Code extension exposed. Functioning as a real AI tool, it silently dropped malware. Microsoft removed it after 21 installs.

Attackers exploit GitHub forks ("Repo Squatting") to push HijackLoader malware via official-looking URLs. Technique remains active; verify all downloads.

Malicious npm package "ansi-universal-ui" drops "G_Wagon" infostealer to steal cloud keys and wallets. Check for .gwagon_status and rotate creds now.
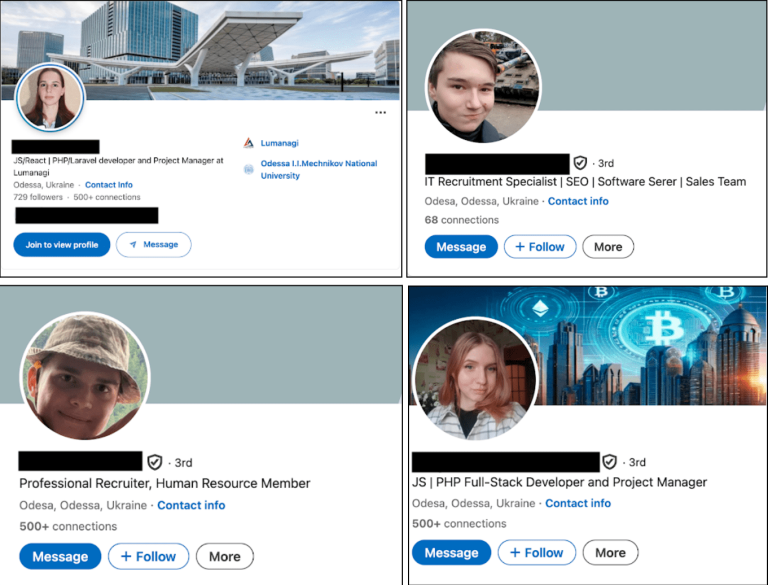
North Korean group PurpleBravo uses fake job offers to breach IT firms. The "Contagious Interview" campaign deploys malware via coding tests.

Official EmEditor installer hijacked to push malware. This supply chain attack steals credentials & evades detection. Check your logs for these domains.
CISA adds 4 flaws to KEV, including critical Versa Concerto auth bypass (CVSS 9.2) & malicious "Prettier" package. Patch by Feb 12 to stop active attacks.

Malicious PyPI package "sympy-dev" impersonates SymPy to install XMRig miners via fileless execution. Check your dependencies immediately.

Attackers are hijacking Linux Snap Store apps by registering expired developer domains. Malicious updates target crypto wallets. Secure your accounts now.

Critical Orval flaw CVE-2026-23947 (CVSS 9.3) allows code injection via OpenAPI specs. Update to v8.0.2 now to secure your generated TypeScript clients.

"Contagious Interview" evolves: DPRK hackers now abuse VS Code tasks & npm install to breach developer systems. Jamf warns of new infection vectors.
Trend Micro reveals Evelyn Stealer, a malware campaign weaponizing Visual Studio Code extensions. It uses DLL injection to steal developer secrets & crypto.

Wiz reveals "CodeBreach": A regex typo in AWS CodeBuild could have let hackers hijack the AWS Console via the JS SDK. Issue is now patched.

Sansec uncovers a keylogger on a major US bank's employee portal. 200,000 staff at risk of credential theft via hidden "side door" malware.