
 Do Son
Proofpoint details 'CursorJack', a novel exploit using malicious MCP deeplinks in the Cursor AI editor to execute arbitrary code on developer machines.
supply chain attack

StepSecurity uncovers a supply chain attack where a verified GitHub org, dev-protocol, was hijacked to spread malicious Polymarket bots and steal crypto.

Socket Research exposes how GlassWorm malware abuses Open VSX dependencies for transitive delivery of an RCE backdoor using Solana blockchain dead drops.

Socket uncovers a Packagist supply chain attack targeting Vietnamese OphimCMS streaming sites with trojanized themes linked to sanctioned entity FUNNULL.

Aikido uncovers a supply chain attack via AstrOOnauta, backdooring two popular React Native packages to steal crypto wallets and developer credentials.
Critical 10.0 CVSS flaw in SandboxJS (CVE-2026-26954) allows attackers to escape the sandbox and achieve Remote Code Execution. Patch to version 0.8.34 now.
A critical 9.4 CVSS tag poisoning attack (CVE-2026-31976) hit the xygeni-action GitHub Action, injecting a C2 backdoor into CI/CD pipelines. Update now.
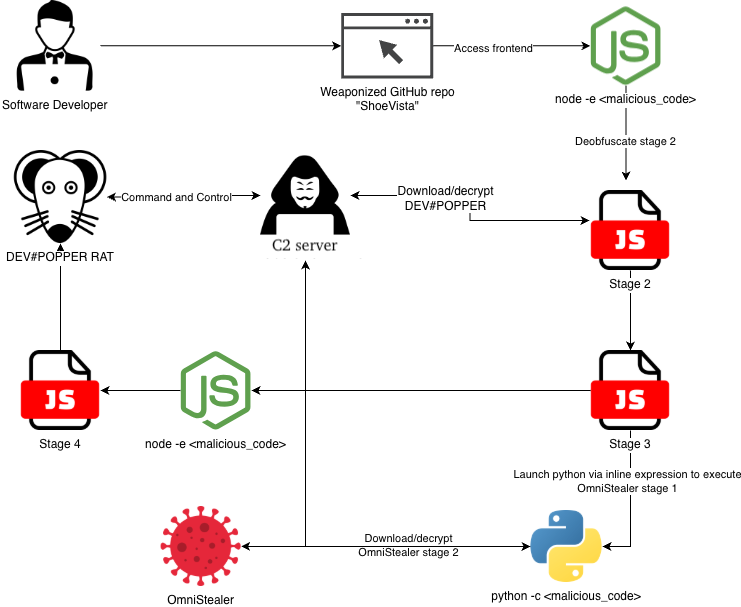
eSentire exposes DEV#POPPER, a North Korean RAT hiding in GitHub repos. It uses blockchain to deploy OmniStealer, targeting crypto and dev secrets.
A critical 9.3 CVSS flaw (CVE-2026-25921) in Gogs' LFS handling allows attackers to silently overwrite repository files, risking severe supply-chain attacks.

Socket researchers uncover a Packagist supply chain attack where fake Laravel utility packages secretly install a persistent Remote Access Trojan (RAT).
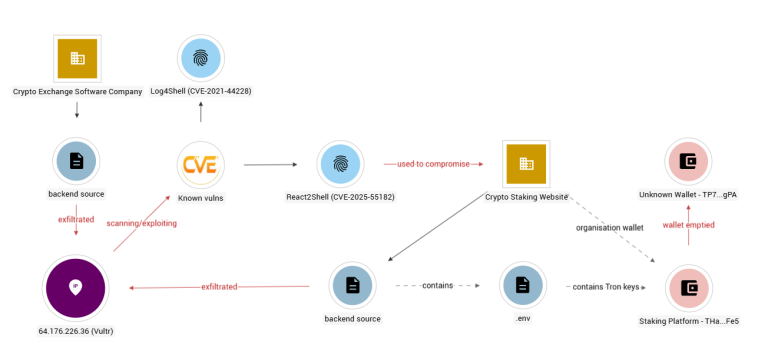
Ctrl-Alt-Intel exposes a suspected DPRK campaign using an 'Amazon Kill Chain' and React2Shell to systematically breach crypto exchanges and steal code.
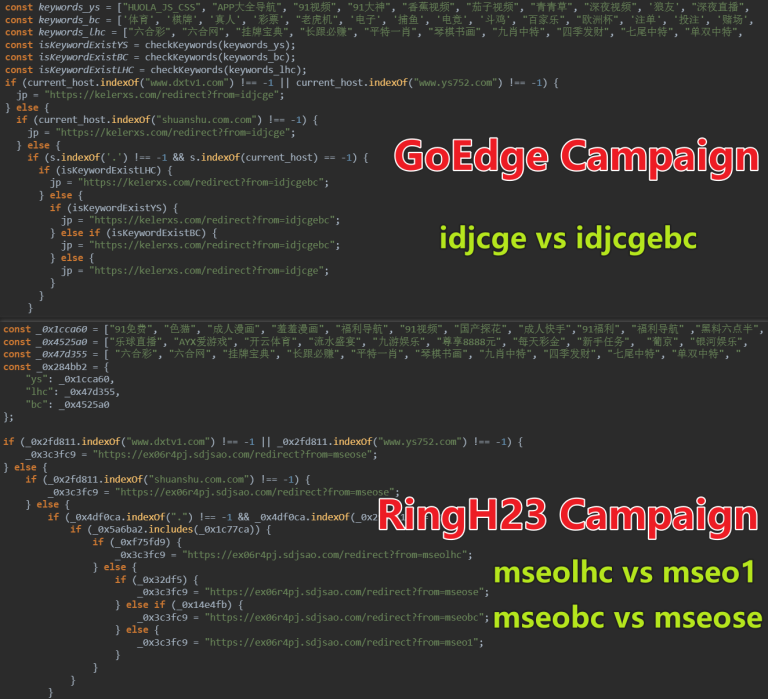
XLab researchers reveal the return of OFAC-sanctioned Funnull. The group is using the new RingH23 framework to hijack CDNs and poison supply chains.

Socket reveals how an AI bot hijacked the Aqua Trivy VS Code extension, using prompt injection to turn developer AI assistants into stealthy data thieves.

OpenSSF warns of "hackerbot-claw," an autonomous AI bot exploiting GitHub Actions to hijack repositories. Secure your CI/CD pipeline before it’s too late.

Socket uncovers "StegaBin," a North Korean malware campaign hiding C2 URLs in Pastebin essays to steal developer secrets via 26 typosquatted npm packages.
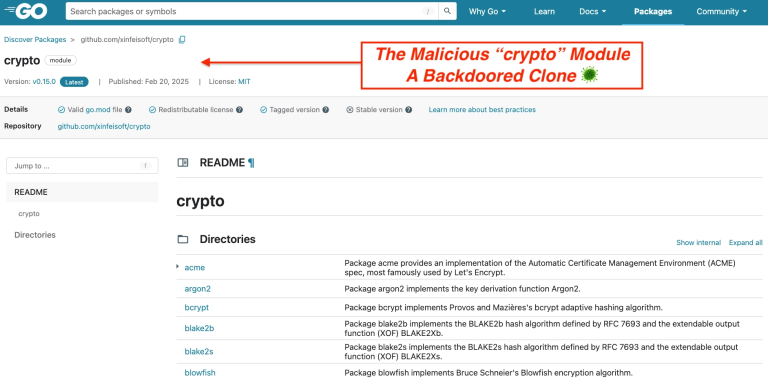
Socket uncovers a malicious Go module mimicking golang.org/x/crypto. It steals passwords via ReadPassword and deploys the Rekoobe backdoor on Linux systems.
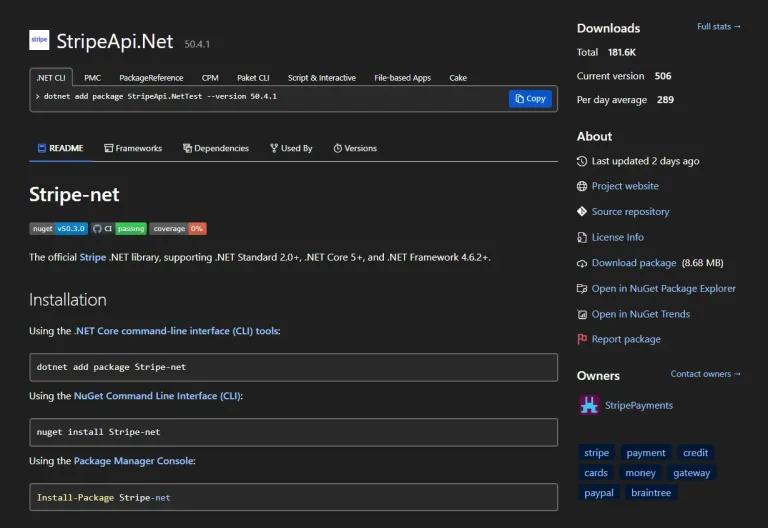
ReversingLabs uncovers a malicious NuGet package mimicking Stripe.net. Discover how attackers are targeting the financial sector via supply chain poisoning.

Tenable uncovers "ambar-src," a malicious npm package mimicking "ember-source." It uses preinstall scripts to deploy reverse shells and Apfell malware.
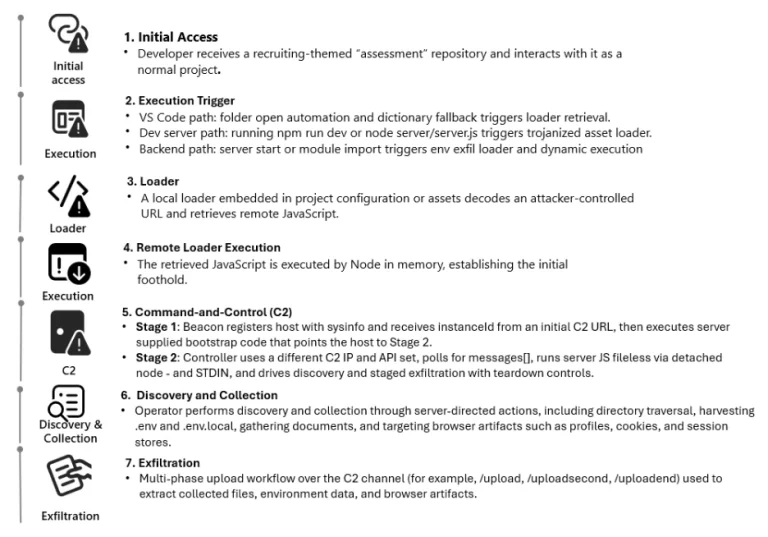
Microsoft warns of a new campaign targeting engineers via fake Next.js technical assessments. Malware hides in VS Code tasks and npm scripts to steal secrets.
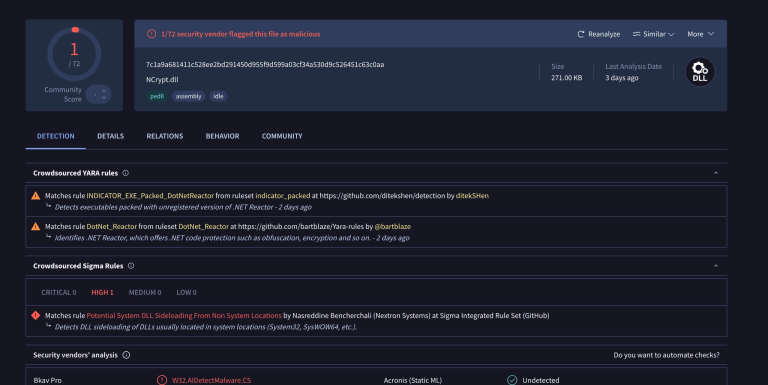
Socket researchers uncover a NuGet supply chain attack using "NCryptYo" to hijack ASP.NET apps. Attackers inject backdoors into production authorization layers.
Insikt Group exposes GrayCharlie compromising WordPress sites & US law firms. Attackers use "ClickFix" fake CAPTCHAs to deploy the NetSupport RAT.
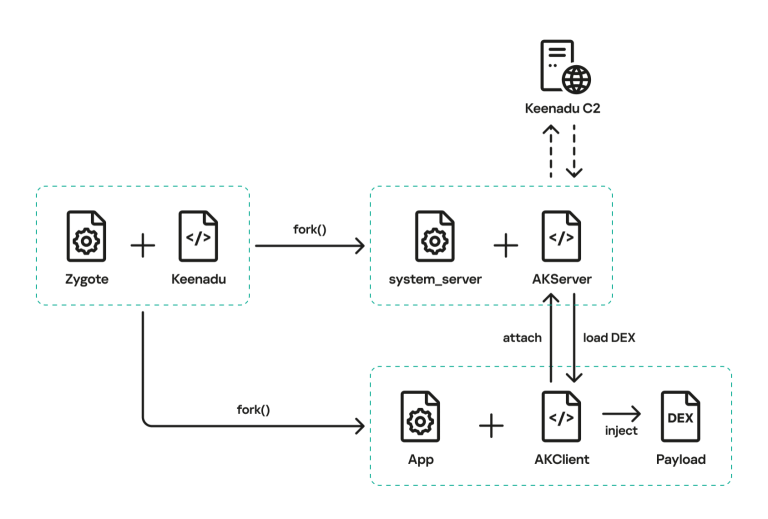
Kaspersky uncovers Keenadu, a firmware-level Android backdoor infecting the Zygote process. This pre-installed malware gives attackers full control.