
 Do Son
GlassWASM malware hides WebAssembly payloads in trojanized Open VSX extensions, abusing Solana memos for stealthy command-and-control.
supply chain attack
A Mastra supply chain attack compromised 140+ npm packages, using the typosquatted easy-day-js dependency to drop a crypto-stealing infostealer.
A ShapedPlugin supply chain attack (CVE-2026-10735) injected malware into WordPress Pro plugins. Discover the impact and how to protect your site today.
The Uncanny Automator breach exposed customer data and pushed a backdoored plugin build (7.3.0.5). Here's what happened and how to secure your site.

A massive PyPI supply chain attack has hit developers. Learn how Socket malware detection uncovered the Hades cluster stealing cloud credentials.
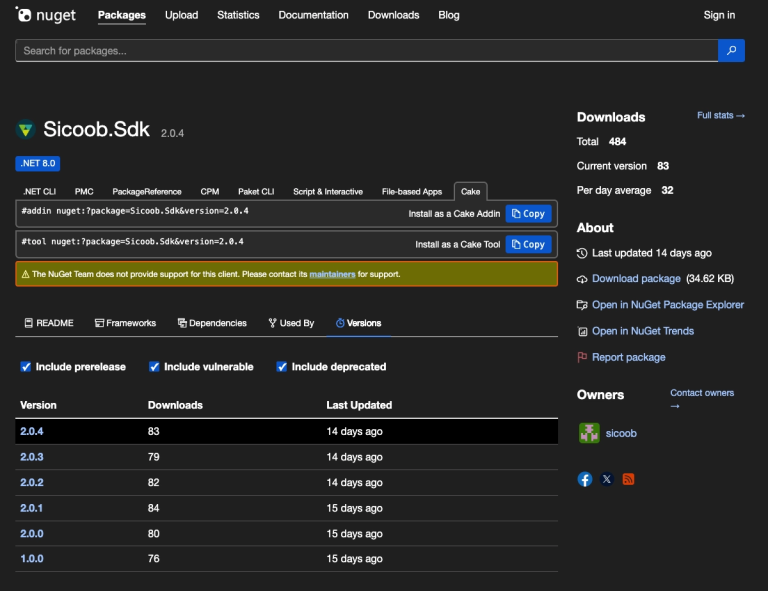
A dangerous Sicoob SDK banking malware campaign triggers a major NuGet supply chain attack. Learn how it exfiltrates private financial certificates.

A dangerous macOS cryptocurrency malware wave drives the latest JINX-0164 developer campaign. Learn how to secure your repositories now.

Read our weekly threat intelligence briefing. Our active vulnerability report reveals new zero-day exploits and CISA KEV additions for May 2026.

Microsoft uncovers a massive npm dependency confusion attack targeting enterprise infrastructure. Learn how these malicious packages discovered run code.
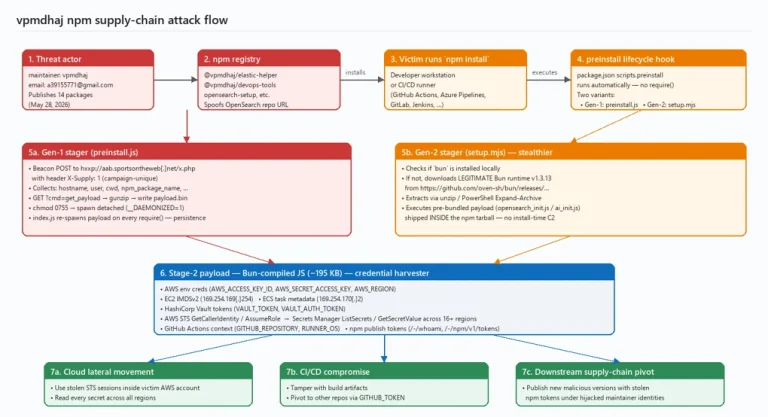
A critical npm supply chain attack exploits lookalike packages to distribute credential harvesting malware. Learn how to protect your cloud assets.

Security researchers have exposed a malicious Go module backdoor hidden inside the shopsprint/decimal package that executes code using stealthy DNS TXT records.

Socket exposes a clever cross-ecosystem supply chain attack targeting PHP packages by hiding a malicious JS postinstall backdoor inside package.json.
DevOps Alert: Over 700 laravel-lang localization package versions have been backdoored with a cross-platform 17-collector info-stealer. Audit your logs.

GitHub confirms a perimeter breach by TeamPCP. An administrative VS Code extension supply-chain worm exfiltrated 3,800 proprietary core source repositories.

Grafana Labs confirms a targeted cyberattack and source code theft after a missed token from the Mini Shai-Hulud npm worm left a repository exposed.

The Mini Shai-Hulud npm worm has hijacked the atool account, poisoning AntV & timeago.js to scrape GitHub runner memory. Execute a full reset now!

Urgent: Malicious Nx Console v18.95.0 briefly hit the VS Code Marketplace, targeting 2M+ installs with a macOS backdoor and token stealer. Audit now!

Cato CTRL intercepts "TencShell," a new stealth malware derived from open-source Rshell. Attackers use third-party access to breach networks!

Gen Digital exposes a JDownloader site breach (May 6-7, 2026). Attackers used WDAC policies to kill antivirus and r77 rootkits for total system invisibility.

GemStuffer exploits RubyGems as an illicit data transport to scrape UK council portals. Discover how this supply chain attack bypasses standard defenses.
Critical Alert: CVE-2026-25244 (CVSS 9.8) in WebdriverIO allows RCE via unsanitized git branch names. Secure your CI/CD pipeline and update to 9.24.0 now.
Urgent: 84 TanStack npm packages hijacked to harvest GitHub Actions secrets. Over 12M weekly downloads impacted. Audit your CI/CD pipelines and rotate tokens.