
 Do Son
JDownloader's website was breached on May 6, swapping official installers for malware. If you downloaded it between May 6-7, your system may be compromised.
supply chain attack
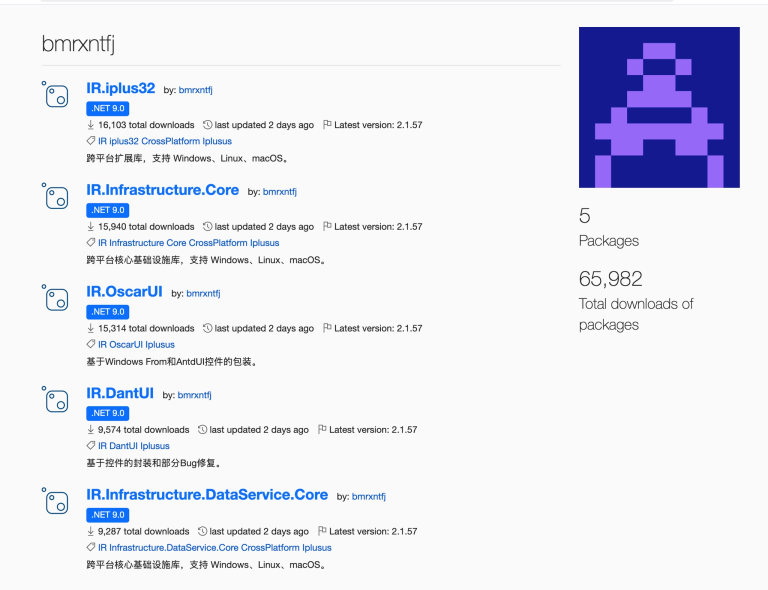
Critical alert: A stealth NuGet supply chain attack has hijacked 65,000 .NET workstations. Audit your CI/CD for malicious IR.* packages immediately.

OceanLotus targets Python developers worldwide via PyPI supply chain attacks. New ZiChatBot malware hijacks Zulip APIs for invisible C2 traffic. Patch now!

Trend Micro uncovers QLNX, a fileless Linux RAT targeting AWS, NPM, and Kubernetes keys. Learn how its eBPF rootkit hides from even the deepest system scans.
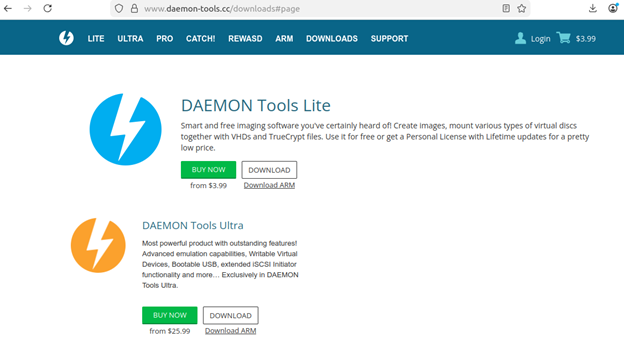
Kaspersky warns that DAEMON Tools installers (v12.5) are trojanized with the QUIC RAT. Signed binaries are being used for global espionage. Update and audit now!
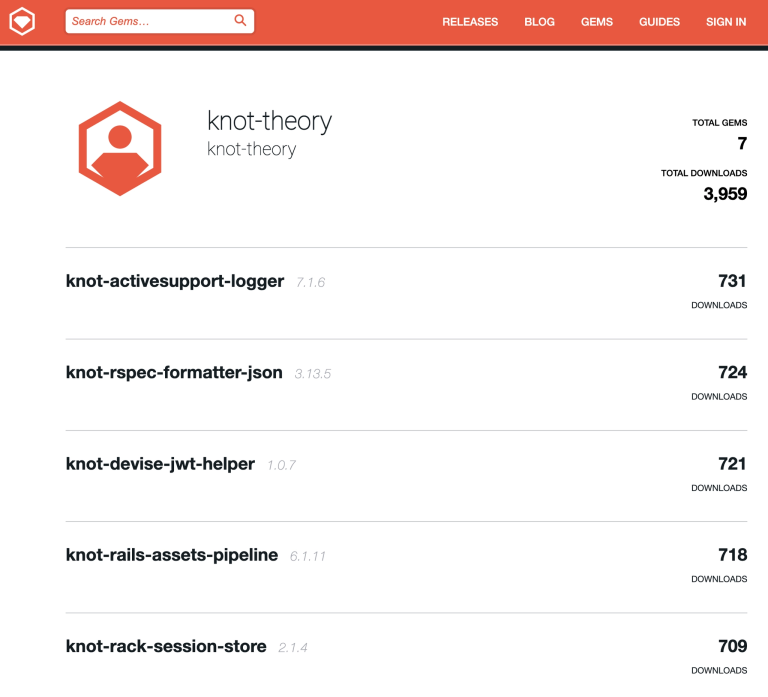
Socket uncovers a BufferZoneCorp "sleeper" campaign targeting Ruby and Go. Malicious packages steal SSH keys and subvert CI/CD pipelines. Patch now!
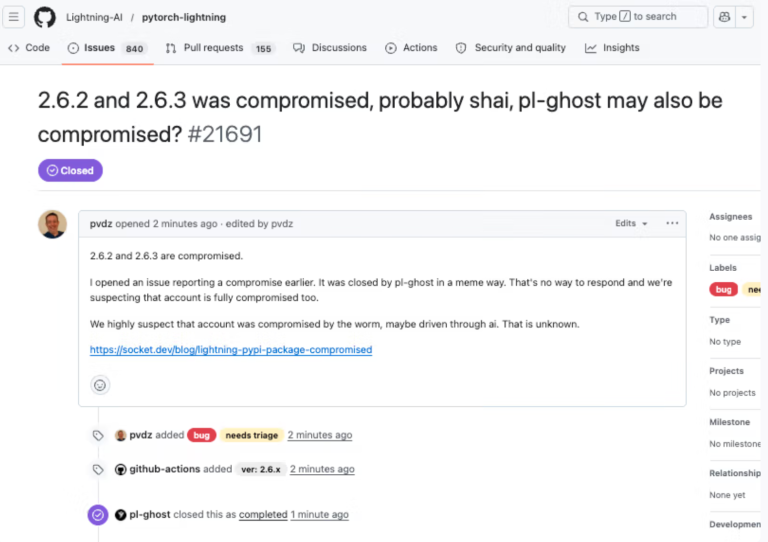
Lightning framework v2.6.2 & 2.6.3 are malicious. The "TEAM PCP" worm steals cloud secrets and poisons repos. Downgrade to 2.6.1 and rotate keys immediately!

A malicious unscoped "tanstack" npm package used live-debugged postinstall scripts to steal .env secrets via Svix webhooks. Check your dependencies now.
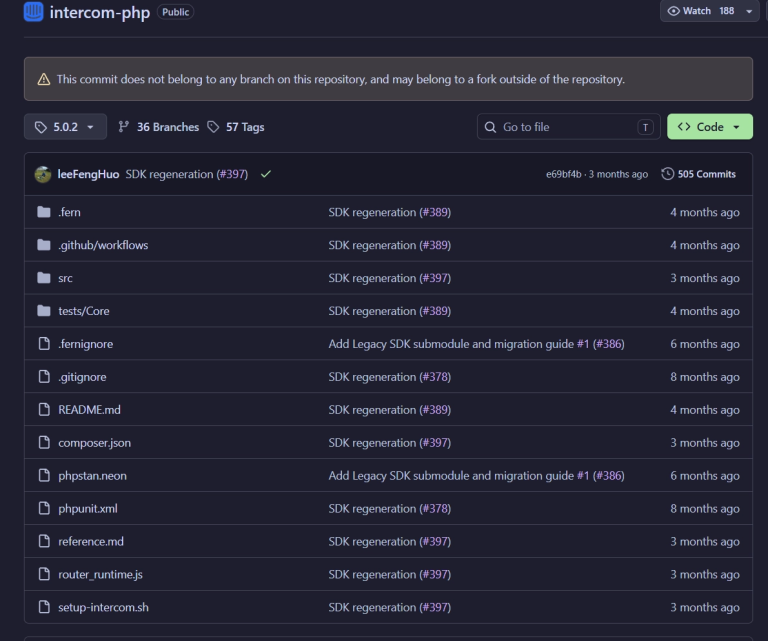
Socket uncovers a massive Mini Shai-Hulud breach in the Intercom PHP SDK. Malicious version 5.0.2 steals cloud secrets and GitHub tokens. Rotate keys now!

ReversingLabs uncovers PromptMink: A DPRK campaign using LLM-generated npm packages to trick AI coding agents into installing crypto-stealing malware.
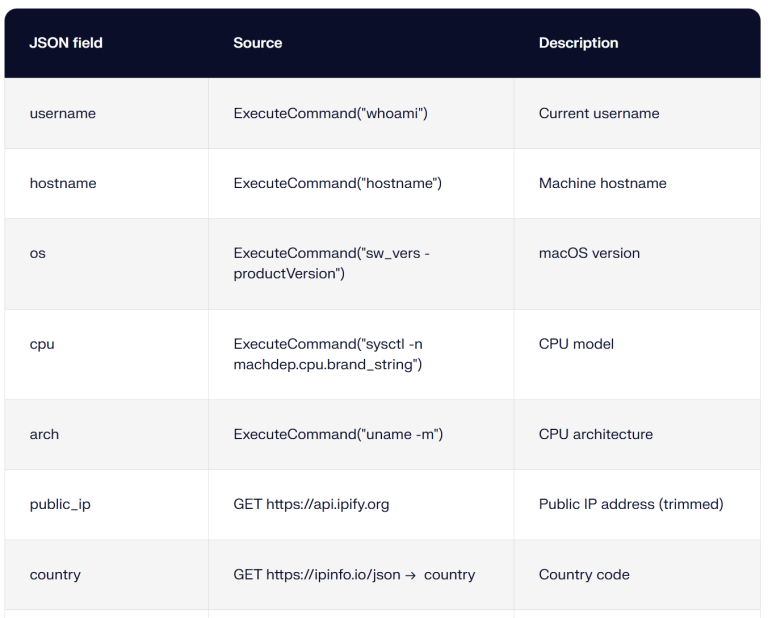
Minirat, a Go-based macOS RAT, exploits npm supply chains to bypass security. It features VM detection, AES encryption, and persistence. Secure your dev tools.

Yeeth Security uncovers a sophisticated Open VSX campaign using string-fragment reconstruction to hide malware. 16 malicious extensions identified.
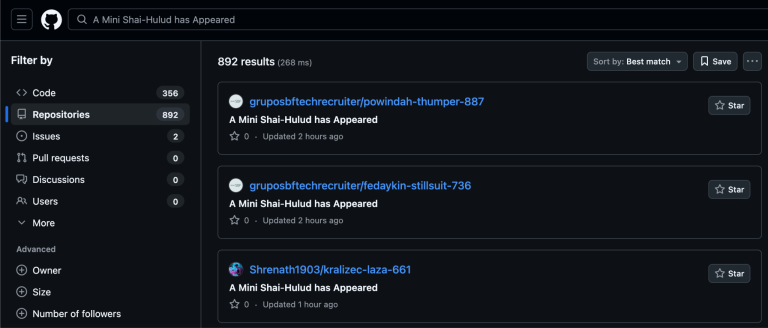
SAP developers are under attack. A surgical credential stealer hijacks CI/CD runners and cloud tokens via npm preinstall hooks. Rotate all secrets immediately.
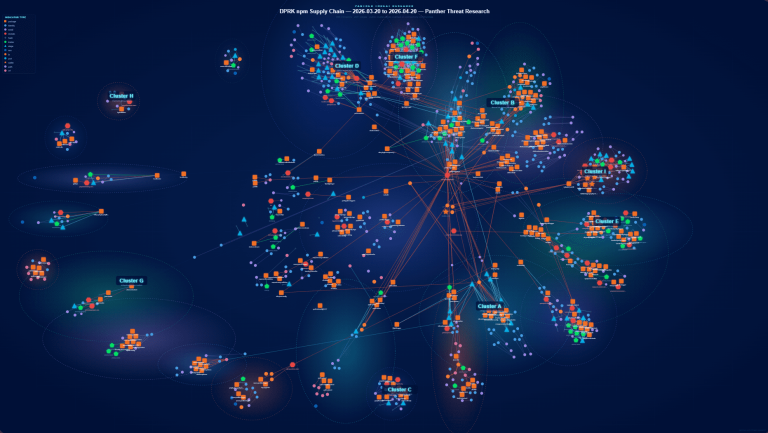
Panther Research exposes a massive 2026 DPRK npm campaign using blockchain dead-drops to steal crypto keys and AI secrets. Secure your CI/CD pipelines now.

Checkmarx discloses a major GitHub breach via a Trivy supply chain flaw. Attackers injected malicious code and exfiltrated data for a month. Get the facts.

Vimeo metadata and customer emails were exposed via a breach at third-party vendor Anodot. Internal systems remain secure. Learn how to manage vendor risk.

Bitwarden CLI v2026.4.0 compromised in "Dune"-themed supply chain attack. Malware steals cloud secrets and SSH keys. Rotate your credentials immediately.
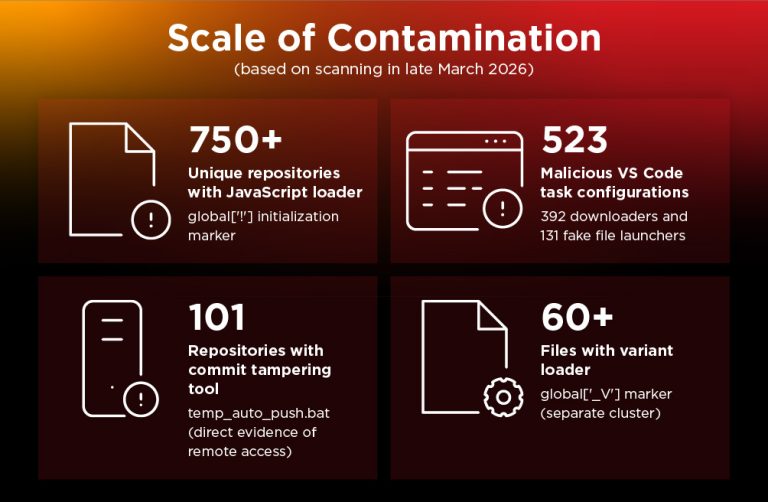
Void Dokkaebi turns developers into vectors. With 750+ infected repos and malicious VS Code tasks, this supply chain worm is hunting your CI/CD and crypto.
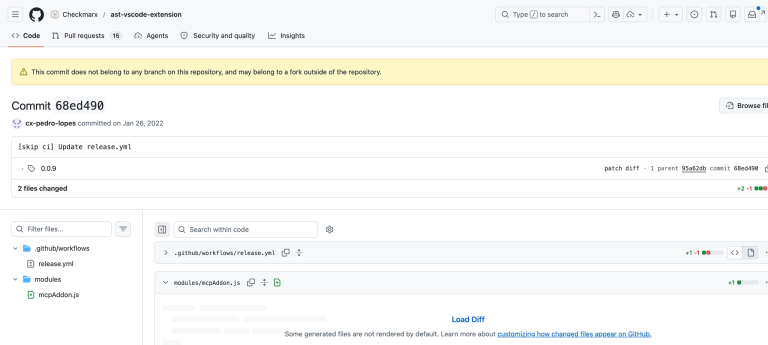
Checkmarx Docker images and VS Code extensions hijacked by TeamPCP to siphon cloud secrets and spread via npm. Audit your "Dune" repositories today.
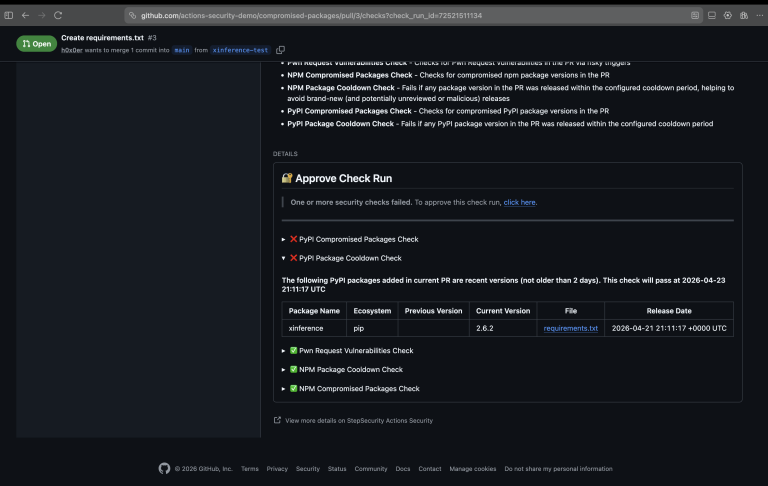
Critical supply chain attack hits Xinference (v2.6.0-2.6.2). TeamPCP’s malware siphons cloud credentials and MLOps secrets. Audit your MLOps pipeline today.
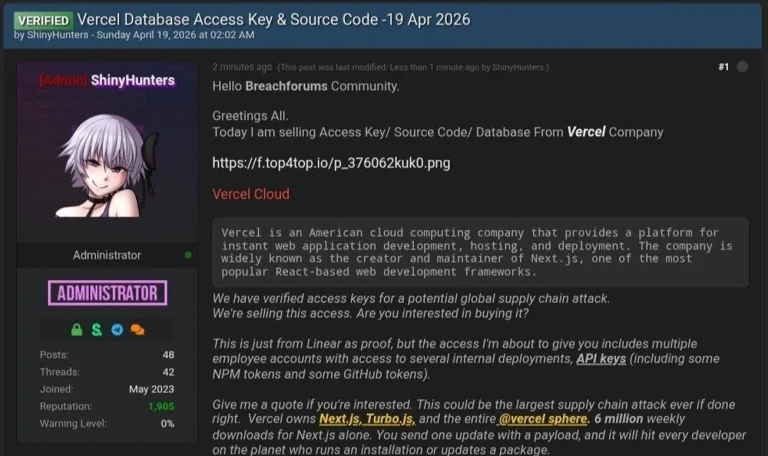
Vercel investigates a major breach by ShinyHunters. With Next.js source code and tokens at risk, developers must rotate secrets immediately. Stay updated.
PolinRider targets 1,900+ GitHub repos using "history-falsification" to hide malware. DPRK's Lazarus Group uses fake job tests to breach developers.