Ivanti Connect Secure Vulnerability Exploited in the Wild via Zero-Day Chain
 Do Son
TL;DR
Ivanti updated an urgent security update on October 29, 2026, addressing a critical Ivanti Connect Secure vulnerability chain. This flaw is actively exploited in the wild against enterprise gateways. Attackers combine an authentication bypass with local privilege escalation to take over virtual private network appliances. System administrators must apply the latest patches immediately and scan their systems with the vendor integrity tool.
- Product: Ivanti Connect Secure
- Vulnerabilities: 2 flaws (CVE-2026-104935, CVE-2026-111357)
- Highest severity: 8.6 (High · CVSSv3)
- Status: Exploited in the wild
- Exploit Intel (PatchThis): 1 of 2 confirmed
- Action: Update to 25.1.3.0, 25.1.3.1, 22.8R2.5, 22.7R2.14 now
| CVE | CVSS (CVSSv3) | Type | Fixed in | Status | PoC |
|---|---|---|---|---|---|
| CVE-2026-104935 | 8.6 | CWE-290 | 25.1.3.0, 25.1.3.1, 22.8R2.5 (+1) | Exploited in the wild | Available (Nuclei) |
| CVE-2026-111357 | 7 | CWE-829 | — | Exploited in the wild | — |
Why It Matters
Ivanti Connect Secure provides remote access solutions to thousands of organizations worldwide. According to internet scan data from security researchers and Shodan, over ten thousand appliances remain visible on public networks. Consequently, edge gateways represent prime targets for espionage and network infiltration.
According to the security advisory, threat actors are actively abusing these flaws in real-world campaigns. Specifically, the vendor confirmed: “We are aware of exploitation in the wild affecting a limited number of customers at the time of disclosure when CVE-2026-104935, CVE-2026-111357 and CVE-2026-118527 are chained.” Cybersecurity firm Volexity collaborated with Ivanti to analyze the threat actor behavior. While attackers have weaponized the chain in the wild, no public proof-of-concept exploit code has been confirmed.
How the Attack Works
Remote Command Execution via Authentication Bypass
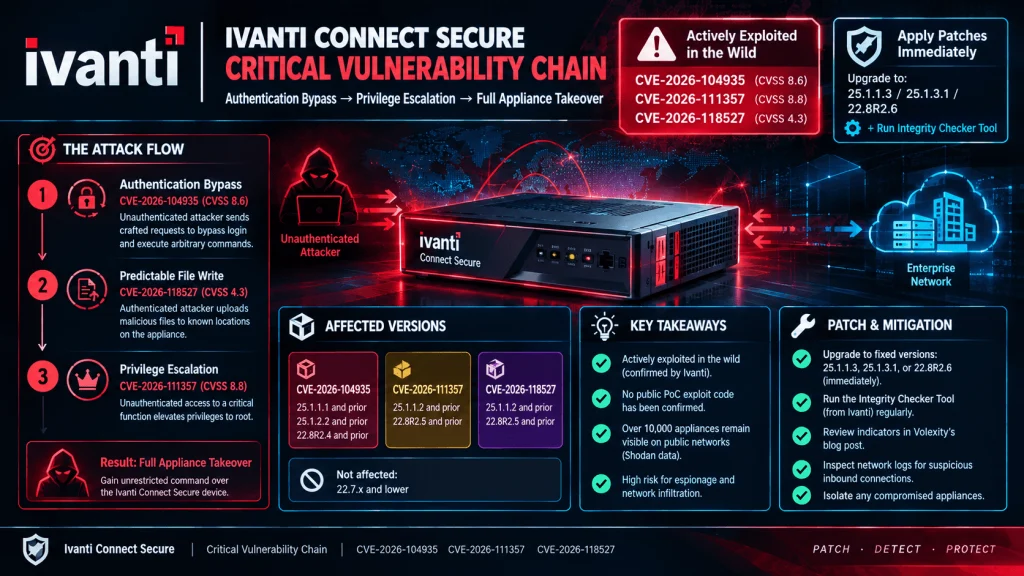
The primary flaw, CVE-2026-104935 (CVSS 8.6), stems from authentication bypass by spoofing in the web components. An unauthenticated remote attacker sends crafted network requests to bypass login verification. As a result, the attacker executes arbitrary commands on the appliance.
Privilege Escalation and Predictable File Writes
Next, the attacker chains two secondary vulnerabilities to solidify control. CVE-2026-118527 (CVSS 4.3) involves predictable filenames during file processing. An authenticated attacker uploads malicious files to known locations on the local disk. Subsequently, the attacker invokes CVE-2026-111357 (CVSS 8.8), which lacks authentication for a critical function. This local flaw elevates privileges to root, giving the attacker unrestricted command over the device.
Affected Versions
This chained Ivanti Connect Secure vulnerability impacts multiple software branches. For CVE-2026-104935, affected releases include versions 25.1.1.1 and prior, 25.1.2.2 and prior, and 22.8R2.4 and prior. Meanwhile, CVE-2026-111357 and CVE-2026-118527 affect versions 25.1.1.2 and prior, as well as 22.8R2.5 and prior. Versions 22.7.x and lower do not contain these vulnerabilities.
Patch and Mitigation Steps
Ivanti released software patches for all supported releases. In its advisory, Ivanti noted that “A fix is available now for all vulnerabilities which were chained and exploited in the wild.”
Administrators should upgrade affected systems to versions 25.1.1.3, 25.1.3.1, or 22.8R2.6 immediately. In addition, the vendor stated: “Customers should review available indicators in Volexity’s blog post HERE and run the Integrity Checker Tool regularly.” Operators should inspect network logs for suspicious inbound connections and isolate any compromised appliances.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
