 Do Son
Ivanti security advisories fix 13 flaws, including Ivanti Endpoint Manager RCE CVE-2026-121653 (CVSS 9.8) and CSA bug CVE-2026-121683.
Ivanti
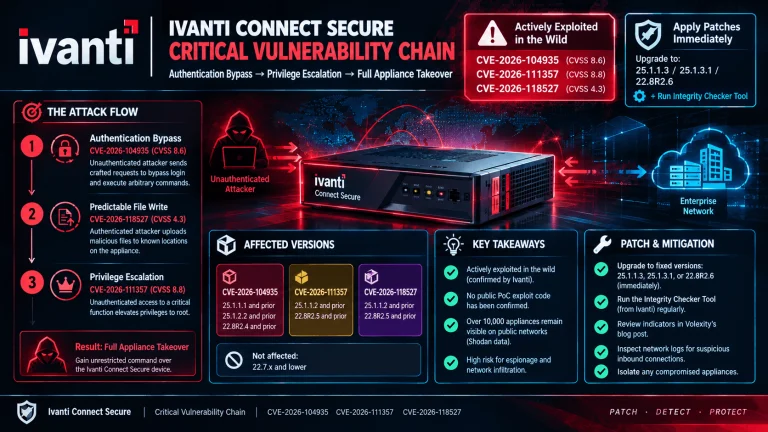
Patch the Ivanti Connect Secure vulnerability now. This Ivanti Connect Secure zero-day chain with CVE-2026-104935 is actively exploited in the wild.
UTA0576 chained an Ivanti Connect Secure zero-day, CVE-2026-104935, with a root exploit to steal AD credentials. Patch now and check memory.
Two Ivanti critical vulnerabilities rated CVSS 9.9 in Neurons Patch for Intune and Xtraction risk credential theft. Update Xtraction and rotate secrets.
Ivanti Connect Secure vulnerability CVE-2026-104935 is exploited in the wild, letting unauthenticated attackers run commands. Update to 25.1.1.2 now.
Ivanti released patches for high severity Ivanti vulnerabilities affecting Sentry and EPMM. Secure your enterprise deployments against these flaws now.
75 CVEs confirmed exploited in Q2 2026. Microsoft leads with 15, Ivanti tops EPSS at 99%. Full breakdown by vendor, CWE, and publication-to-exploit gap.

Ivanti confirms active exploitation of EPMM (CVE-2026-6973). Attackers are using old credentials to hijack mobile management. Patch to v12.8.0.1 immediately!
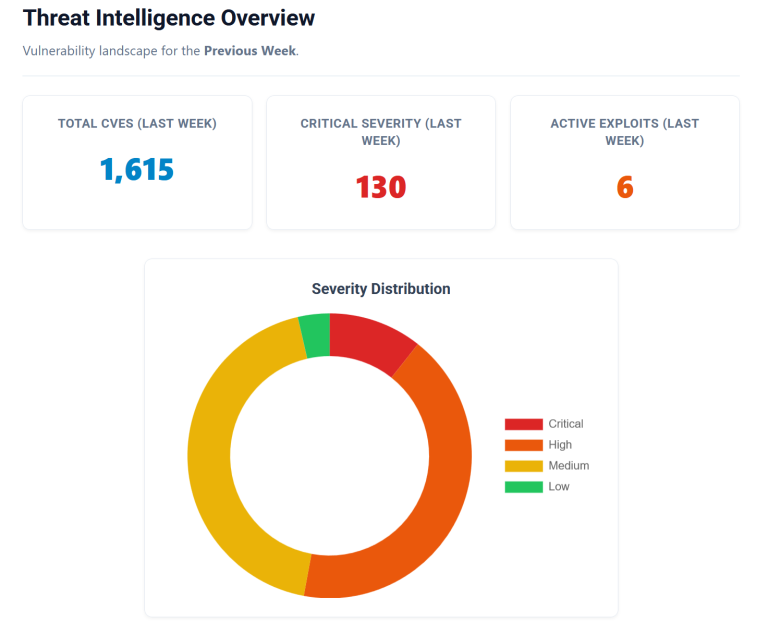
Weekly vulnerability digest (April 6-12, 2026): 1,615 new flaws, CISA KEV alerts for Ivanti and Fortinet, and critical RCE in AI tools like Flowise.

CISA has released a new report detailing how attackers are exploiting Ivanti EPMM flaws to deploy malicious listeners and gain remote code execution.

Ivanti has released a security update for Endpoint Manager, patching two high-severity RCE flaws (CVSS 8.8) that could allow unauthenticated attackers to execute code.

Ivanti patches three Workspace Control flaws exposing sensitive credentials due to hardcoded keys. Update immediately to secure your enterprise.

Ivanti patches CVE-2025-22462, a critical CVSS 9.8 auth bypass flaw in Neurons for ITSM. Risk of full admin access. Patch or restrict IIS access now.

Ivanti fixes EPMM flaws CVE-2025-4427 and CVE-2025-4428, exploited in the wild for unauthenticated RCE. Update now or apply strict API access controls.
DslogdRAT malware exploited Ivanti Connect Secure via CVE-2025-0282, using web shells and C2 channels to evade detection and persist in networks.

A China-nexus APT group exploited Ivanti Connect Secure VPN vulnerabilities to infiltrate organizations globally, deploying the SPAWNCHIMERA malware toolkit

Week of April 7-13 saw critical Ivanti, WordPress, & Windows vulnerabilities exploited, plus major data breaches impacting millions.

Rapid7 reveals details of Ivanti zero-day CVE-2025-22457, a critical stack-based buffer overflow actively exploited by a China-linked group. Learn about the vulnerability and available patches.

Stay informed about the latest cybersecurity event, including new malware threats and critical vulnerabilities being exploited.

Learn about CVE-2025-22457, a critical vulnerability in Ivanti products that allows remote code execution by attackers.

Uncover the CVE-2024-13159 PoC exploit code. Learn how this high-severity vulnerability affects Ivanti Endpoint Manager.

Stay protected from the CVE-2025-22467 vulnerability in Ivanti Connect Secure. Learn how to update your system and mitigate potential risks.