 Do Son
Two critical RabbitMQ flaws allow authentication bypass. One forges TLS client certs; the other tricks OAuth2 JWKS to accept any JWT.
A malicious NuGet package, Braintree.Net, acts as a credit card skimmer and steals merchant API keys. The Braintree NuGet typosquat hits .NET devs.
 cybernewswire
San Francisco, United States, 15th July 2026, CyberNewswire
Zoom vulnerability CVE-2026-53412 (CVSS 9.8) allows unauthenticated account takeover over the network. Update Zoom Workplace for Windows to 7.0.0 now.

Clubfoot Wolf targets Russian companies with phishing that drops NetSupport Manager as a stealthy remote access tool, BI.ZONE reports.
JetBrains vulnerabilities patched: CVE-2026-62422 (CVSS 10) YouTrack authentication bypass, IntelliJ IDEA RCE CVE-2026-59792, and four TeamCity flaws.
Toronto, Canada, 15th July 2026, CyberNewswire
Four critical Coolify vulnerabilities let low-privileged users reach remote code execution and cross-tenant server access. Update to v4.1.2 now.

Introduction The increasing adoption of AI-enabled creative tools is a trend currently observed playing out in the...
A high-severity Cursor zero day vulnerability allows automatic remote code execution via malicious git.exe files. Read how this flaw remains unpatched.
The Google Images 25th anniversary update brings real-time personalized results and Nano Banana image generation built into AI Overviews.

A CrySome RAT phishing attack used a fake freight rate confirmation to bypass AMSI, disable Defender, and steal browser credentials on Windows.
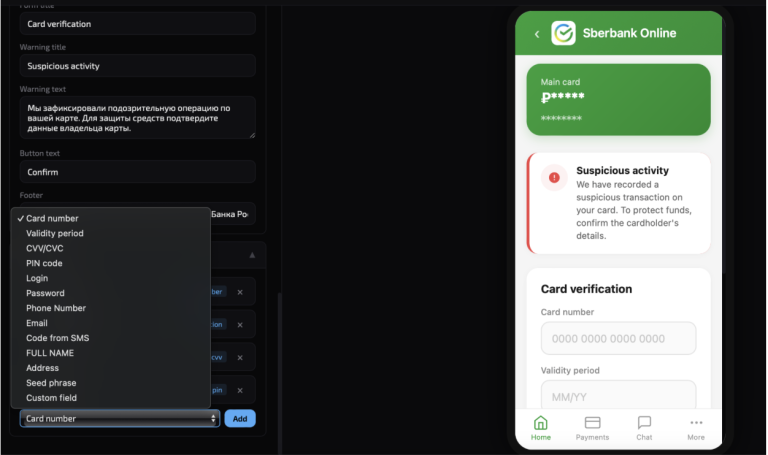
RedWing Android malware is a rental spyware sold as malware-as-a-service on Telegram. It steals banking logins, intercepts 2FA, and hijacks phones.
Rockwell Automation vulnerability CVE-2026-10577 (CVSS 10) exposes an unauthenticated debug port in 1715 Redundant I/O modules. Update to firmware 3.011.
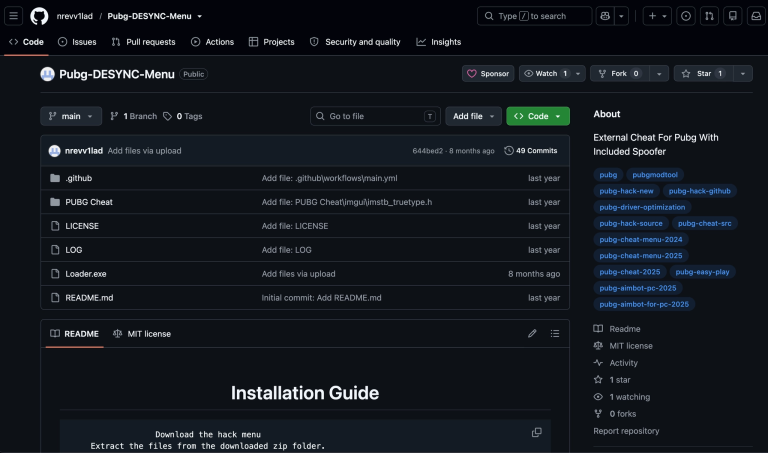
A malicious Go module exposed a GitHub lure network of 222 repositories, dubbed Operation Muck and Load, staging RATs and infostealers.
GodDamn ransomware is the latest Beast ransomware rebrand from Hyadina. It uses a Microsoft-signed malicious kernel driver, PoisonX, to disable EDR.
Notepad++ vulnerabilities now have public PoC exploit code. CVE-2026-52886, CVE-2026-54758, and CVE-2026-57233 are fixed in v8.9.7. Update now.
Google's Chrome security update 150.0.7871.124 fixes 15 flaws, including critical use-after-free bugs CVE-2026-15764 and CVE-2026-15765. Update now.
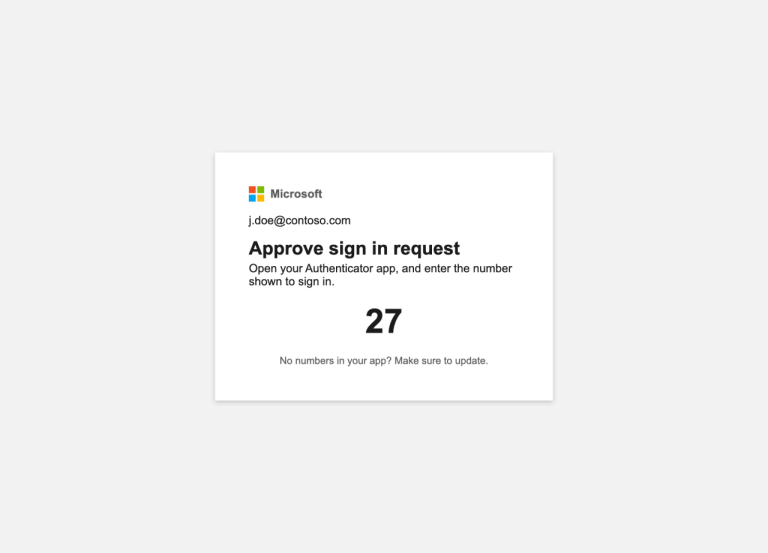
A vishing attack tricks Microsoft 365 users into passkey phishing, letting O-UNC-066 enroll its own passkey and hijack Entra accounts for extortion.
CISA warns SharePoint vulnerabilities CVE-2026-32201, CVE-2026-45659, and CVE-2026-56164 are exploited in the wild. Patch and harden servers now.

A LNK phishing attack drops a Node.js backdoor and hides its C2 on the TON blockchain using EtherHiding, LevelBlue reports.
SonicWall SMA1000 SSRF flaw CVE-2026-15409 (CVSS 10.0) is exploited in the wild. Upgrade to hotfix 12.4.3-03453 or 12.5.0-02835 now.