Skip to content
November 1, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
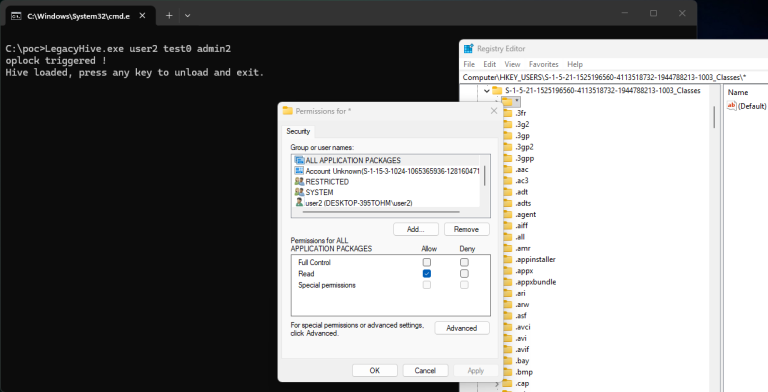
LegacyHive: Exploit Code and Full Details Publicly Disclosed for Unpatched Windows Privilege Escalation Flaw LegacyHive exploit public disclosure Windows privilege escalation flaw by Nightmare-Eclipse
  • Vulnerability Report

LegacyHive: Exploit Code and Full Details Publicly Disclosed for Unpatched Windows Privilege Escalation Flaw

Do Son July 14, 2026 0

LegacyHive exploit code is public. This unpatched Windows privilege escalation flaw from Nightmare-Eclipse defeats the July 2026 patch.
Microsoft July 2026 Patch Tuesday Fixes 570 Flaws, Two Zero-Days Exploited in the Wild Microsoft July 2026 Patch Tuesday zero-day vulnerabilities CVE-2026-56155 and CVE-2026-56164
  • Vulnerability Report

Microsoft July 2026 Patch Tuesday Fixes 570 Flaws, Two Zero-Days Exploited in the Wild

Do Son July 14, 2026 0

Microsoft's July 2026 Patch Tuesday fixes 570 flaws. Zero-days CVE-2026-56155 and CVE-2026-56164 are exploited in the wild. Patch now.
Tego AI Finds Claude Tag Slack Integration Can Trigger Unauthorized Enterprise Actions watermarked_img_2256307174777406298_1784021571yc2c34V8Fl
  • Press Release

Tego AI Finds Claude Tag Slack Integration Can Trigger Unauthorized Enterprise Actions

cybernewswire July 14, 2026 0
Tel Aviv, Israel, 14th July 2026, CyberNewswire
Read More Read more about Tego AI Finds Claude Tag Slack Integration Can Trigger Unauthorized Enterprise Actions
CVE-2026-53481 & CVE-2026-53483: Dell PowerProtect Full Takeover (9.8) Image showing a hacker taking complete control of system using CVE-2026-53483 and Dell vulnerabilities
  • Vulnerability Report

CVE-2026-53481 & CVE-2026-53483: Dell PowerProtect Full Takeover (9.8)

Do Son July 14, 2026 0

Critical Dell vulnerabilities like CVE-2026-53483 allow attackers to take complete control of system. Patch PowerProtect flaws to stop remote exploits.
Exploited in the Wild? Debian Webhost Rooted as Public PoCs Land for Bad Epoll (CVE-2026-46242) and IPv6 Frag Escape Bad Epoll CVE-2026-46242 Linux kernel privilege escalation use-after-free public PoC exploit
  • Vulnerability Report

Exploited in the Wild? Debian Webhost Rooted as Public PoCs Land for Bad Epoll (CVE-2026-46242) and IPv6 Frag Escape

Do Son July 14, 2026 0

A Debian webhost was rooted while missing fixes for Bad Epoll (CVE-2026-46242) and an IPv6 frag escape. Public PoC exploit code is now out.
CVE-2026-56000: Use-After-Free Flaw Hits X.Org Server and Xwayland X.Org Server use-after-free vulnerability CVE-2026-56000 patched in xorg-server 21.1.24
  • Vulnerability Report

CVE-2026-56000: Use-After-Free Flaw Hits X.Org Server and Xwayland

Do Son July 14, 2026 0

X.Org Server ships fixes for two flaws, including CVE-2026-56000, a CVSS 9.0 use-after-free. Update xorg-server and Xwayland now.
CVE-2026-59948: PHP Composer Flaw Lets Packages Execute Code Outside the Project Context PHP Composer arbitrary file write vulnerability CVE-2026-59948 patched in version 2.10.2
  • Vulnerability Report

CVE-2026-59948: PHP Composer Flaw Lets Packages Execute Code Outside the Project Context

Do Son July 14, 2026 0

PHP Composer patched three flaws, including CVE-2026-59948, an arbitrary file write that can run code outside your project. Update to 2.10.2 or 2.2.29.
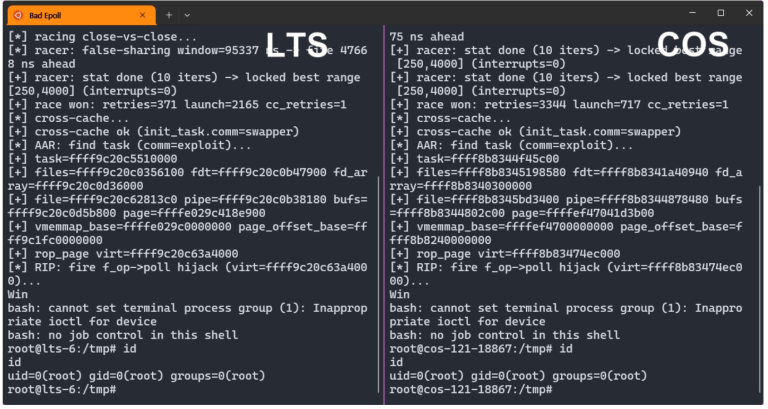
Public Exploit and Details Released for Bad Epoll Root Flaw (CVE-2026-46242) Bad Epoll CVE-2026-46242 Linux kernel use-after-free enabling root privilege escalation
  • Vulnerability Report

Public Exploit and Details Released for Bad Epoll Root Flaw (CVE-2026-46242)

Do Son July 14, 2026 0

Bad Epoll (CVE-2026-46242) is a Linux kernel UAF enabling root privilege escalation. Full details and PoC exploit code are now public. Patch now.
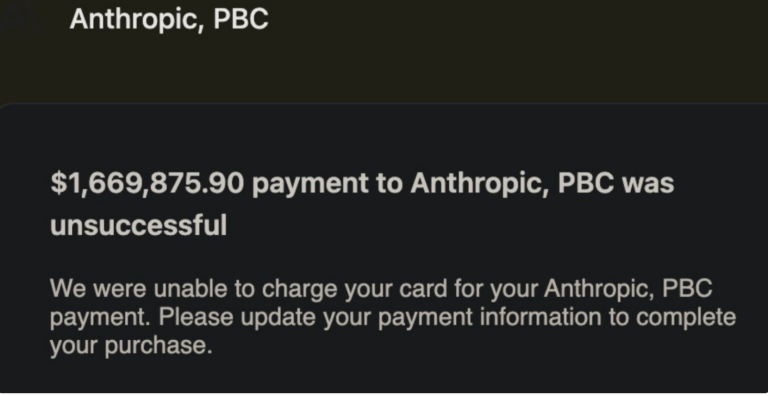
Anthropic API Billing Error Hits Developer for $16M Anthropic API billing error notification, Claude API incorrect charge screenshot
  • Technology

Anthropic API Billing Error Hits Developer for $16M

Do Son July 14, 2026 0

An Anthropic API billing error mistakenly charged a Korean developer $16.6 million. Learn how this massive automated glitch froze his credit card.

VMware Avi Load Balancer Authentication Bypass (CVE-2026-47865, CVSS 9.8) Headlines Seven-Flaw Patch VMware Avi Load Balancer authentication bypass vulnerability CVE-2026-47865 CVSS 9.8 critical patch
  • Vulnerability Report

VMware Avi Load Balancer Authentication Bypass (CVE-2026-47865, CVSS 9.8) Headlines Seven-Flaw Patch
Do Son July 14, 2026 0

VMware Avi Load Balancer patches CVE-2026-47865 (CVSS 9.8), a critical authentication bypass, plus six more flaws. Upgrade the Avi Controller now.
Meta Louisiana Data Center: A $50 Billion AI Gamble Meta Louisiana data center facility, Project Hyperion AI infrastructure investment, 5GW computing capacity server farm
  • Technology

Meta Louisiana Data Center: A $50 Billion AI Gamble

Do Son July 14, 2026 0

Explore the massive Meta Louisiana data center expansion. This $50 billion investment fuels local economic booms but ignites intense Wall Street anxiety.
Grok Build Repository Upload Scandal: Researcher Confirms Privacy Mode Cannot Stop It Grok Build repository upload controversy, SpaceXAI privacy mode response
  • Data Leak

Grok Build Repository Upload Scandal: Researcher Confirms Privacy Mode Cannot Stop It

Do Son July 14, 2026 0

Researcher @Cereblab confirms the Grok Build repository upload bypasses privacy mode; SpaceXAI's /privacy only covers code snippet sharing.
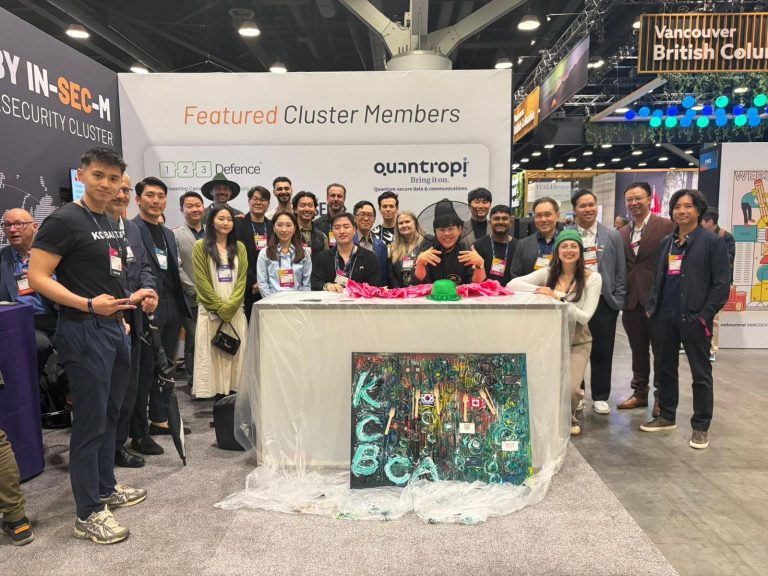
Greenhat Announces Successful Delegation at Web Summit Vancouver 2026 WebSummit_178395613180DohtofDR
  • Press Release

Greenhat Announces Successful Delegation at Web Summit Vancouver 2026

cybernewswire July 14, 2026 0
Vancouver, Canada, 14th July 2026, CyberNewswire
Read More Read more about Greenhat Announces Successful Delegation at Web Summit Vancouver 2026
SAP Patches CVE-2026-44747 (CVSS 9.9): Critical Memory Corruption Flaw in NetWeaver AS ABAP SAP Security Patch Day July 2026 CVE-2026-44747 memory corruption vulnerability in NetWeaver AS ABAP
  • Vulnerability Report

SAP Patches CVE-2026-44747 (CVSS 9.9): Critical Memory Corruption Flaw in NetWeaver AS ABAP

Do Son July 14, 2026 0

SAP Security Patch Day July 2026 fixes CVE-2026-44747 (CVSS 9.9), a memory corruption flaw in NetWeaver AS ABAP, plus two more critical bugs.
CrowdStrike Details New Prompt Injection Attacks on AI Diagram showing how prompt injection attacks and prompt injection techniques threaten AI security.
  • Vulnerability Report

CrowdStrike Details New Prompt Injection Attacks on AI

Do Son July 14, 2026 0

Discover how new prompt injection attacks threaten AI security. Hackers use prompt injection techniques to manipulate AI agents and bypass safety controls.
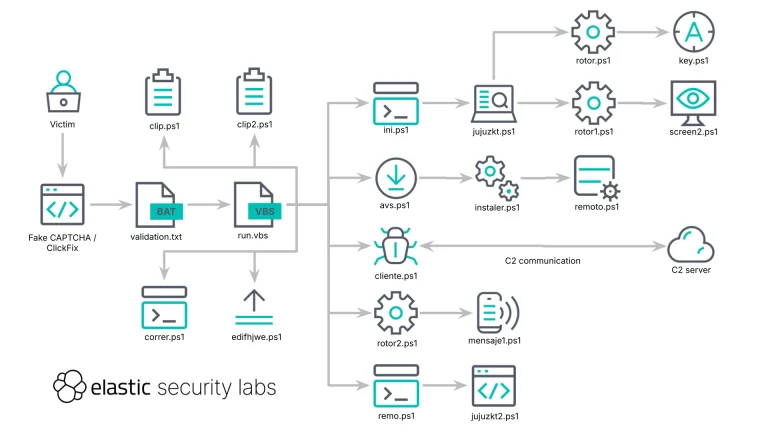
Mexican Banking Fraud: REF6045 Operation Exposed Diagram of the REF6045 operation executing Mexican banking fraud using SCMBANKER.
  • Cybercriminals

Mexican Banking Fraud: REF6045 Operation Exposed

Do Son July 14, 2026 0

Discover how the REF6045 operation executes Mexican banking fraud. Hackers use fake CAPTCHAs and the SCMBANKER toolkit to steal financial data.
WinFsp Patches Two Privilege Escalation Flaws: CVE-2026-3006 and CVE-2026-7162 (CVSS 7.8) WinFsp vulnerabilities CVE-2026-3006 and CVE-2026-7162 enabling local privilege escalation on Windows
  • Vulnerability Report

WinFsp Patches Two Privilege Escalation Flaws: CVE-2026-3006 and CVE-2026-7162 (CVSS 7.8)

Do Son July 14, 2026 0

WinFsp vulnerabilities CVE-2026-3006 and CVE-2026-7162 enable local privilege escalation to SYSTEM on Windows. Update to WinFsp 2026 Beta2 now.
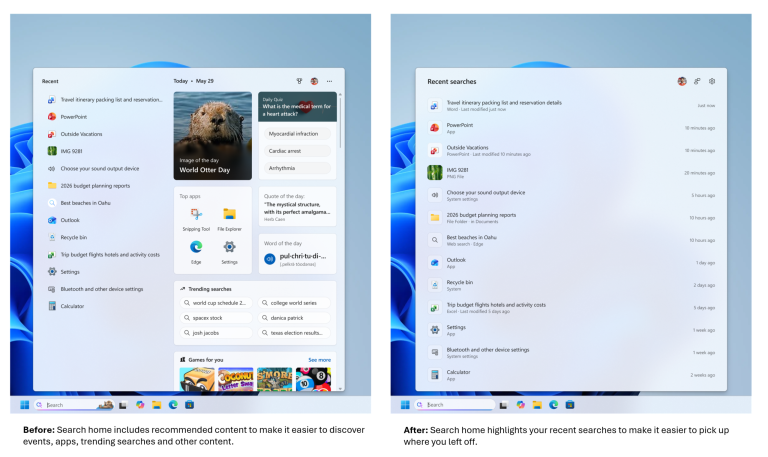
Windows Search Box Improvements Roll Out in Windows 11 Windows search box improvements and refined Windows Search settings in Windows 11
  • Windows

Windows Search Box Improvements Roll Out in Windows 11

Do Son July 14, 2026 0

Discover the new Windows search box improvements in Windows 11. Learn how to disable Bing search distractions and prioritize local file search results.
Telegram t.me Domain Blocked by .ME Registry Links Down Telegram t.me domain serverHold status blocking all contact links and shared content URLs
  • Technology

Telegram t.me Domain Blocked by .ME Registry Links Down

Do Son July 14, 2026 0

The t.me domain is in serverHold status, taking down all Telegram contact and share links. Telegram falls back to telegram.me for new links.
The Grok Build Privacy Controversy: Unauthorized Repository Uploads Grok Build privacy settings interface showing how to disable automated repository data uploads
  • Data Leak

The Grok Build Privacy Controversy: Unauthorized Repository Uploads

Do Son July 14, 2026 0

Grok Build faces severe backlash over unauthorized repository data uploads. Learn how to opt out of data sharing and secure your sensitive code.
Netwrix Password Secure Flaws Enable Authenticated Remote Code Execution (CVSS 9.9), Update to 26.6.100 Netwrix Password Secure vulnerabilities enabling authenticated remote code execution on the server
  • Vulnerability Report

Netwrix Password Secure Flaws Enable Authenticated Remote Code Execution (CVSS 9.9), Update to 26.6.100

Do Son July 14, 2026 0

Netwrix Password Secure vulnerabilities (CVSS 9.9) allow authenticated remote code execution on the server. Update to version 26.6.100 now.
CVE-2026-6875: Critical ServiceNow Sandbox Escape Allows Unauthenticated Remote Code Execution ServiceNow sandbox escape CVE-2026-6875 remote code execution vulnerability in the AI Platform
  • Vulnerability Report

CVE-2026-6875: Critical ServiceNow Sandbox Escape Allows Unauthenticated Remote Code Execution

Do Son July 14, 2026 0

CVE-2026-6875 (CVSS 9.5) is a ServiceNow sandbox escape in the AI Platform allowing unauthenticated remote code execution. Patch to fixed releases now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20356CVSS 7.5
    As part of Cisco's ongoing commitment to proactive security and product quality, the Cisco owned Open Source Snort...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-62048CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Liquid Web / StellarWP...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120338CVSS 10.0
    Prefab UI's Generative UI sandbox runs caller-supplied Python inside Pyodide, Python compiled to WebAssembly, in a Deno subprocess....
    📅 Updated: Nov 1, 2026
  • CVE-2026-120232CVSS 9.3
    A vulnerability was identified in Horizon DataSys Reboot Restore Standard up to 13.2. The impacted element is the...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120231CVSS 9.4
    A vulnerability was determined in WAVLINK WN553X1-B V260403_2.0.0. The affected element is the function sub_416568 of the file...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120230CVSS 9.4
    A vulnerability was found in WAVLINK WN701AE 260105. Impacted is the function del_vlan_group of the component ioos Web...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120229CVSS 9.4
    A vulnerability has been found in WAVLINK WN553X1-B 260403_2.0.0. This issue affects the function sub_416B50 of the file...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120228CVSS 9.4
    A flaw has been found in WAVLINK WN553X1-B V260403_2.0.0. This vulnerability affects the function sub_416D88 of the file...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120308CVSS 9.9
    A Beta9 tenant can attach a volume when deploying a function, endpoint, or task queue. The gateway builds...
    📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.