Skip to content
November 1, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Better Auth SSRF Flaw CVE-2026-53513 (CVSS 9.6) Threatens 19M-Download Auth Library Better Auth SSRF vulnerability CVE-2026-53513 in the SSO plugin exposing OIDC provider registration
  • Vulnerability Report

Better Auth SSRF Flaw CVE-2026-53513 (CVSS 9.6) Threatens 19M-Download Auth Library

Do Son July 14, 2026 0

CVE-2026-53513 is a Better Auth SSRF flaw (CVSS 9.6) in the SSO plugin. It exposes cloud metadata and enables account takeover. Patch to 1.6.11 now.
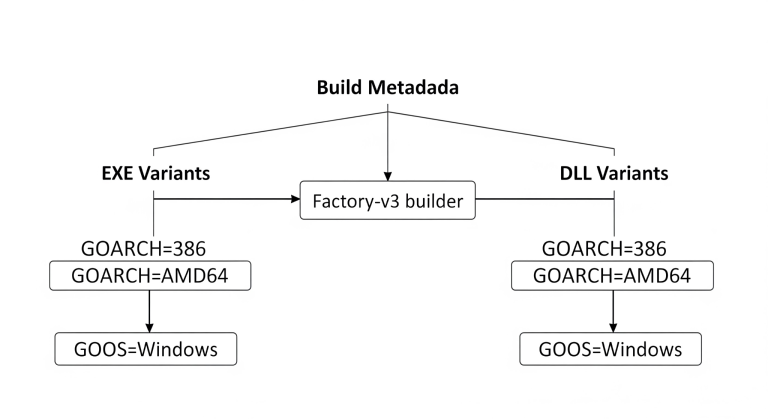
Vidar Stealer Campaign Uses Factory-v3 Loader Diagram showing how a Vidar stealer campaign uses the Factory-v3 loader to infect systems.
  • Malware

Vidar Stealer Campaign Uses Factory-v3 Loader

Do Son July 13, 2026 0

A new Vidar stealer campaign uses the Factory-v3 loader and fake certificates to deploy malware. Learn how attackers hide XMRig and bypass security.
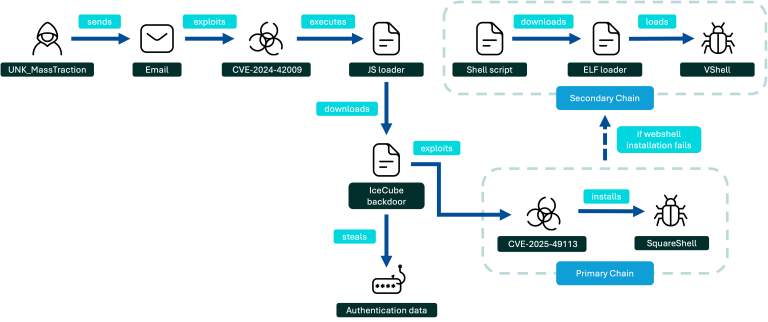
UNK_MassTraction Exploits Roundcube Webmail to Hit University Physics Departments UNK_MassTraction Roundcube exploitation infection chain deploying the VShell backdoor at universities
  • Cybercriminals

UNK_MassTraction Exploits Roundcube Webmail to Hit University Physics Departments

Do Son July 13, 2026 0

UNK_MassTraction, a suspected China-aligned actor, exploits Roundcube webmail flaws to steal credentials and deploy the VShell backdoor at universities.
Torq and Criminal IP Partner to Deliver Decision-Ready Threat Intelligence for Autonomous SOC Operations 1200_700_1783643174kG3odfUo4d
  • Press Release

Torq and Criminal IP Partner to Deliver Decision-Ready Threat Intelligence for Autonomous SOC Operations

cybernewswire July 13, 2026 0
Torrance, California, USA, 13th July 2026, CyberNewswire
Read More Read more about Torq and Criminal IP Partner to Deliver Decision-Ready Threat Intelligence for Autonomous SOC Operations
UAT-7810 Expands Its LapDogs ORB Network With New Router Malware GemStuffer RubyGems Campaign RubyGems Data Exfiltration TanStack npm Compromise Supply Chain Attack DNS Hijacking APT28 (Fancy Bear) OpenVSX Supply Chain Attack Checkmarx Plugin Breach Stryker Cyberattack CISA Alert Trans-Regional Cyber Conflict Operation Epic Fury Cyber Operation MacroMaze APT28 Cyber Espionage Notepad++ Supply Chain Attack Lotus Blossom Group Defense Industrial Base Threats GTIG Report APT28 Operation Neusploit CVE-2026-21509 Bookworm Malware
  • Cybercriminals

UAT-7810 Expands Its LapDogs ORB Network With New Router Malware

Do Son July 13, 2026 0

UAT-7810, a China-nexus APT, grows its LapDogs ORB network with new router malware including LONGLEASH, DOGLEASH, and JARLEASH. Cisco Talos reports.
CVE-2026-20744: Privilege Escalation in EV Chargers Diagram of CVE-2026-20744 privilege escalation flaw in Hydro-Québec charging stations alongside CVE-2026-42952 and CVE-2026-44383.
  • Vulnerability Report

CVE-2026-20744: Privilege Escalation in EV Chargers

Do Son July 13, 2026 0

A critical privilege escalation flaw (CVE-2026-20744) affects Hydro-Québec EV charging stations. Learn how this vulnerability impacts the backend.
Defending Against Vishing and HUMINT: Best Practices for Security Teams DCMTK vulnerabilities enabling path traversal file write in the DICOM toolkit (CVE-2026-50003)
  • Technique

Defending Against Vishing and HUMINT: Best Practices for Security Teams

Do Son July 13, 2026 0
As cyber threats continue to evolve, attackers are increasingly targeting people rather than technology alone. Social engineering...
Read More Read more about Defending Against Vishing and HUMINT: Best Practices for Security Teams
ScreenConnect AsyncRAT Campaign Hides Inside Fake Freeware ScreenConnect AsyncRAT Campaign infrastructure and remote monitoring tools
  • Malware

ScreenConnect AsyncRAT Campaign Hides Inside Fake Freeware

Do Son July 13, 2026 0

A massive ScreenConnect AsyncRAT campaign uses SEO poisoning and spoofed websites to drop malicious installer archives via remote monitoring tools.
Evolving Windows Vulnerability Management with AI Windows vulnerability management using AI code scanning tools
  • Windows

Evolving Windows Vulnerability Management with AI

Do Son July 13, 2026 0

Microsoft leverages advanced AI agents like MDASH to accelerate Windows vulnerability management and secure codebases.
Critical Veeam Remote Code Execution Flaw: CVE-2026-44963 Diagram showing Veeam Backup server affected by CVE-2026-44963 and related CVE-2023-27532 remote code execution vulnerabilities.
  • Vulnerability Report

Critical Veeam Remote Code Execution Flaw: CVE-2026-44963

Do Son July 13, 2026 0

A critical Veeam Backup vulnerability (CVE-2026-44963) allows remote code execution. Patch immediately to avoid ransomware targeting CVE-2023-27532.
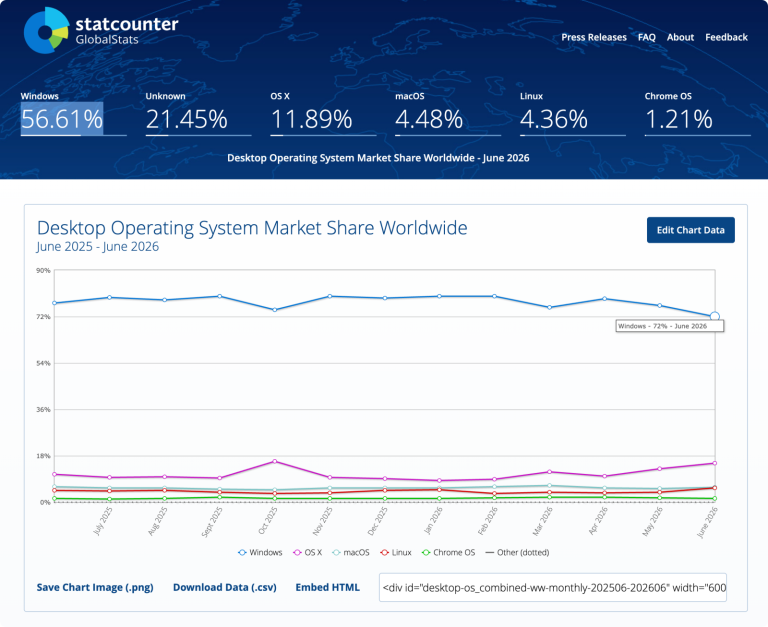
StatCounter Corrects Flawed Windows Market Share Data StatCounter report showing corrected Windows market share and operating system statistics
  • Windows

StatCounter Corrects Flawed Windows Market Share Data

Do Son July 13, 2026 0

StatCounter corrects flawed June 2026 data after reports falsely claimed Windows market share plunged to 56%. The anomaly stemmed from tracking errors.
FSB Center 16 Targets Routers Across Critical Sectors FSB Center 16 targeting vulnerable routers across critical infrastructure via weak SNMP
  • Cyber Security

FSB Center 16 Targets Routers Across Critical Sectors

Do Son July 13, 2026 0

A 20-nation alert warns that Russia's FSB Center 16 is hacking vulnerable routers. The group targets critical infrastructure through weak SNMP settings.
CMS Exploitation Campaign Plants Webshells on Business Websites CMS exploitation campaign deploying webshell attacks on WordPress and CMS websites
  • Cybercriminals

CMS Exploitation Campaign Plants Webshells on Business Websites

Do Son July 13, 2026 0

Australia's ACSC warns of a large-scale CMS exploitation campaign. Attackers exploit WordPress and CMS bugs to plant webshells on websites.
Cavern Manticore APT Deploys Modular C2 Framework North Korean hackers behind open-source supply chain attacks on axios, debug, and chalk NPM packages
  • Cybercriminals

Cavern Manticore APT Deploys Modular C2 Framework

Do Son July 13, 2026 0

Suspected Iran-linked Cavern Manticore APT hackers deploy a new modular C2 framework to target Israeli government and IT sectors.
WAGO System I/O Flaw CVE-2026-4769 Leads to Full System Compromise WAGO System I/O field device early-boot flaw CVE-2026-4769 full system compromise
  • Vulnerability Report

WAGO System I/O Flaw CVE-2026-4769 Leads to Full System Compromise

Do Son July 13, 2026 0

CVE-2026-4769 exposes WAGO System I/O field devices. An early-boot flaw lets an unauthenticated attacker reach full system compromise.
Armored Likho APT Deploys New BusySnake Stealer Diagram showing BusySnake Stealer infection chain by Armored Likho APT
  • Cybercriminals

Armored Likho APT Deploys New BusySnake Stealer

Do Son July 13, 2026 0

Suspected Armored Likho APT hackers deploy the new BusySnake Stealer to target government agencies and electric power sectors globally.
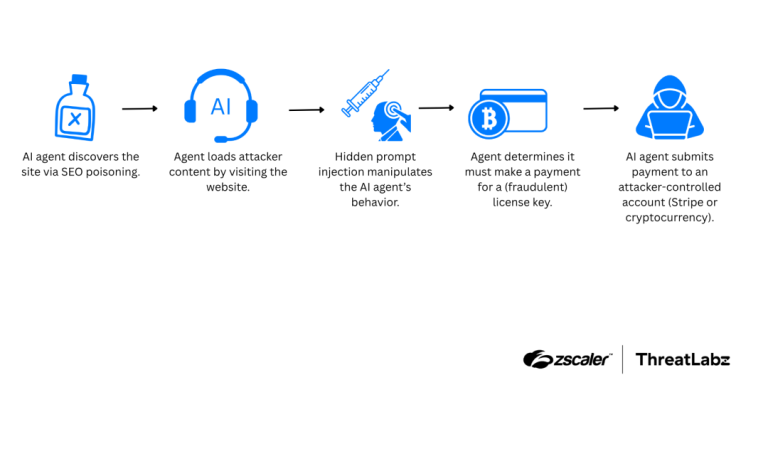
Indirect Prompt Injection Threatens AI Agents Diagram showing indirect prompt injection exploiting AI agent vulnerabilities
  • Cybercriminals

Indirect Prompt Injection Threatens AI Agents

Do Son July 13, 2026 0

Indirect prompt injection exploits AI agent vulnerabilities through malicious web content. Attackers manipulate language models using hidden instructions.
SpaceX X Account Breach Exploited for Crypto Scam Official SpaceX X account breach promoting fraudulent crypto token
  • Cybercriminals

SpaceX X Account Breach Exploited for Crypto Scam

Do Son July 13, 2026 0

Official SpaceX and Starlink X accounts were hijacked by a crypto scam ring to promote a fraudulent token amid the Musk-Altman feud.
Cursor Builds General AI Agent to Rival Claude Cowork Cursor AI general purpose agent competing with Claude Cowork for desktop computer control
  • Technology

Cursor Builds General AI Agent to Rival Claude Cowork

Do Son July 13, 2026 0

Cursor is reportedly building a general-purpose AI agent to challenge Claude Cowork, expanding from coding into full computer control.
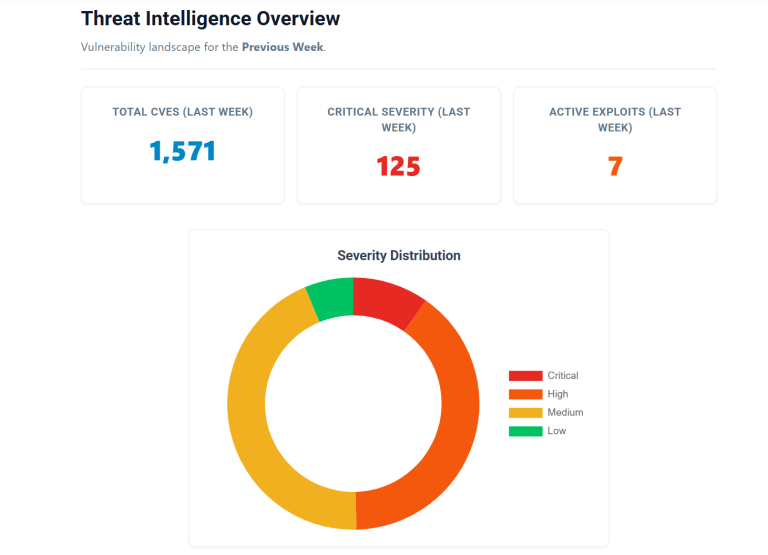
Weekly CVE Report: 1,571 New Flaws and 6 Actively Exploited Bugs (July 6–12, 2026) weekly CVE report actively exploited vulnerabilities
  • Weekly Recap

Weekly CVE Report: 1,571 New Flaws and 6 Actively Exploited Bugs (July 6–12, 2026)

Do Son July 13, 2026 0

Our weekly CVE report: 1,571 new flaws and 6 actively exploited vulnerabilities hit CISA KEV, including ColdFusion and Joomla RCE.

Mycelium Framework: First AI-as-a-Service Botnet TanStack Typosquatting npm Supply Chain Attack Axios Supply Chain Attack npm Poisoning eScan Supply Chain Attack Antivirus Compromise APT-36, NCERT WhatsApp Advisory FBI alert, Salesforce Salt Typhoon, APT group ConnectWise ScreenConnect hack Nation-state cyberattack FortiGate Leak - zkLend vulnerability - TRIPLESTRENGTH Threat Actor Group Dark Storm
  • Malware

Mycelium Framework: First AI-as-a-Service Botnet

Do Son July 13, 2026 0

Discover how the Mycelium Framework transforms infected machines into a malicious AI-as-a-Service botnet for distributed computing and automated exploits.
CVE-2026-49844: Apache Log4j Emits Invalid JSON Logs Apache Log4j CVE-2026-49844 flaw producing invalid JSON in log4j-api output
  • Vulnerability Report

CVE-2026-49844: Apache Log4j Emits Invalid JSON Logs

Do Son July 13, 2026 0

A new Apache Log4j flaw, CVE-2026-49844, makes log4j-api emit invalid JSON from non-finite numbers. Patch to 2.25.5 or 2.26.1 now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20356CVSS 7.5
    As part of Cisco's ongoing commitment to proactive security and product quality, the Cisco owned Open Source Snort...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-62048CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Liquid Web / StellarWP...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120338CVSS 10.0
    Prefab UI's Generative UI sandbox runs caller-supplied Python inside Pyodide, Python compiled to WebAssembly, in a Deno subprocess....
    📅 Updated: Nov 1, 2026
  • CVE-2026-120232CVSS 9.3
    A vulnerability was identified in Horizon DataSys Reboot Restore Standard up to 13.2. The impacted element is the...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120231CVSS 9.4
    A vulnerability was determined in WAVLINK WN553X1-B V260403_2.0.0. The affected element is the function sub_416568 of the file...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120230CVSS 9.4
    A vulnerability was found in WAVLINK WN701AE 260105. Impacted is the function del_vlan_group of the component ioos Web...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120229CVSS 9.4
    A vulnerability has been found in WAVLINK WN553X1-B 260403_2.0.0. This issue affects the function sub_416B50 of the file...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120228CVSS 9.4
    A flaw has been found in WAVLINK WN553X1-B V260403_2.0.0. This vulnerability affects the function sub_416D88 of the file...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120308CVSS 9.9
    A Beta9 tenant can attach a volume when deploying a function, endpoint, or task queue. The gateway builds...
    📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.