Skip to content
November 1, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
decompress npm Vulnerability CVE-2026-53486 (CVSS 9.1) Threatens 2.8 Million Weekly Downloads decompress npm vulnerability CVE-2026-53486 path traversal in Node.js archive extraction
  • Vulnerability Report

decompress npm Vulnerability CVE-2026-53486 (CVSS 9.1) Threatens 2.8 Million Weekly Downloads

Do Son July 12, 2026 0

A decompress npm vulnerability (CVE-2026-53486, CVSS 9.1) lets crafted archives write files outside the target folder via path traversal. Patch now.
State of Exploited Vulnerabilities — Q2 2026 75 CVEs confirmed exploited in Q2 2026. Microsoft leads with 15, Ivanti tops EPSS at 99%. Full breakdown by vendor, CWE, and publication-to-exploit gap.
  • Report

State of Exploited Vulnerabilities — Q2 2026

Do Son July 11, 2026 0

75 CVEs confirmed exploited in Q2 2026. Microsoft leads with 15, Ivanti tops EPSS at 99%. Full breakdown by vendor, CWE, and publication-to-exploit gap.

Apache IoTDB Fixes Path Traversal and Authentication Bypass Flaws (CVE-2026-24014) Apache IoTDB vulnerabilities path traversal and authentication bypass in DataNode RPC
  • Vulnerability Report

Apache IoTDB Fixes Path Traversal and Authentication Bypass Flaws (CVE-2026-24014)

Do Son July 11, 2026 0

Three Apache IoTDB vulnerabilities include a critical path traversal (CVE-2026-24014) and an authentication bypass. Upgrade to 2.0.8 now.

Silver Fox Ghost Distributor Delivers MODBEACON Trojan to Chosen Targets Harvester APT Linux Backdoor OT Cyberattack Iranian APT Operation Olalampo MuddyWater APT Prince of Persia APT, Tonnerre v50 Patchwork APT, DLL Sideloading Subtle Snail, cyber espionage ShadowSilk, cyber espionage Volt Typhoon APT Group - Chinese Cybersecurity Firm
  • Cyber Security

Silver Fox Ghost Distributor Delivers MODBEACON Trojan to Chosen Targets

Do Son July 11, 2026 0

Silver Fox's Ghost distributor delivers MODBEACON, a modular Rust trojan, to picked targets in Operation Phnom Penh, per Qianxin. Here's what to know.
Apache Camel Vulnerabilities Expose Routes to Header Injection and SSRF Apache Camel vulnerabilities diagram showing header injection and server-side request forgery attack flow across Camel routes
  • Vulnerability Report

Apache Camel Vulnerabilities Expose Routes to Header Injection and SSRF

Do Son July 10, 2026 0

Four Apache Camel vulnerabilities allow header injection, server-side request forgery, secret disclosure, and an authentication bypass. Patch to 4.21.0 now.
Gardyn IoT Hub Flaw CVE-2026-13768 (CVSS 10) Enables Unauthenticated Remote Code Execution Gardyn IoT Hub advisory graphic showing CVE-2026-13768 remote code execution risk on smart garden devices
  • Vulnerability Report

Gardyn IoT Hub Flaw CVE-2026-13768 (CVSS 10) Enables Unauthenticated Remote Code Execution

Do Son July 10, 2026 0

CISA warns of a Gardyn IoT Hub flaw. CVE-2026-13768 (CVSS 10) enables unauthenticated remote code execution on smart garden devices. Update now.
FreeBSD Patches Three Kernel Flaws That Enable Local Privilege Escalation FreeBSD privilege escalation advisory chart highlighting a kernel use-after-free and two local root flaws
  • Vulnerability Report

FreeBSD Patches Three Kernel Flaws That Enable Local Privilege Escalation

Do Son July 10, 2026 0

Three FreeBSD privilege escalation flaws, including a kernel use-after-free, let local users gain root. Patch FreeBSD 14 and 15 now.
Kafka Authentication Bypass in the OAUTHBEARER JWT Path Kafka authentication bypass through OAUTHBEARER JWT replay on Apache Kafka 4.0.x brokers
  • Vulnerability Report

Kafka Authentication Bypass in the OAUTHBEARER JWT Path

Do Son July 10, 2026 0

A Kafka authentication bypass lets attackers replay expired JWTs against 4.0.x brokers. The OAUTHBEARER path checks nbf but not exp. No fix yet.
FastNetMon Launches Netomics, a Self-Hosted Routing Intelligence Platform Netomics_Self-hosted_Routing_Intelligence_for_Netw_1783602857g1YFYzWQZz
  • Press Release

FastNetMon Launches Netomics, a Self-Hosted Routing Intelligence Platform

cybernewswire July 10, 2026 0
London, United Kingdom, 10th July 2026, CyberNewswire
Read More Read more about FastNetMon Launches Netomics, a Self-Hosted Routing Intelligence Platform
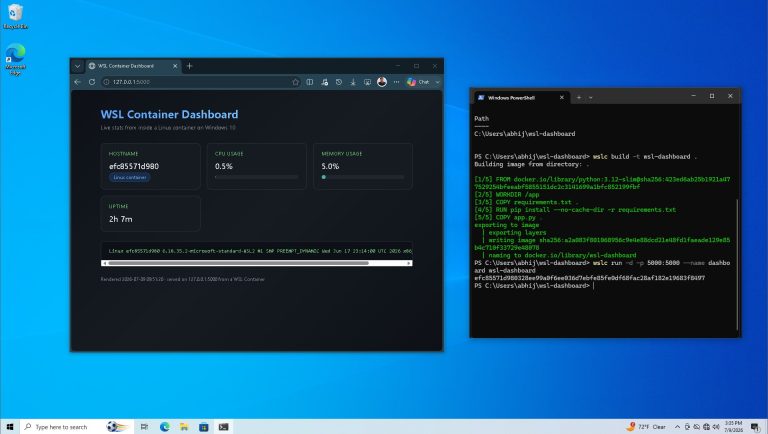
WSL Containers Now Runs on Windows 10 Too WSL Containers running on Windows 10 without Docker Desktop using wslc command in Windows Terminal
  • Windows

WSL Containers Now Runs on Windows 10 Too

Do Son July 10, 2026 0

Microsoft confirms WSL Containers works on Windows 10 (Build 19041+) without Docker Desktop. Here's how to deploy it in six steps.
CVE-2026-13753: HP Missing Authorization Vulnerability HP Deskjet missing authorization vulnerability CVE-2026-13753 exposing printer API security flaw
  • Vulnerability Report

CVE-2026-13753: HP Missing Authorization Vulnerability

Do Son July 10, 2026 0

CVE-2026-13753 exposes a missing authorization vulnerability in HP Deskjet 2800 printers. Unauthenticated attackers can extract sensitive Wi-Fi credentials.
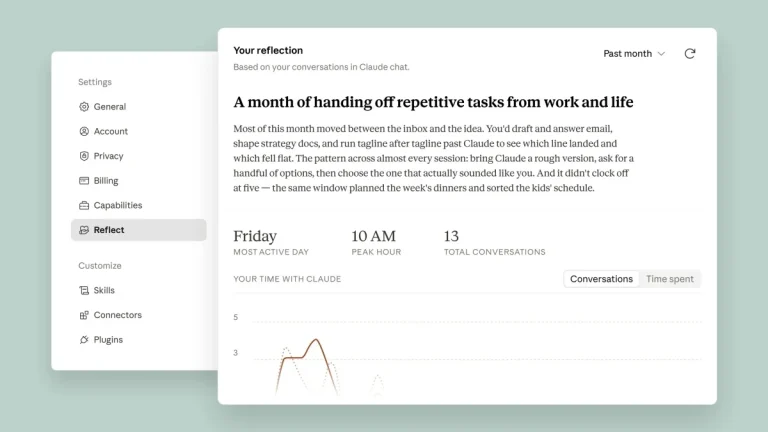
Claude Reflect Dashboard: Anthropic’s New AI Tool Claude Reflect dashboard interface visualizing AI usage statistics and productivity metrics.
  • Technology

Claude Reflect Dashboard: Anthropic’s New AI Tool

Do Son July 10, 2026 0

Discover the Claude Reflect dashboard. Anthropic's new digital health tool visualizes your AI usage, optimizes prompts, and promotes healthy collaboration.
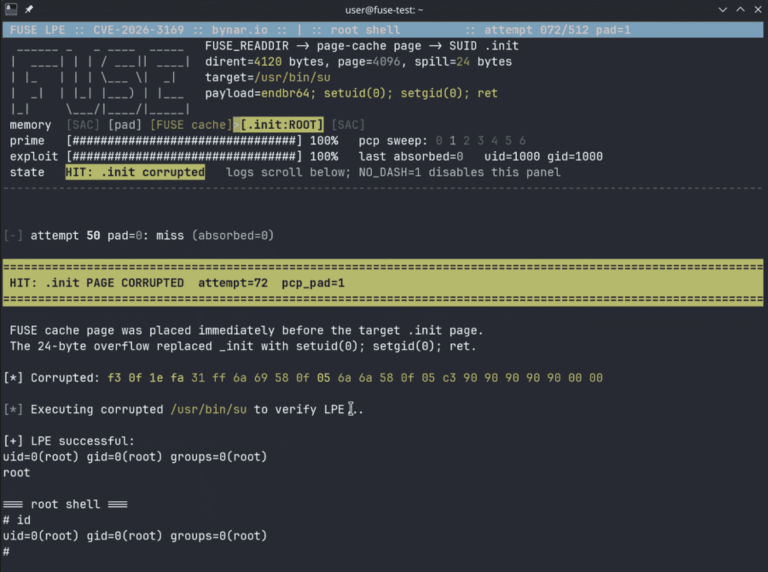
Public PoC Discloses CVE-2026-31694, a Linux Kernel FUSE Local Privilege Escalation Linux kernel FUSE local privilege escalation via CVE-2026-31694 page cache overflow
  • Vulnerability Report

Public PoC Discloses CVE-2026-31694, a Linux Kernel FUSE Local Privilege Escalation

Do Son July 10, 2026 0

Public PoC and full details are out for CVE-2026-31694, a Linux kernel FUSE page cache overflow that gives local privilege escalation to root. Patch now.
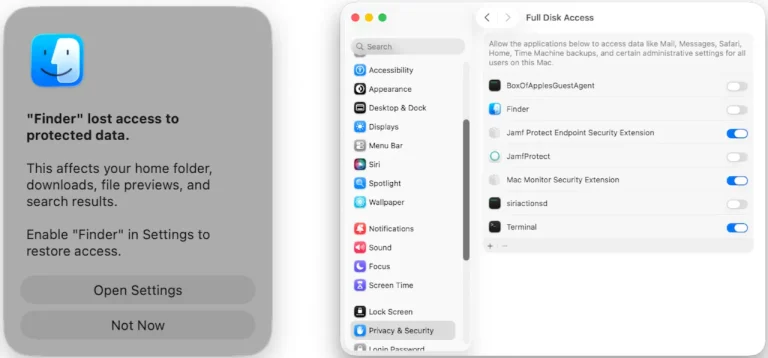
PamStealer macOS Malware Poses as Maccy to Steal Passwords PamStealer macOS malware delivering a Rust infostealer through a fake Maccy clipboard app
  • Malware

PamStealer macOS Malware Poses as Maccy to Steal Passwords

Do Son July 10, 2026 0

PamStealer macOS malware hides in a fake Maccy app and drops a Rust infostealer that checks your password via PAM before stealing it.
GNU Guix Vulnerabilities Expose guix substitute and guix pull GNU Guix vulnerabilities in guix substitute and guix pull enabling remote privilege escalation
  • Vulnerability Report

GNU Guix Vulnerabilities Expose guix substitute and guix pull

Do Son July 10, 2026 0

Four GNU Guix vulnerabilities in guix substitute and guix pull allow remote privilege escalation, file overwrite, and local file disclosure. Update now.
JADEPUFFER Marks the First AI-Driven Agentic Ransomware Attack JADEPUFFER agentic ransomware attack chain diagram from Langflow RCE to database extortion
  • Malware

JADEPUFFER Marks the First AI-Driven Agentic Ransomware Attack

Do Son July 10, 2026 0

Sysdig documented JADEPUFFER, the first agentic ransomware run end-to-end by an AI agent. It breached Langflow via CVE-2025-3248 and extorted a database.
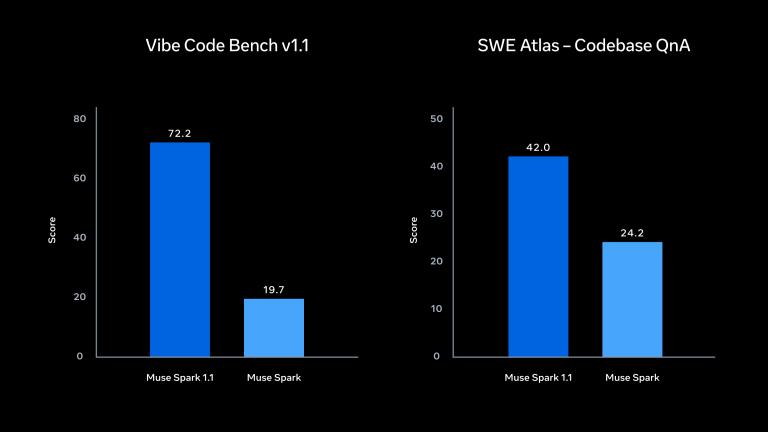
Meta Introduces Muse Spark 1.1 AI Model Meta Muse Spark 1.1 artificial intelligence model for agent tasks and programming.
  • Technology

Meta Introduces Muse Spark 1.1 AI Model

Do Son July 10, 2026 0

Meta introduces Muse Spark 1.1, a closed-source AI model built for complex agent tasks and programming. Discover its advanced capabilities and pricing.
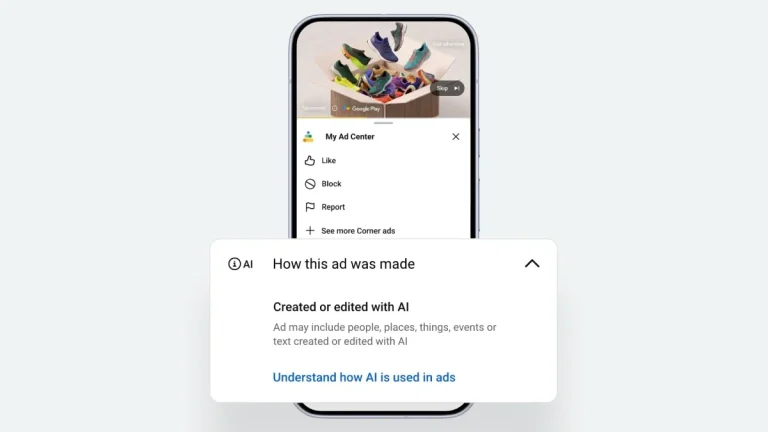
Google Ads AI Transparency Tools to Combat Fake Content Google Ads AI transparency tools displayed within the My Ad Center interface.
  • Technology

Google Ads AI Transparency Tools to Combat Fake Content

Do Son July 10, 2026 0

Google Ads AI transparency tools will soon label artificial content in My Ad Center. Discover how this update aims to protect consumer trust globally.
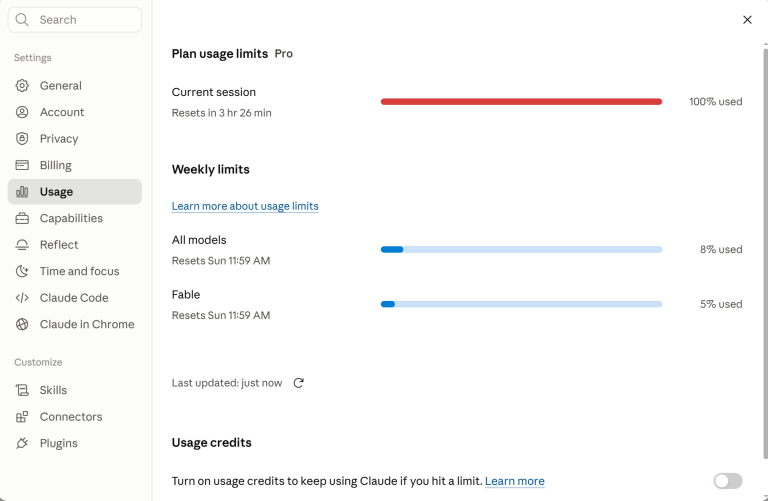
Claude Code Credit Reset Sparks AI Rivalry Claude Code credit reset notification dashboard illustrating the competitive AI model rivalry.
  • Technology

Claude Code Credit Reset Sparks AI Rivalry

Do Son July 10, 2026 0

The recent Claude Code credit reset intensifies the AI race with OpenAI, allowing developers extended access to the powerful Claude Fable 5 model.
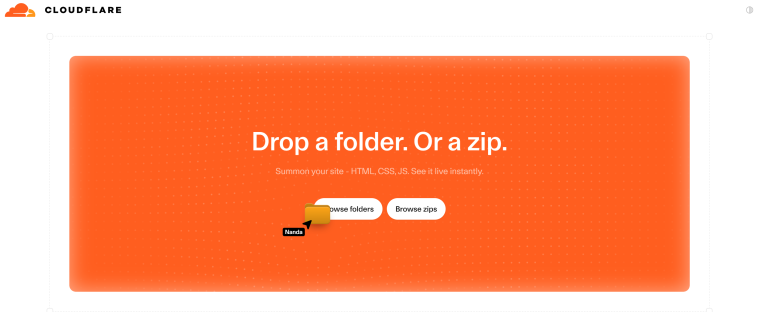
Cloudflare Launches Drop for Temporary and Permanent Static Site Hosting Cloudflare Drop static website hosting interface with instant global deployment.
  • Technology

Cloudflare Launches Drop for Temporary and Permanent Static Site Hosting

Do Son July 10, 2026 0

Cloudflare Drop offers free, rapid hosting for static websites with automatic global CDN acceleration. Claim your site for permanent access.
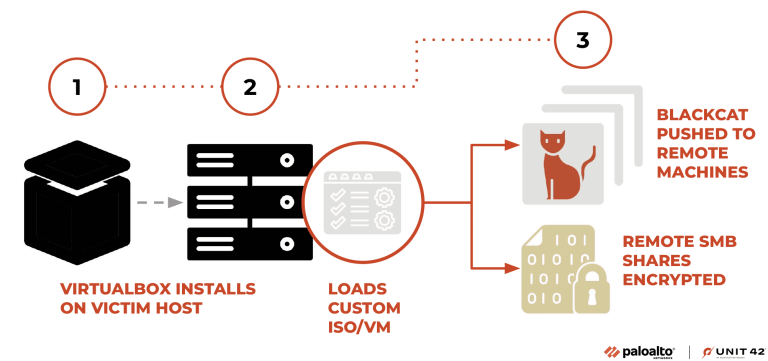
Florida Ransomware Negotiator Sentenced for Betraying Victims to BlackCat Florida ransomware negotiator sentenced for BlackCat ransomware extortion scheme
  • Cybercriminals

Florida Ransomware Negotiator Sentenced for Betraying Victims to BlackCat

Do Son July 10, 2026 0

A Florida ransomware negotiator got 70 months for feeding clients' secrets to BlackCat ransomware actors. The DOJ seized over $10 million in proceeds.
Django SQL Injection Flaw CVE-2026-1207 Is Being Exploited in the Wild Django SQL injection CVE-2026-1207 exploited in the wild via PostGIS RasterField raster lookups
  • Vulnerability Report

Django SQL Injection Flaw CVE-2026-1207 Is Being Exploited in the Wild

Do Son July 10, 2026 0

CVE-2026-1207 is a Django SQL injection flaw (CVSS 8.3) in PostGIS raster lookups. Canada's CCCS says it is exploited in the wild. Patch now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20356CVSS 7.5
    As part of Cisco's ongoing commitment to proactive security and product quality, the Cisco owned Open Source Snort...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120308CVSS 9.9
    A Beta9 tenant can attach a volume when deploying a function, endpoint, or task queue. The gateway builds...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120307CVSS 9.9
    The Beta9 worker serves the sandbox file API from outside the container. getHostPathFromContainerPath turns the tenant's container path...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120306CVSS 9.9
    Beta9 turns each shell command in a tenant image definition into a Dockerfile RUN line and executes it...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120227CVSS 9.4
    A vulnerability was detected in WAVLINK WN701AE M01AE_V260105. This affects the function del_staticrule of the file static_route_setting.sh of...
    📅 Updated: Nov 1, 2026
  • CVE-2026-39738CVSS 9.8
    Deserialization of Untrusted Data vulnerability in Aman FunnelKit Automations wp-marketing-automations allows Object Injection.This issue affects FunnelKit Automations: from...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120225CVSS 9.4
    A weakness has been identified in Oray Pugongying X5 Pro up to 7.6.1. Affected by this vulnerability is...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120224CVSS 9.4
    A security flaw has been discovered in Oray Pugongying X5 Pro up to 7.6.1. Affected is the function...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120198CVSS 10.0
    A vulnerability has been found in WAVLINK WL-WN530BE1-A V251117. Affected is the function con_check_read_finish of the file /protocol.csp....
    📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.