Skip to content
November 1, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Roundcube 1.7.2 Patches Zero-Click Stored XSS CVE-2026-54433 Roundcube zero-click XSS warning showing CVE-2026-54433 stored XSS in plain-text email rendering
  • Vulnerability Report

Roundcube 1.7.2 Patches Zero-Click Stored XSS CVE-2026-54433

Do Son July 9, 2026 0

A Roundcube zero-click XSS, CVE-2026-54433, lets an email run script with no click. Roundcube 1.7.2 also fixes a second stored XSS. Update now.
Apache Lucene.NET Vulnerability Trio Fixed in Beta 18 Apache Lucene.NET vulnerability advisory showing a Lucene.Net.Replicator path traversal risk
  • Vulnerability Report

Apache Lucene.NET Vulnerability Trio Fixed in Beta 18

Do Son July 9, 2026 0

Three Apache Lucene.NET vulnerability fixes land, including a Lucene.Net.Replicator path traversal flaw enabling unauthenticated file read. Patch now.
Feast Feature Server Flaw Lets Unauthenticated Attackers Write Files Feast Feature Server arbitrary file write vulnerability advisory graphic
  • Vulnerability Report

Feast Feature Server Flaw Lets Unauthenticated Attackers Write Files

Do Son July 9, 2026 0

A critical Feast Feature Server flaw (CVE-2026-23537) lets unauthenticated attackers perform arbitrary file write and risk remote code execution. Act now.
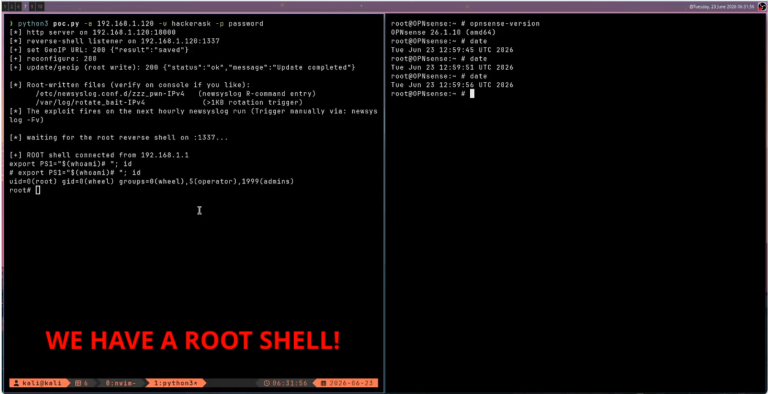
OPNsense Root RCE Flaw CVE-2026-57155 (CVSS 9.9): Details and PoC Publicly Disclosed OPNsense root RCE advisory graphic showing an arbitrary file write chain to root on the firewall
  • Vulnerability Report

OPNsense Root RCE Flaw CVE-2026-57155 (CVSS 9.9): Details and PoC Publicly Disclosed

Do Son July 9, 2026 0

OPNsense root RCE flaws are public with PoC code. CVE-2026-57155 (9.9) chains an arbitrary file write to root. Patch 26.1.11 or 26.4.1p1 now.
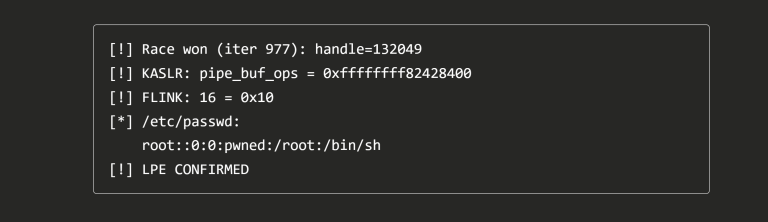
Linux Kernel Privilege Escalation Flaw CVE-2026-46215: PoC and Full Write-Up Public Linux kernel privilege escalation CVE-2026-46215 DRM GEM use-after-free root exploit diagram
  • Vulnerability Report

Linux Kernel Privilege Escalation Flaw CVE-2026-46215: PoC and Full Write-Up Public

Do Son July 9, 2026 0

Public PoC and write-up detail a Linux kernel privilege escalation flaw (CVE-2026-46215) in DRM GEM. A local user gets root in ~99% of runs.
MOVEit Transfer Fixes Stored XSS and Two Other Vulnerabilities MOVEit Transfer stored XSS vulnerability CVE-2026-11903 patched in version 2026.0.1
  • Vulnerability Report

MOVEit Transfer Fixes Stored XSS and Two Other Vulnerabilities

Do Son July 9, 2026 0

Progress patched three MOVEit Transfer flaws, including a stored XSS bug (CVE-2026-11903). No exploitation is confirmed. Update now.
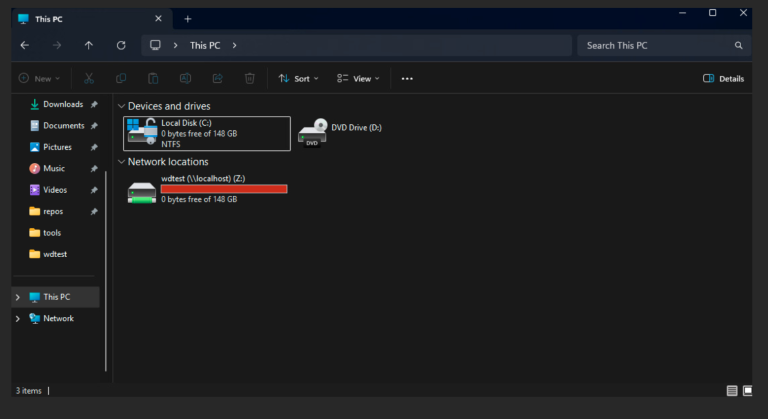
Microsoft Patches RoguePlanet Defender Zero-Day That Grants SYSTEM Access Microsoft Defender zero-day RoguePlanet CVE-2026-50656 patched via Malware Protection Engine update
  • Vulnerability Report

Microsoft Patches RoguePlanet Defender Zero-Day That Grants SYSTEM Access

Do Son July 9, 2026 0

Microsoft patched the RoguePlanet Microsoft Defender zero-day, CVE-2026-50656, a race condition that grants SYSTEM privileges. A public PoC exists.
Chrome MV2 Extensions Removed from Web Store Aug 31 Chrome Web Store removing all Manifest V2 extensions on August 31 2026 affecting uBlock Origin and others
  • Technology

Chrome MV2 Extensions Removed from Web Store Aug 31

Do Son July 9, 2026 0

Google will remove all MV2 extensions from the Chrome Web Store on August 31, 2026. Back up your CRX files now before they are gone.
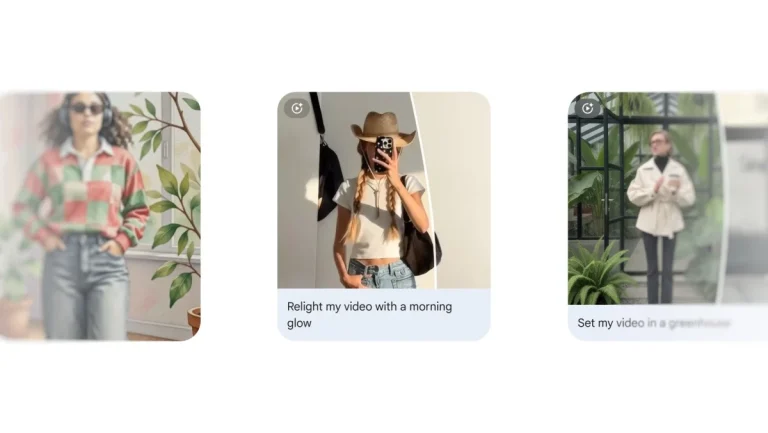
Google Photos Video Remix Uses Gemini Omni AI Google Photos Video Remix feature using Gemini Omni AI to apply filters and swap video backgrounds
  • Technology

Google Photos Video Remix Uses Gemini Omni AI

Do Son July 9, 2026 0

Google launches Video Remix in Google Photos, powered by Gemini Omni. Users can apply filters, swap backgrounds, and add avatars in seconds.
North Korea-Linked PolinRider Supply Chain Attack Expands Across Open Source PolinRider supply chain attack diagram showing North Korean hackers hiding loaders in open-source packages
  • Cybercriminals

North Korea-Linked PolinRider Supply Chain Attack Expands Across Open Source

Do Son July 9, 2026 0

Socket links the PolinRider supply chain attack to North Korean hackers. The campaign hid loaders in 108 open-source packages across four ecosystems.
KDDI Data Breach: Millions of Emails and Passwords Stolen KDDI data breach illustration, KDDI email leak security concept
  • Data Leak

KDDI Data Breach: Millions of Emails and Passwords Stolen

Do Son July 9, 2026 0

Discover the details of the recent KDDI data breach. Hackers stole over 12 million email addresses and millions of passwords. Learn how to protect yourself.

Rare Werewolf Phishing Campaign Targets Russian Aerospace With AnyDesk WhatsApp Worm, Brazilian Banking Trojan LAPSUS$ Alliance, Scattered Spider Ransomware, Cybercrime RedCurl APT group Russian Cyberespionage, ApolloShadow Malware
  • Cybercriminals

Rare Werewolf Phishing Campaign Targets Russian Aerospace With AnyDesk

Do Son July 9, 2026 0

Seqrite ties a Rare Werewolf phishing campaign to Russian aerospace firms, using a fake invoice to plant AnyDesk for stealthy remote access.
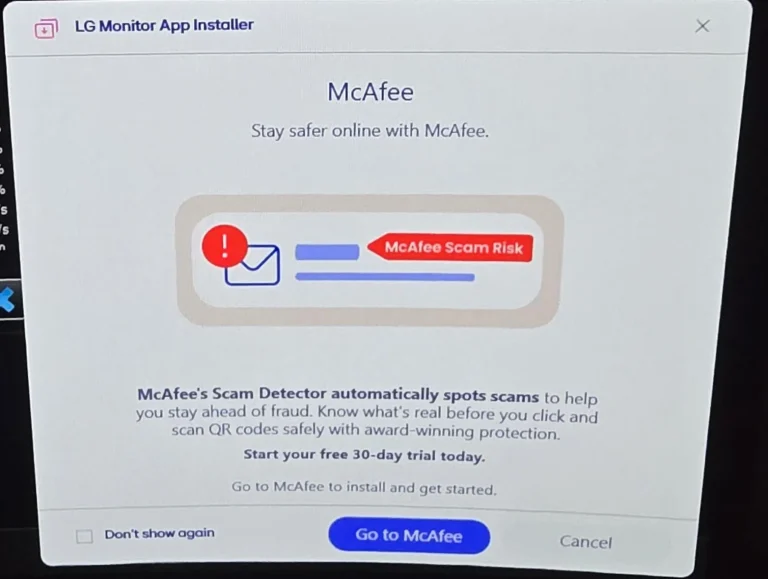
Hidden LG Monitor Adware: Stop Unwanted Pop-ups Now LG monitor adware warning showing unwanted McAfee pop-ups and bloatware installation
  • Malware

Hidden LG Monitor Adware: Stop Unwanted Pop-ups Now

Do Son July 9, 2026 0

Discover how hidden LG monitor adware automatically installs unwanted McAfee pop-ups on your PC. Learn how to stop this intrusive bloatware today.
HPLIP Vulnerability CVE-2026-14544 (CVSS 9.8) Allows Arbitrary Code Execution HPLIP vulnerability advisory graphic showing CVE-2026-14544 arbitrary code execution via crafted print data
  • Vulnerability Report

HPLIP Vulnerability CVE-2026-14544 (CVSS 9.8) Allows Arbitrary Code Execution

Do Son July 9, 2026 0

A critical HPLIP vulnerability, CVE-2026-14544 (CVSS 9.8), lets a remote attacker gain arbitrary code execution via crafted print data. Patch now.
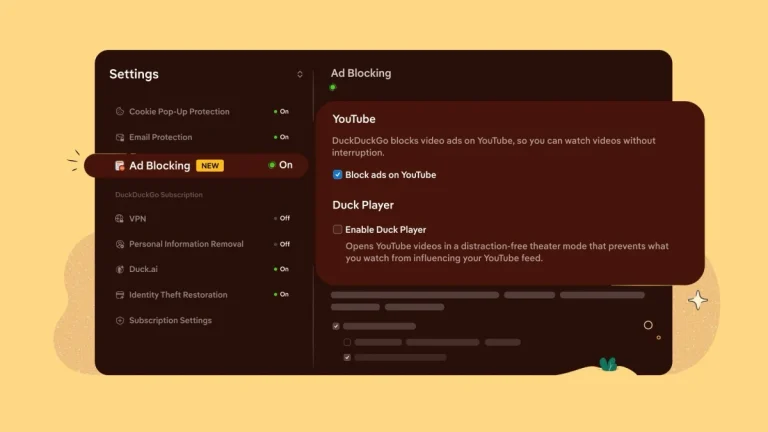
DuckDuckGo Blocks YouTube Ads by Default on All Platforms DuckDuckGo browser blocking YouTube video ads by default using uBlock Origin community filter lists
  • Technology

DuckDuckGo Blocks YouTube Ads by Default on All Platforms

Do Son July 9, 2026 0

DuckDuckGo browser now blocks YouTube video ads by default on iOS, Windows, and Mac, using uBlock Origin filters as Chrome's MV3 limits rival tools.
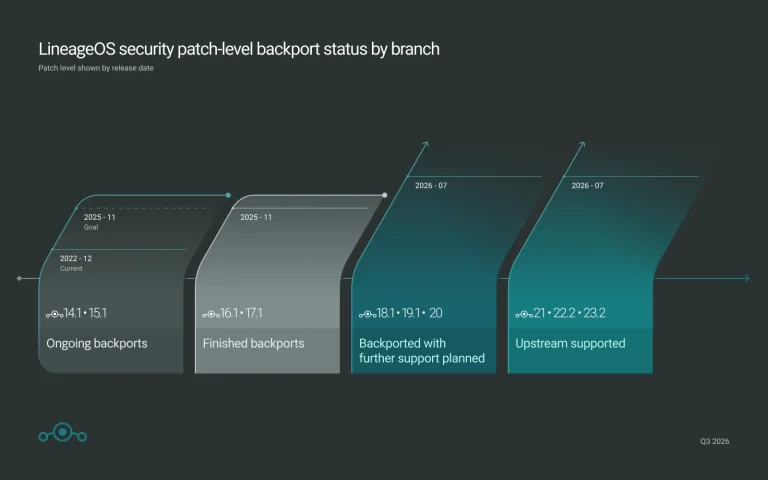
LineageOS Browser Flash Tool Makes ROM Install Easier LineageOS browser-based flashing tool using WebUSB ADB Fastboot for custom Android ROM installation
  • Android

LineageOS Browser Flash Tool Makes ROM Install Easier

Do Son July 9, 2026 0

LineageOS launches a browser-based flashing tool via WebUSB, a redesigned updater showing patch levels, and streaming A/B OTA updates.
GitLab Patch Release Fixes Eight Flaws, Including a High-Severity XSS Bug (CVE-2026-6896) GitLab patch release fixing cross-site scripting vulnerability CVE-2026-6896 in version 19.1.2
  • Vulnerability Report

GitLab Patch Release Fixes Eight Flaws, Including a High-Severity XSS Bug (CVE-2026-6896)

Do Son July 9, 2026 0

The GitLab patch release fixes 8 flaws, including a high-severity cross-site scripting bug (CVE-2026-6896). Update to 19.1.2 now.
CVE-2026-0288: PAN-OS Buffer Overflow Can Execute Arbitrary Code PAN-OS buffer overflow CVE-2026-0288 enabling arbitrary code execution on Palo Alto firewall
  • Vulnerability Report

CVE-2026-0288: PAN-OS Buffer Overflow Can Execute Arbitrary Code

Do Son July 9, 2026 0

A PAN-OS buffer overflow, CVE-2026-0288, enables arbitrary code execution on Palo Alto firewalls. Patch now.
Chrome Security Update Patches 27 Flaws, Including Two Critical Use-After-Free Bugs Chrome security update patching critical use-after-free vulnerabilities in version 150.0.7871.114
  • Vulnerability Report

Chrome Security Update Patches 27 Flaws, Including Two Critical Use-After-Free Bugs

Do Son July 9, 2026 0

Google's latest Chrome security update fixes 27 flaws, including two critical use-after-free bugs. Update to 150.0.7871.114 now.
Foxit PDF Reader Flaws Enable Arbitrary Code Execution Foxit PDF Reader arbitrary code execution vulnerability patched in version 2026.1.2
  • Vulnerability Report

Foxit PDF Reader Flaws Enable Arbitrary Code Execution

Do Son July 8, 2026 0

Foxit fixed 28 flaws in Foxit PDF Reader and PDF Editor. Twenty allow arbitrary code execution via crafted PDFs. Update to 2026.1.2 now.
OpenSSH 10.4 Ships Eight Security Fixes for SSH Clients and Servers OpenSSH 10.4 security fixes including a client use-after-free and SFTP SCP path flaws
  • Vulnerability Report

OpenSSH 10.4 Ships Eight Security Fixes for SSH Clients and Servers

Do Son July 8, 2026 0

OpenSSH 10.4 ships eight security fixes, including a client use-after-free (CVE-2026-60002) plus SFTP and SCP path bugs. Update now.
Ghost Cache Poisoning Flaw Lets Attackers Hijack Staff Accounts Ghost cache poisoning XSS via x-ghost-preview header advisory graphic
  • Vulnerability Report

Ghost Cache Poisoning Flaw Lets Attackers Hijack Staff Accounts

Do Son July 8, 2026 0

A critical Ghost cache poisoning bug lets an unauthenticated x-ghost-preview header hijack staff accounts. Update to Ghost v6.37.0 now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20356CVSS 7.5
    As part of Cisco's ongoing commitment to proactive security and product quality, the Cisco owned Open Source Snort...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-62048CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Liquid Web / StellarWP...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120338CVSS 10.0
    Prefab UI's Generative UI sandbox runs caller-supplied Python inside Pyodide, Python compiled to WebAssembly, in a Deno subprocess....
    📅 Updated: Nov 1, 2026
  • CVE-2026-120232CVSS 9.3
    A vulnerability was identified in Horizon DataSys Reboot Restore Standard up to 13.2. The impacted element is the...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120231CVSS 9.4
    A vulnerability was determined in WAVLINK WN553X1-B V260403_2.0.0. The affected element is the function sub_416568 of the file...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120230CVSS 9.4
    A vulnerability was found in WAVLINK WN701AE 260105. Impacted is the function del_vlan_group of the component ioos Web...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120229CVSS 9.4
    A vulnerability has been found in WAVLINK WN553X1-B 260403_2.0.0. This issue affects the function sub_416B50 of the file...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120228CVSS 9.4
    A flaw has been found in WAVLINK WN553X1-B V260403_2.0.0. This vulnerability affects the function sub_416D88 of the file...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120308CVSS 9.9
    A Beta9 tenant can attach a volume when deploying a function, endpoint, or task queue. The gateway builds...
    📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.