 Do Son
Cisco Talos exposes ARToken, a phishing platform using device code phishing to steal Microsoft 365 tokens and bypass MFA.
A critical IBM Power HMC vulnerability (CVE-2026-12943) allows unauthenticated attackers to execute commands. Patch your systems immediately.
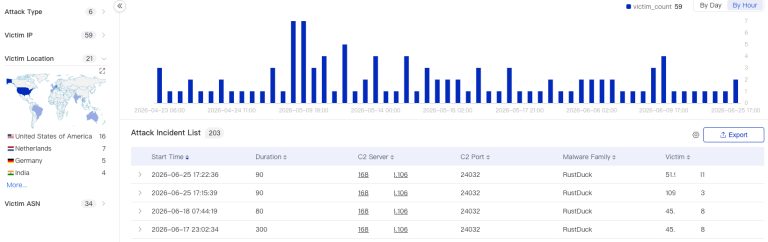
The RustDuck botnet is a fast-evolving two-stage DDoS threat moving from C to Rust, with encrypted C2 and heavy anti-analysis, per XLab.
Microsoft tests Windows 11 cloud rebuild in WinRE, letting users reinstall via the internet without USB drives when the system fails to boot.
A Linux kernel vulnerability (CVE-2024-26582) has a public PoC that turns a TLS use-after-free into a root shell. Details and exploit are out.
Discover how AI generated malware from DeepSeek turns hallucinated ideas into real browser native ransomware using the File System Access API.
CVE-2026-11405 is a Tenda authentication backdoor. It allows full administrative access without valid credentials. Protect your network with these steps.
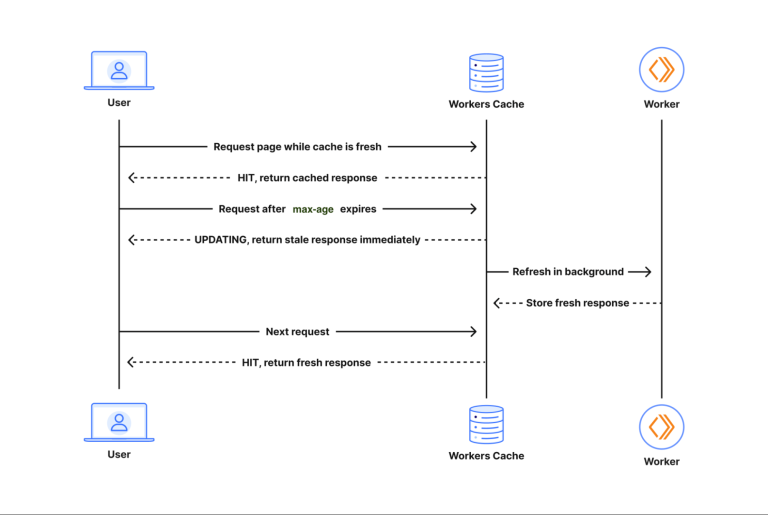
Cloudflare Workers Cache adds a two-layer edge caching system to Workers, cutting CPU costs, boosting SSR performance, and enabling Cache-Tag invalidation.
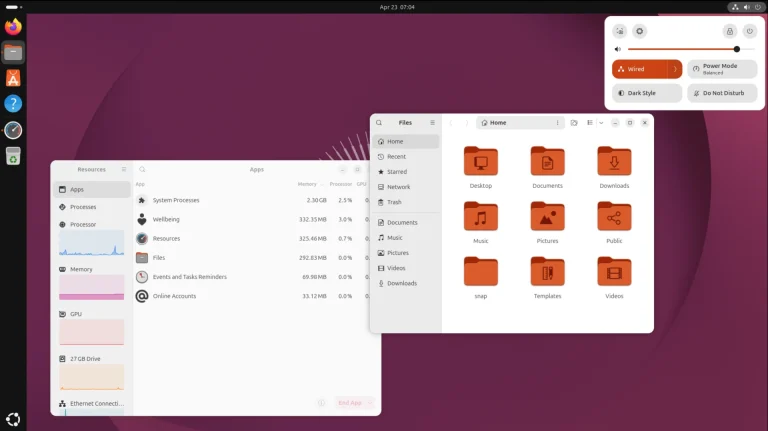
Canonical elevates Ubuntu Arm64 support to first-class in the 26.04 LTS release. Explore Livepatch updates, Snapdragon compatibility, and FEX gaming.
The recent Microsoft Xbox layoffs impact 4,800 employees as the gaming division restructures, divests studios, and aims for financial independence.
A recent Windows 11 storage bug causes the Capability Access Manager log file to consume hundreds of gigabytes. Learn how to verify and fix this issue quickly.
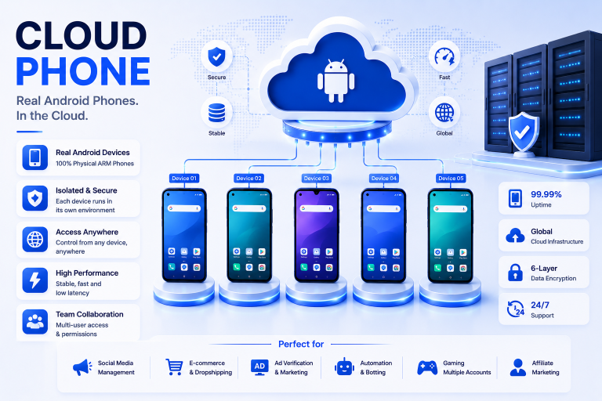
Compare 5 cloud phone tools in 2026, including MoreLogin, Hubstudio, VMOS, DuoPlus, and Multilogin for Android workflows and account teams.
BeyondTrust patched two critical pre-authentication vulnerabilities (CVE-2026-40138, CVE-2026-40139, CVE-2026-40140). Update Remote Support instances now.
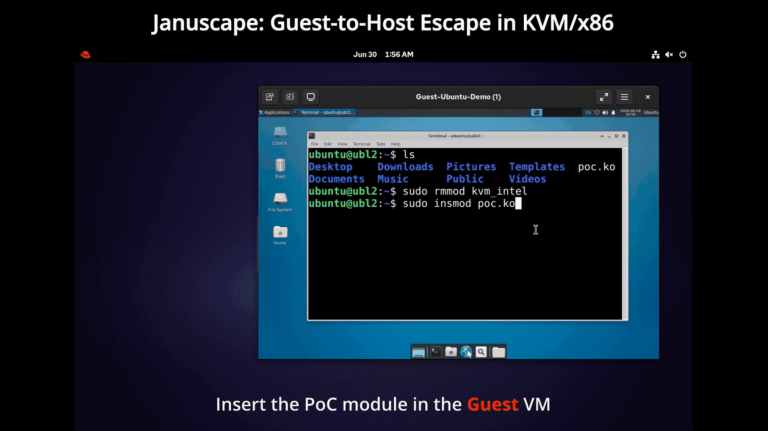
Researchers disclosed a PoC for the Januscape KVM escape (CVE-2026-53359). This use-after-free KVM bug impacts public clouds, allowing host panics and LPE.
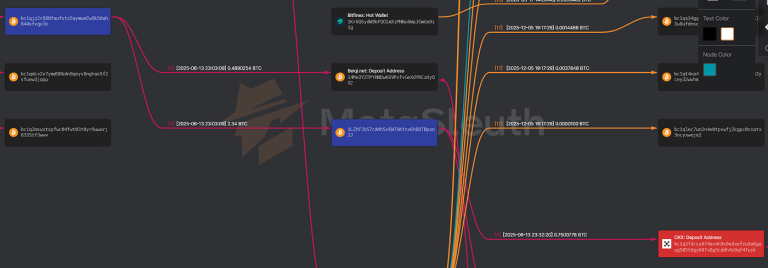
A case study on Kairos ransomware data extortion highlights the futility of paying a $1 million ransom without data encryption.
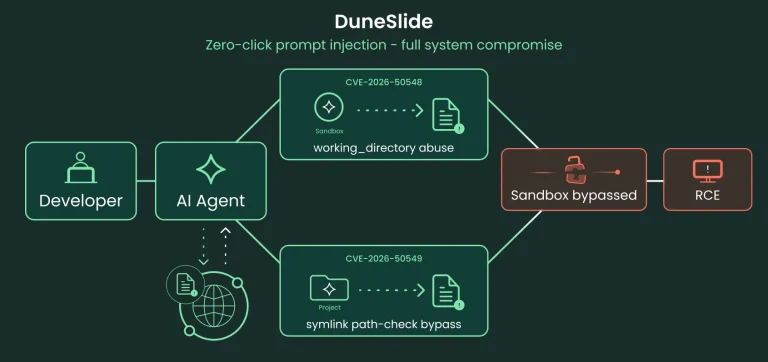
Discover the new Cursor IDE RCE vulnerability called DuneSlide. This critical sandbox escape flaw assigned CVE-2026-50548 threatens developer environments.
A widespread OpenSSL error handling flaw makes apt fail HTTPS in FIPS mode. A stale error queue entry gets misread as fatal. Audit your code.
Discover how Microsoft GDID tracking helped the FBI apprehend a Scattered Spider hacker, revealing the hidden power of Windows device telemetry.
 cybernewswire
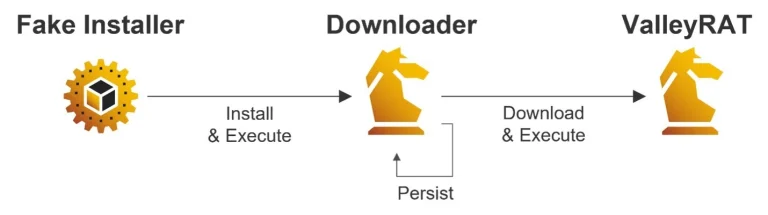
LevelBlue tracks a ValleyRAT malware email campaign using DLL sideloading and fileless execution to hit Japanese and Chinese users.
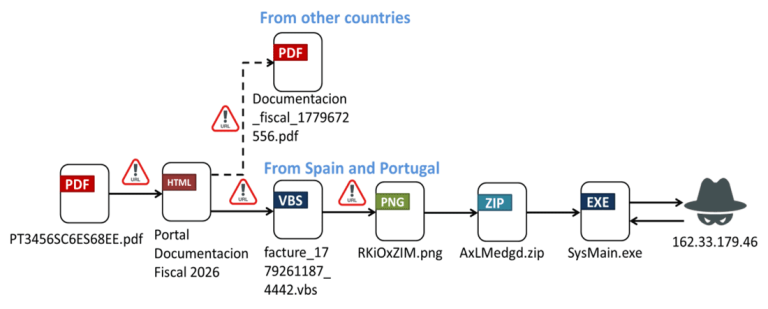
FortiGuard Labs discovered a new Ousaban banking trojan campaign. The attackers use geo-blocking to target banking users in Spain and Portugal.
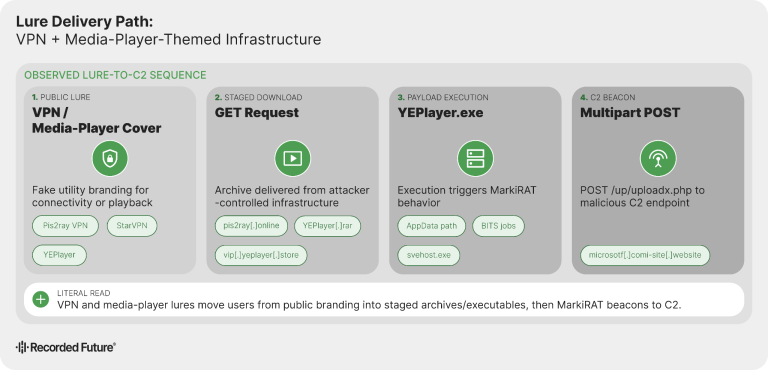
Insikt Group discovered the TAG-182 threat cluster spreading MarkiRAT malware via fake VPN apps to spy on Iranians and alleged dissidents globally.